
CVE-2023-27163-lab
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
container-securitydefensive-toolseducation+6
amulyakaushik/cve-2023-27163-labDocker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
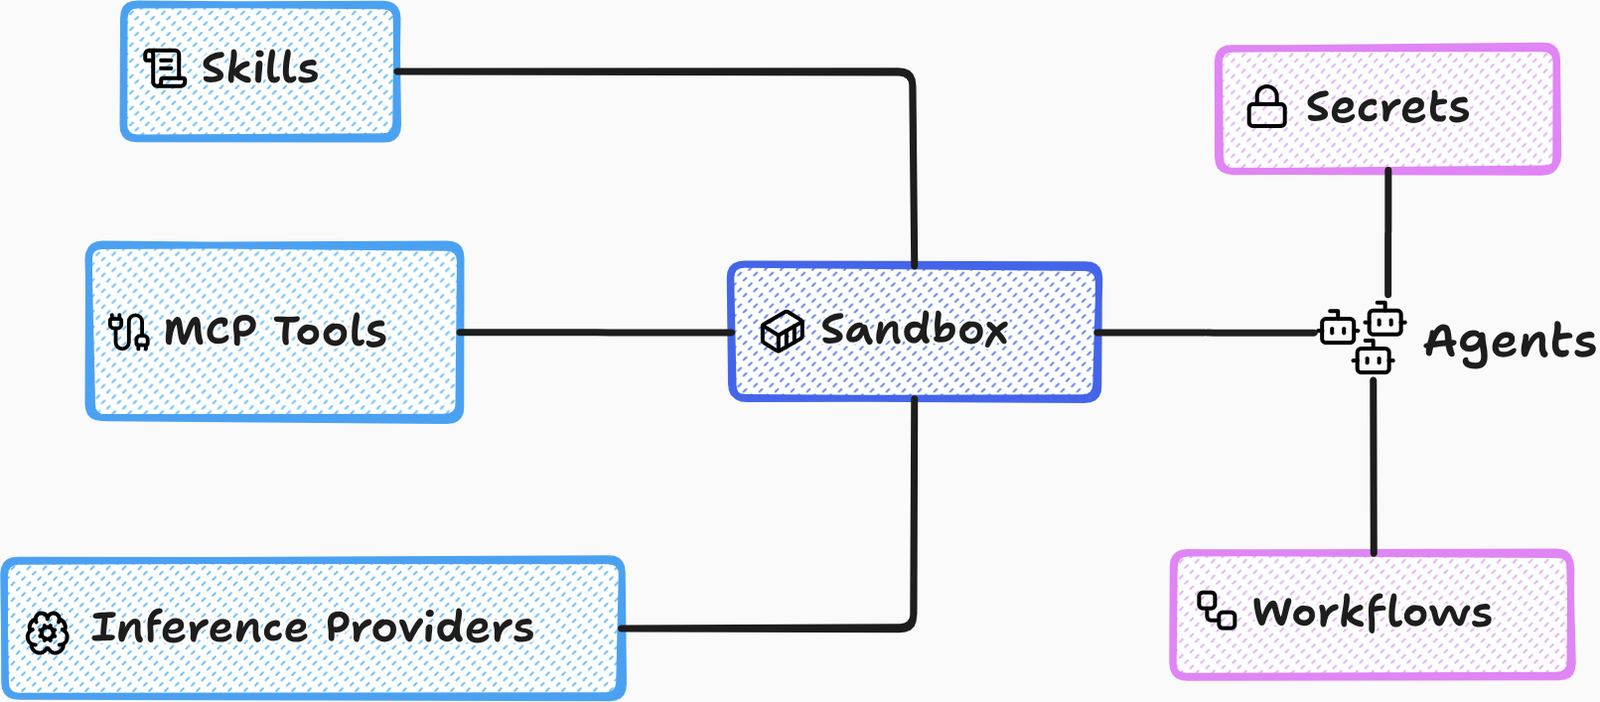 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.
 ashok523/cve-2026-31431
Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…
 detect-defenselab/cve-2026-31431-detection-defense
Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide
 bvabhishek/cve-2026-3288-lab
Docker-based vulnerable lab for CVE-2026-3288 NGINX Ingress configuration injection, with exploit scripts, detection monitoring, and remediation…
 septembersend/cve--2026-24061
Dockerized proof-of-concept environment for CVE-2026-24061, targeting InetUtils telnetd vulnerability for security testing and research.
 chaostoolkit/chaostoolkit-kubernetes
Kubernetes driver extension of the Chaos Toolkit probes and actions API
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…