
CVE-2026-46595-proof
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
binary-analysiscode-analysiscontainer-security+4
sdodson/cve-2026-46595-proofGo proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
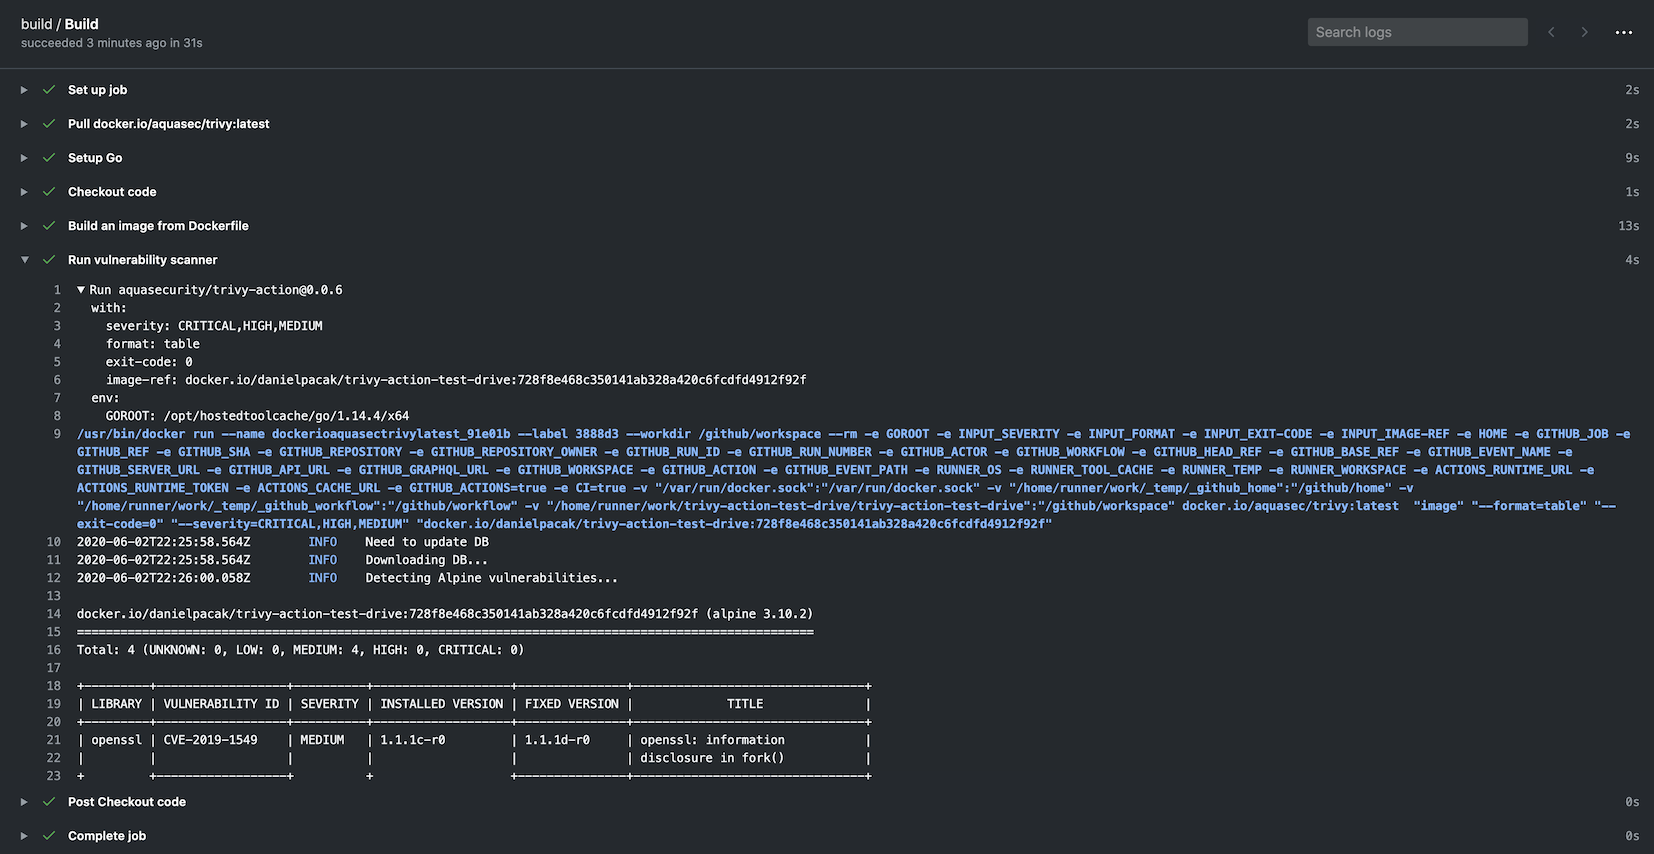 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 trailofbits/claude-code-devcontainer
Sandboxed devcontainer for running Claude Code in bypass mode safely. Built for security audits and untrusted code review.
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 learner202649/cve-2026-40217-poc
The code for personally reproducing the corresponding vulnerability
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 santhreal/keyhog
Open-source secret scanner in Rust
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 safedep/vet
Protect against malicious open source packages 🤖
 mhaggis/package-inferno
A Public Package Scanner for The Community
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…