Kestra-cve-2026-53576

End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…

End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…

Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.

Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…

PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

PoC for Docker `docker cp` arbitrary file write, exploiting symlink and tar extraction flaws to overwrite host binaries or launch agents for…

Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…

Proof-of-concept exploit for CVE-2026-5555, demonstrating container escape via /proc/self/fd symlink in rshared volumes to overwrite host files and…

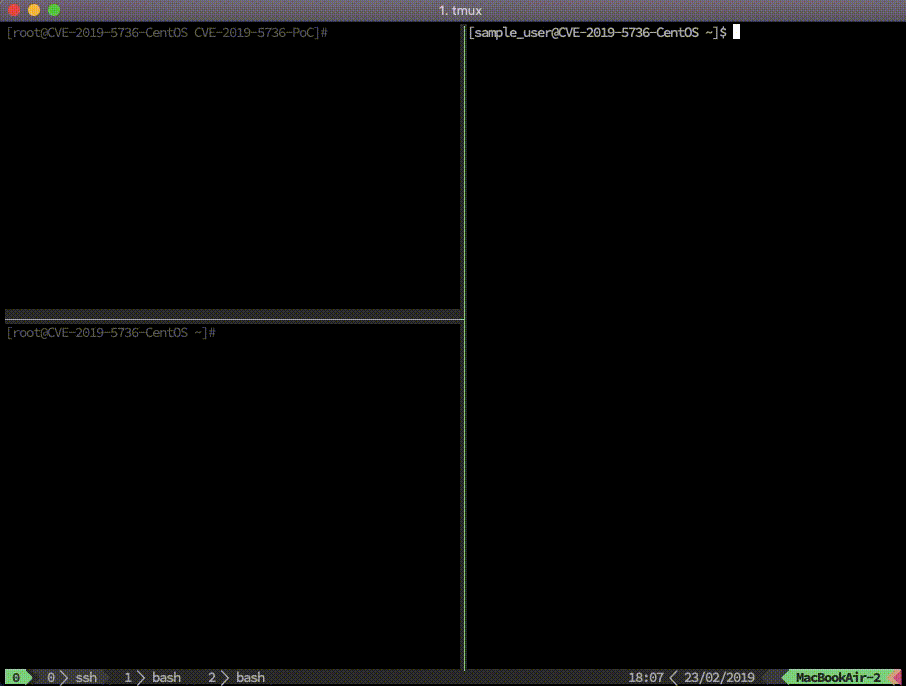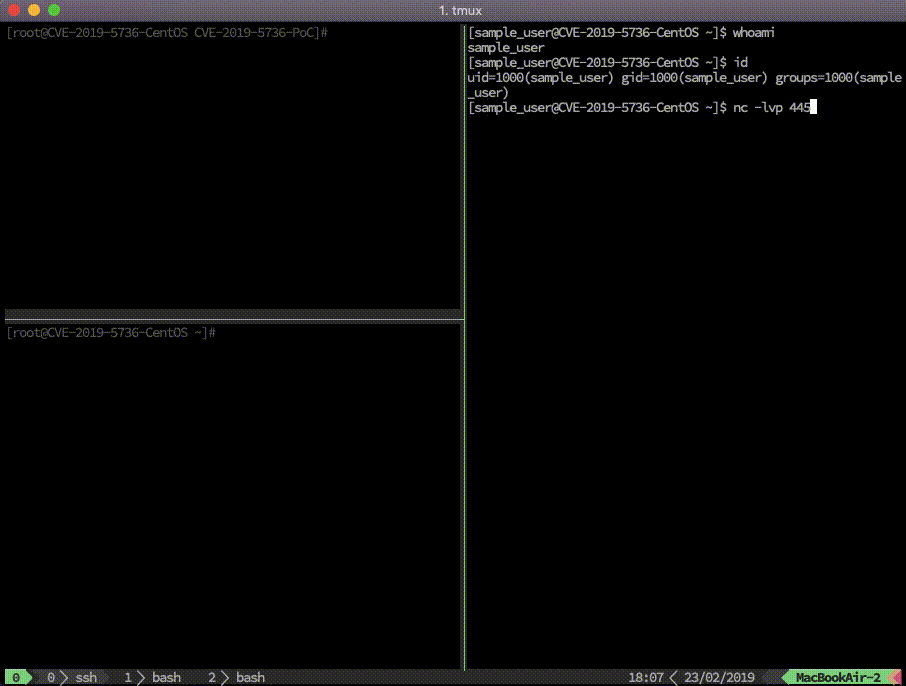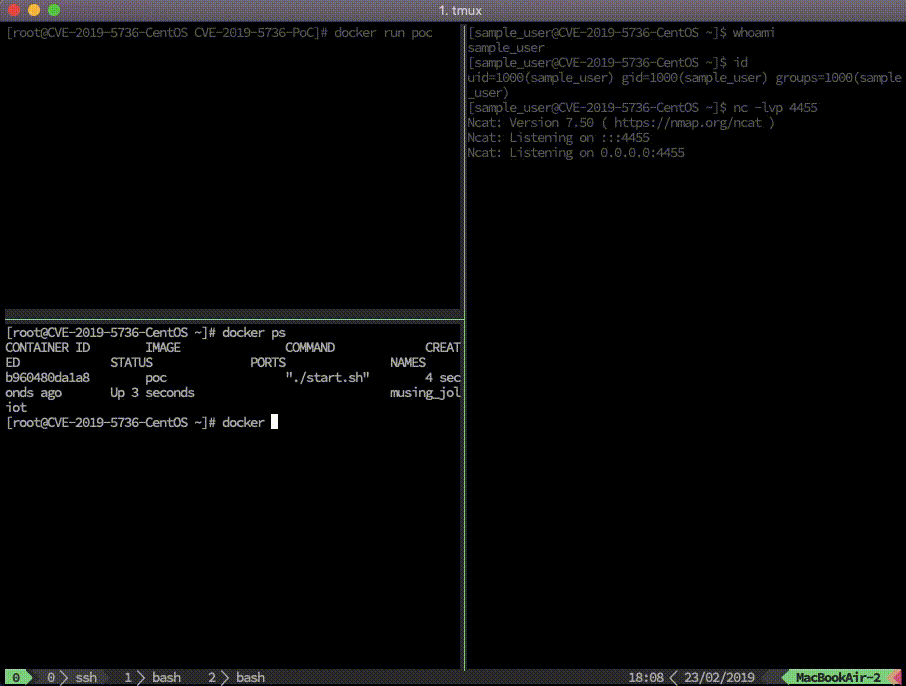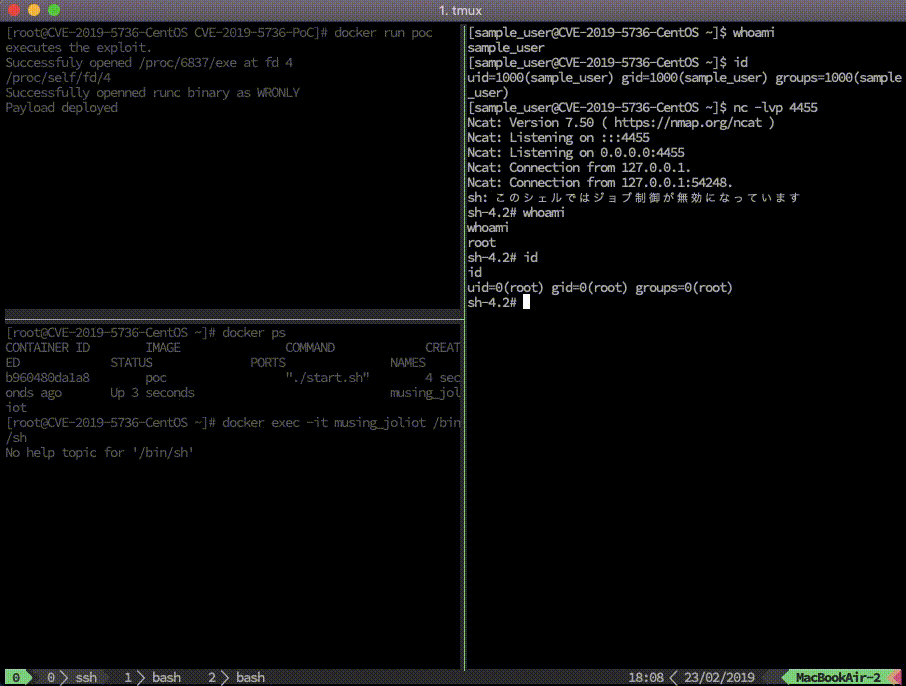
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, enabling host shell access via Docker container breakout.

Lab reproduction of CVE-2026-34040: bypasses Docker/Moby AuthZ plugins using oversized (>1MB) request bodies to create privileged containers with…

Demonstration of CVE-2024-21626 container escape exploit allowing host root access via malicious Docker image, with step-by-step attack scenario for…

Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…

Information about Kubernetes CVE-2020-8558, including proof of concept exploit.

Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)

Proof-of-concept exploit for Kata Containers container escape (CVE-2020-2023) using mknod to modify guest filesystem and overwrite system binaries…

Docker CVE-2022-37708

Proof-of-concept exploit for CVE-2022-39253 demonstrating Docker container escape via malicious Git repository build, enabling host file system read…