

limeyard
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
container-securitydevsecopsdns-subdomain-enumeration+8
clickswave/limeyardDeliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 runewardd/runeward
Governed execution cells for AI agents.
 flowerwitch/cve-2026-85706_docker_exp
Docker-based reproduction environment and PoC for CVE-2026-85706, demonstrating GitLab LFI bypass via .json suffix and trailing slash path tricks.
 microsoft/mxc
Policy-driven, layered isolation and containment
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 vaibhav91one/drupalgeddon2-cve-lab
Intentionally vulnerable Drupal 7.57 lab for reproducing CVE-2018-7600 (Drupalgeddon2) in a Docker container, with an installer script and PHP…
 morzelowski/cve-2026-12243-nltk-poc
Docker lab demonstrating CVE-2026-12243 path traversal in NLTK before 3.10.0, contrasting vulnerable and patched behavior with a synthetic secret in…
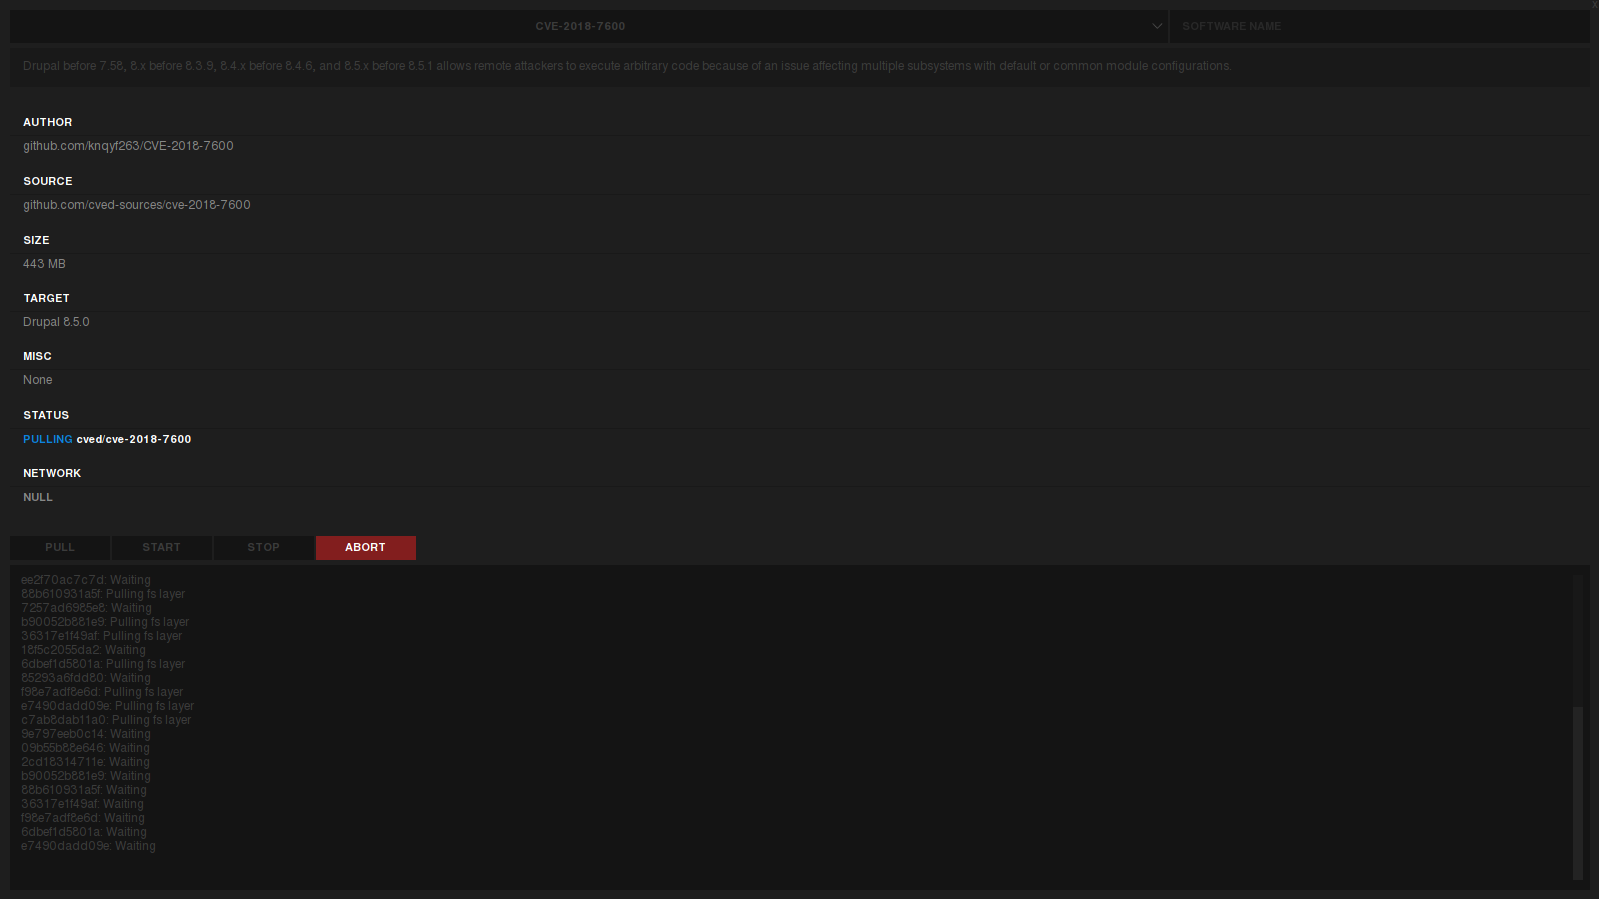 git-rep-src/cved
A tool to manage vulnerable docker containers
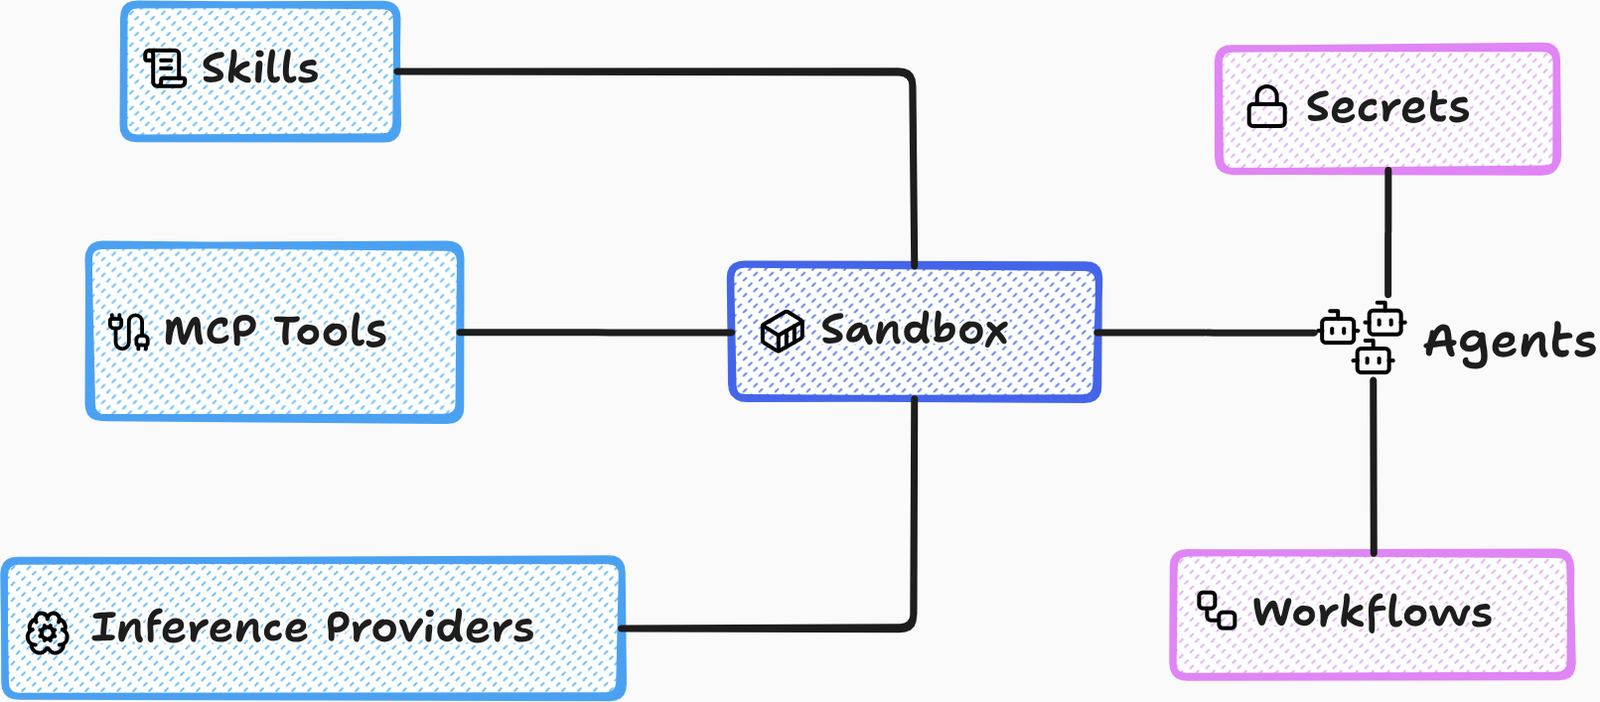 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.
 rootdirective-sec/cve-2026-39987-lab
Local Docker lab reproducing CVE-2026-39987, a pre-auth RCE in marimo's terminal WebSocket. Compares vulnerable and patched versions with least-harm…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4