
EXPLOIT-CVE-2026-87902
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
container-securityeducationexploitation+6
joaovicdev/exploit-cve-2026-87902Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
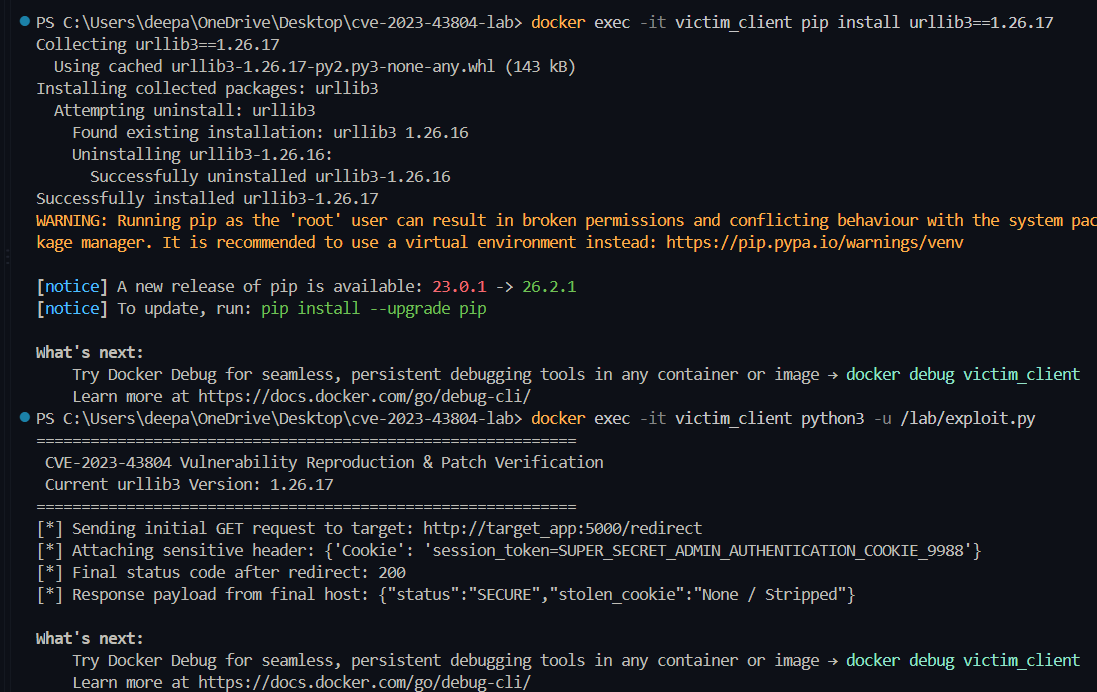 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 runewardd/runeward
Governed execution cells for AI agents.
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 slauger/cve-2026-31431
Analysis and mitigation guide for CVE-2026-31431, a Linux kernel local privilege escalation in the crypto algif_aead subsystem, with impact…
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 makitos666/cve-2026-31431-copy-fail-detection-toolkit
Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 devstuff/harden-docker-seccomp
Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 boreas37/cve-2026-58455-poc
PoC for CVE-2026-58455: Dockwatch <=0.6.567 unauthenticated RCE. Stdlib-only Python.
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems