

grype
 anchore/grype
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
anchore/grypeA vulnerability scanner for container images and filesystems
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 agppp/cve-2019-5736-poc
getshell test
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 fahmifj/docker-breakout-runc
Modified version of CVE-2019-5736-PoC by Frichetten
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 mrchucu1/cve-2022-0847-docker
Docker exploit
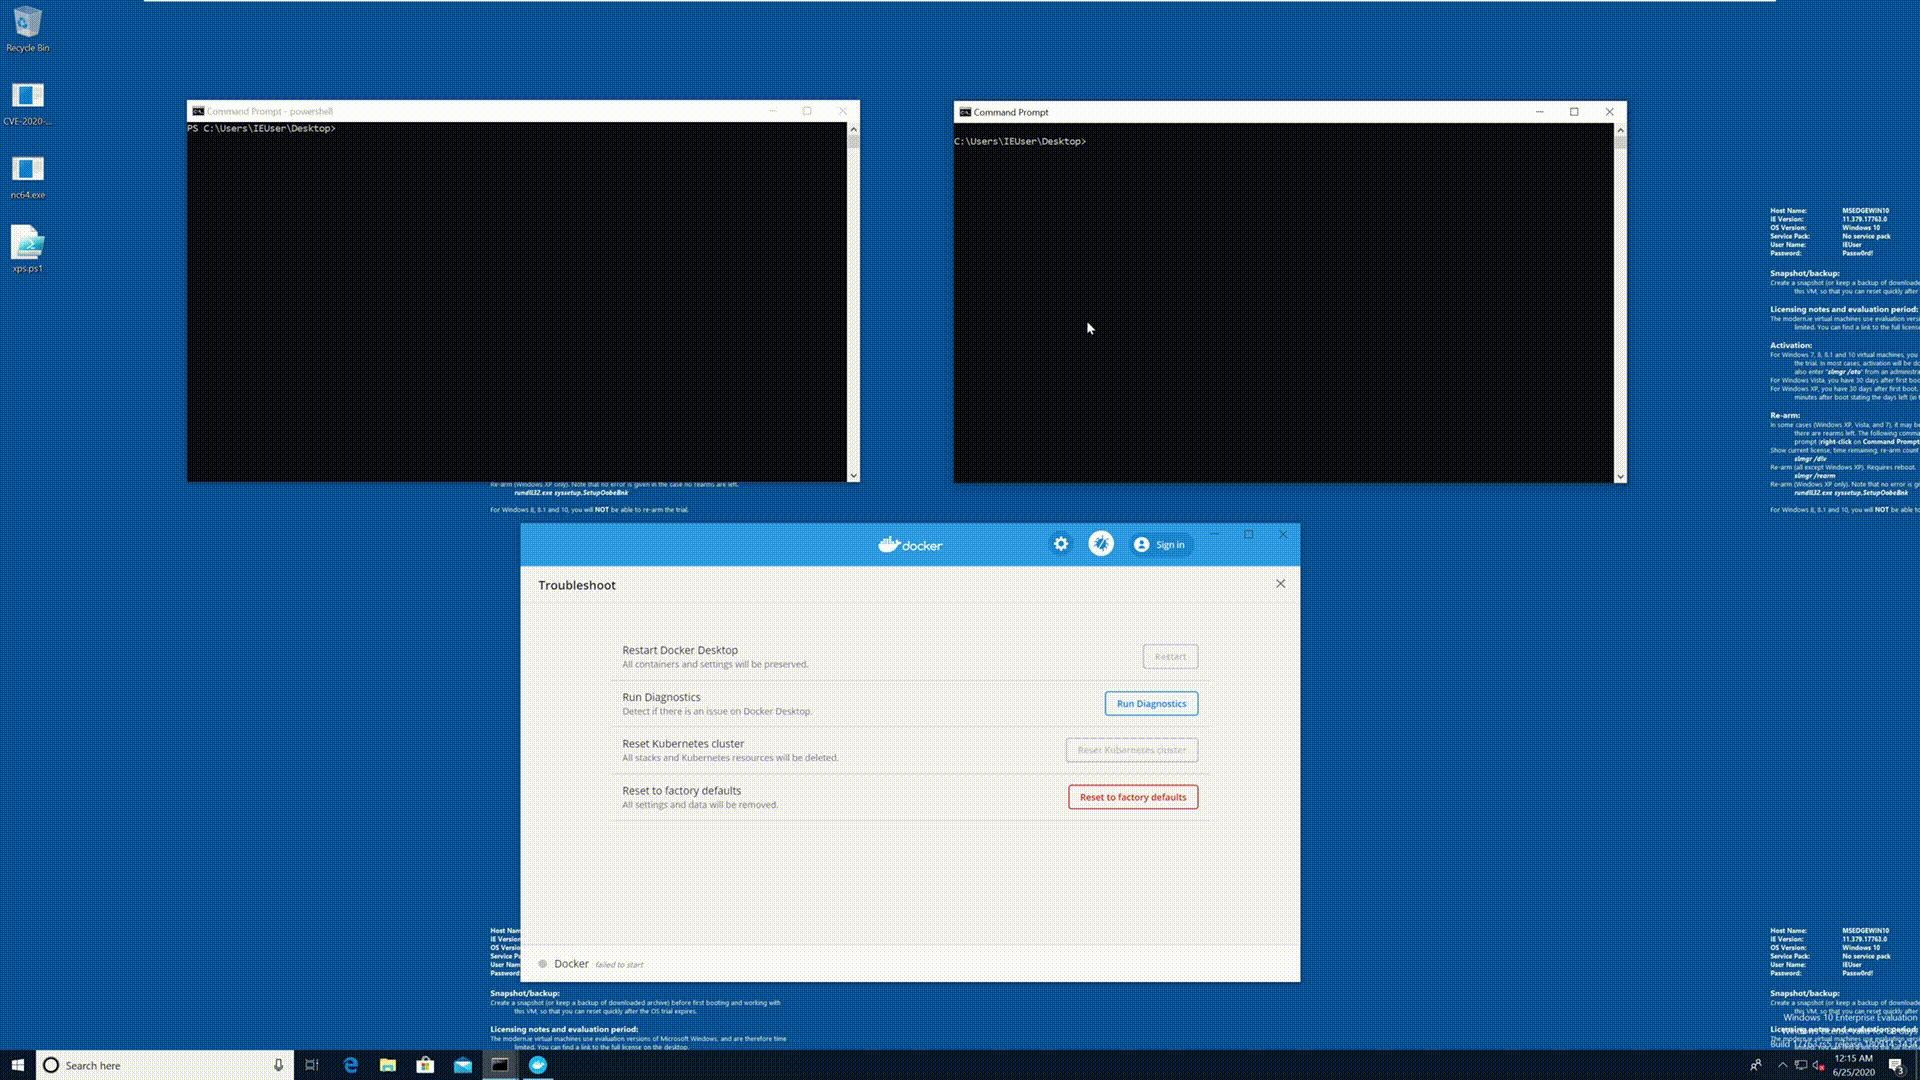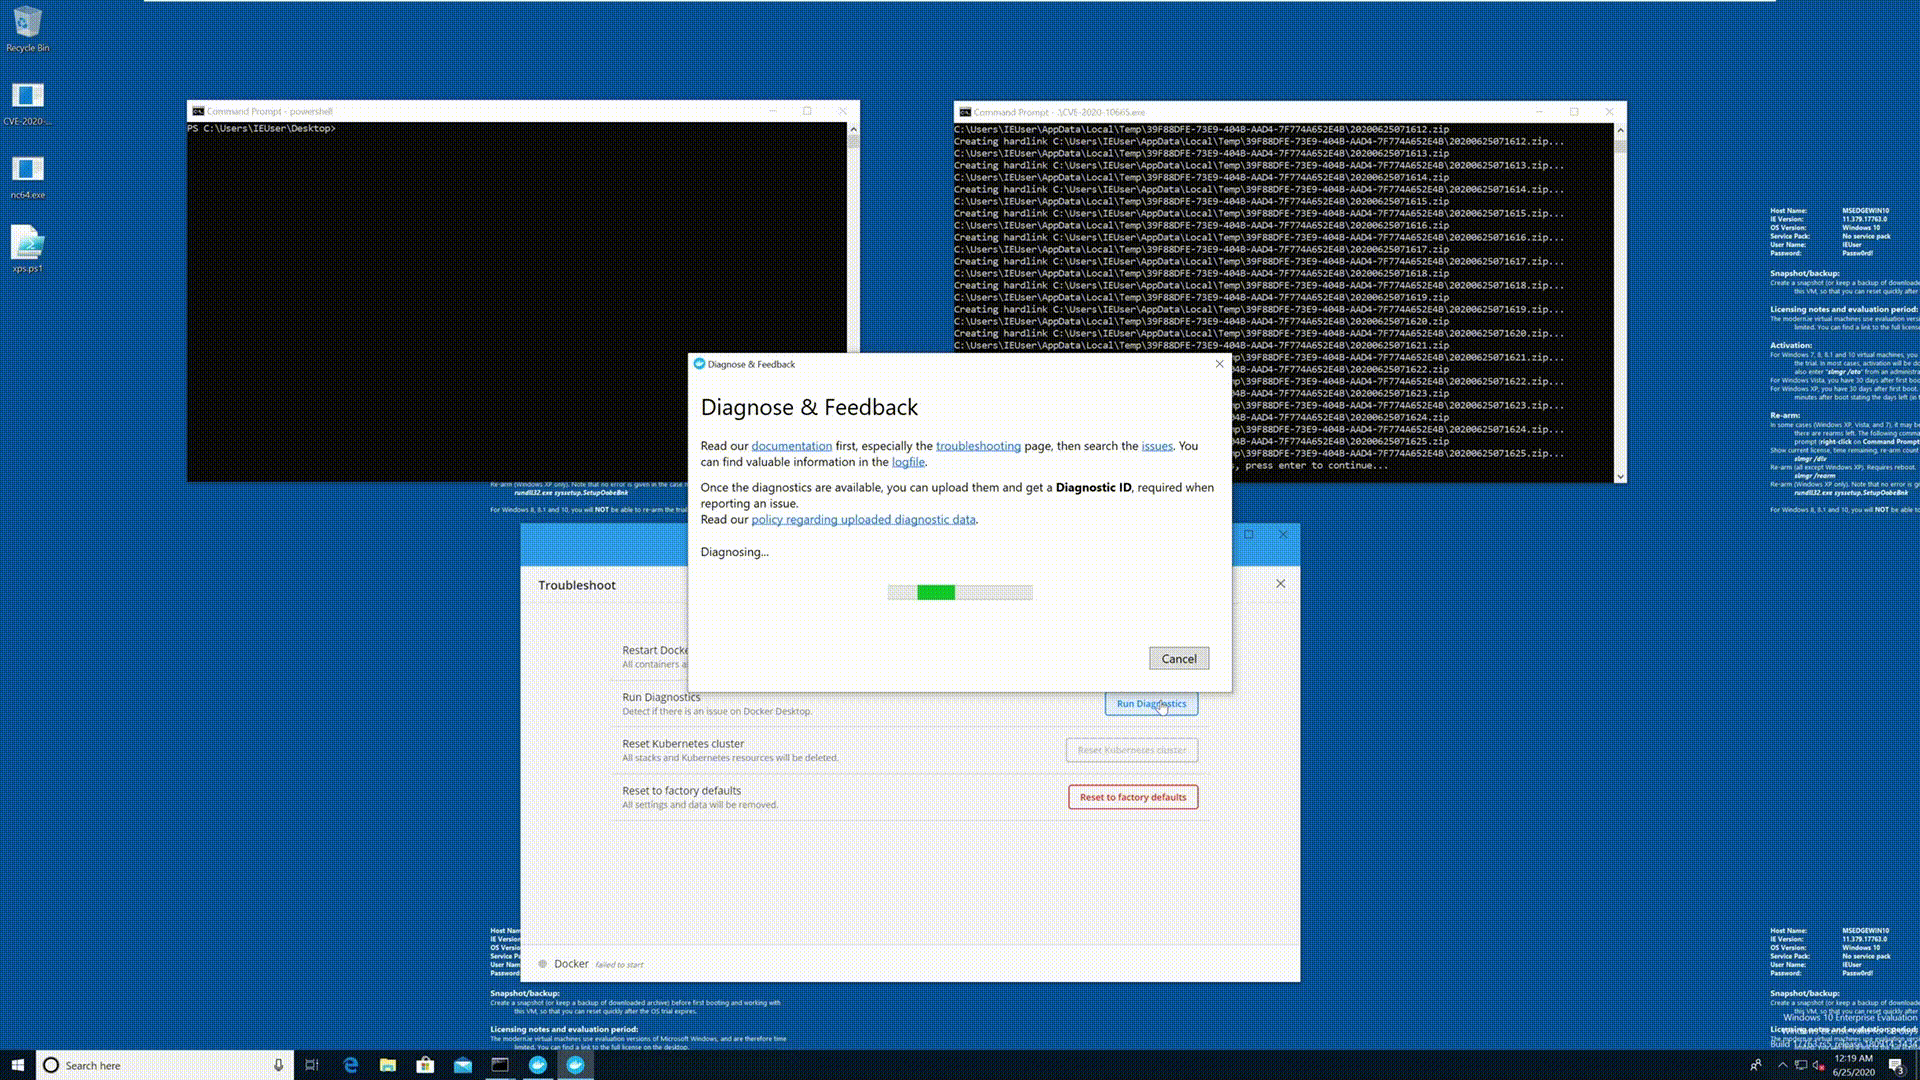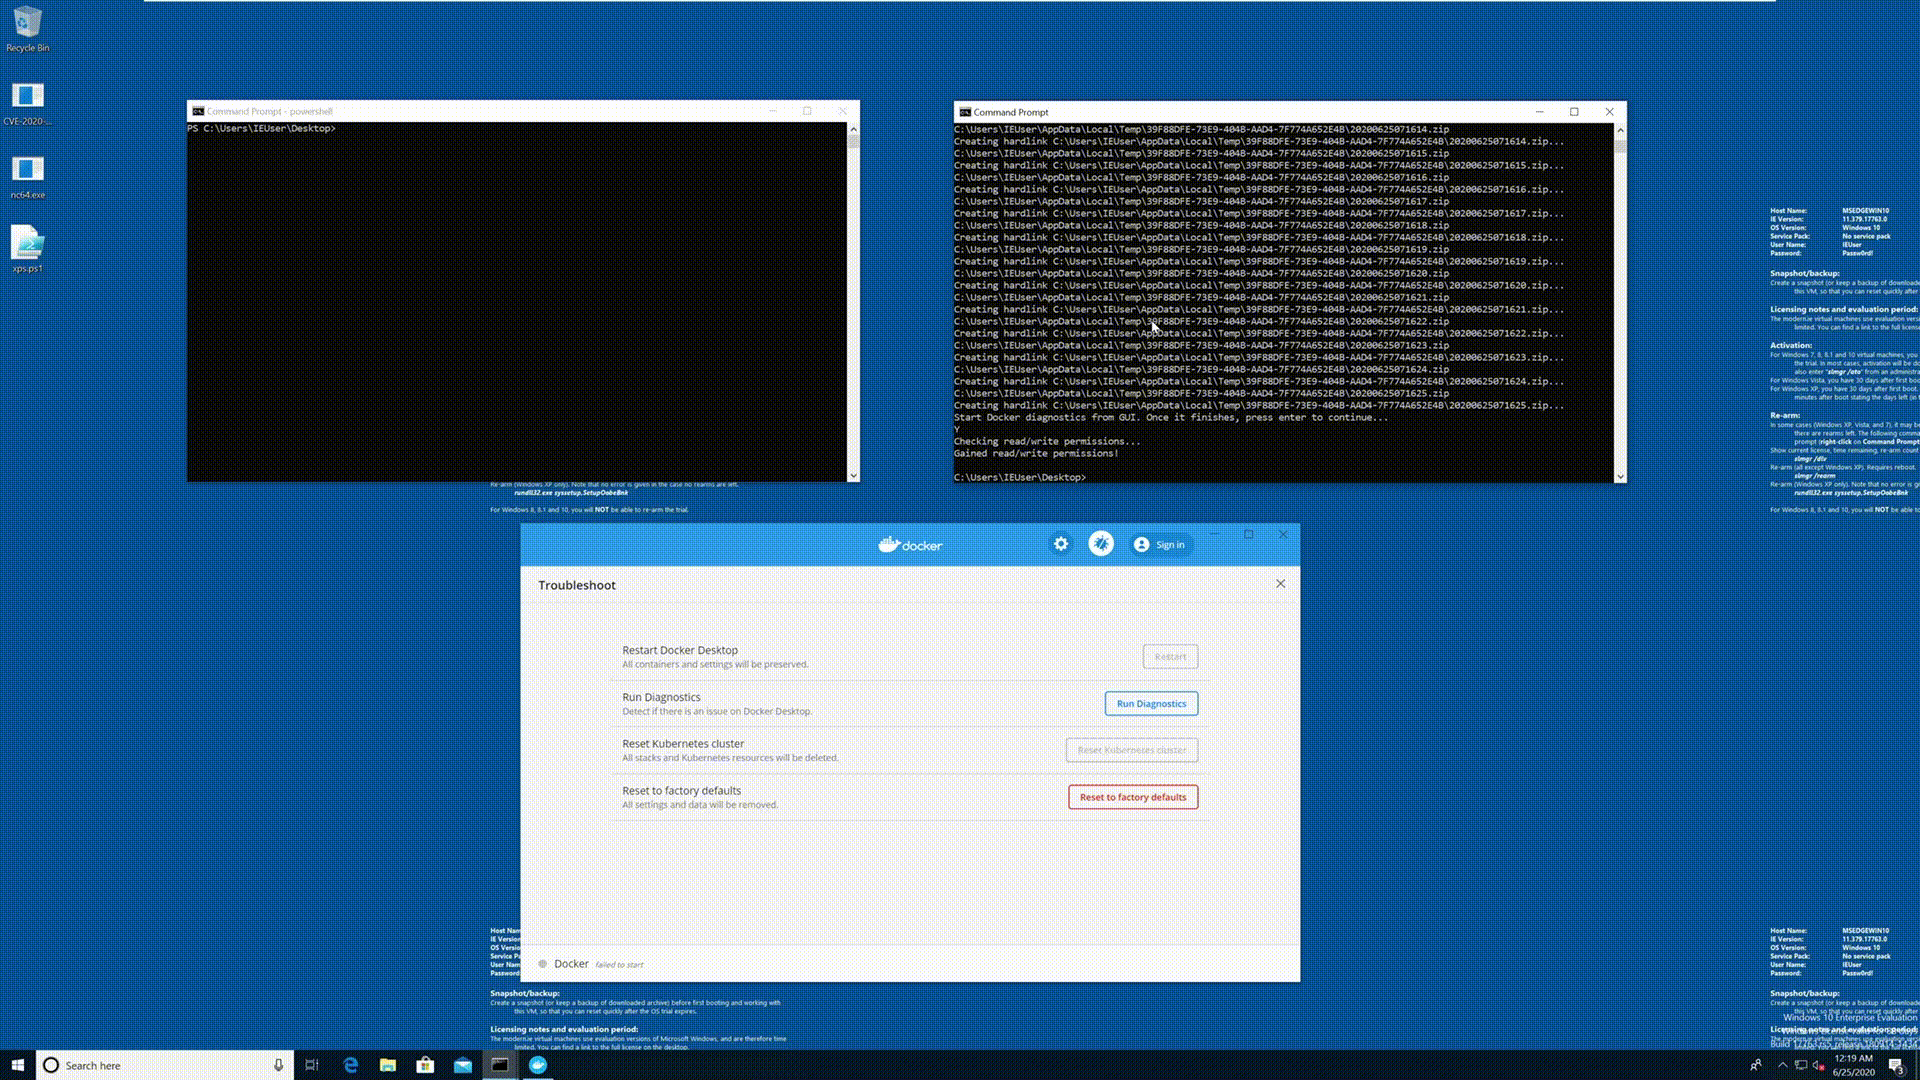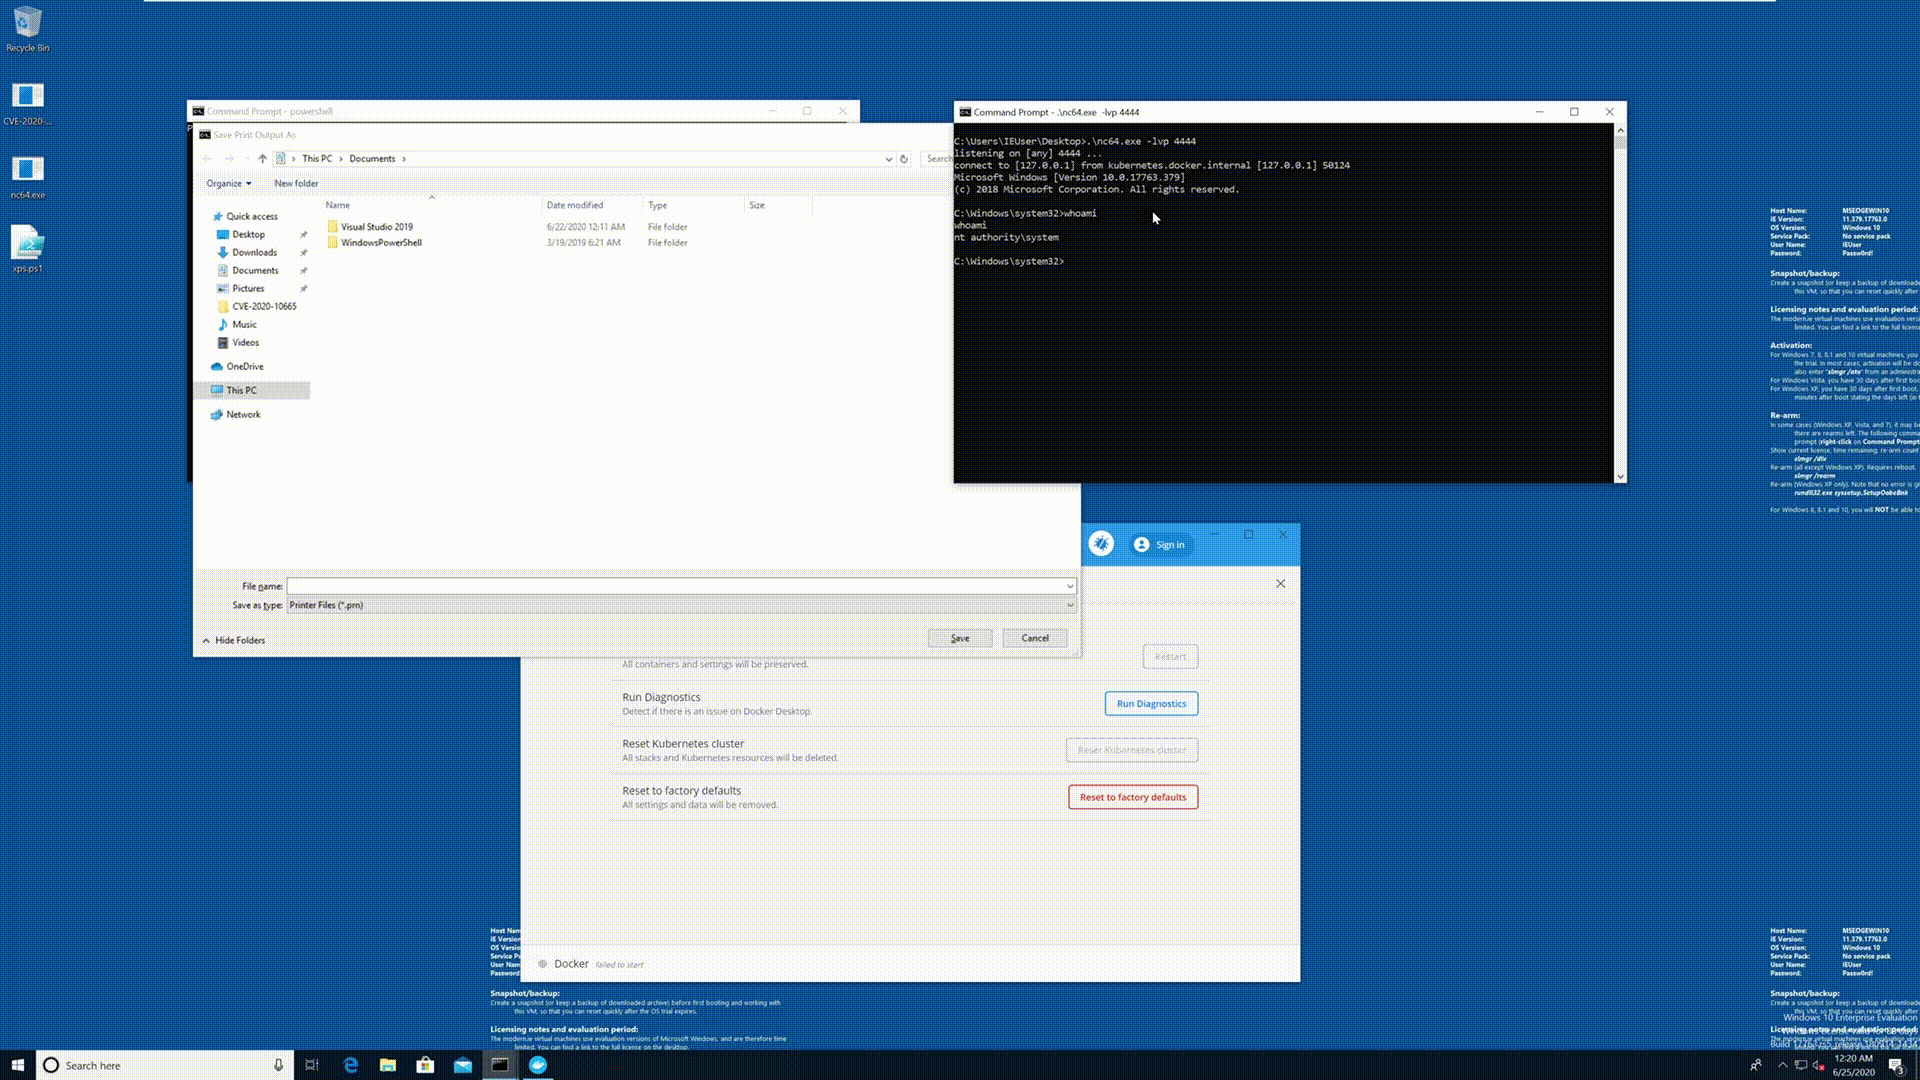 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
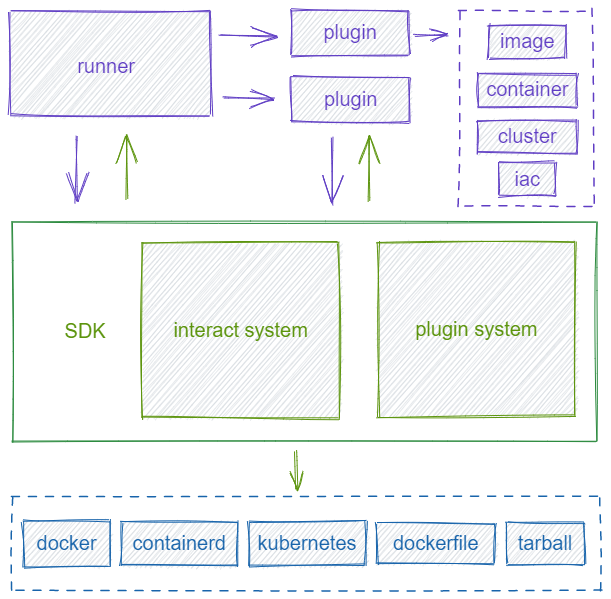 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.