

kubernetes-goat
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
cloud-securitycontainer-escapecontainer-security+4
5.8k
madhuakula/kubernetes-goatIntentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 owasp/owasp-ctf
Self-hosted CTF control plane for security-learning events: team registration, live leaderboard, and patch-to-score, quiz, jeopardy, and AI challenge…
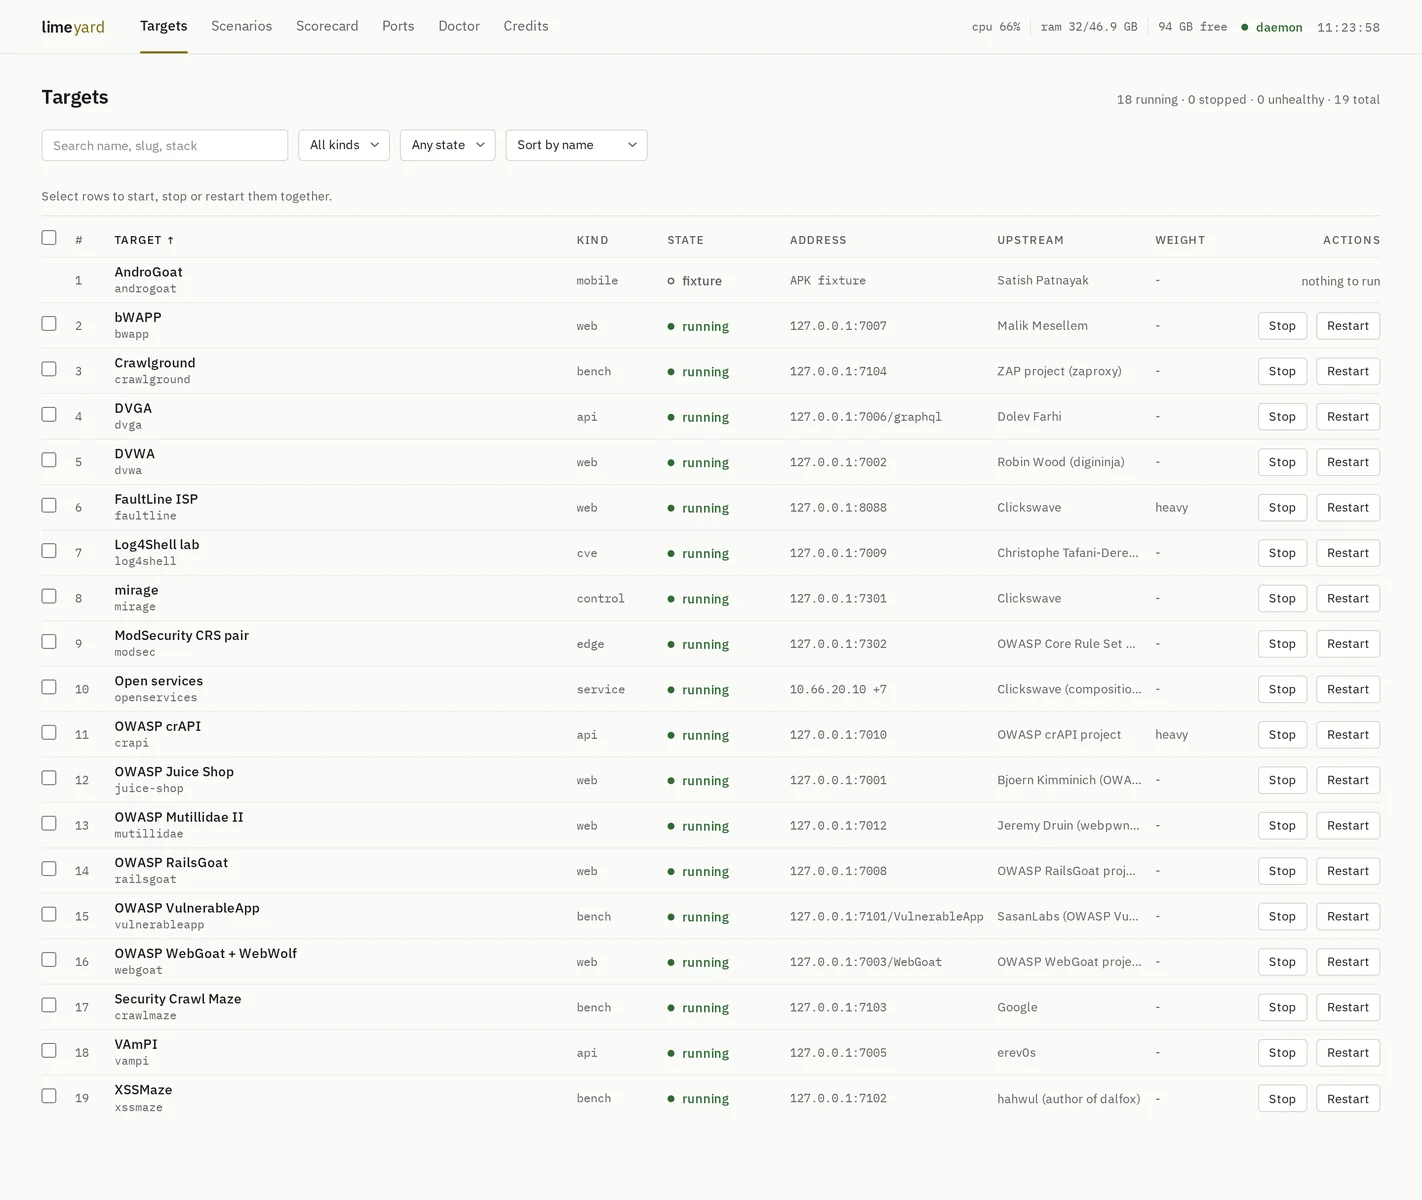 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 owasp/docker-security
Getting a handle on container security
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…