

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.3k1 day ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 anchore/grype
A vulnerability scanner for container images and filesystems
 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 paradigmxyz/iron-proxy
An egress firewall for untrusted workloads.
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 cilium/cilium
eBPF-based Networking, Security, and Observability
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 seanrickerd/cve-2024-53677
Vulnerable Environment and Exploit for CVE-2024-53677
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
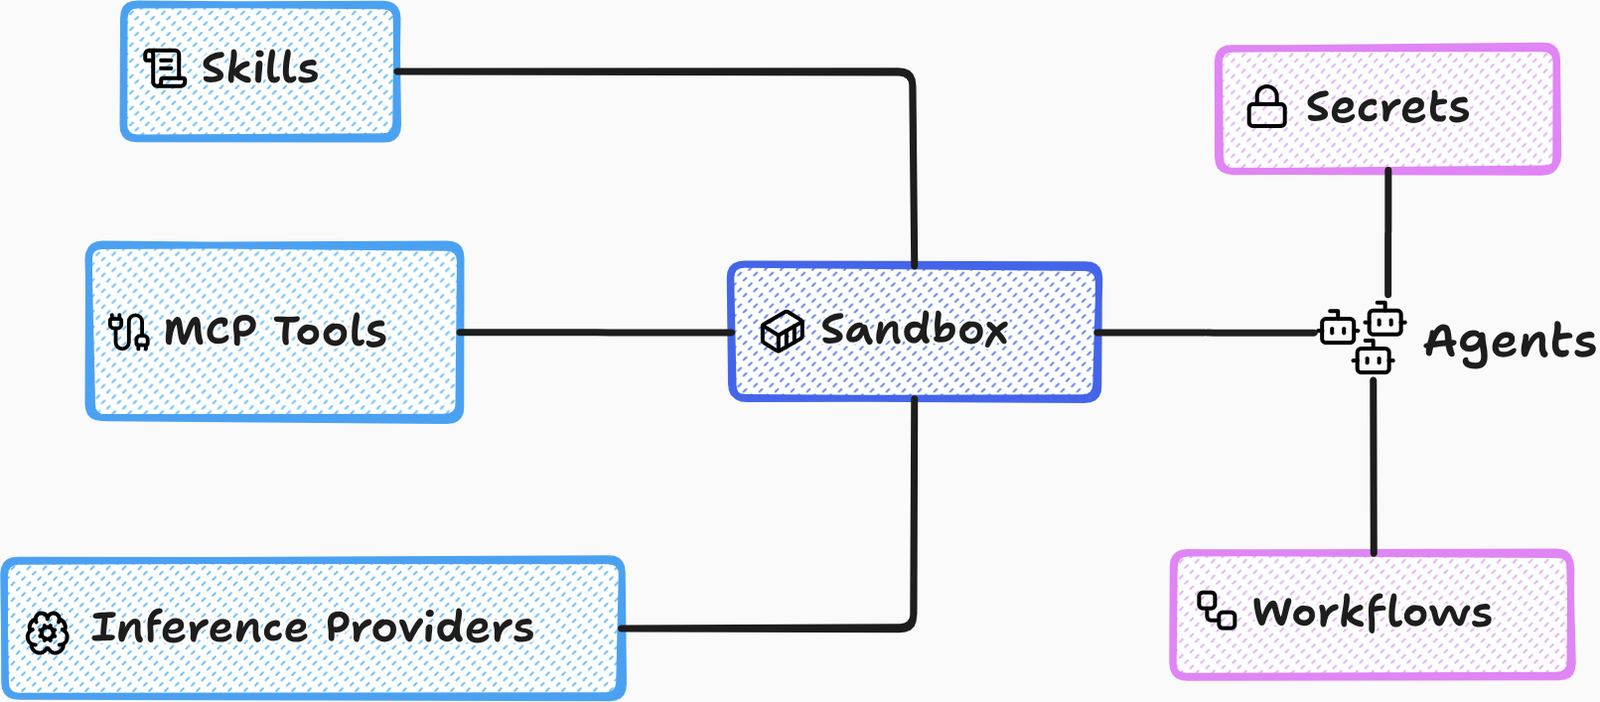 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.