
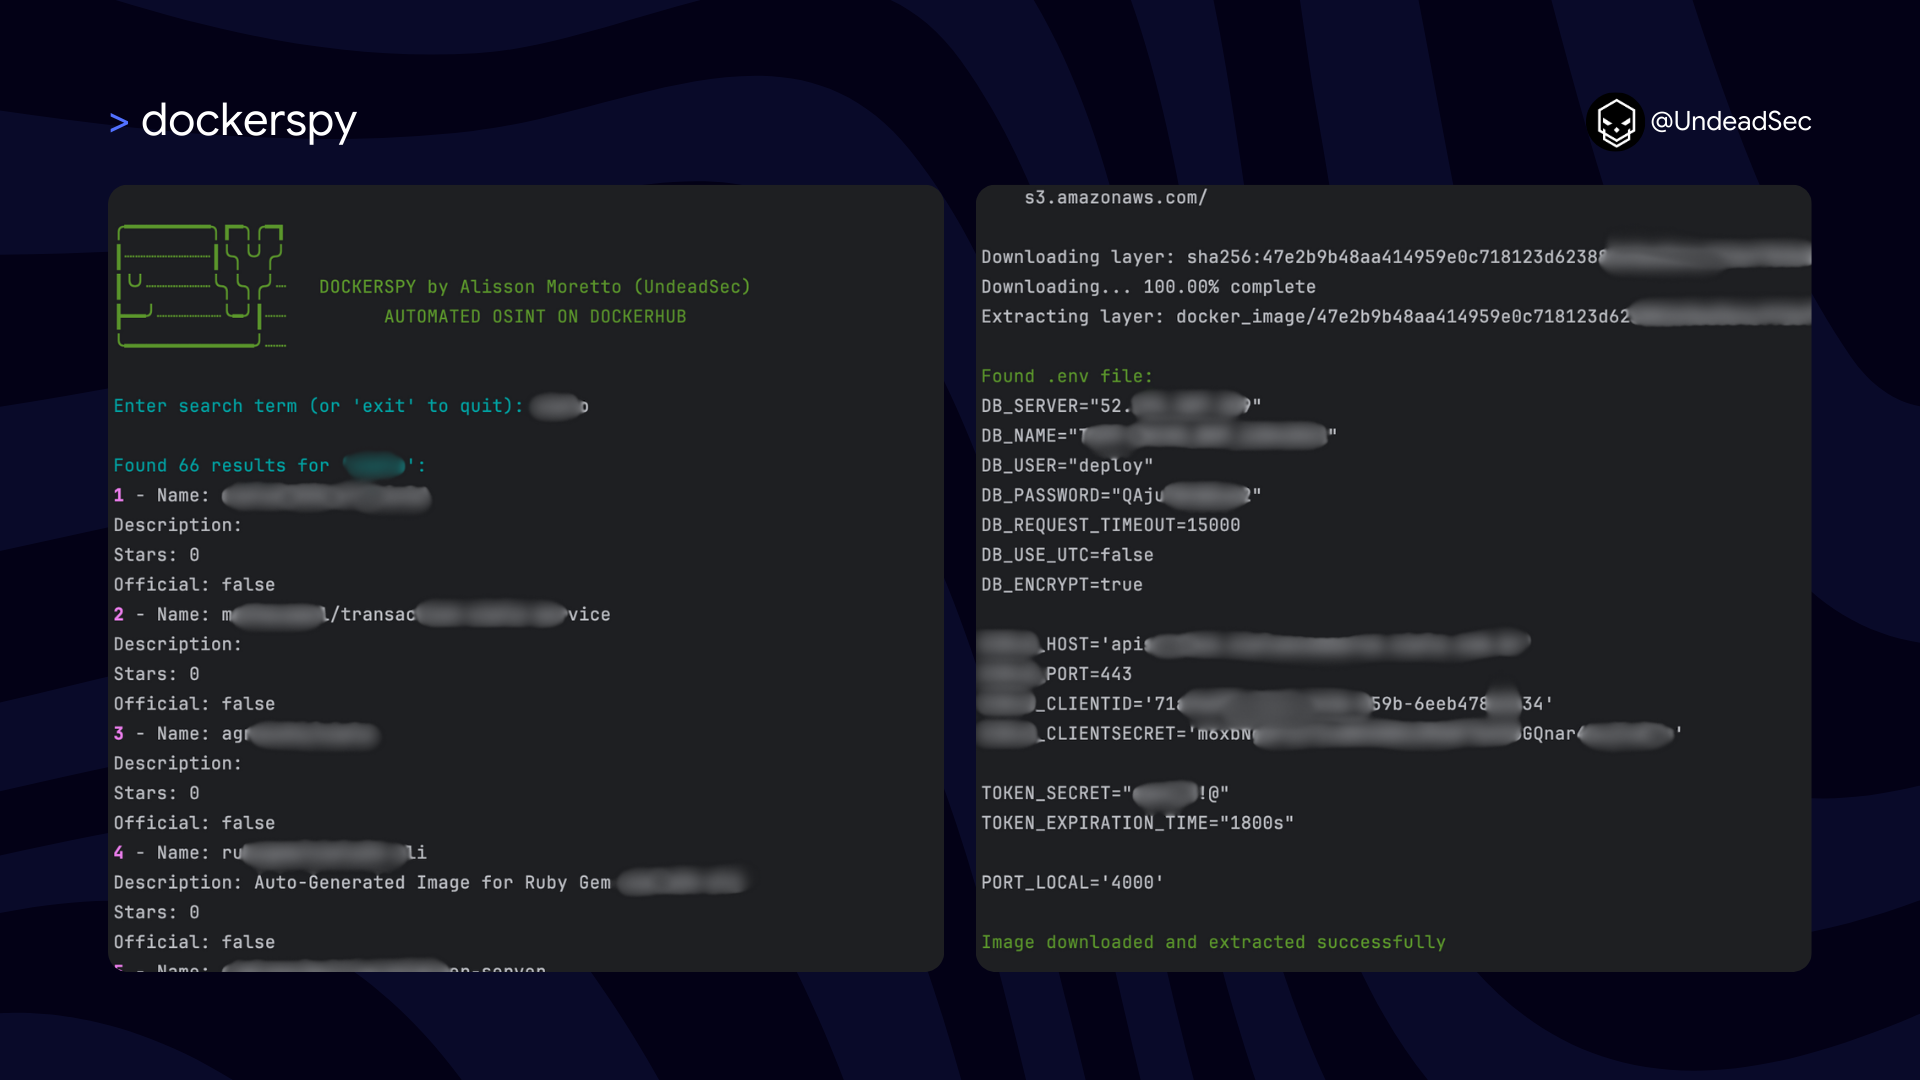
DockerSpy
 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
container-securityinformation-gatheringosint+1
248
undeadsec/dockerspyScans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 target/strelka
Real-time, container-based file scanning at enterprise scale
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…