
beelzebub
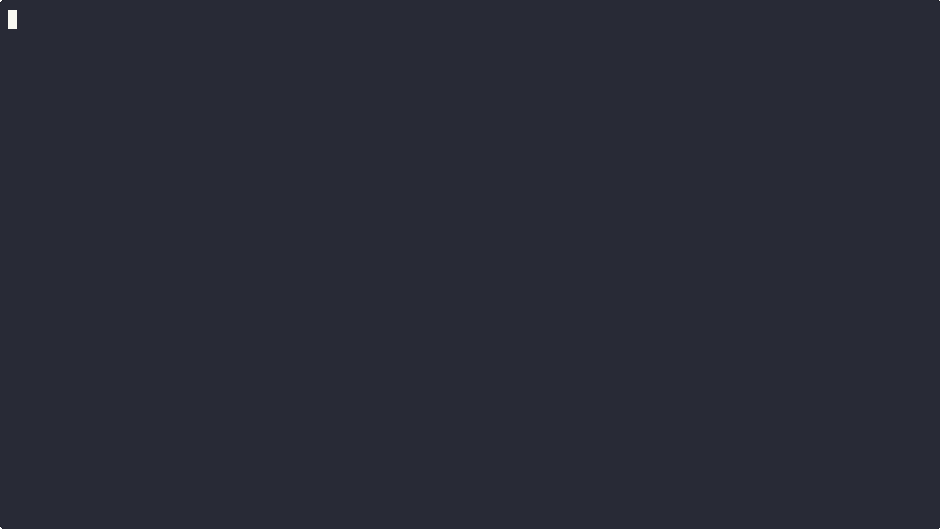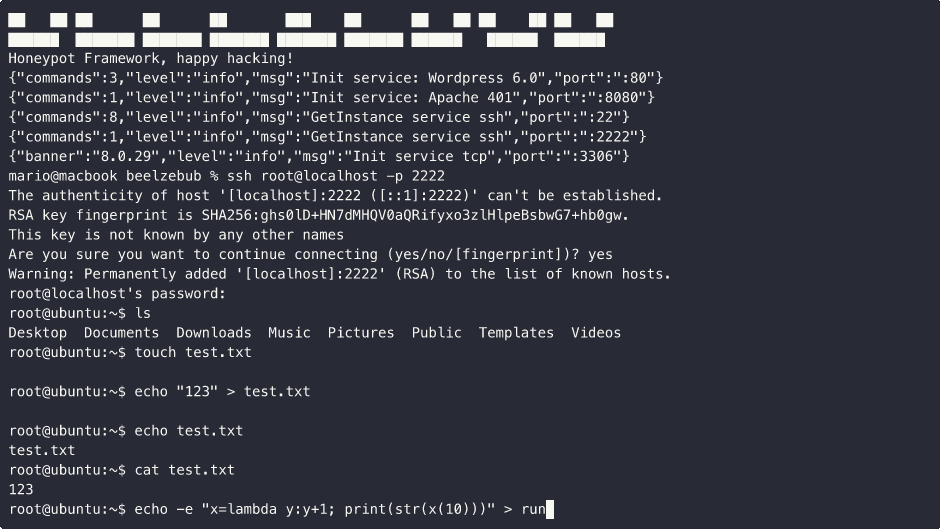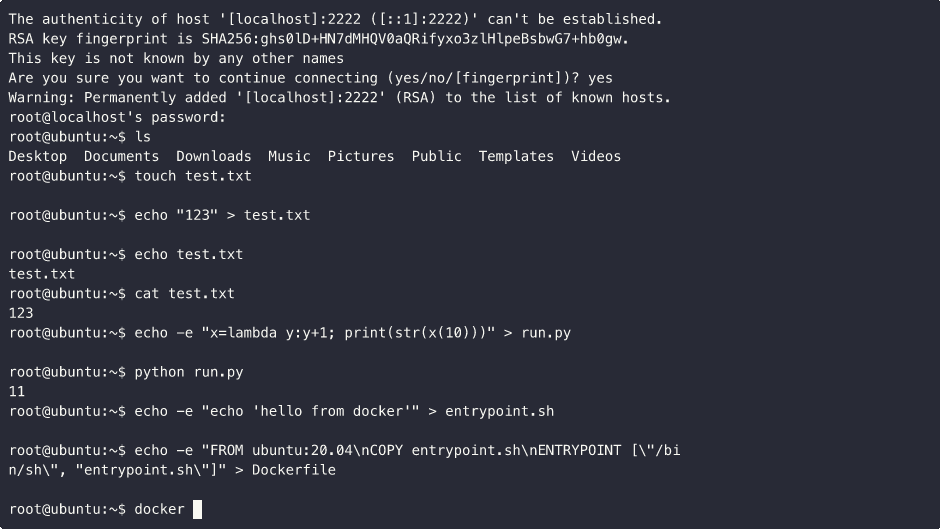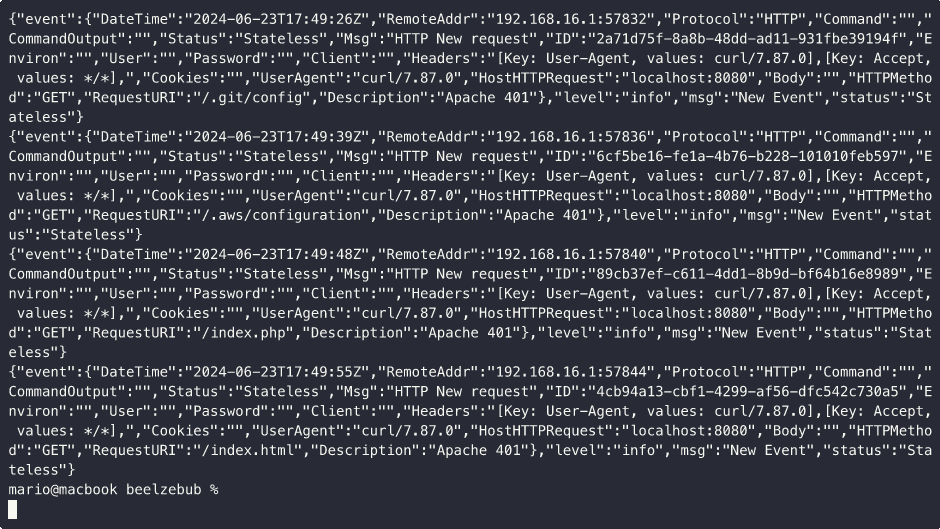
 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
ai-securityapi-securitycontainer-security+7
2.2k
beelzebub-labs/beelzebubA secure low code deception runtime framework, leveraging AI for System Virtualization.
 cyberharsh/shellbash-cve-2014-6271
Docker-based lab environment for exploiting Shellshock (CVE-2014-6271) via CGI scripts, demonstrating remote command injection through crafted HTTP…
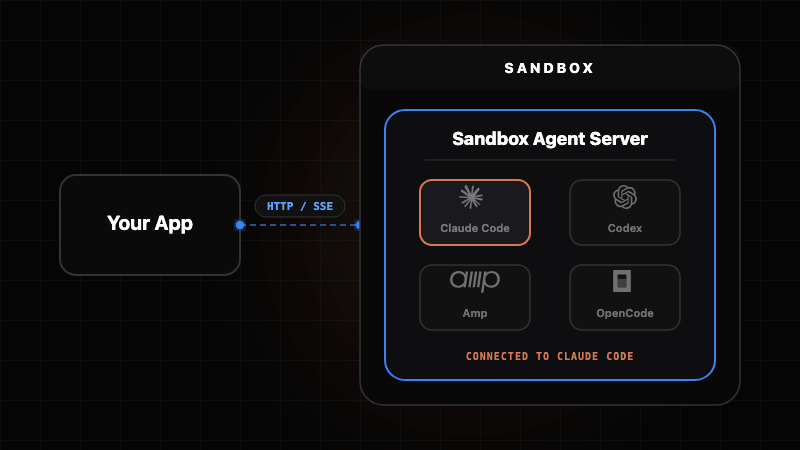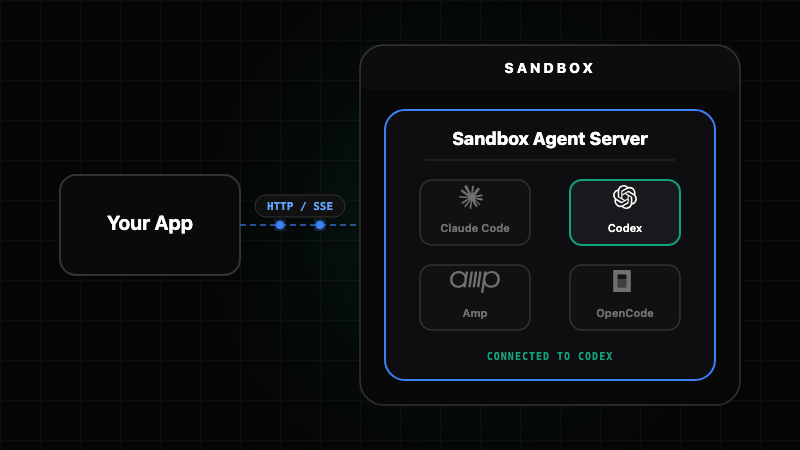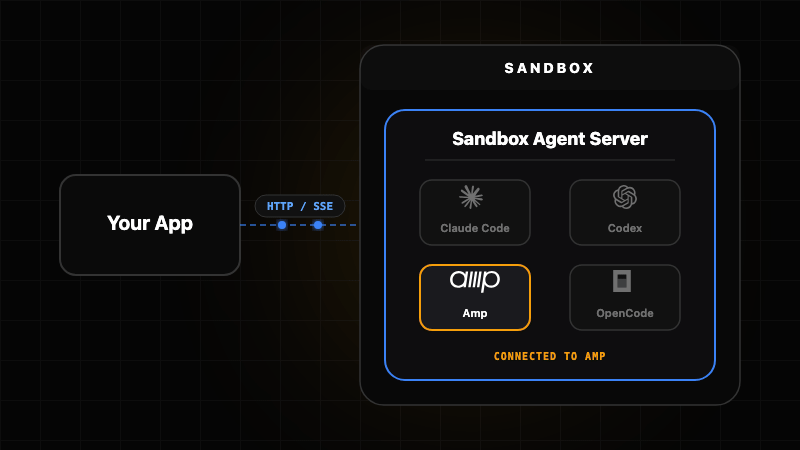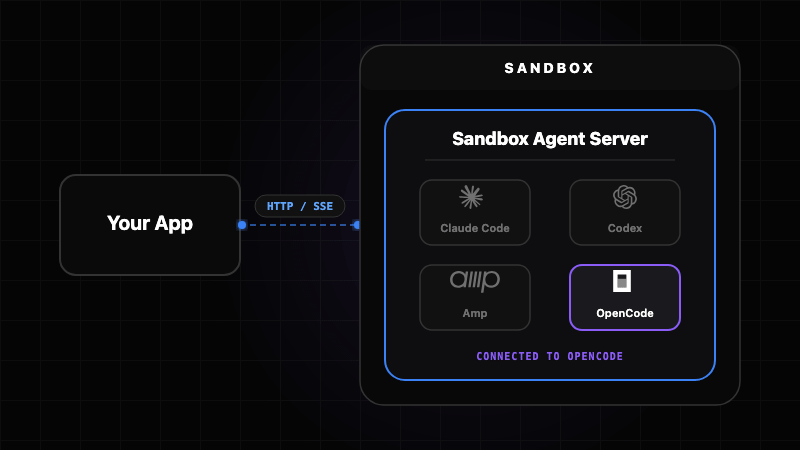 rivet-dev/sandbox-agent
Run Coding Agents in Sandboxes. Control Them Over HTTP. Supports Claude Code, Codex, OpenCode, and Amp.
 michaelsanford/log4shell-honeypot
Dockerized honeypot for CVE-2021-44228.
 axelcurmi/log4shell-docker-lab
Log4Shell (CVE-2021-44228) docker lab
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 12345qwert123456/cve-2021-42013
Vulnerable configuration Apache HTTP Server version 2.4.49/2.4.50
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 layarkacasiber/cve-2021-41773
Docker-based lab environment for CVE-2021-41773 (Apache HTTP Server 2.4.49) path traversal and RCE exploitation with step-by-step setup instructions.
 berraesen/apache-cve-2021-42013-lab
Docker ortamında Apache HTTP Server 2.4.49 (CVE-2021-42013) zafiyetinin gösterildiği laboratuvar çalışması.
 al0ne/linuxcheck
Linux应急处置/信息搜集/漏洞检测工具,支持基础配置/网络流量/任务计划/环境变量/用户信息/Services/bash/恶意文件/内核Rootkit/SSH/Webshell/挖矿文件/挖矿进程/供应链/服务器风险等13类70+项检查
 layarkacasiber/cve-2021-42013
Docker-based lab environment for exploiting CVE-2021-42013 (Apache HTTP Server path traversal and RCE) with step-by-step setup instructions for…
 hackarada/cve-2015-3306
Dockerized exploit environment for CVE-2015-3306 (ProFTPD copy_file_range) with FTP and HTTP services for penetration testing and vulnerability…
 12345qwert123456/cve-2021-41773
Vulnerable configuration Apache HTTP Server version 2.4.49
 b0b0haha/cve-2026-29955
Proof-of-concept for CVE-2026-29955, a command injection vulnerability in KubePlus kubeconfiggenerator allowing remote code execution and…
 dolby360/cve-2022-27518_poc
Proof-of-concept exploit for CVE-2022-27518 targeting Citrix ADC and Citrix CPX containers, demonstrating remote code execution via crafted HTTP…
 jas9reet/cve-2021-42013-lab
Docker-based lab environment for exploiting Apache HTTP Server 2.4.50 path traversal and RCE vulnerability (CVE-2021-42013) with automated exploit…