
cilium
 cilium/cilium
eBPF-based Networking, Security, and Observability
api-securitycloud-securitycontainer-security+2
cilium/ciliumeBPF-based Networking, Security, and Observability
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 seanrickerd/cve-2024-53677
Vulnerable Environment and Exploit for CVE-2024-53677
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
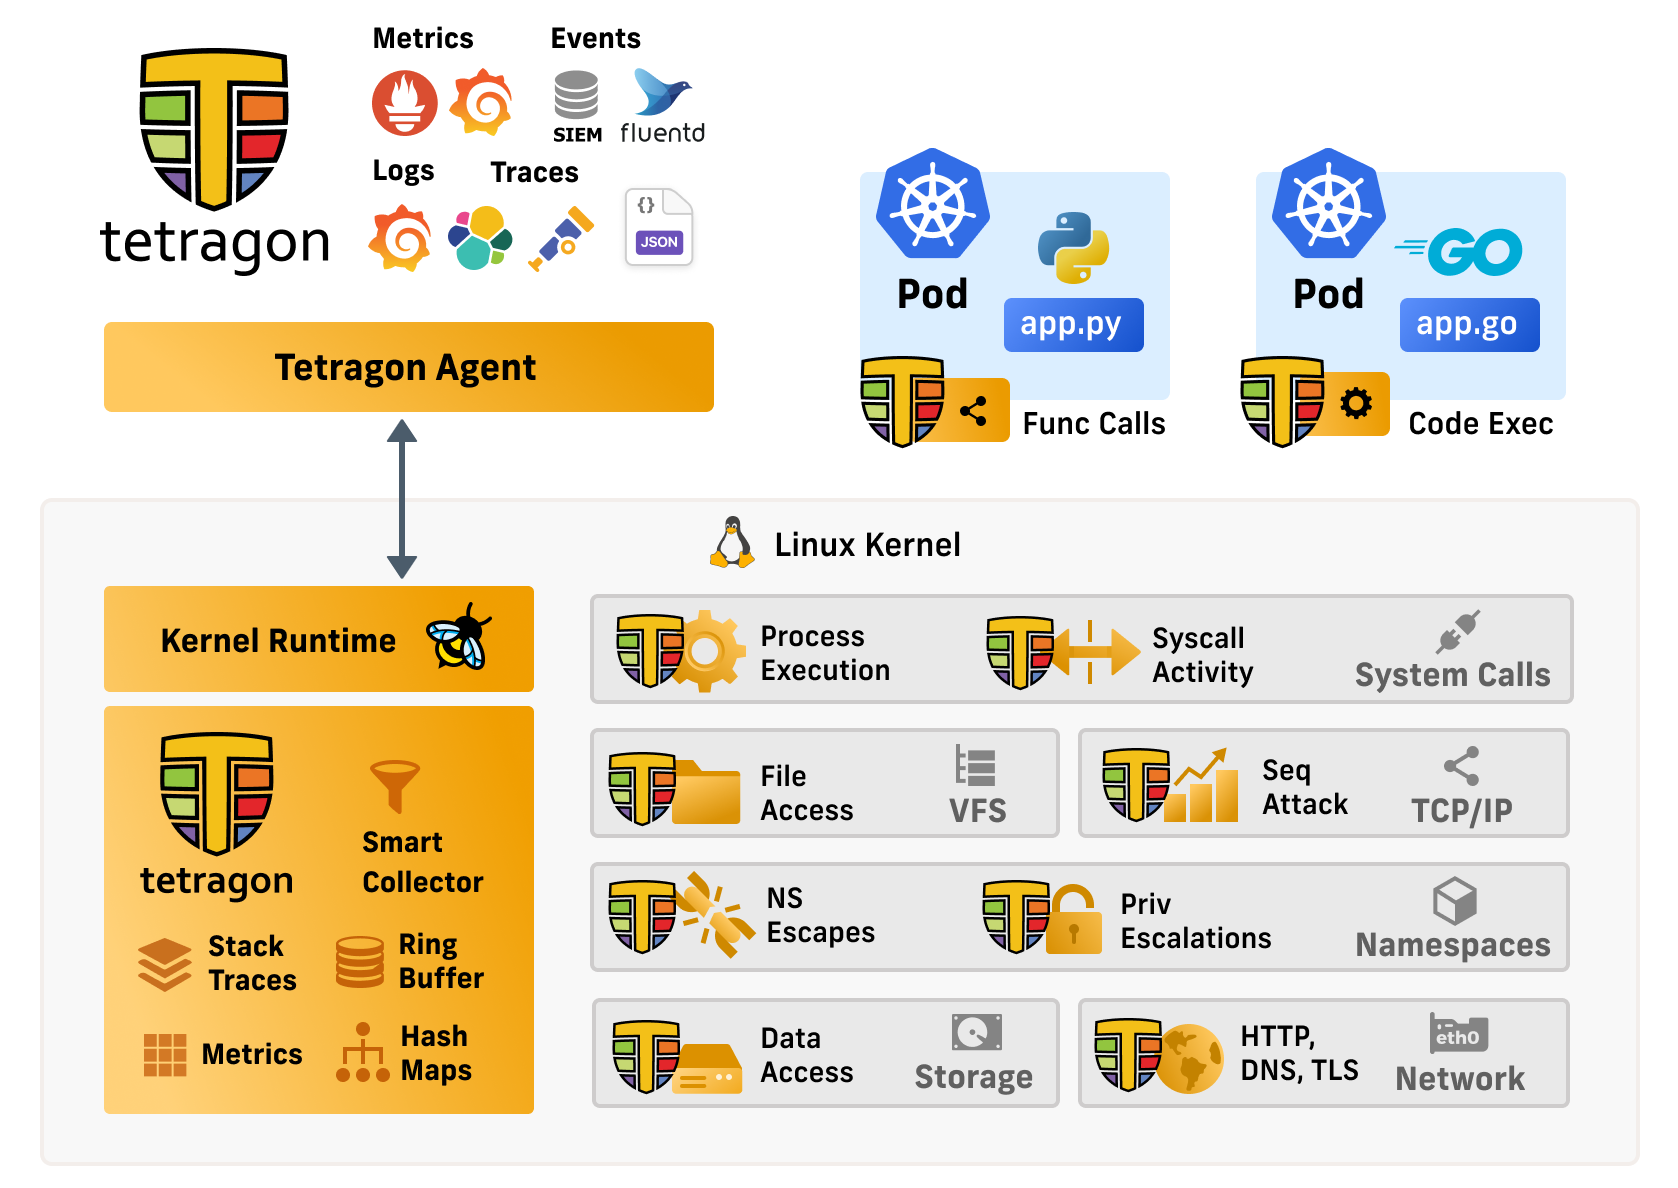 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 eeriedusk/nysm
eBPF-based stealth container that hides processes, sockets, eBPF objects, and audit logs from system monitoring tools, enabling covert…
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 project-oak/oak
Meaningful control of data in distributed systems.
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
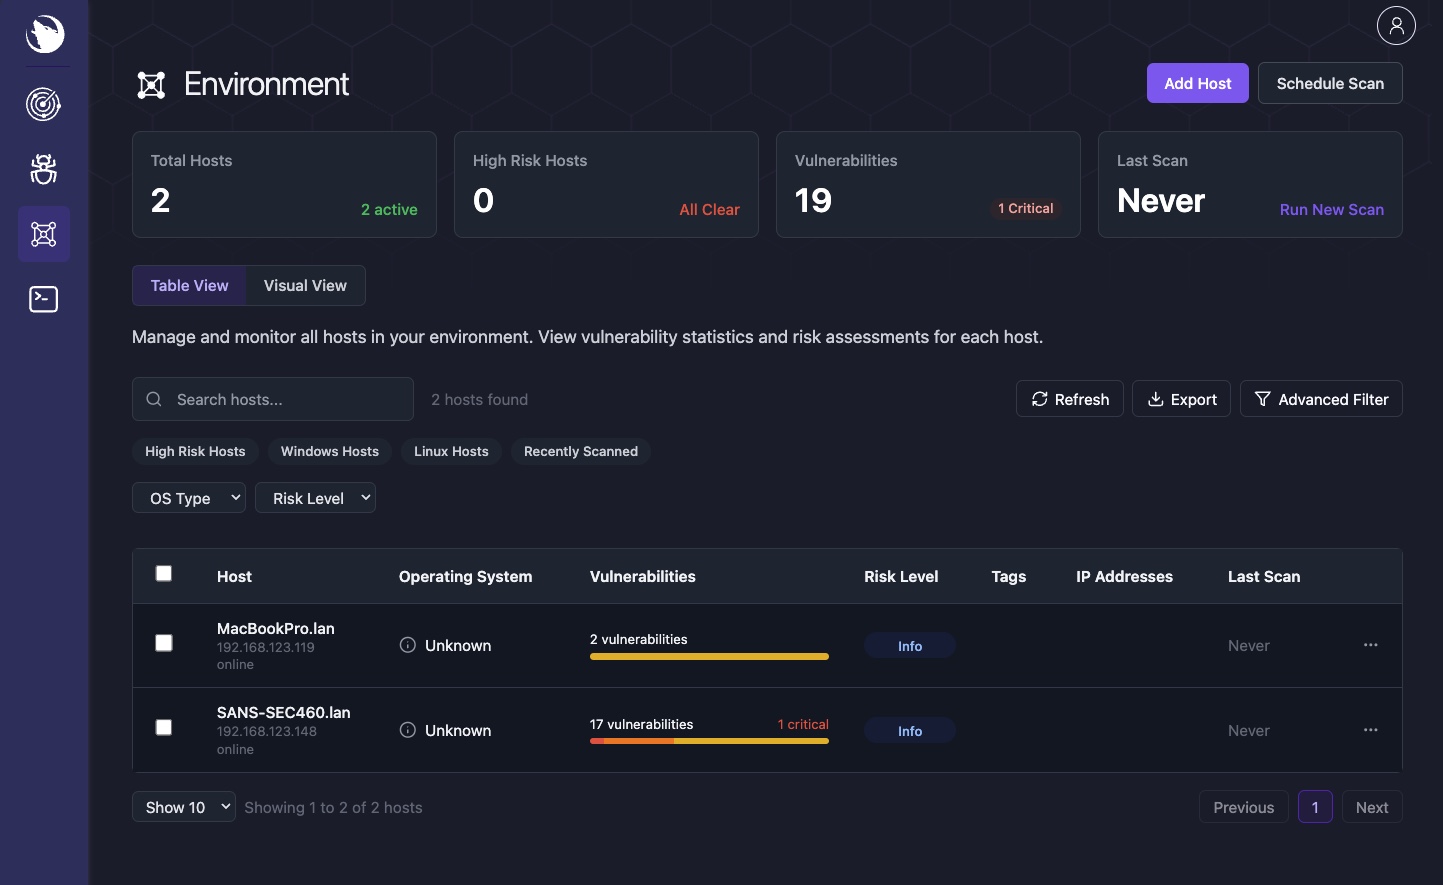 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
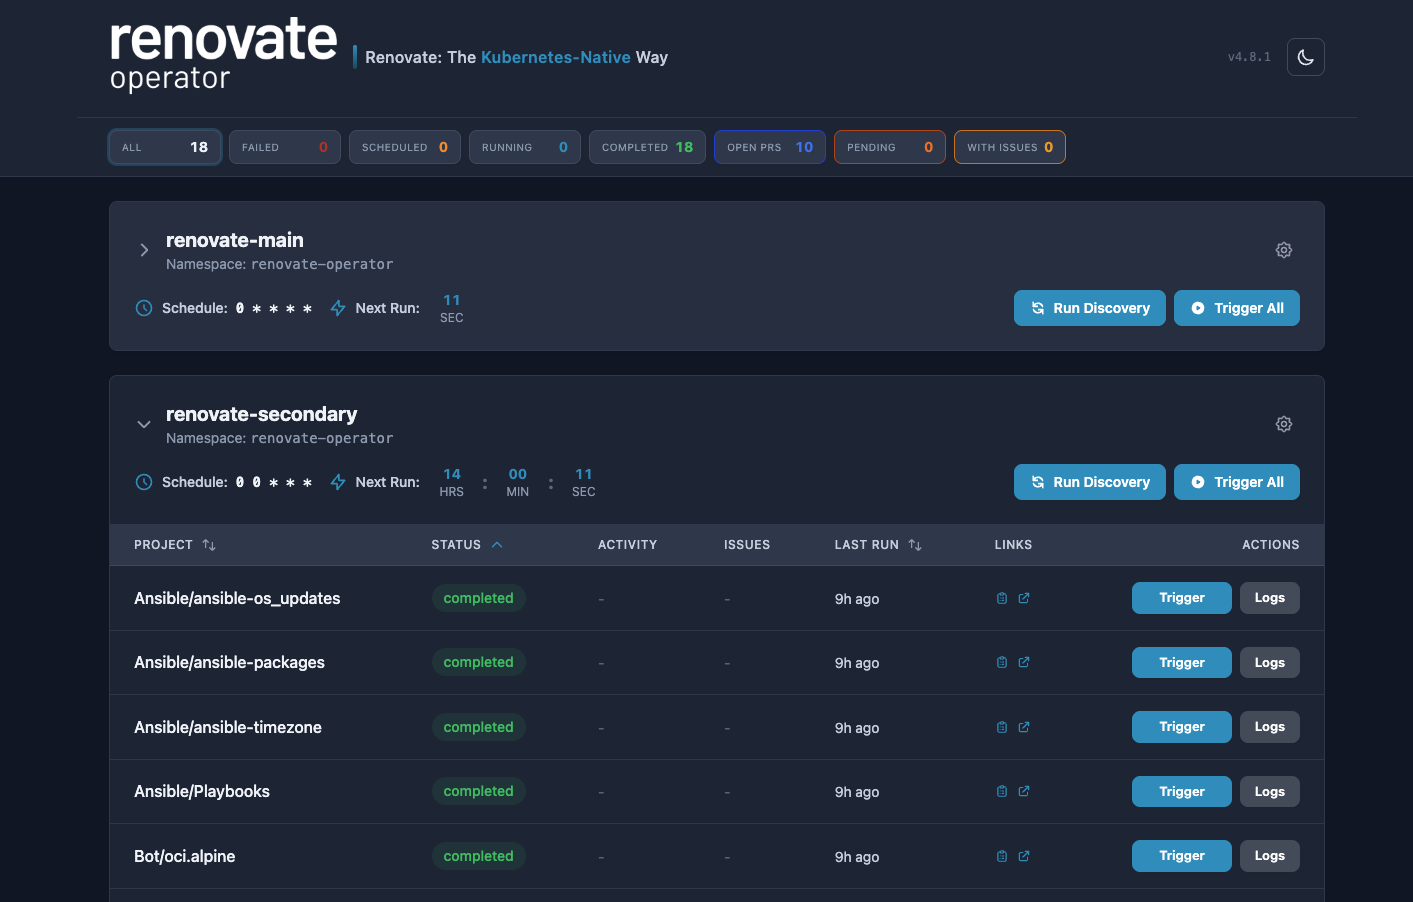 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
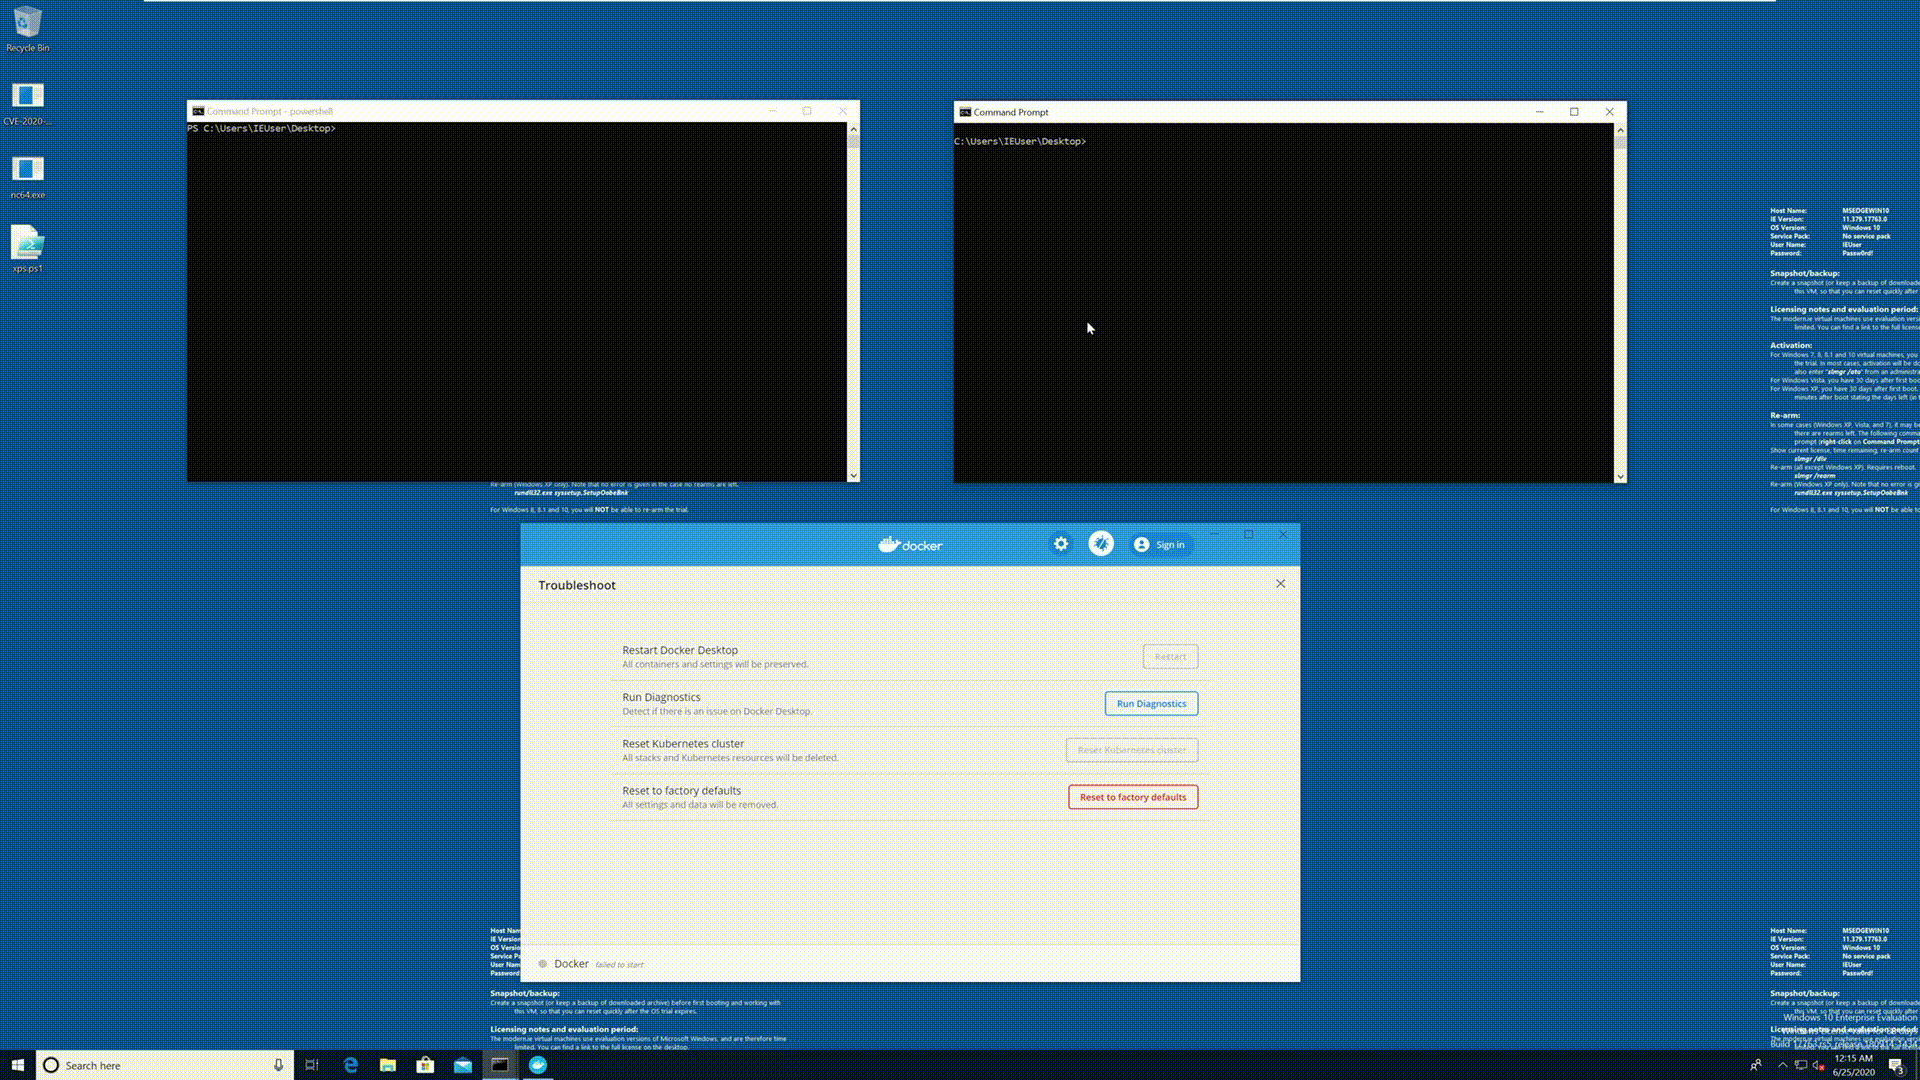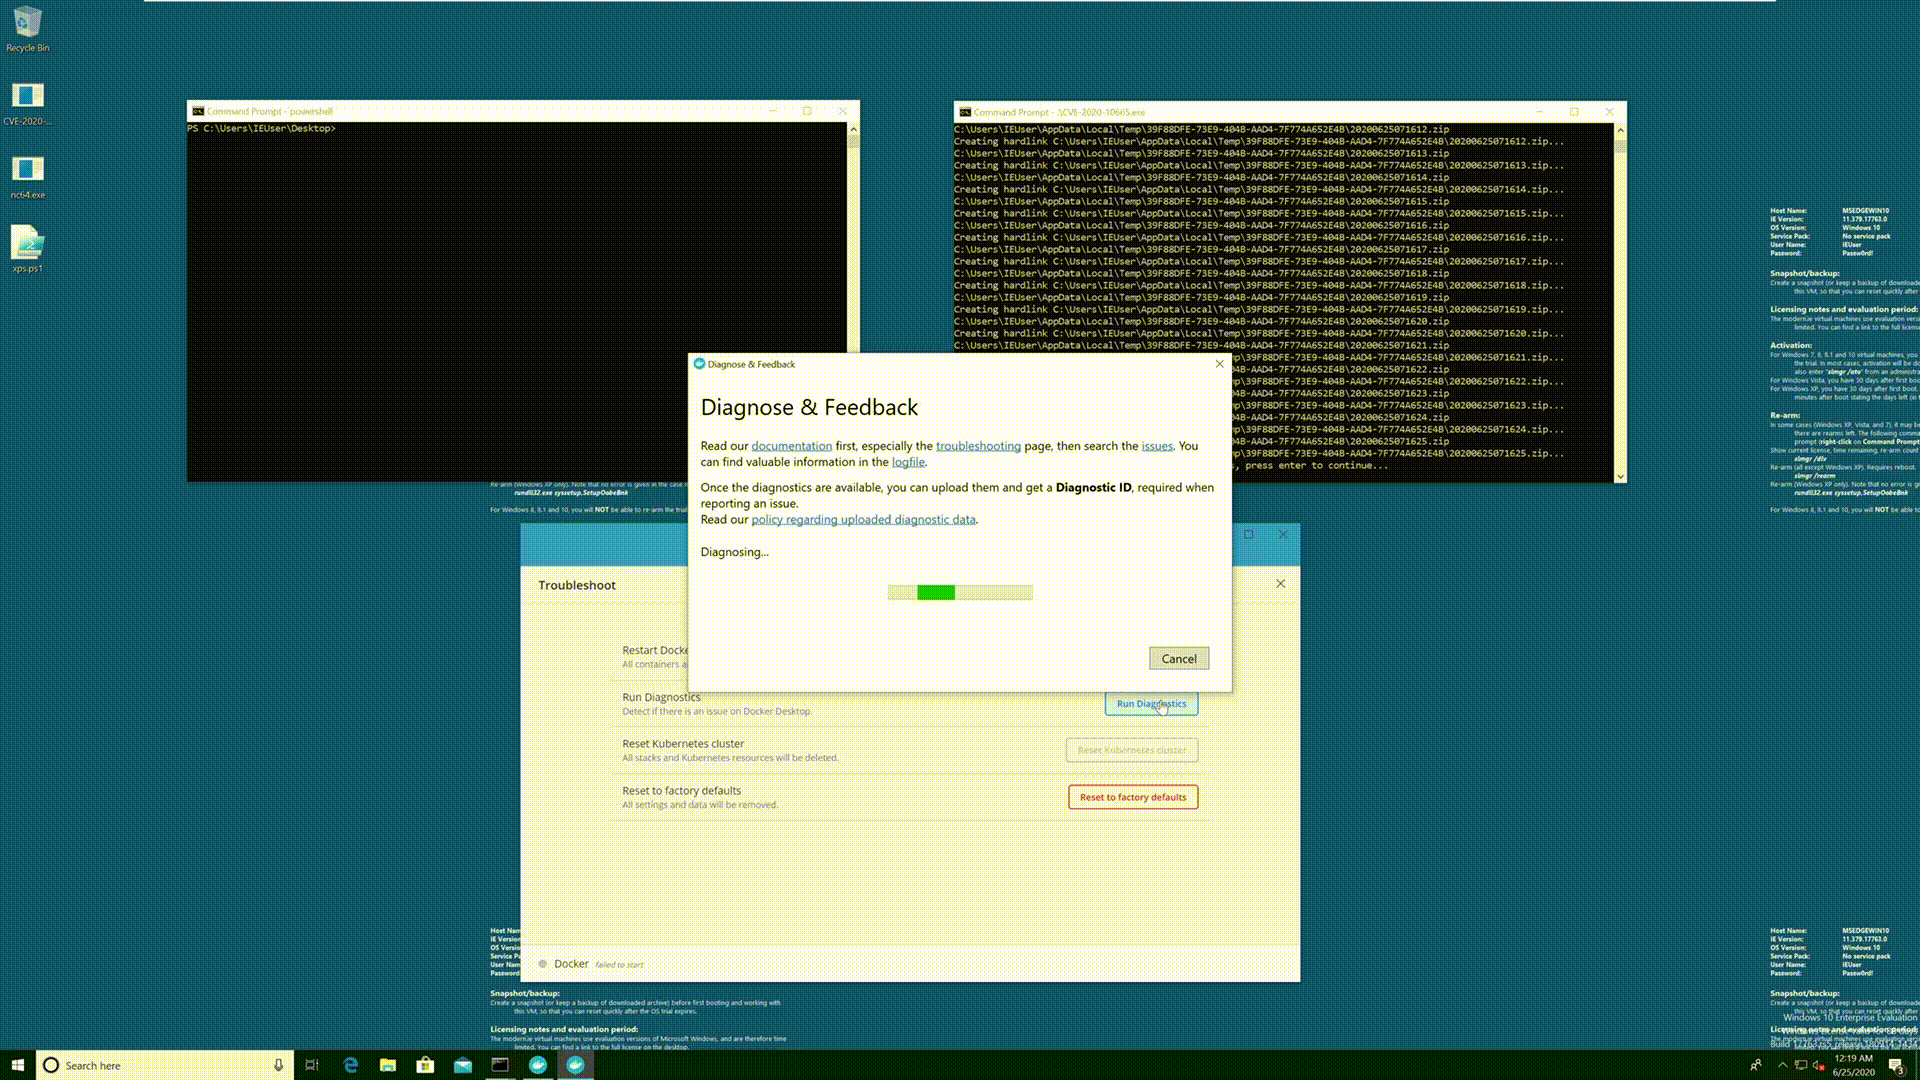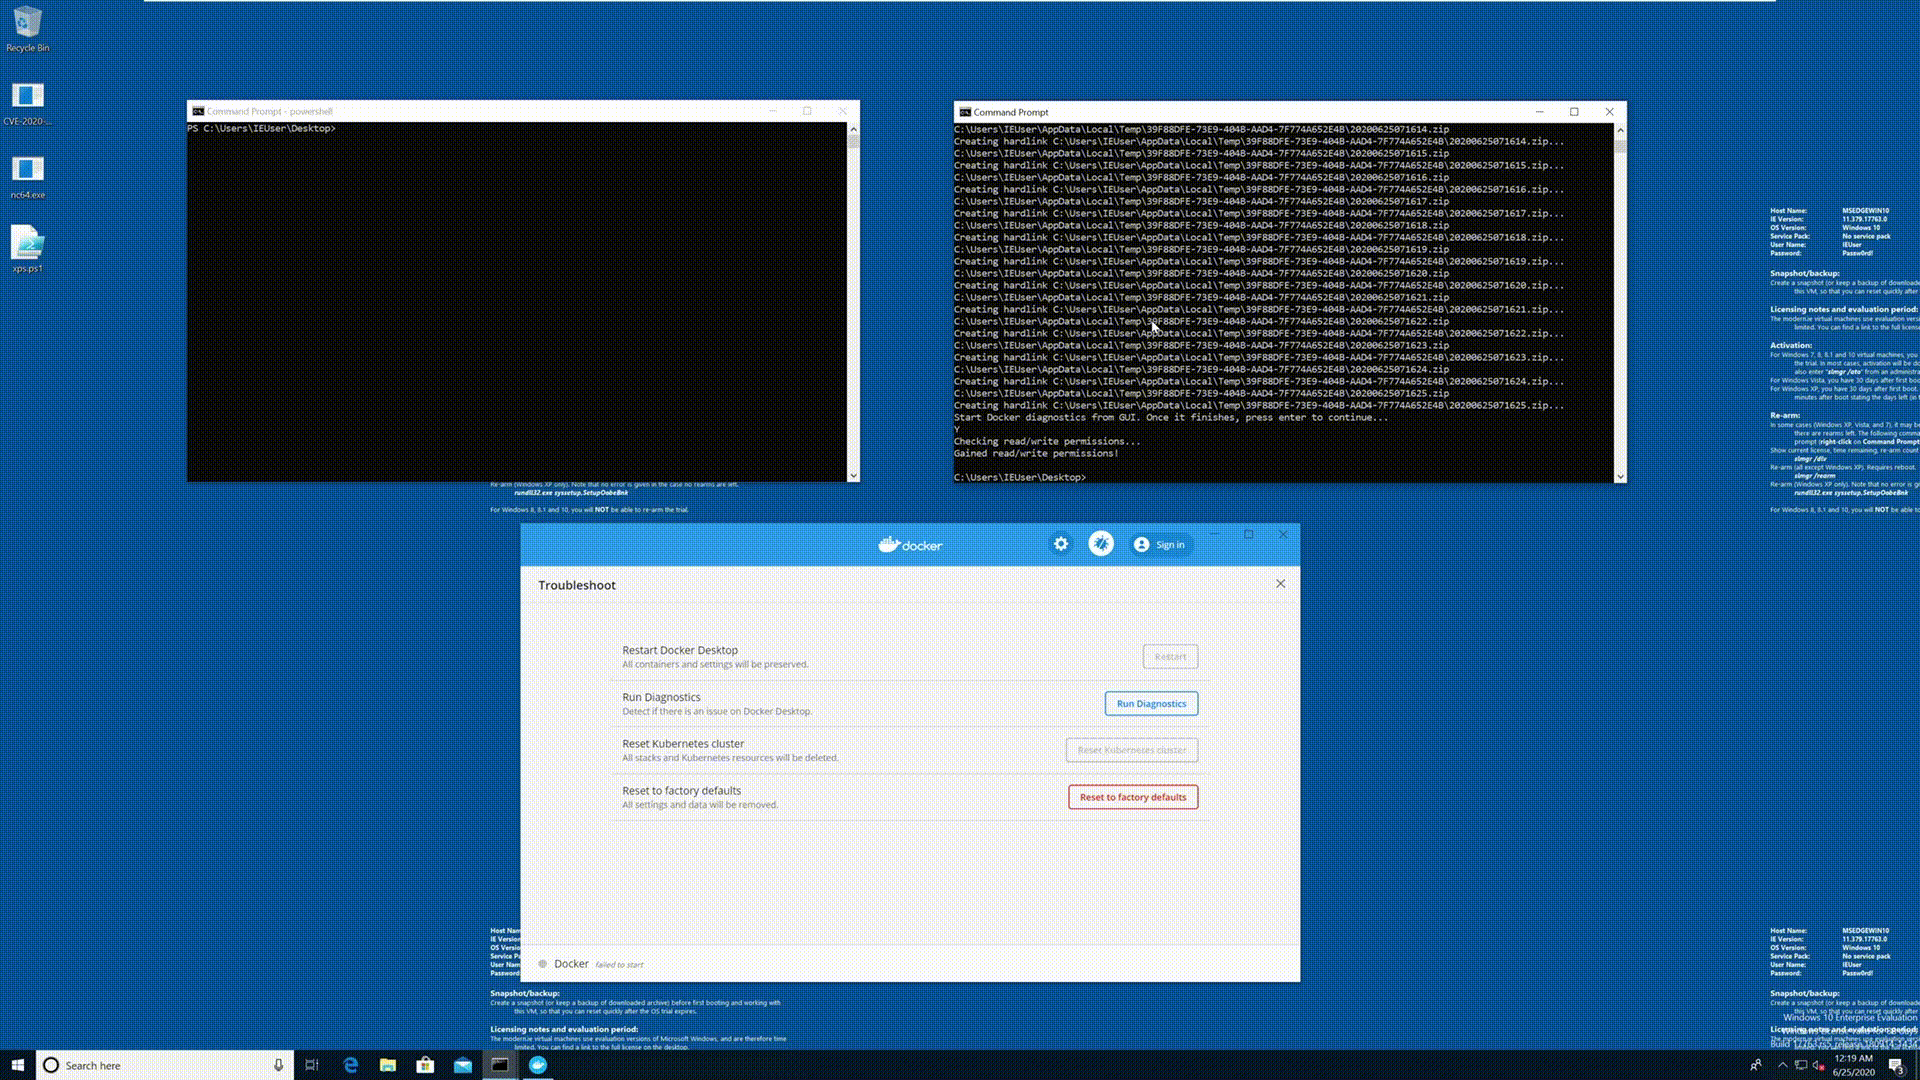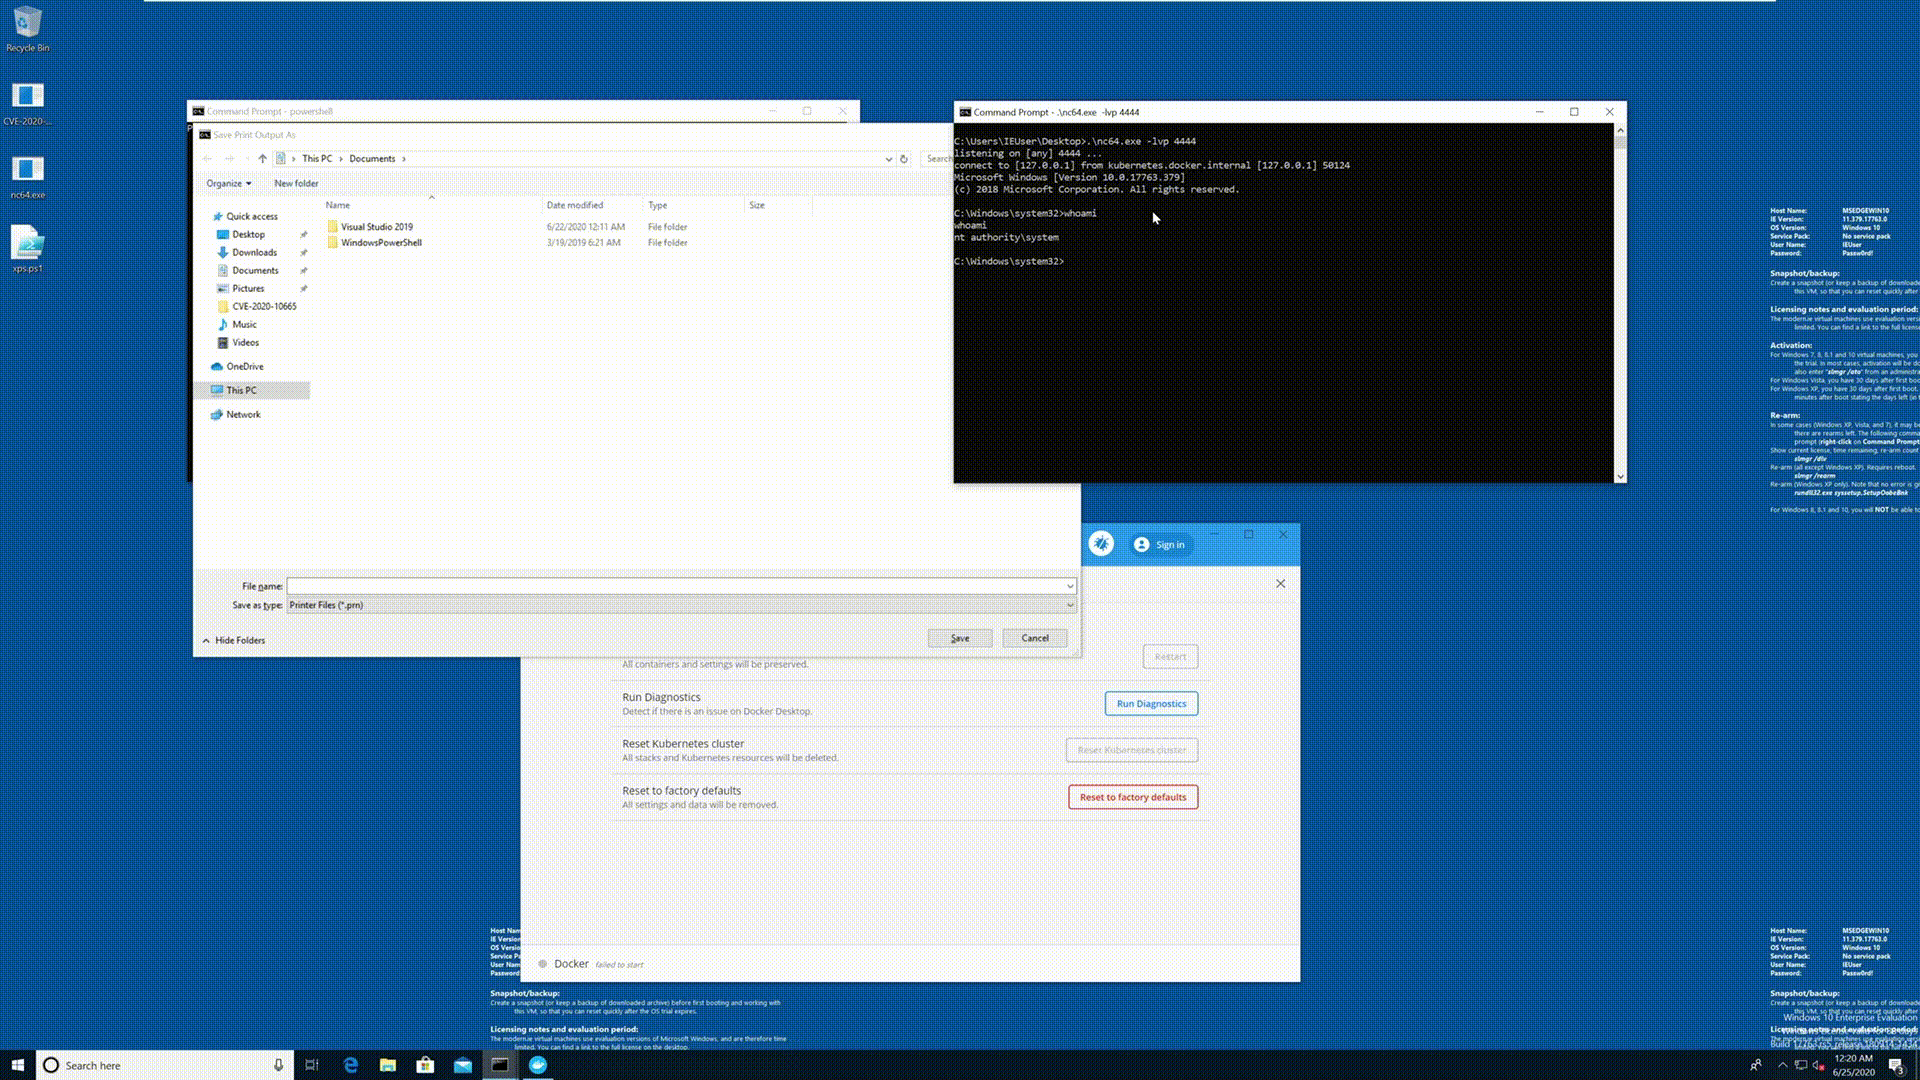 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 target/strelka
Real-time, container-based file scanning at enterprise scale
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.