
ci-supplychain-guard
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
code-analysiscontainer-securitydevsecops+5
28
otsmane-ahmed/ci-supplychain-guardStatic analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 santhreal/keyhog
Open-source secret scanner in Rust
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 goodwithtech/dockle
Container Image Linter for Security, Helping build the Best-Practice Docker Image, Easy to start
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 juliosuas/copyfail-guard
Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.
 sda-se/cluster-image-scanner
Discover vulnerabilities and container image misconfiguration in production environments.
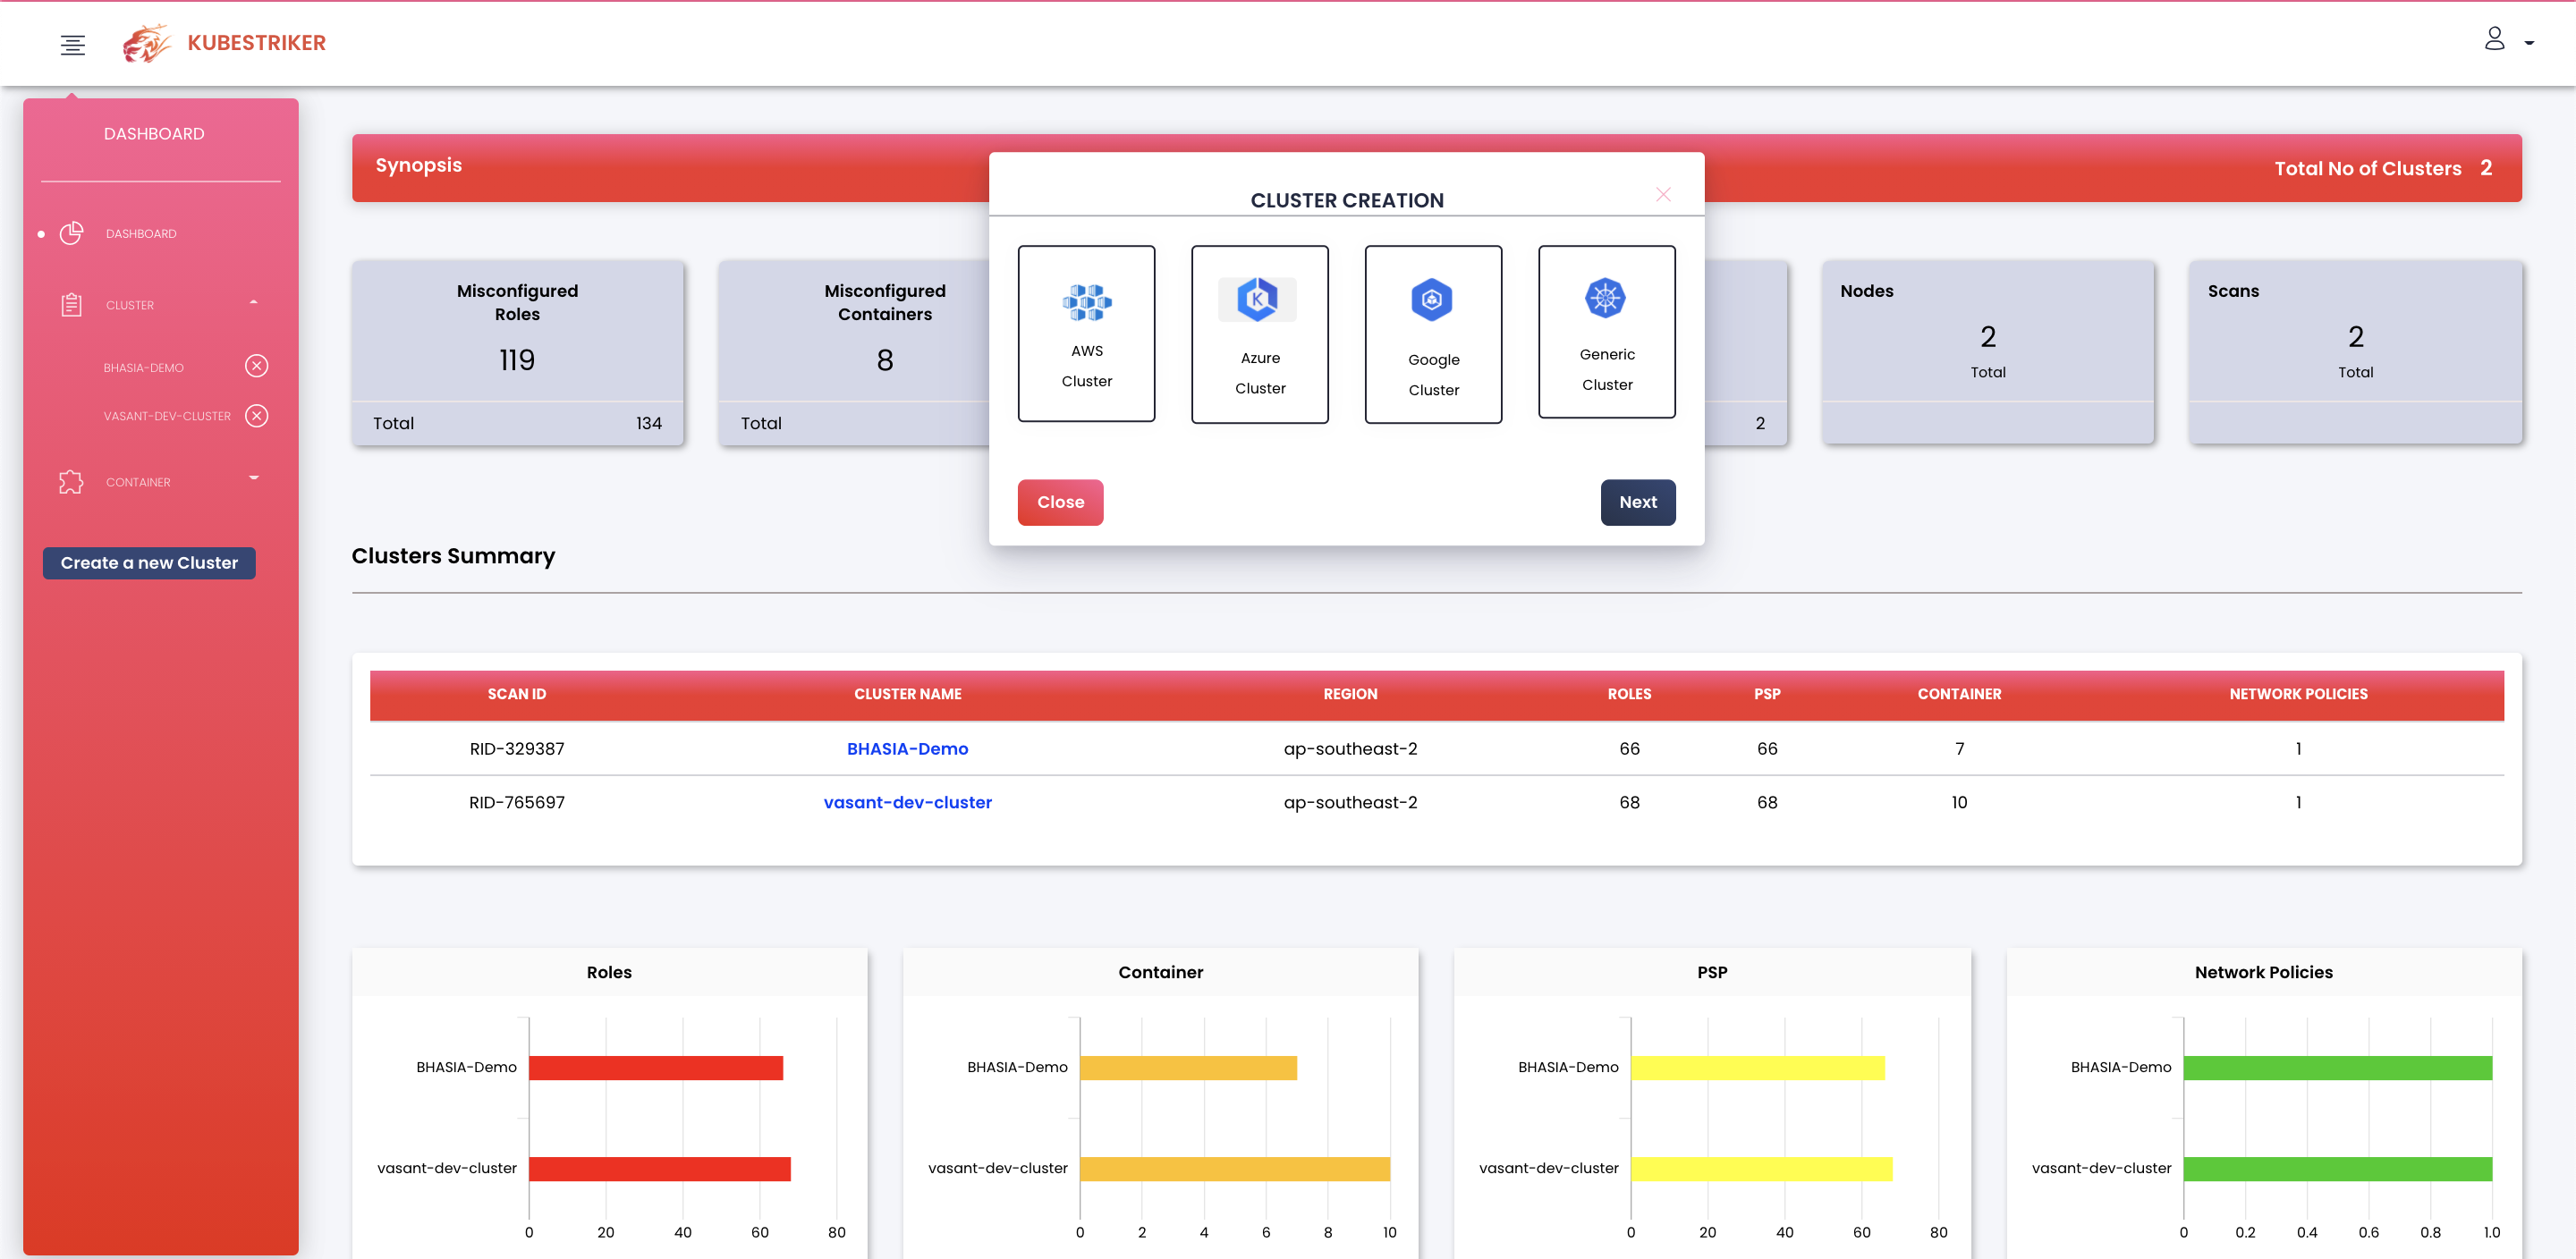 vchinnipilli/kubestriker
A Blazing fast Security Auditing tool for Kubernetes
 wolf1892/cve-2019-7609
docker lab setup for kibana-7609
 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra — taken past the base PoC to show how a common…