
metarget
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
cloud-securitycontainer-securityeducation+4
metarget/metargetMetarget is a framework providing automatic constructions of vulnerable infrastructures.
 cved-sources/cve-2018-3811
Docker container providing a vulnerable environment for CVE-2018-3811, designed for security testing and exploit practice within the Cved vulnerable…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 armourbird/csf
ArmourBird CSF - Container Security Framework
 cved-sources/cve-2017-1000486
Docker container providing a pre-configured vulnerable environment for CVE-2017-1000486, designed for security testing and exploit practice within…
 flame-11/cve-2018-15133-laravel-framework
Reproducible Docker lab for CVE-2018-15133 (Laravel Framework token unserialize RCE) with a known APP_KEY and a /poc route for testing exploit…
 cved-sources/cve-2014-0160
Docker container for CVE-2014-0160 (Heartbleed) vulnerability, part of the Cved framework for managing and deploying vulnerable environments for…
 cved-sources/cve-2018-15877
Docker container providing a pre-configured vulnerable environment for CVE-2018-15877, designed for security training and exploit practice within the…
 cved-sources/cve-2015-5602
Docker container with CVE-2015-5602 for practicing privilege escalation in a controlled environment. Part of the Cved framework for managing…
 cved-sources/cve-2016-6515
Docker container providing a vulnerable environment for CVE-2016-6515 exploitation, part of the Cved framework for managing and testing against known…
 cved-sources/cve-2019-10678
Docker container providing a vulnerable environment for CVE-2019-10678, designed for security training and exploitation practice within the Cved…
 cved-sources/cve-2018-15473
Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…
 cved-sources/cve-2019-6340
Docker container for CVE-2019-6340 exploitation lab, part of the Cved vulnerable container management framework for practicing Drupal security…
 sonatype-workshops/struts2-rce
Exploitable target to CVE-2017-5638
 cved-sources/cve-2019-9194
Docker container with CVE-2019-9194 for practicing vulnerability exploitation in a controlled environment. Part of the Cved vulnerable container…
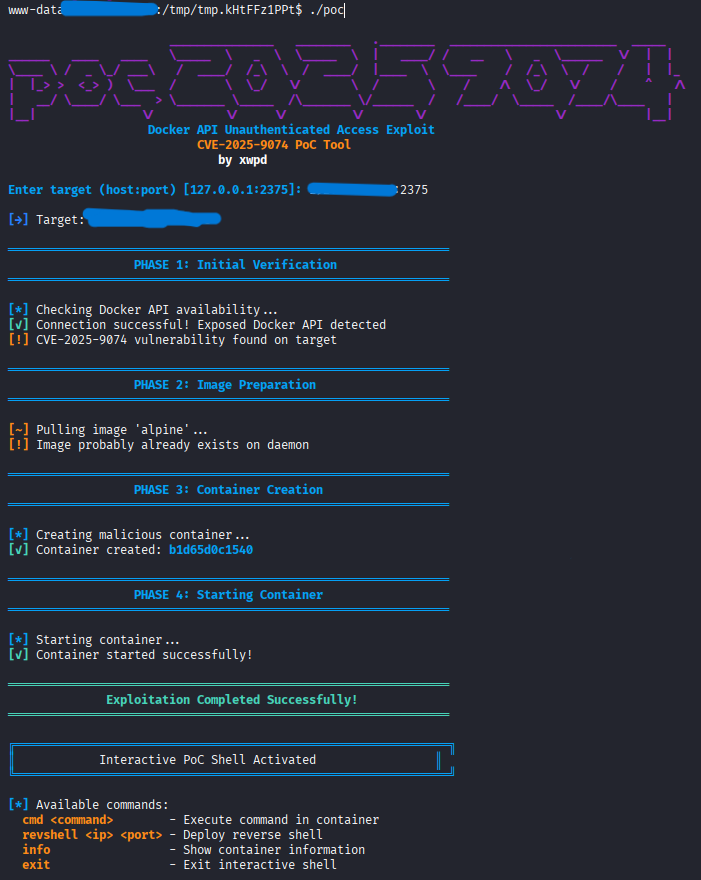 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 azdevops143/fragnesia-charan-cve-2026-46300
Hardened container staging framework with seccomp syscall whitelisting and eBPF telemetry to detect and block container escape and kernel ULP…
 cved-sources/cve-2018-1273
Docker container for CVE-2018-1273 exploitation lab, part of the Cved vulnerable environment management framework for security training and testing.