
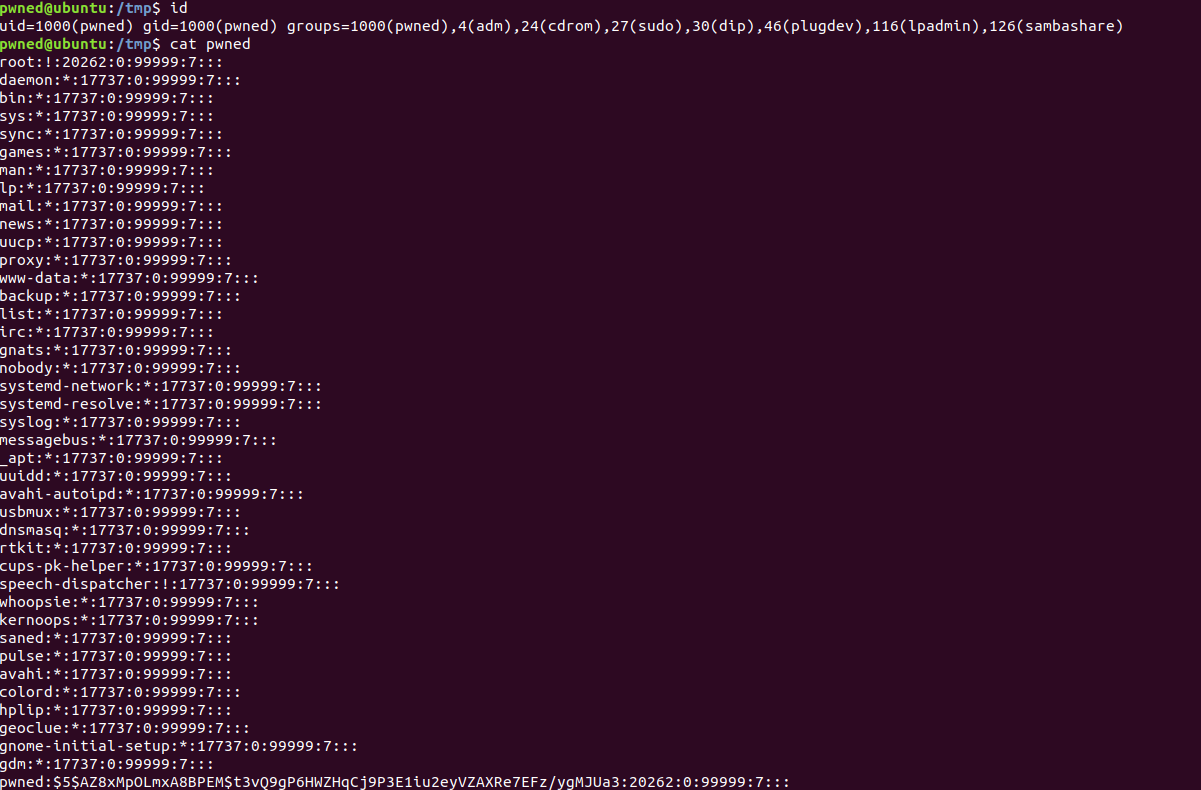
cve_2019-5736-PoC
 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
container-escapecontainer-securityeducation+3
perimora/cve_2019-5736-pocC-based PoC for CVE-2019-5736
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 ianxtianxt/cve-2019-16097
Batch exploit script for CVE-2019-16097, targeting Harbor container registry to create unauthorized admin accounts via crafted API requests.
 rootdirective-sec/cve-2026-39987-lab
Local Docker lab reproducing CVE-2026-39987, a pre-auth RCE in marimo's terminal WebSocket. Compares vulnerable and patched versions with least-harm…
 detect-defenselab/cve-2026-31431-detection-defense
Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 sgkdev/bad_garbage
CVE-2026-53361 AF_UNIX GC vs MSG_PEEK use-after-free container escape
 devstuff/harden-docker-seccomp
Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.
 hackspeak/cve-2026-17106
PoC for Docker `docker cp` arbitrary file write, exploiting symlink and tar extraction flaws to overwrite host binaries or launch agents for…
 yandex-cloud-examples/yc-mk8s-sctphantom-mitigation
DaemonSet для митигации уязвимости CVE-2026-64564 (SCTPhantom)
 forxiucn/nginx-cve-2026-42945-poc
Proof-of-concept exploit for CVE-2026-42945, a critical heap overflow in NGINX rewrite module enabling unauthenticated remote code execution via…
 takumak/cve-2019-5736-reproducer
Reproducer for CVE-2019-5736, a RunC container escape vulnerability. Provides build scripts and a KVM-based lab to confirm the exploit against…
 rootdirective-sec/cve-2026-23744-lab
Docker lab to compare vulnerable and patched builds of MCPJam Inspector for CVE-2026-23744, demonstrating network binding differences and API…
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 tangjie1/cve-2026-31431-check
CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script