
grype
 anchore/grype
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
12.9k22h 43m ago
anchore/grypeA vulnerability scanner for container images and filesystems
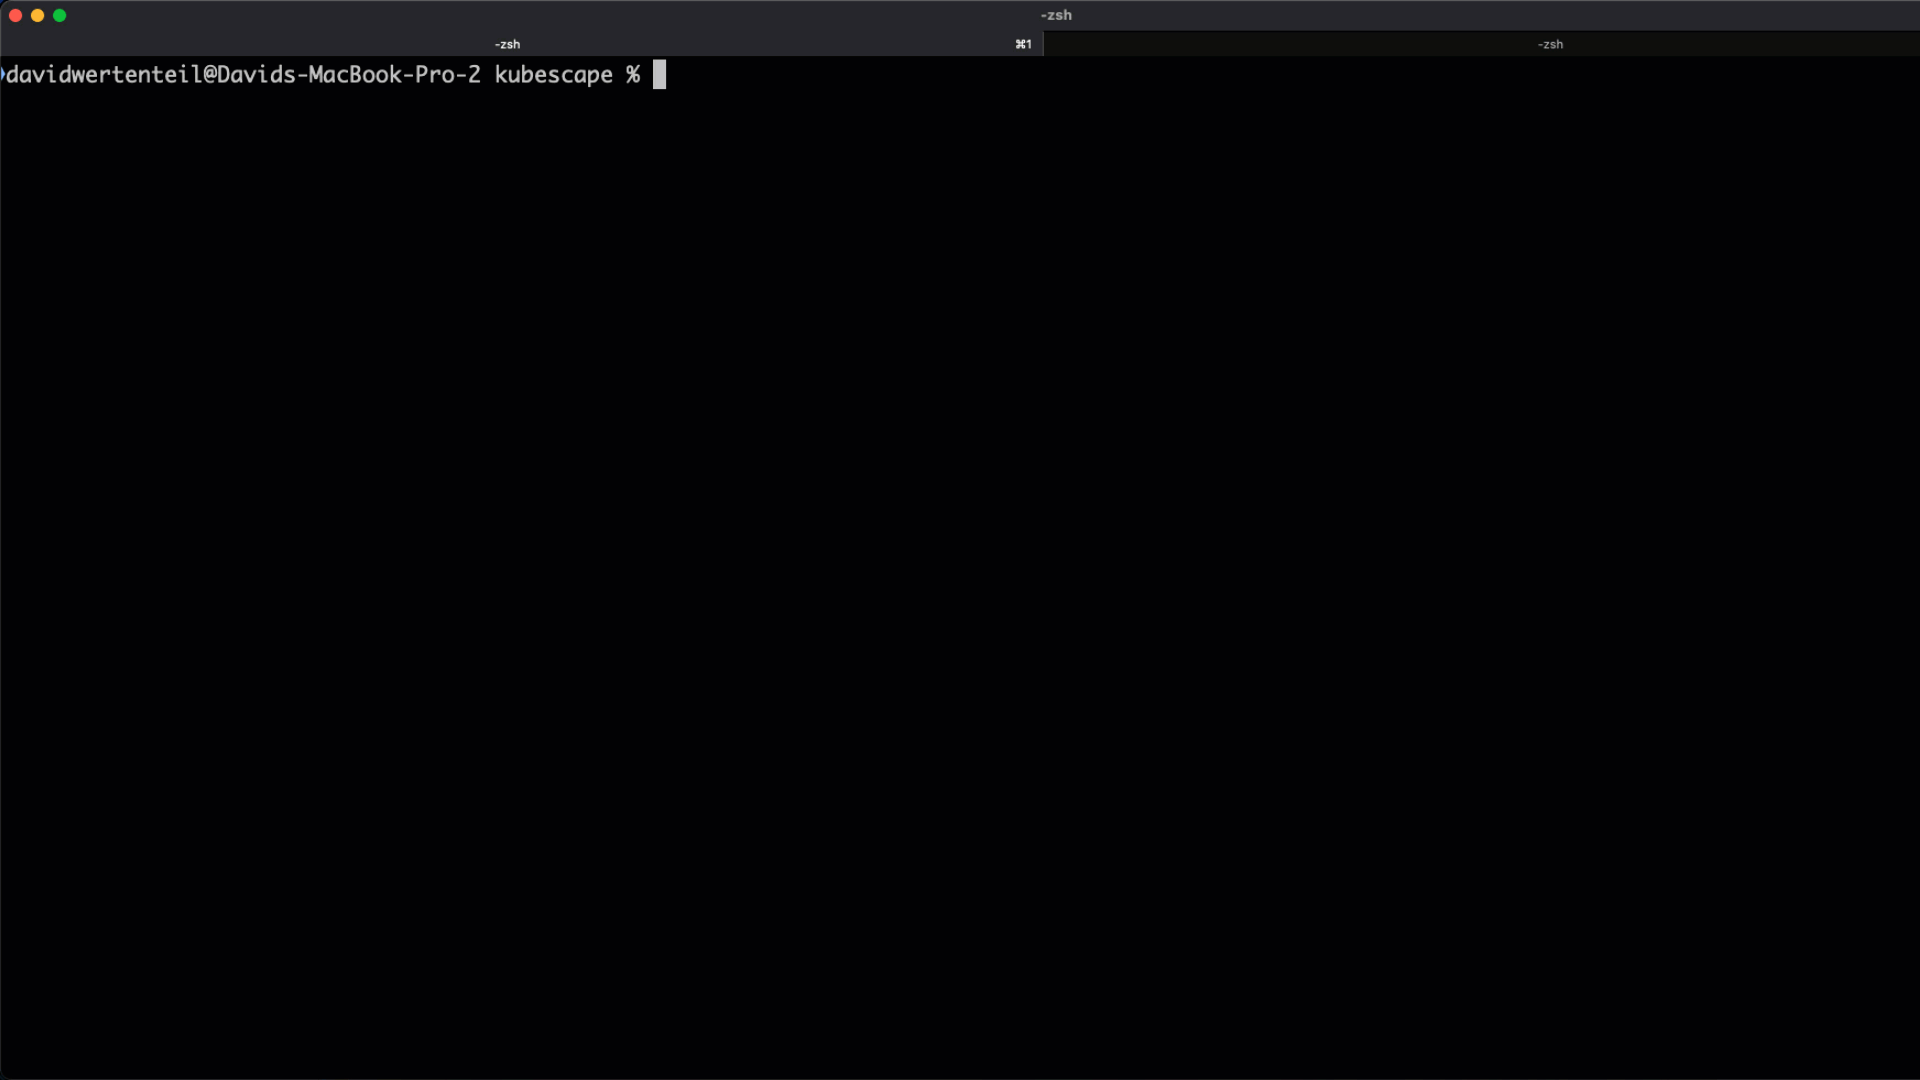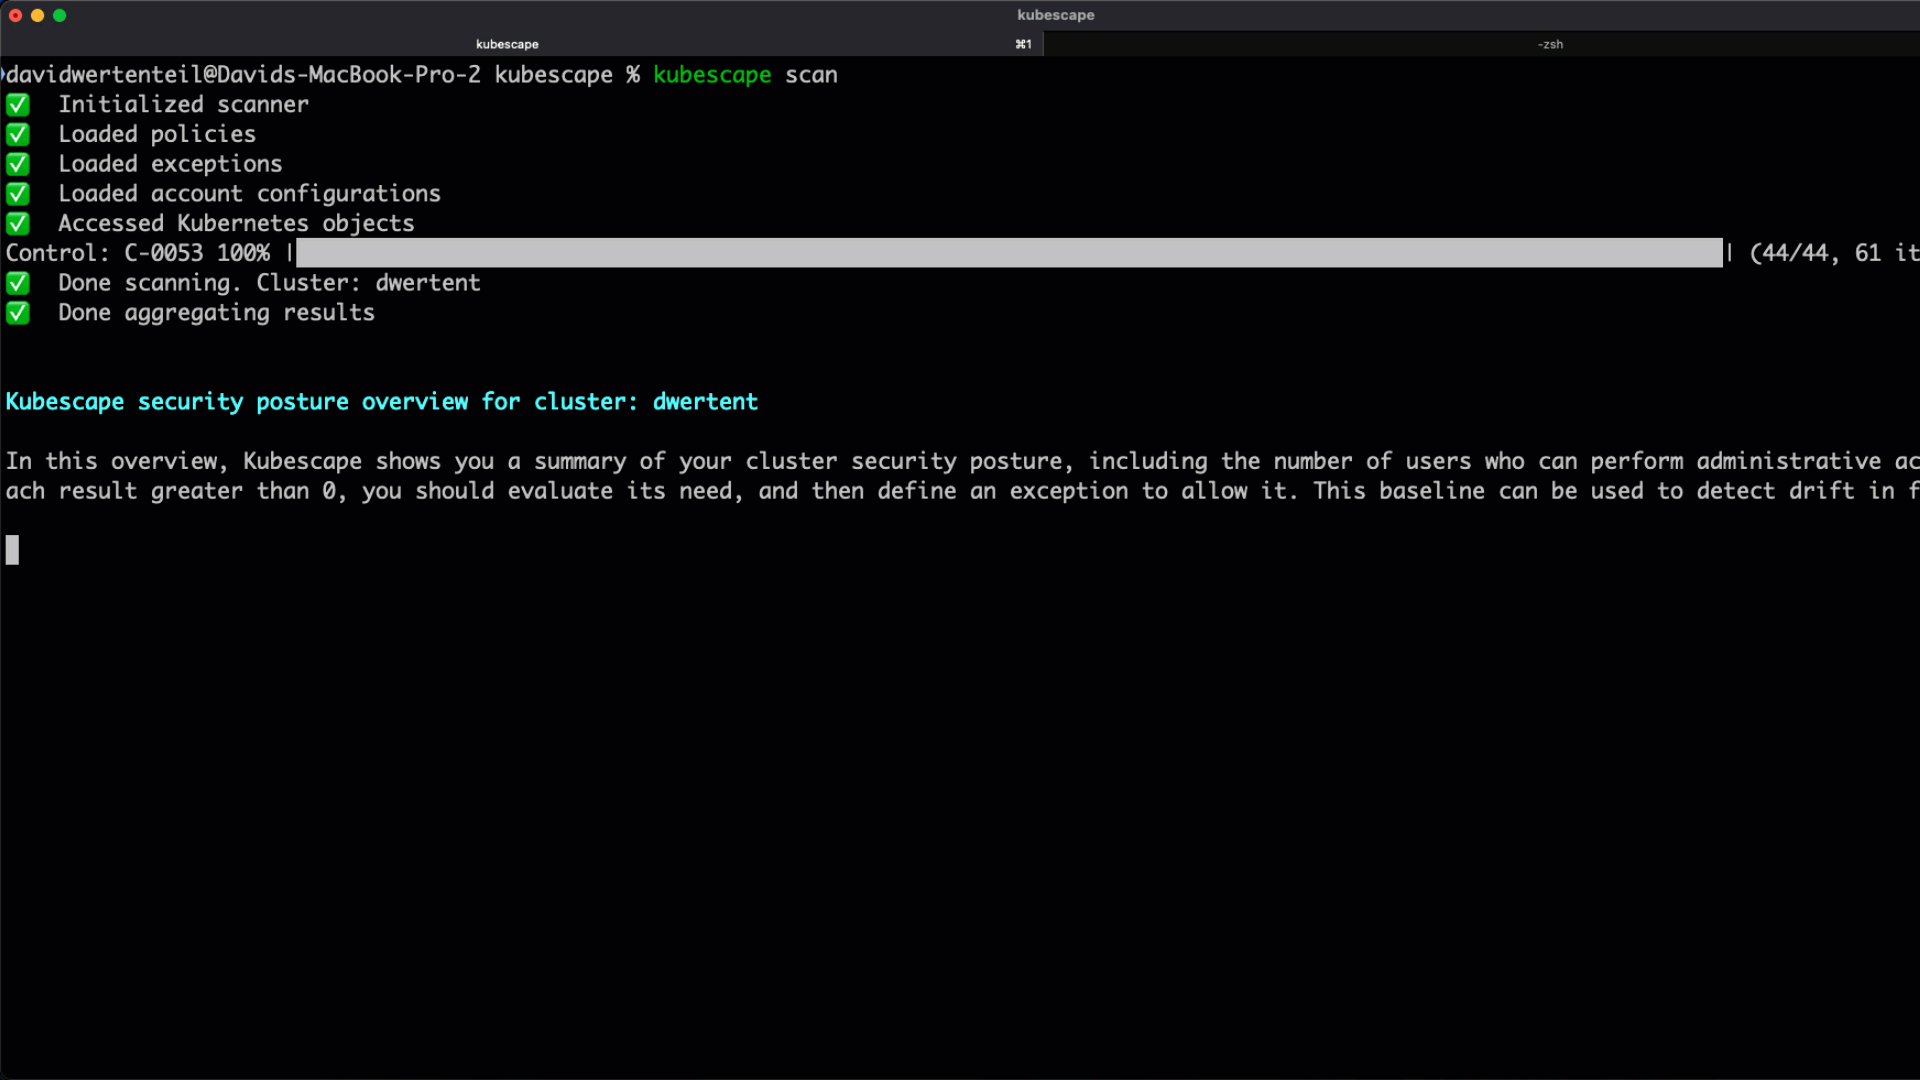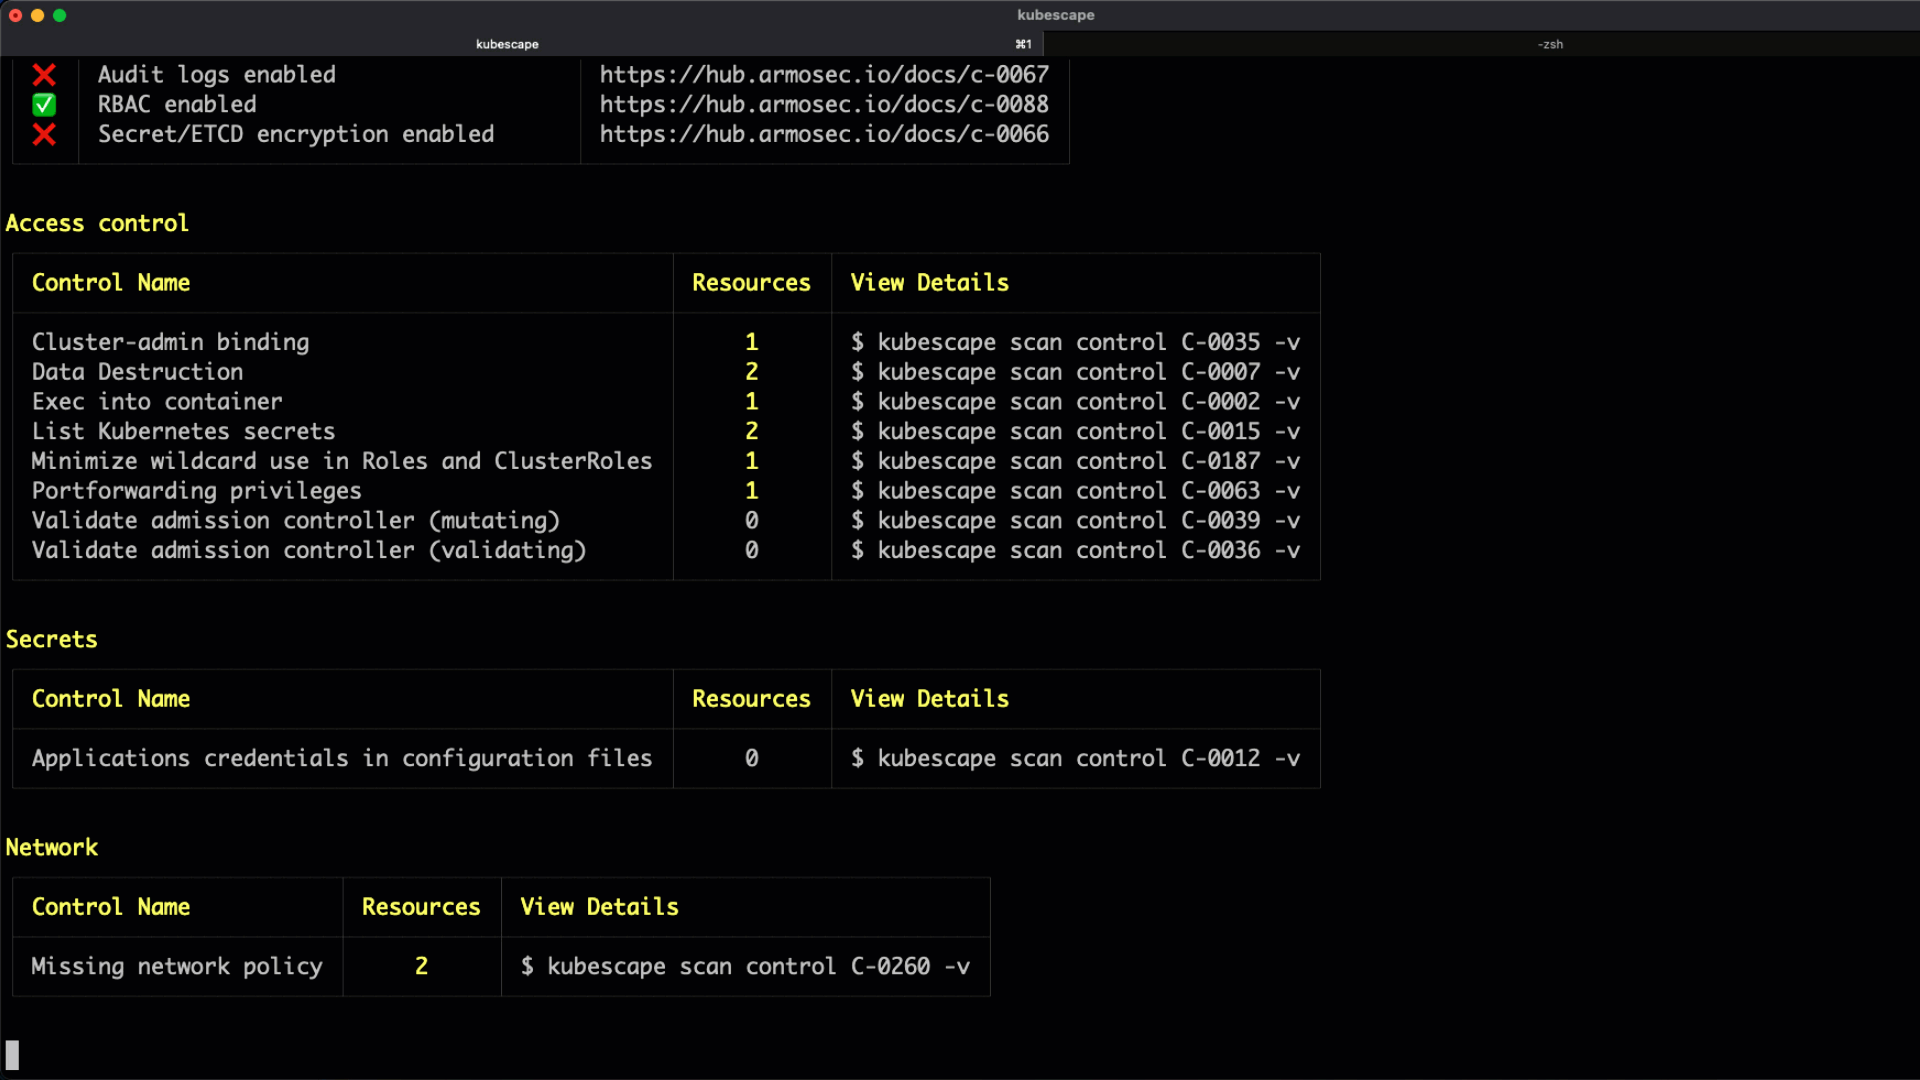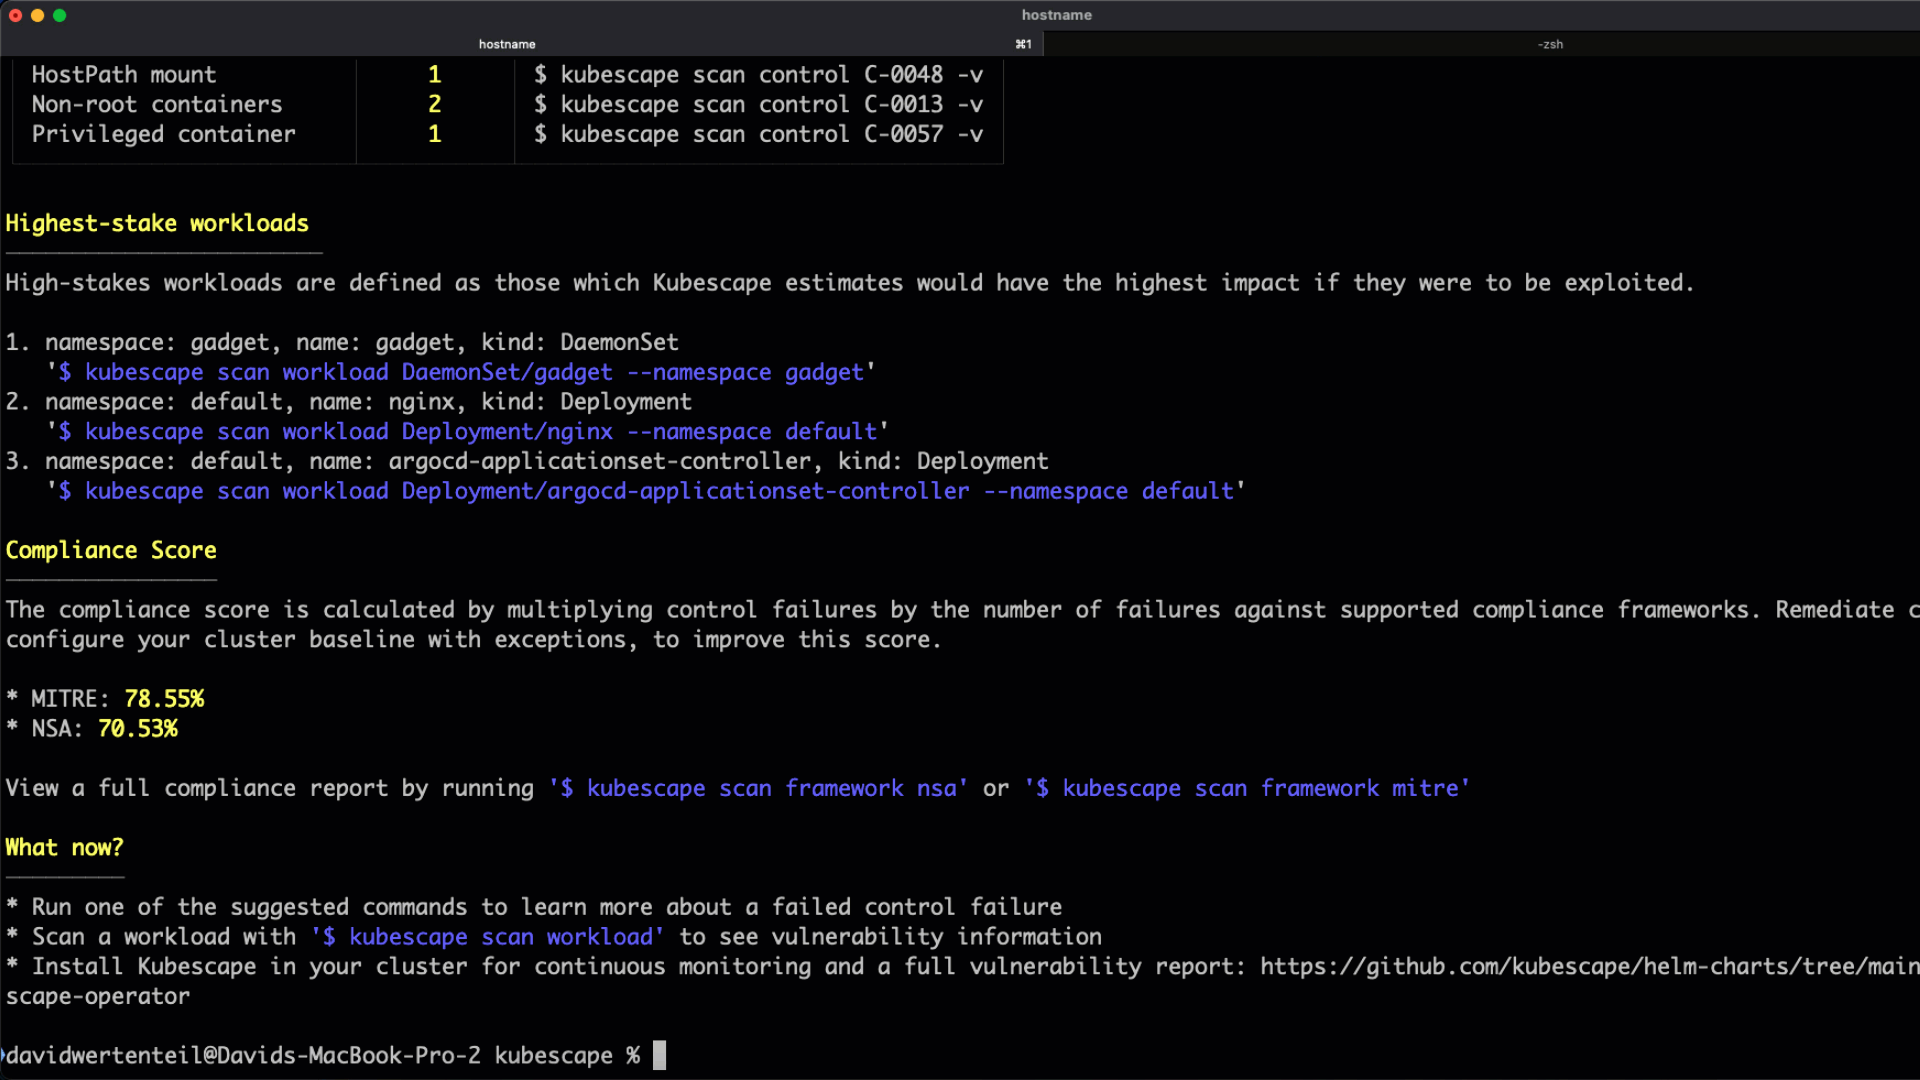 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
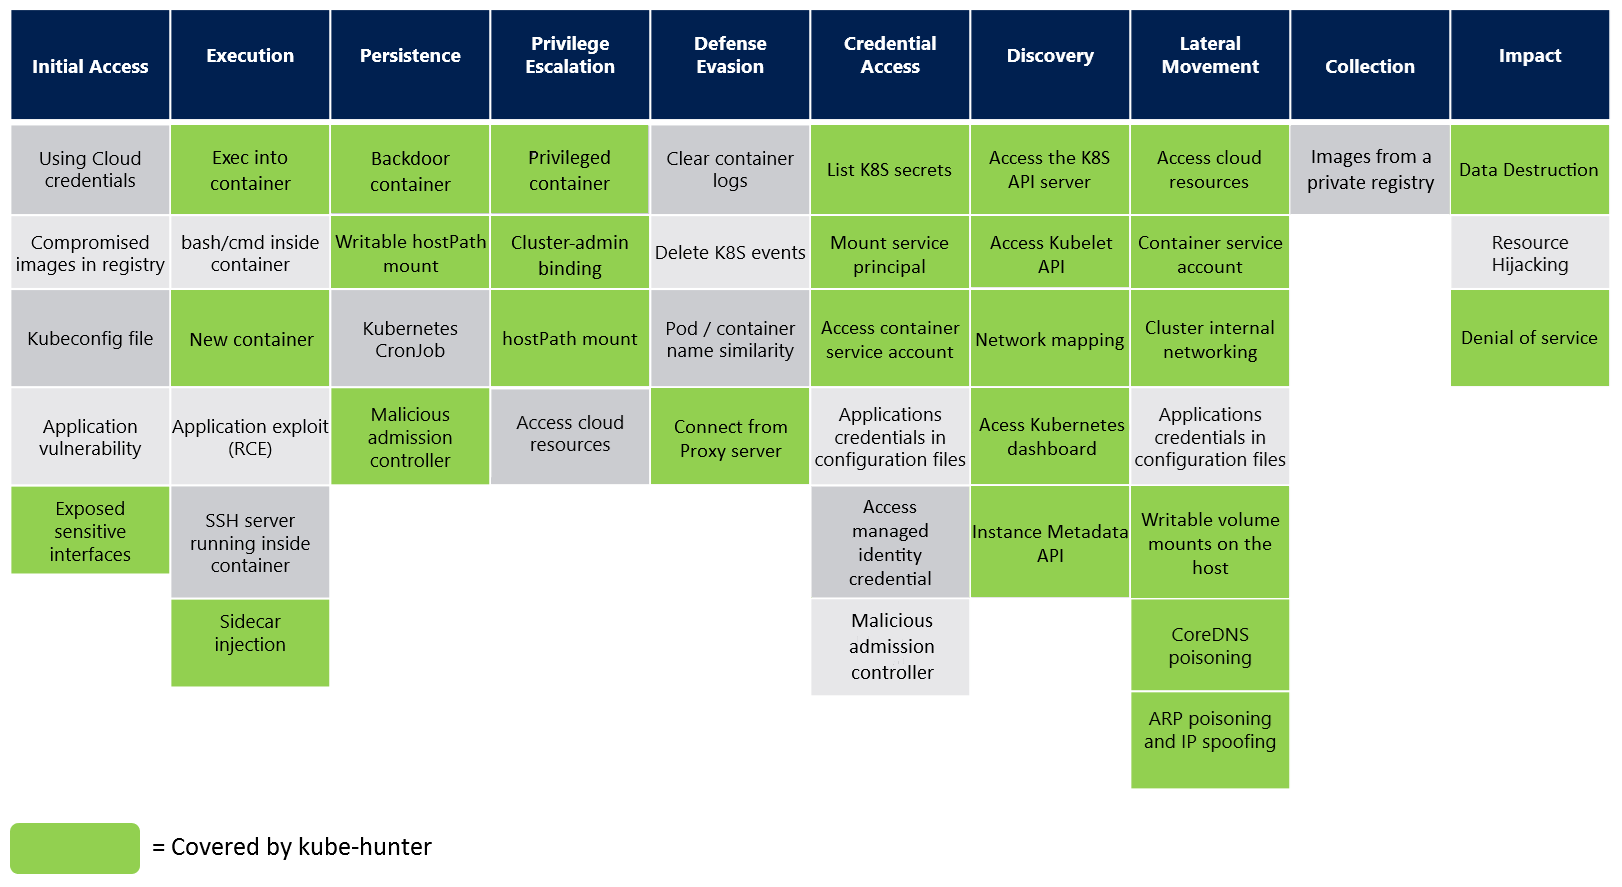 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
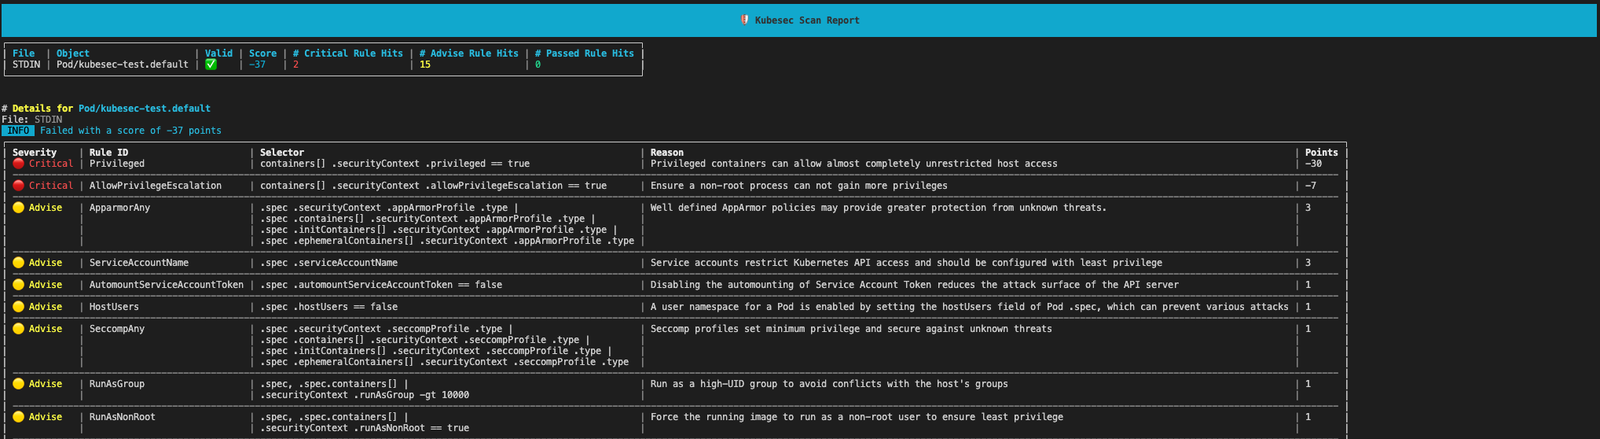 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 impalabs/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 nitrocao/cve-2024-21626
PoC and Detection for CVE-2024-21626
 yoshino-s/cve-2025-1974
Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…
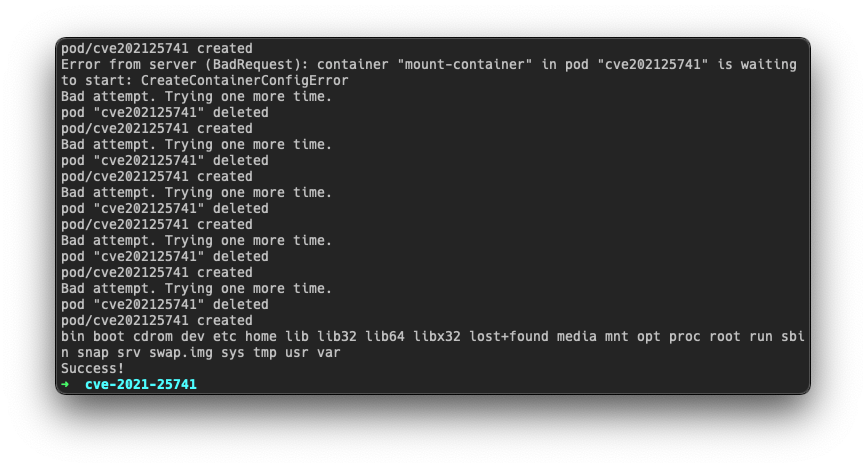 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…