

offensive-one-liners
 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
container-escapectfcurated-resources+9
wattocyber/offensive-one-liners110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 nccgroup/abstractshimmer
Proof of concept for CVE-2020-15257 in containerd.
 scherepiuk/container-escape-ebpf
POCs and Tetragon Rules for CVE-2024-21626 and CVE-2025-31133
 sgkdev/ipv6_frag_escape
Linux LPE - Reliable Jail/Container Escape
 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 skysbsb/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in Docker/runc. Demonstrates file descriptor manipulation to break out…
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 jpts/cve-2022-0847-dirtypipe-container-breakout
Proof-of-concept exploit for CVE-2022-0847 (DirtyPipe) enabling container breakout via kernel privilege escalation. Includes demonstration and…
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
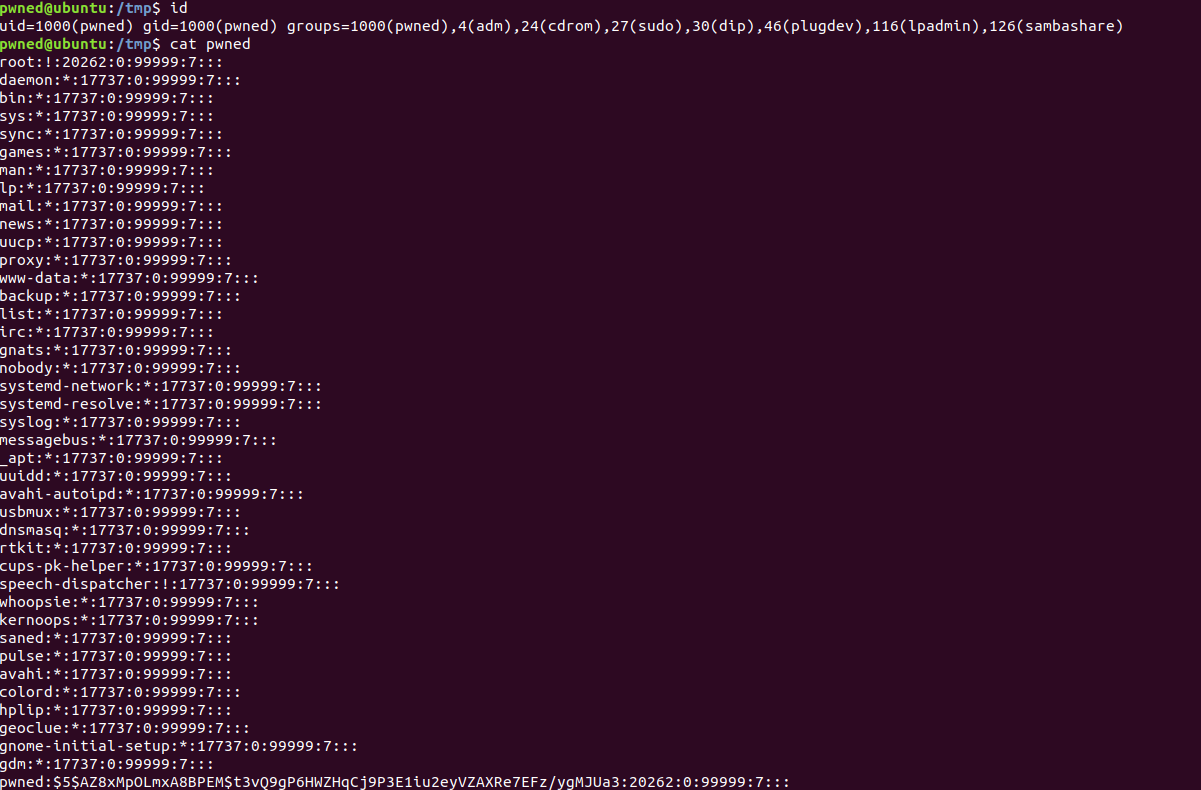 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs
 kagami/docker_cve-2015-2925
Docker + CVE-2015-2925 = escaping from --volume
 prabeershakya/cve-2022-0185-poc
Proof-of-concept exploit for CVE-2022-0185, a Linux kernel heap buffer overflow enabling local privilege escalation and container escape via FUSE and…
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.