

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.8k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
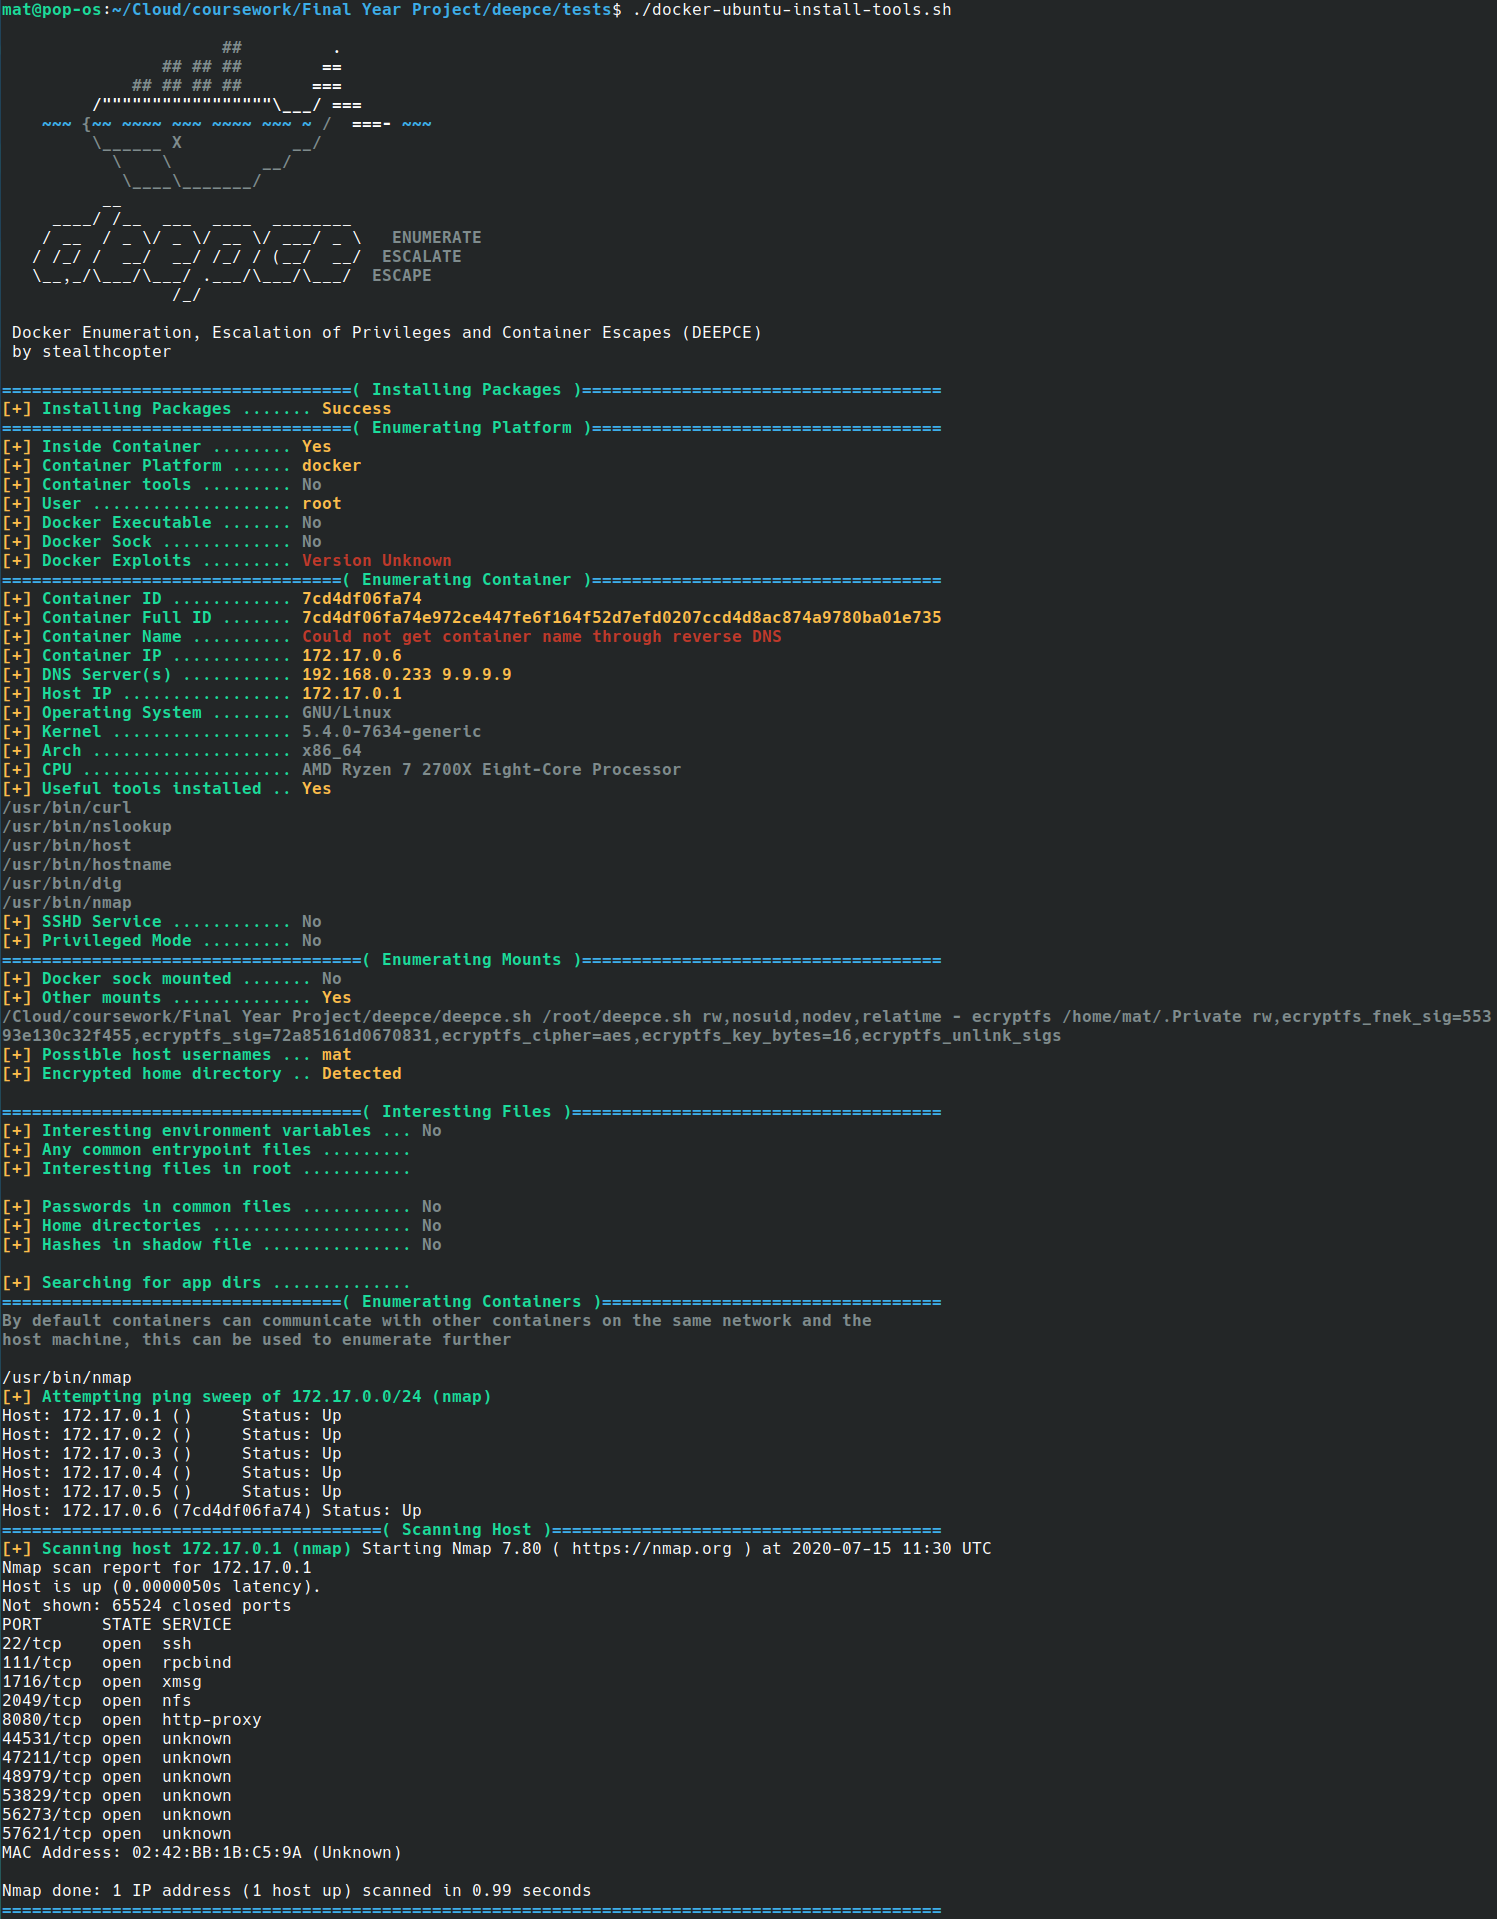 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
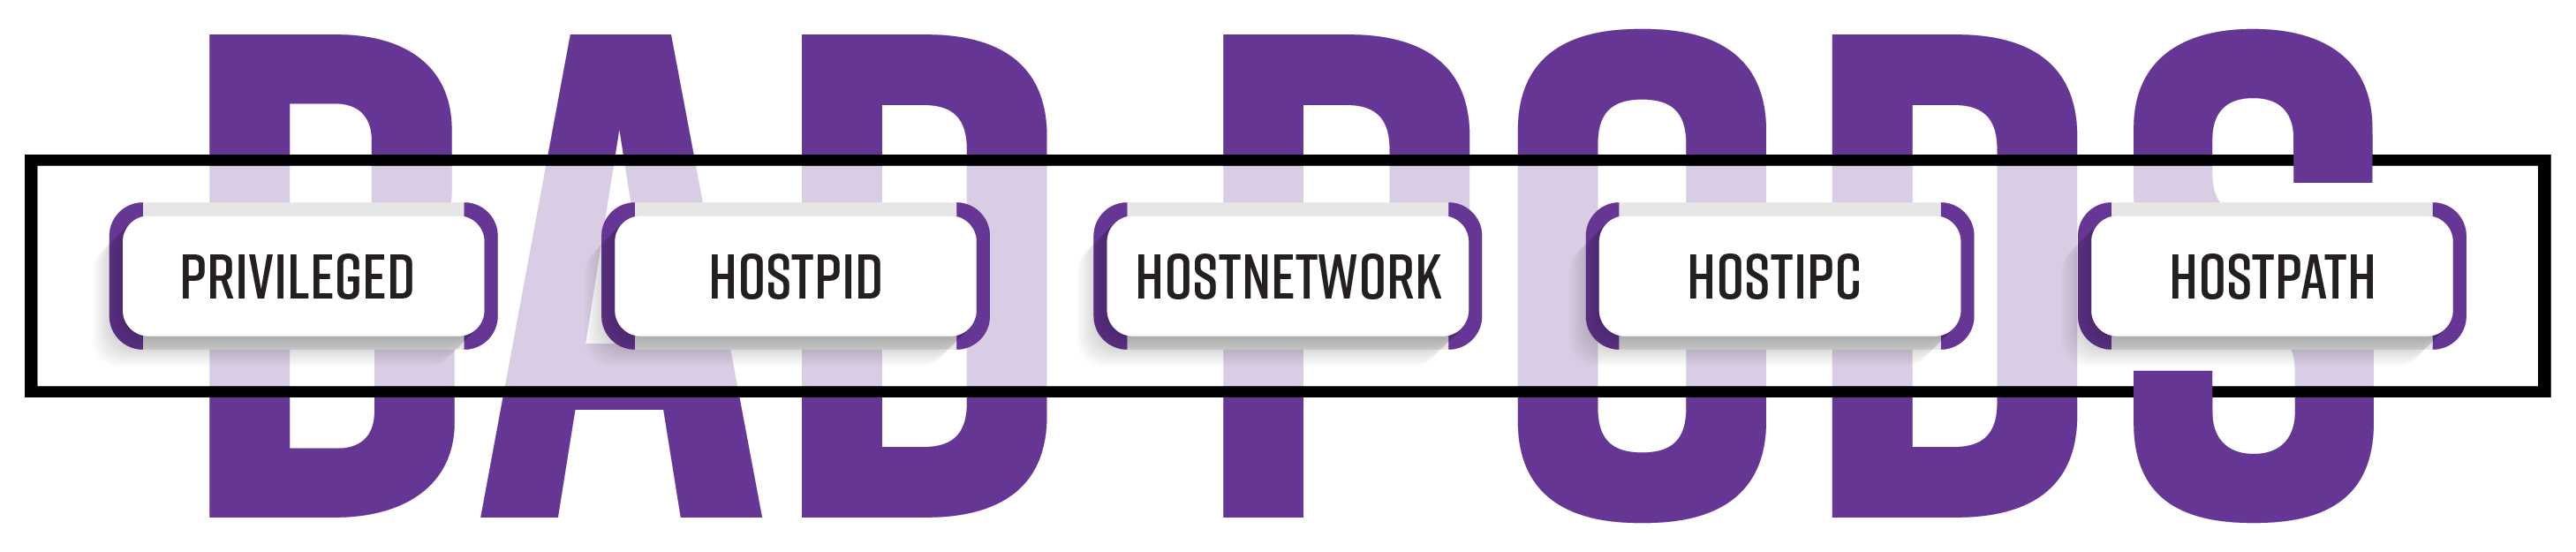 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
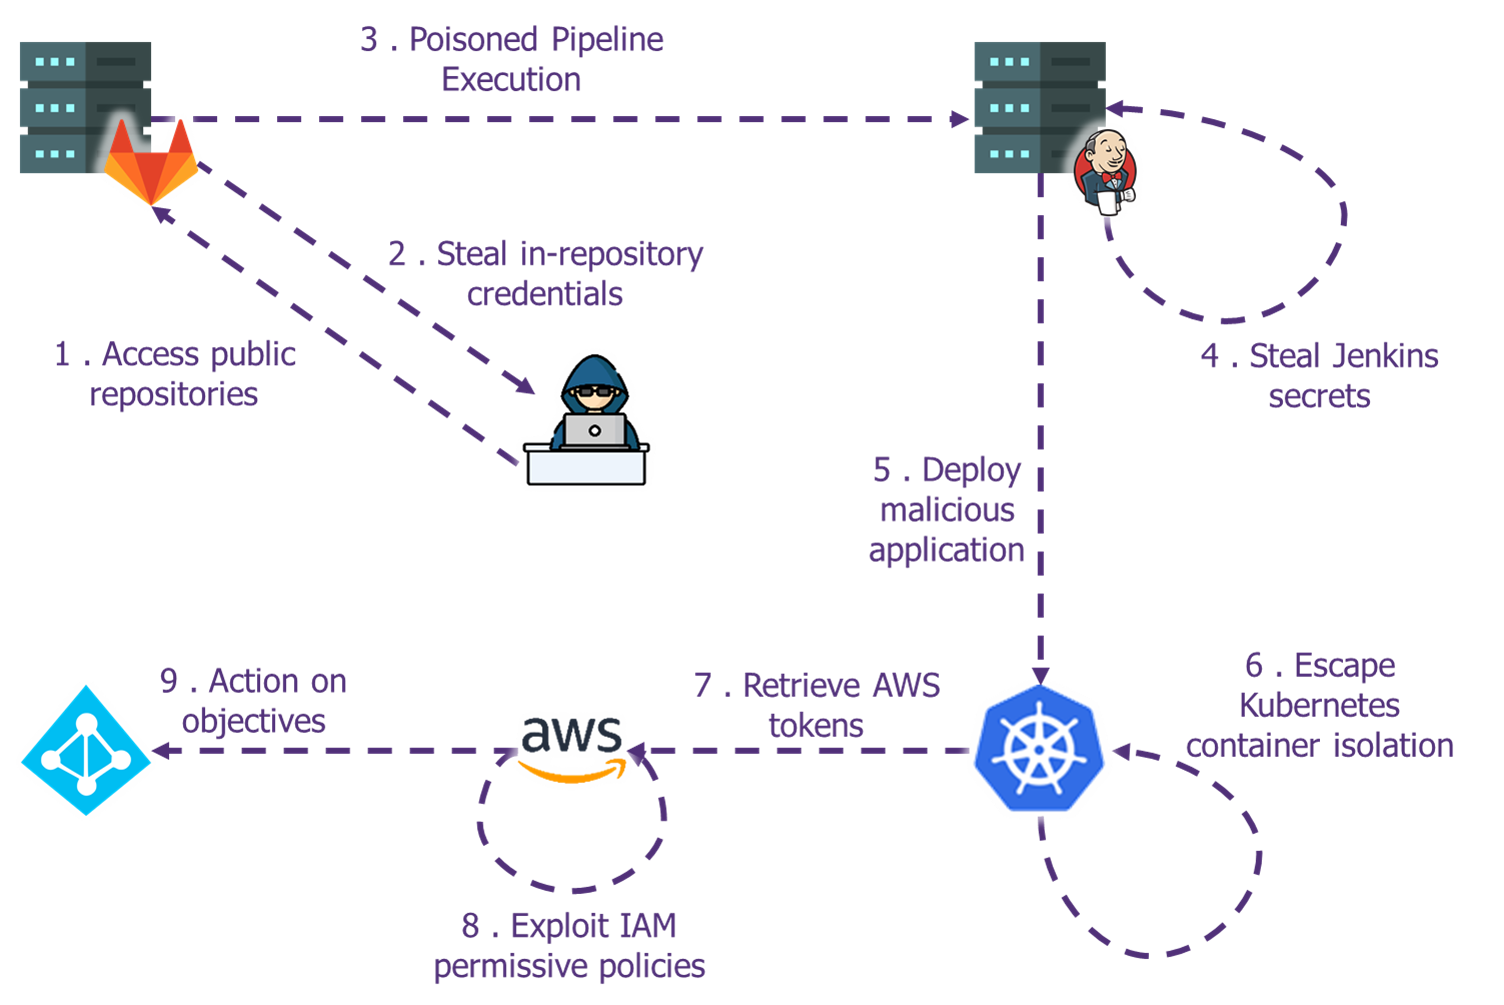 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
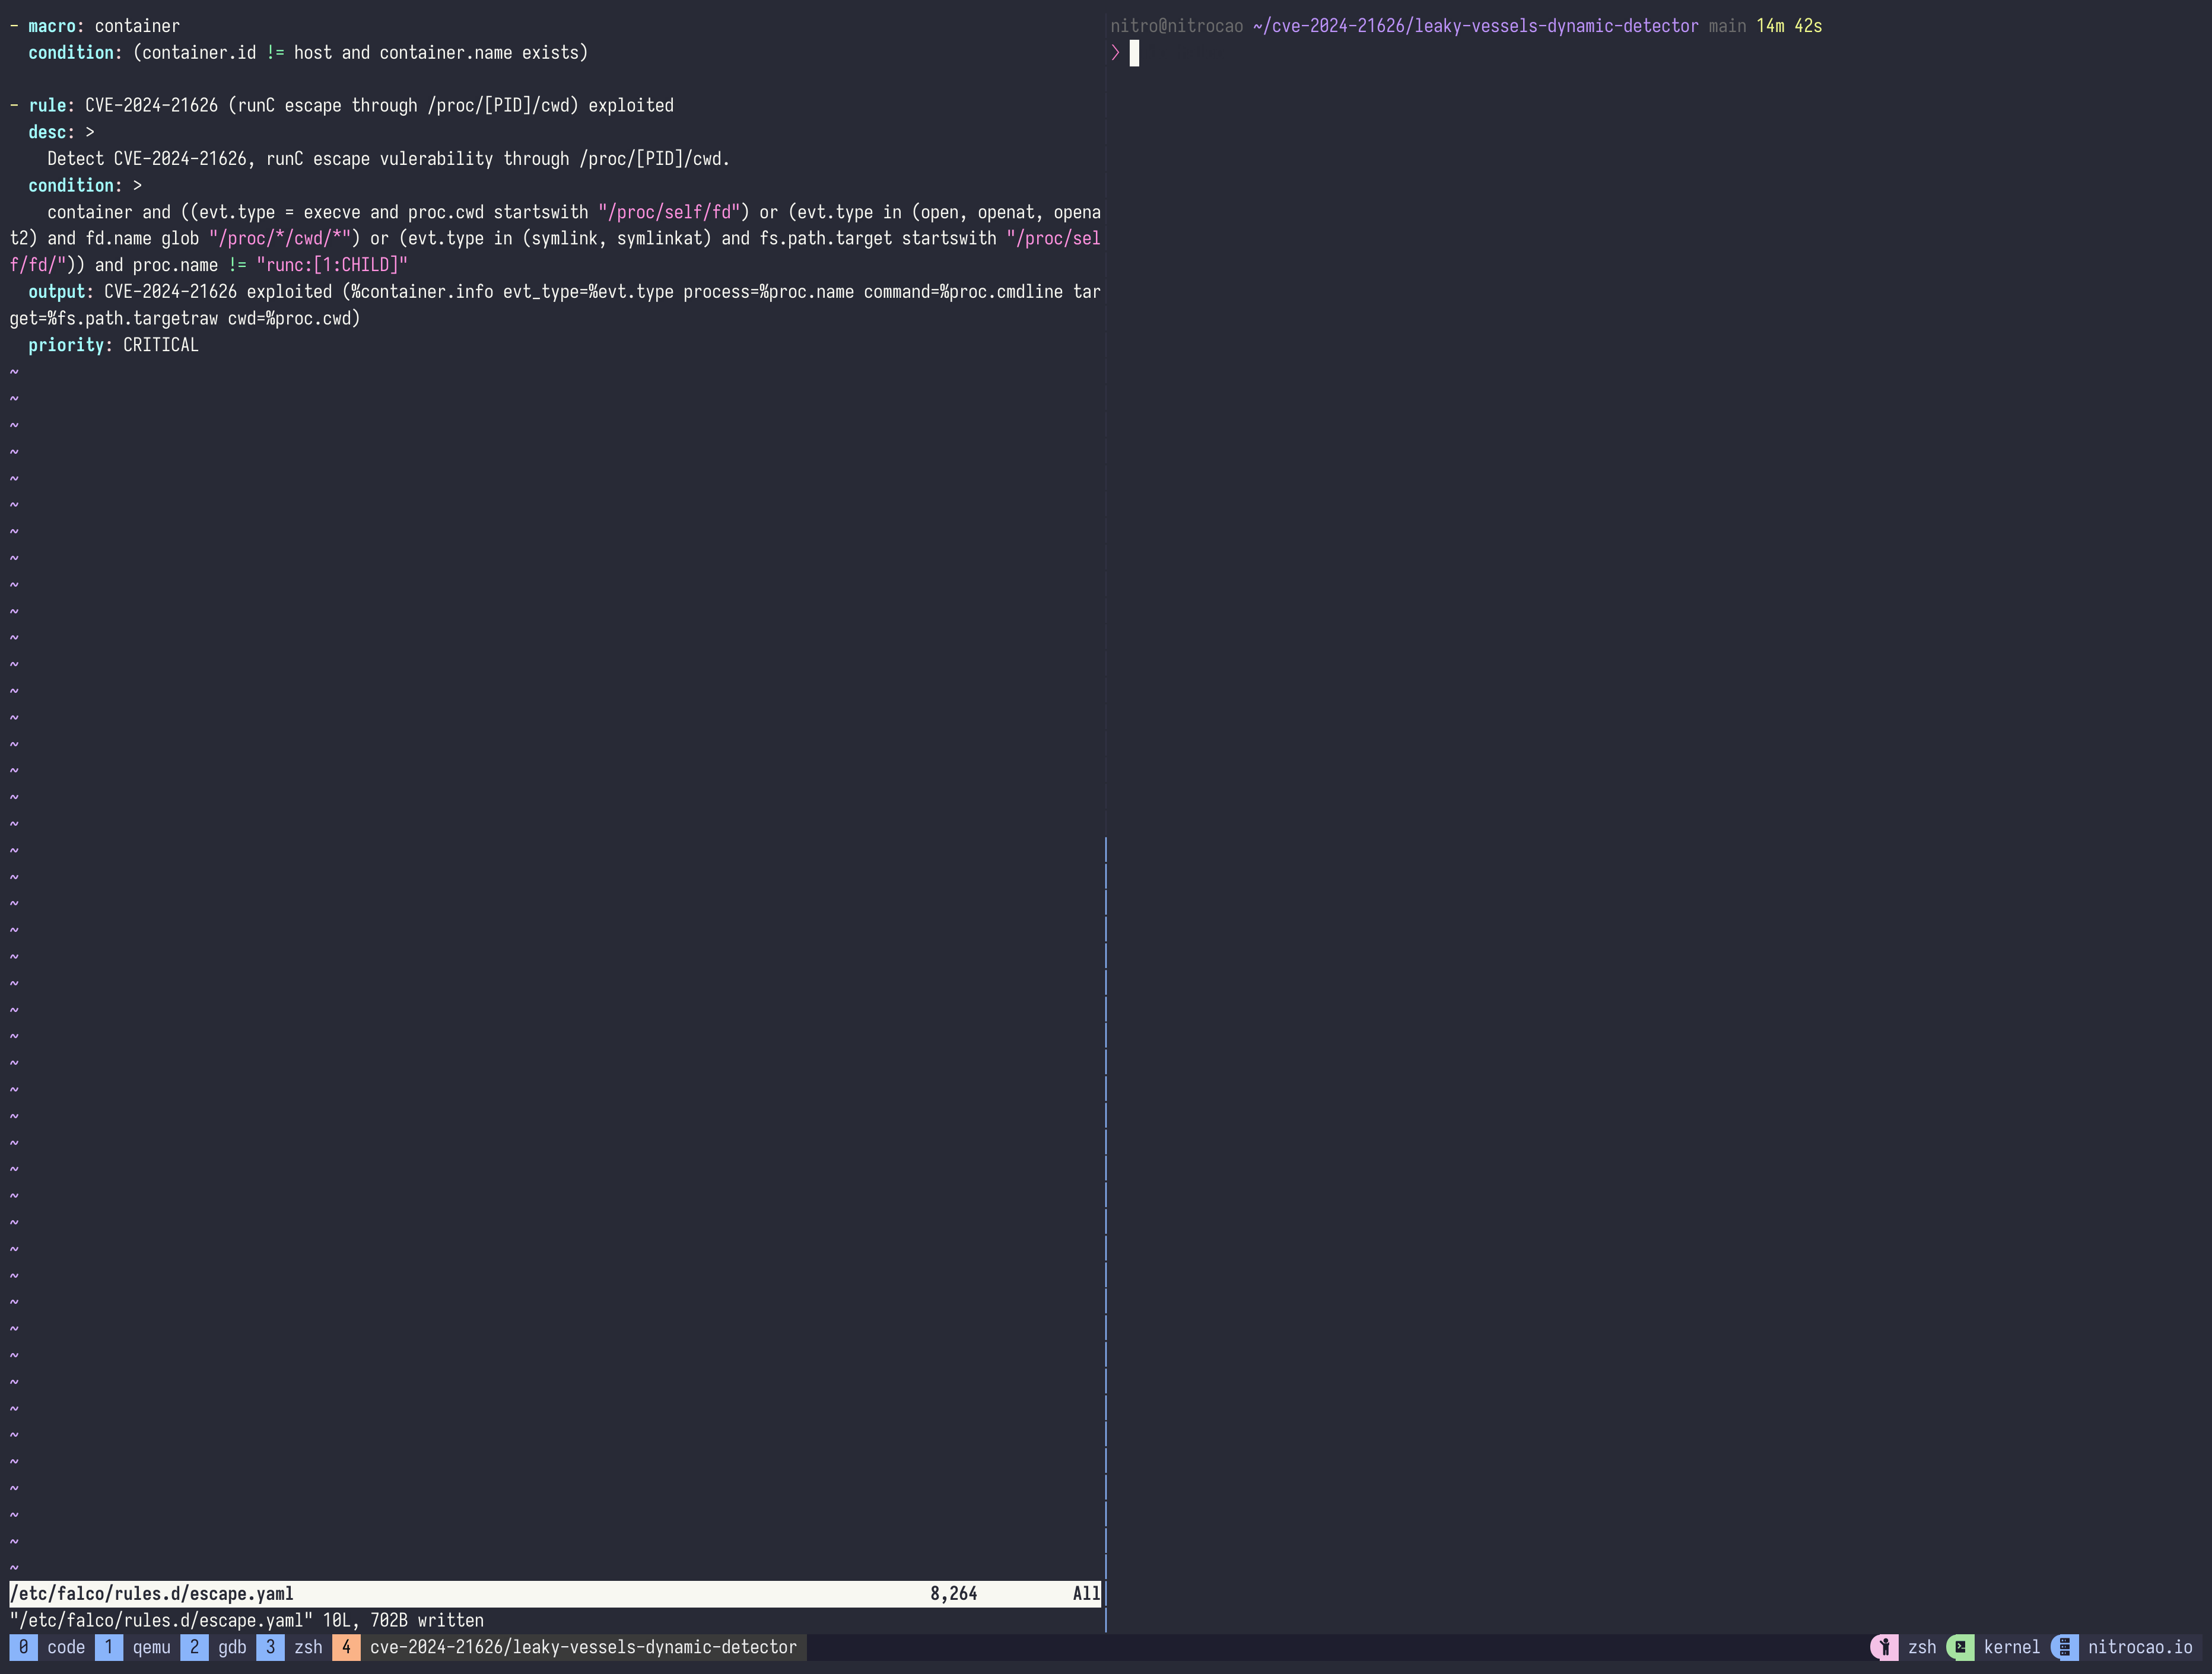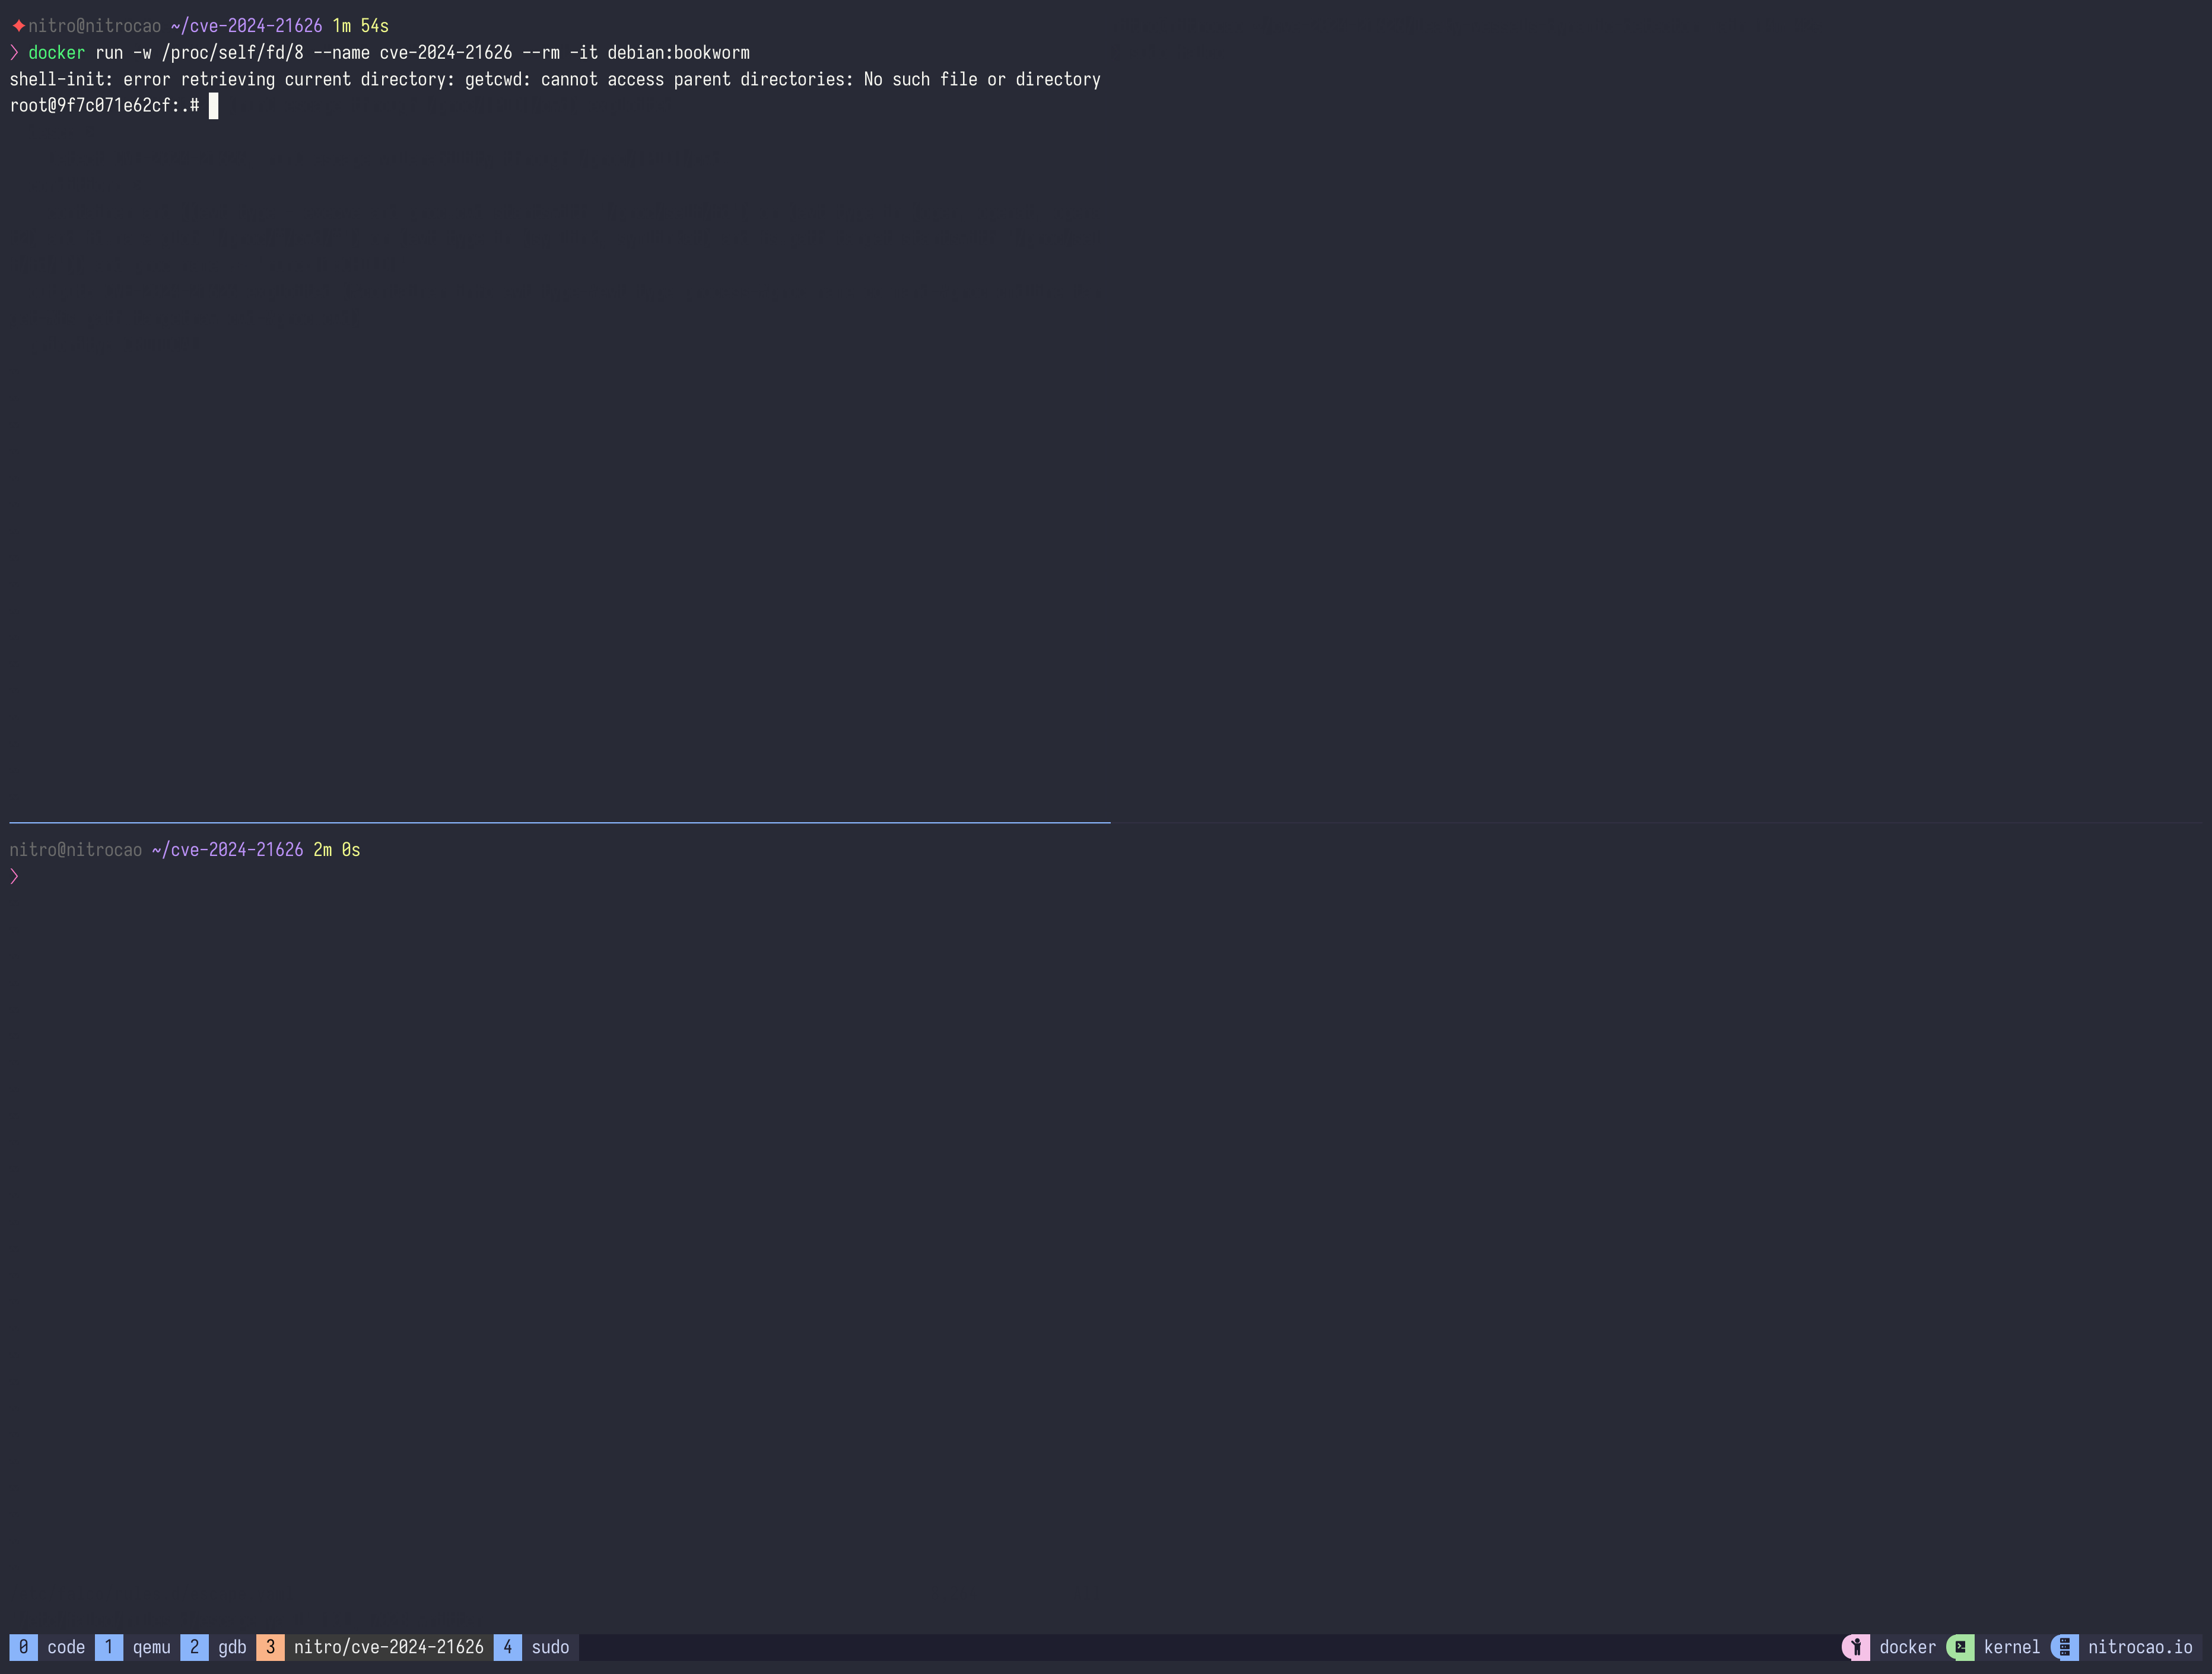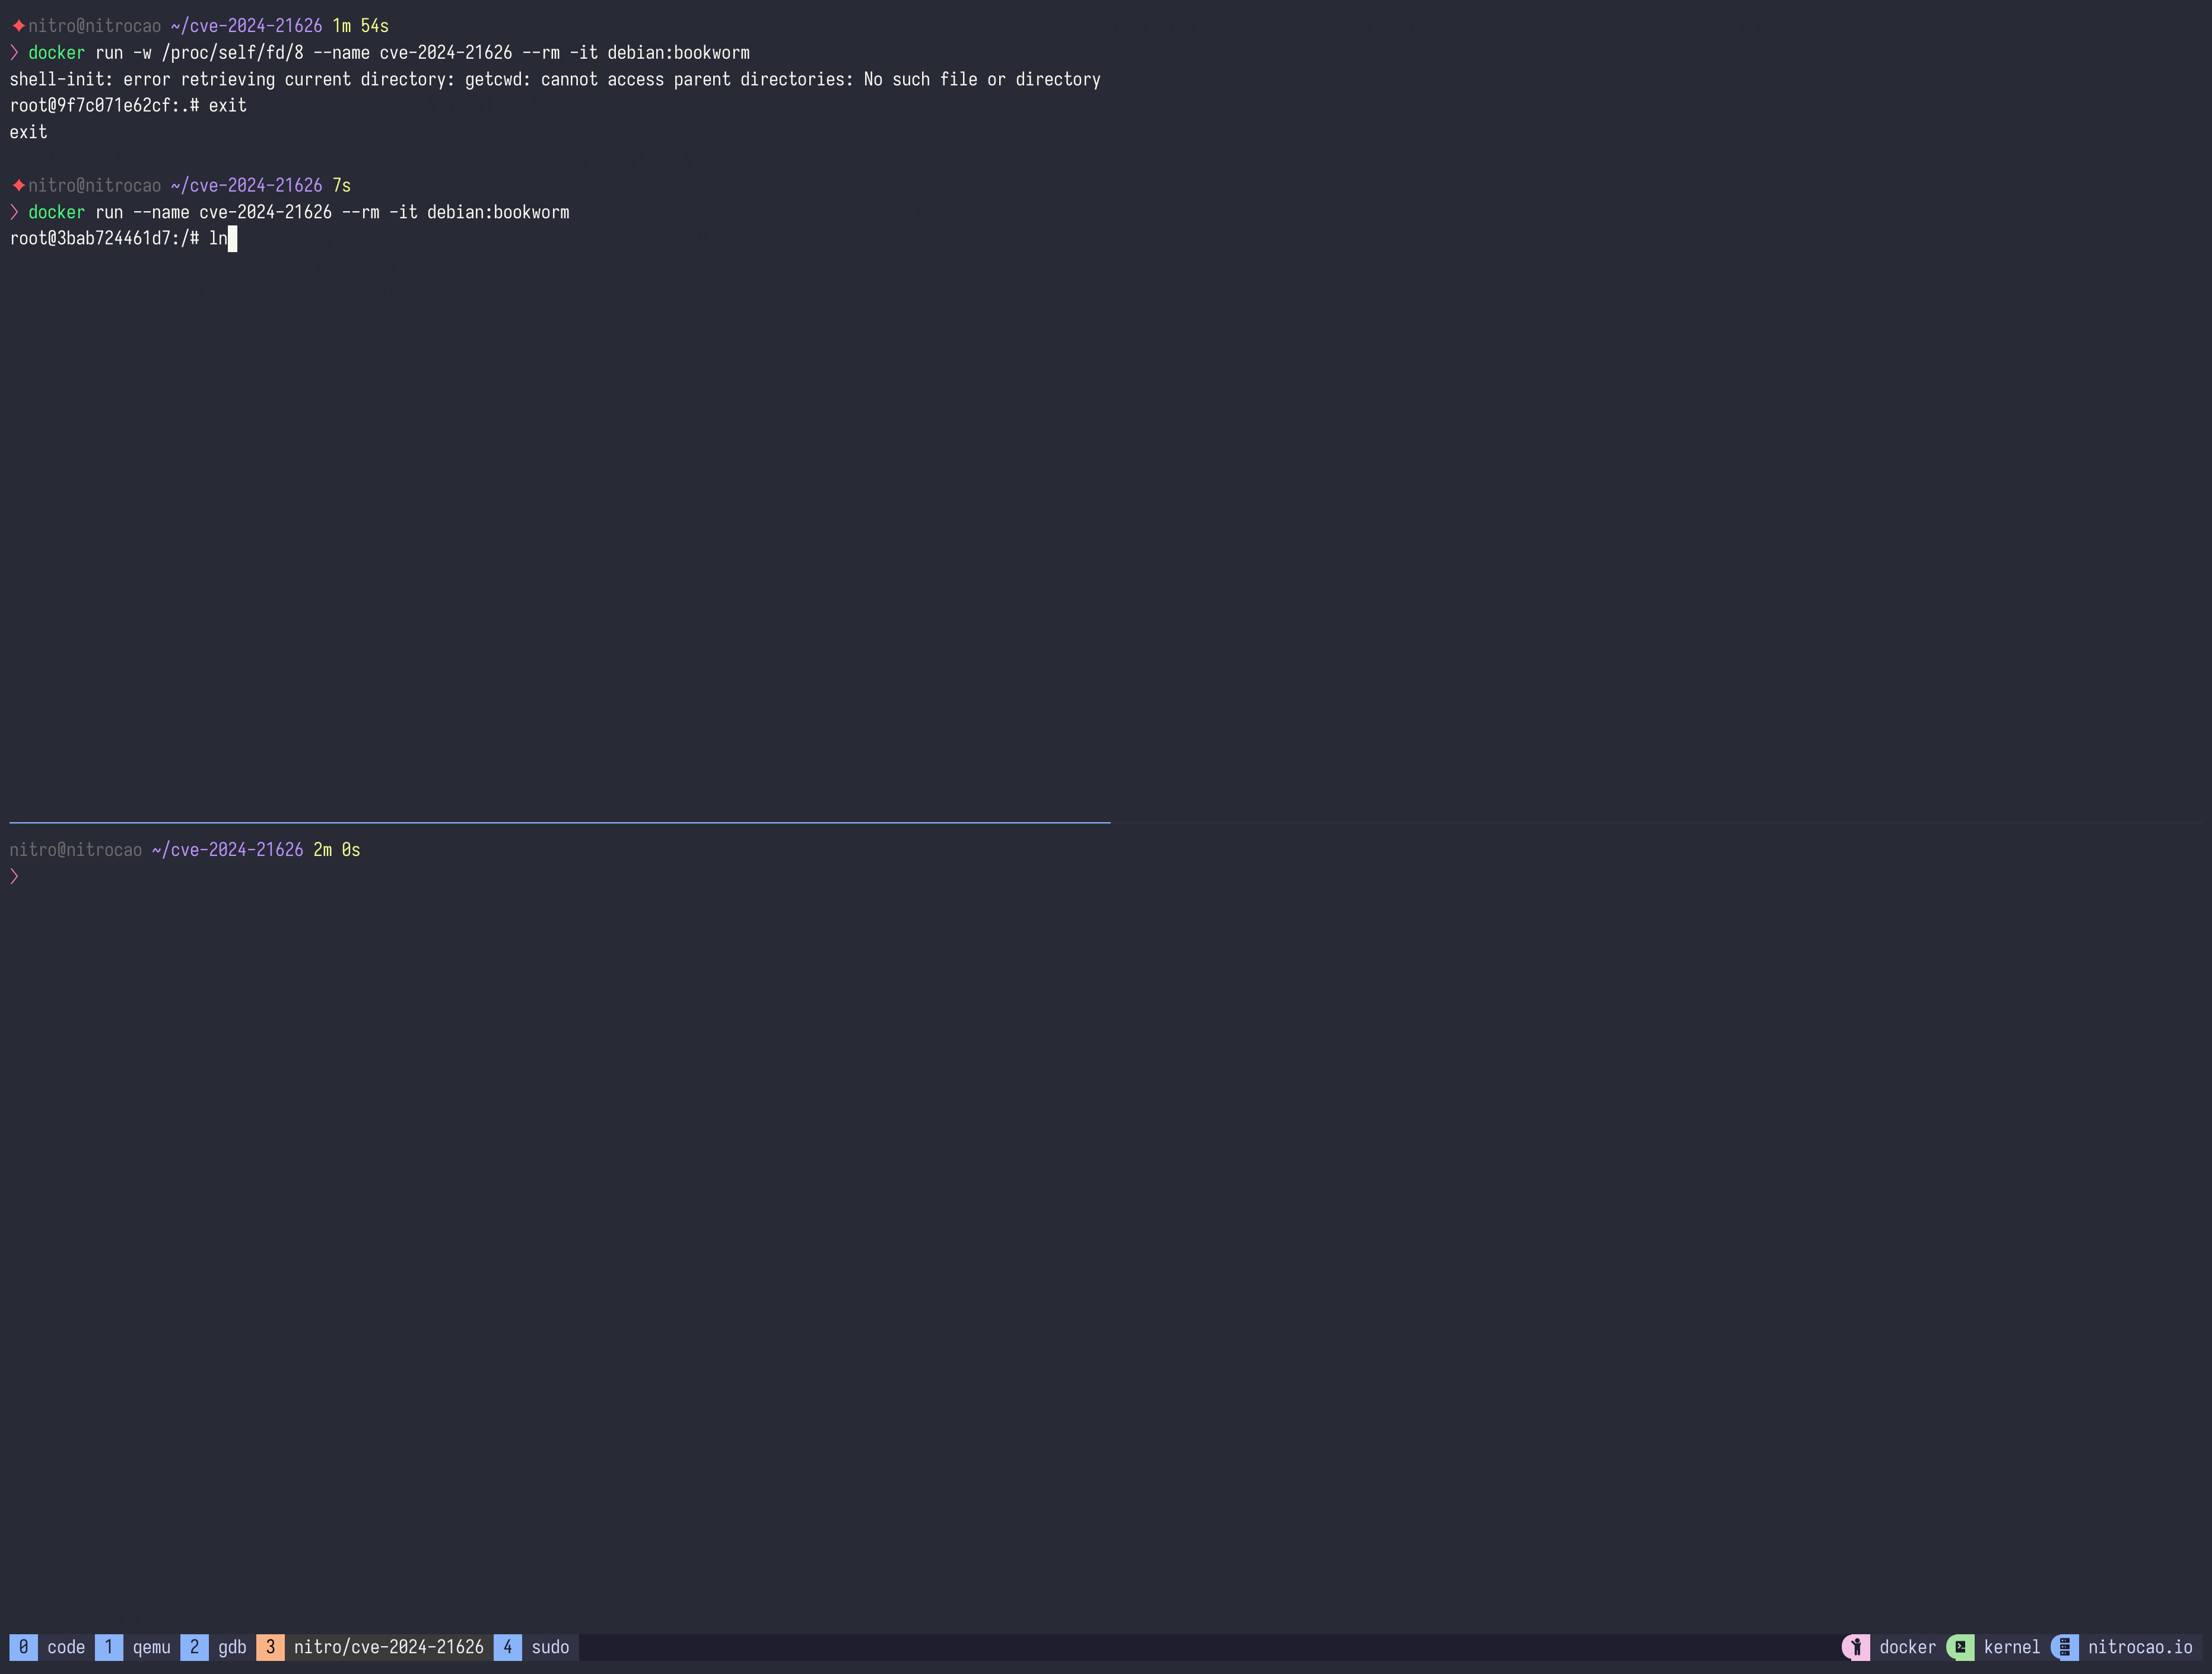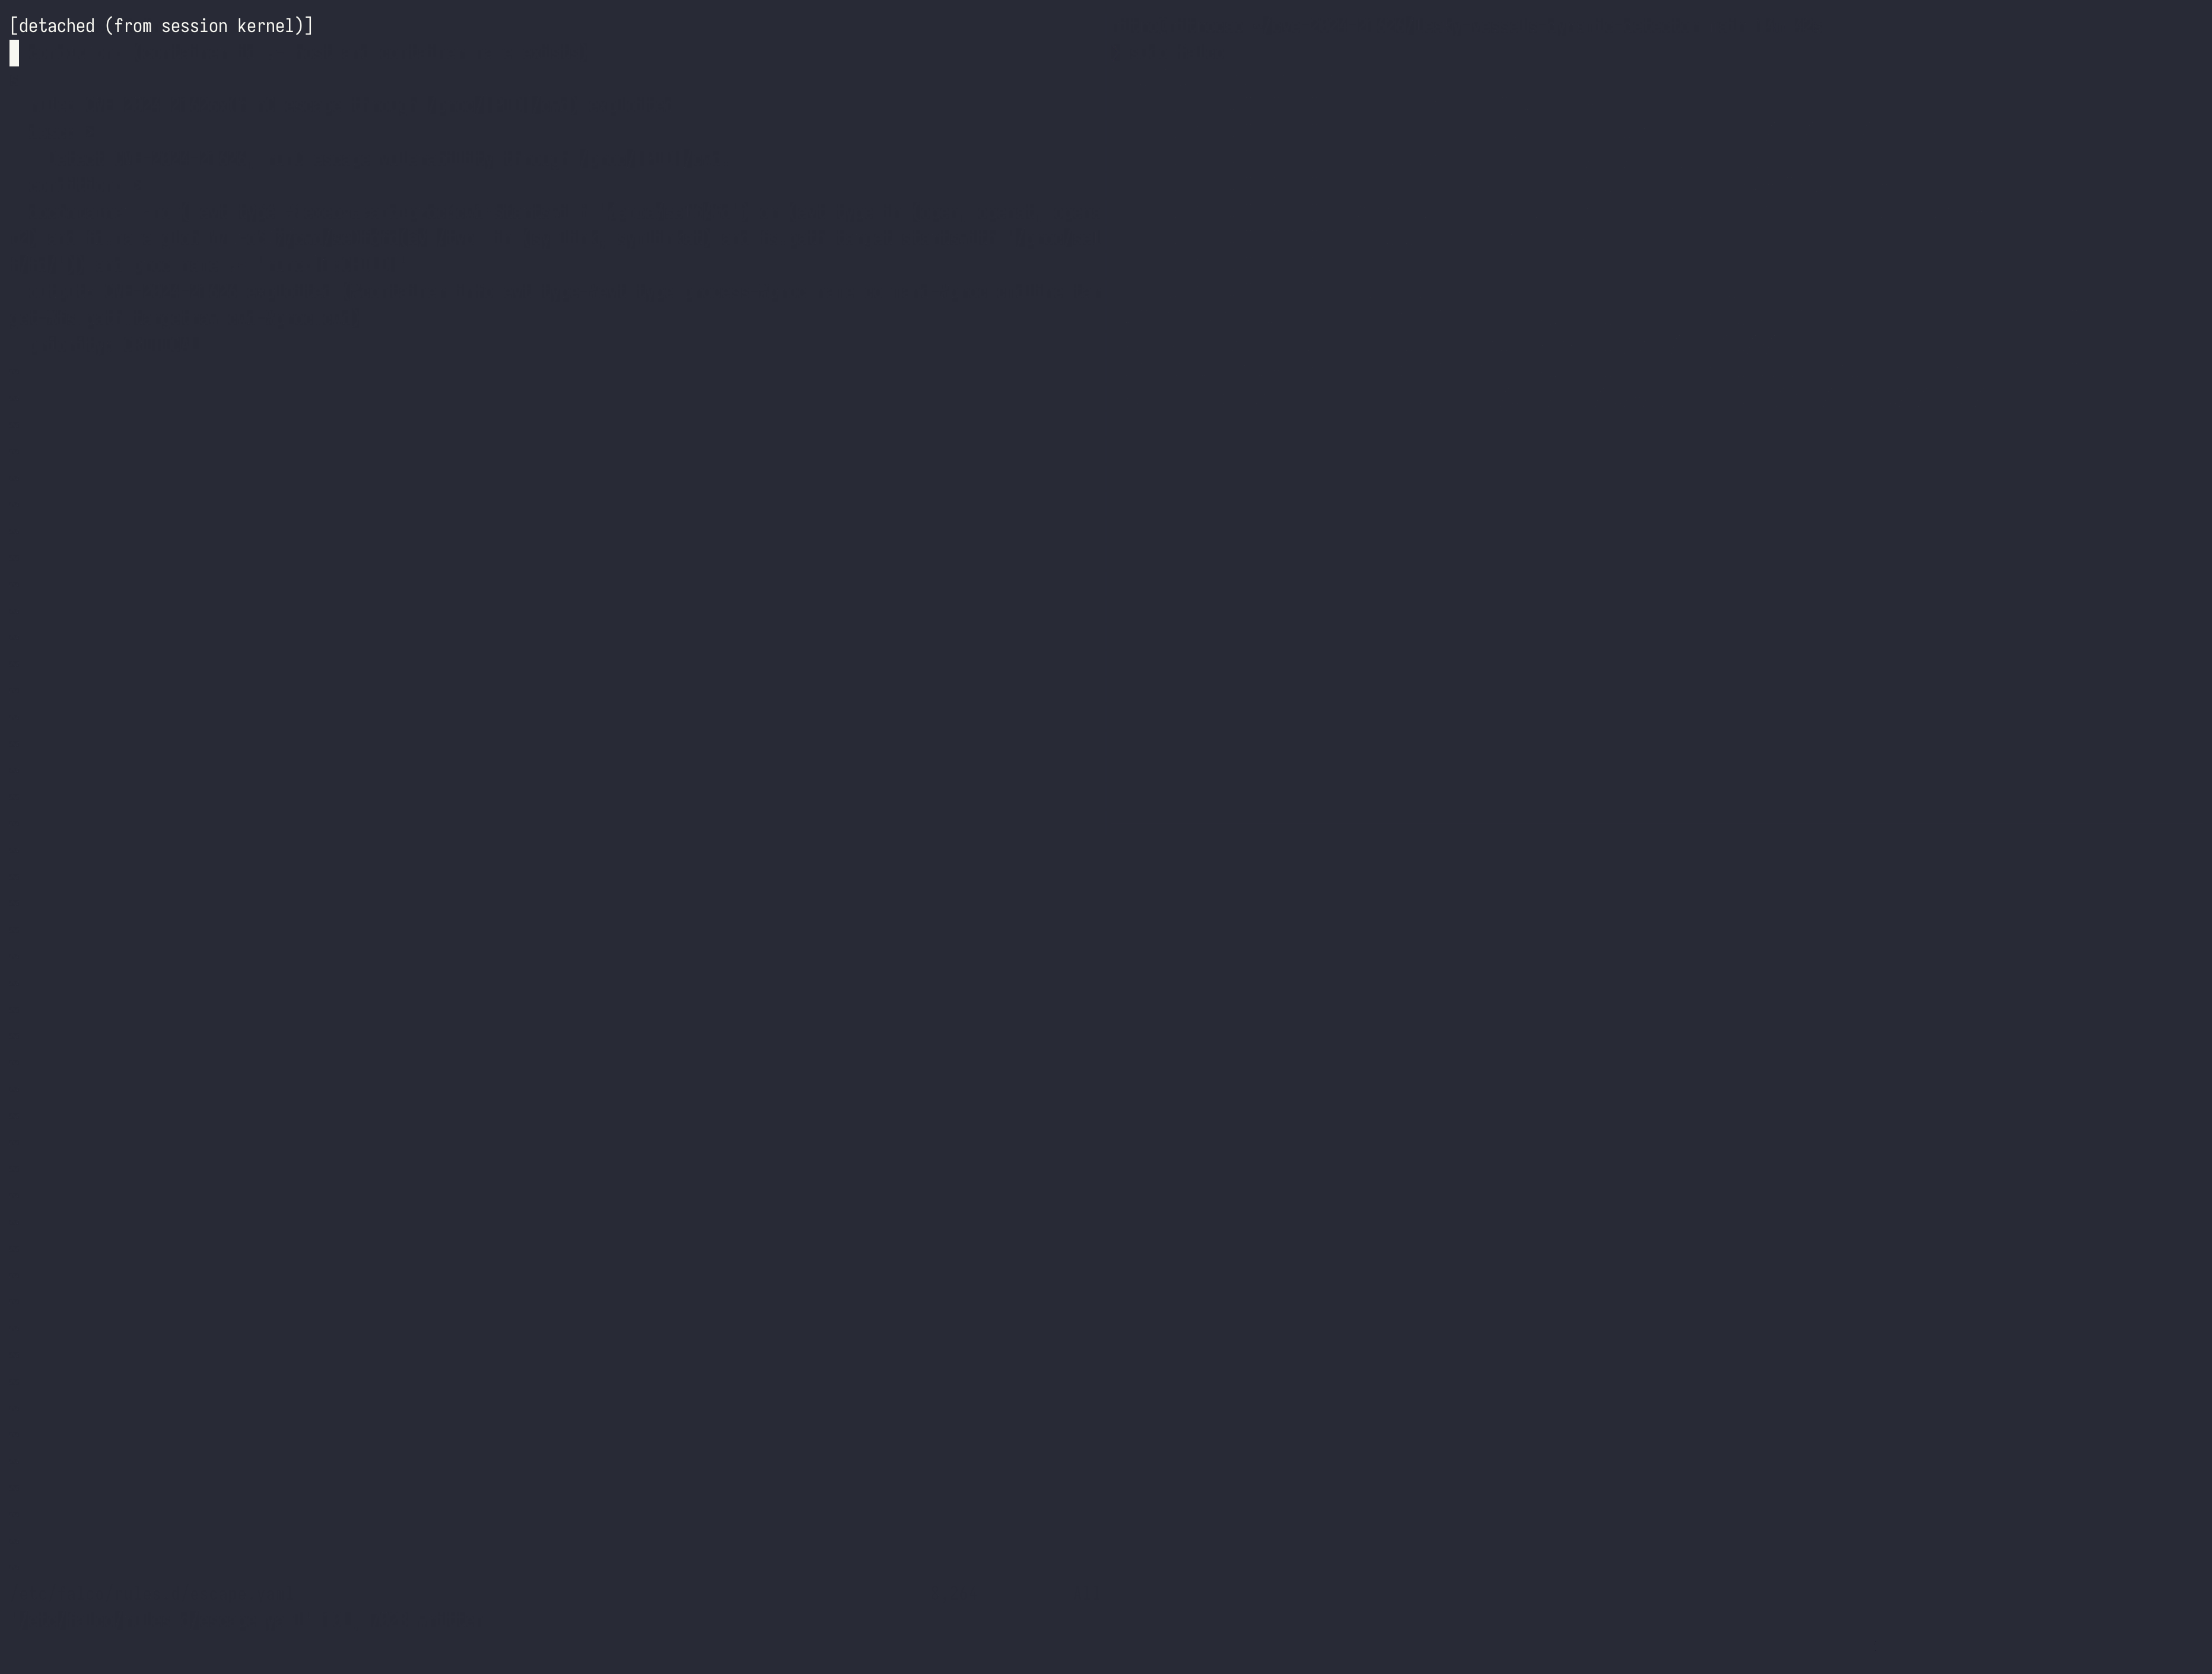 nitrocao/cve-2024-21626
PoC and Detection for CVE-2024-21626
 spiralbl0ck/cve-2023-1206-cve-2025-40040-cve-2024-49882
3 linux kernel bugs chains to do secure comm app using side channel to establish key and establish covert channe;
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
 thekevinday/docker_lightman_exploit
Docker CVE-2022-37708