
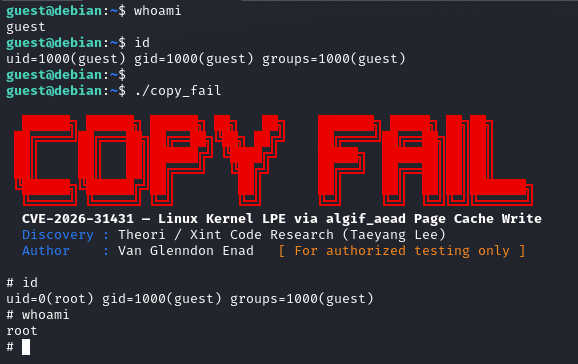
CVE-2026-31431-PoC
 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
binary-exploitationcontainer-escapeexploitation+4
4
sl4ck0th/cve-2026-31431-pocProof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 ishankaru/cve-2026-23111-nftables-lab
Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…
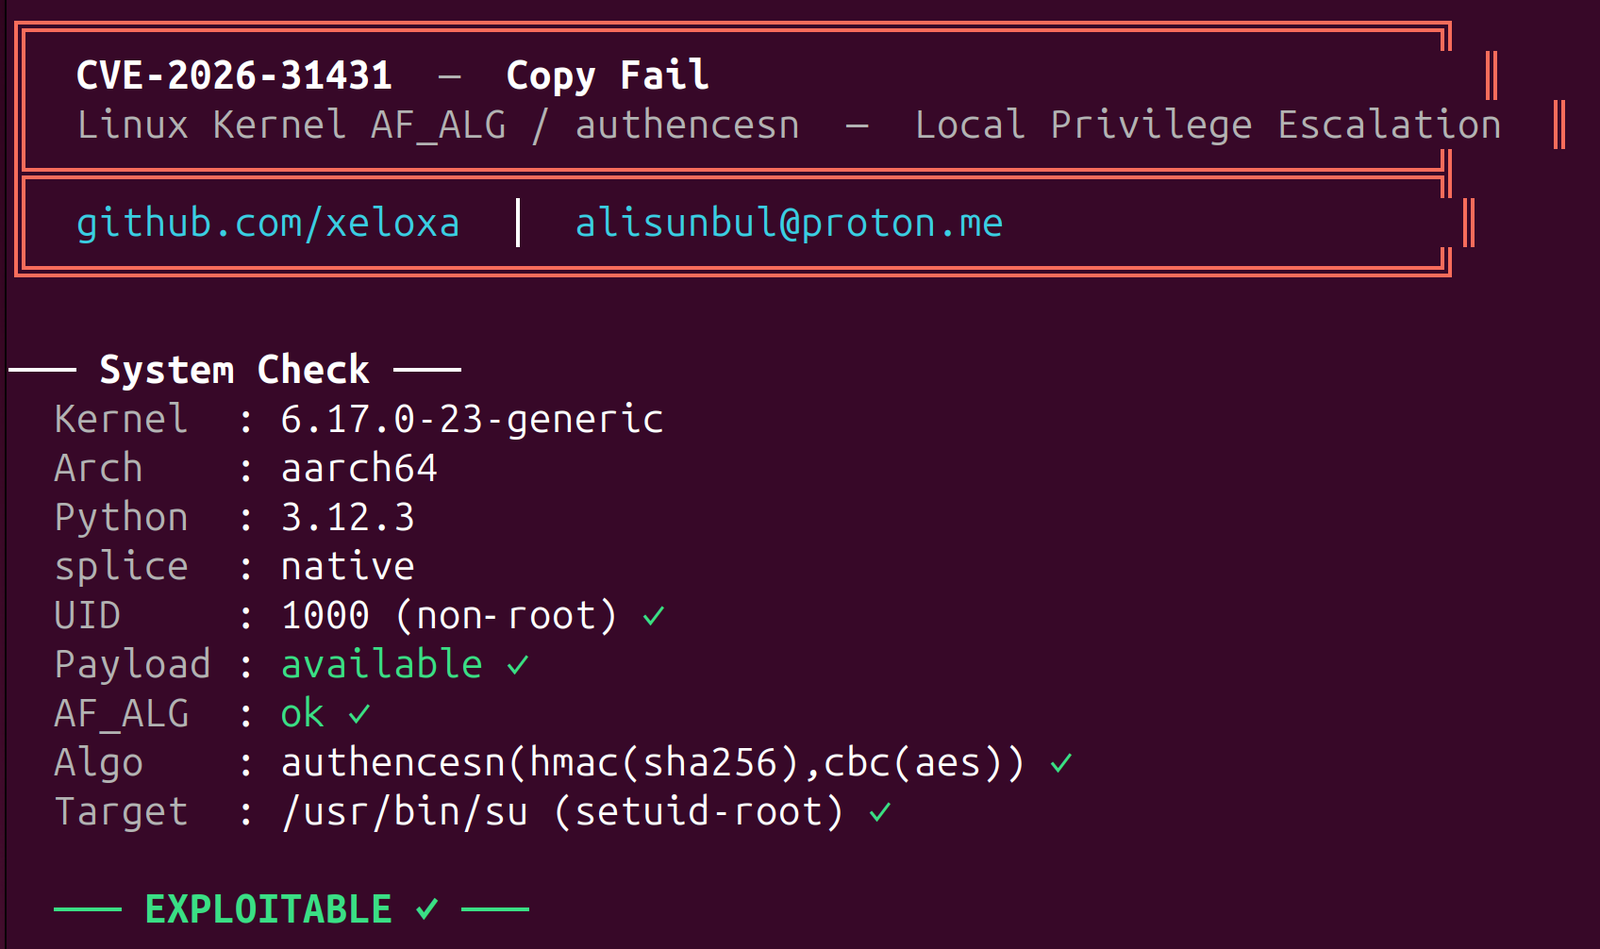 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
 mishl-dev/cve_2026_31431
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…
 prabeershakya/cve-2022-0185-poc
Proof-of-concept exploit for CVE-2022-0185, a Linux kernel heap buffer overflow enabling local privilege escalation and container escape via FUSE and…
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
 teawater/cve-2017-5123
Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…
 1neptune/copyfail
go CVE-2026-31431 (CopyFail) local privilege escalation exploit
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit