
insject
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
container-escapecontainer-securitypenetration-testing+1
50
nccgroup/insjectinsject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
 skysbsb/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in Docker/runc. Demonstrates file descriptor manipulation to break out…
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 teawater/cve-2017-5123
Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…
 datadog/dirtypipe-container-breakout-poc
Container Excape PoC for CVE-2022-0847 "DirtyPipe"
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
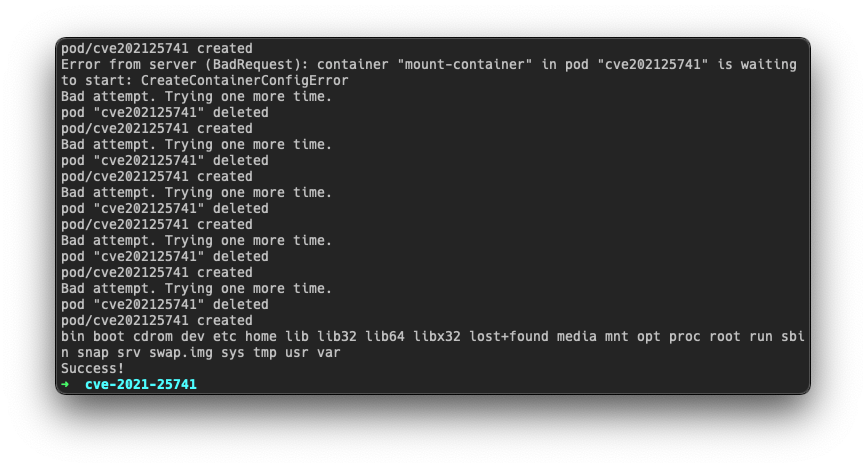 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 likekabin/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, appending a payload to the host runc binary via Docker container escape.
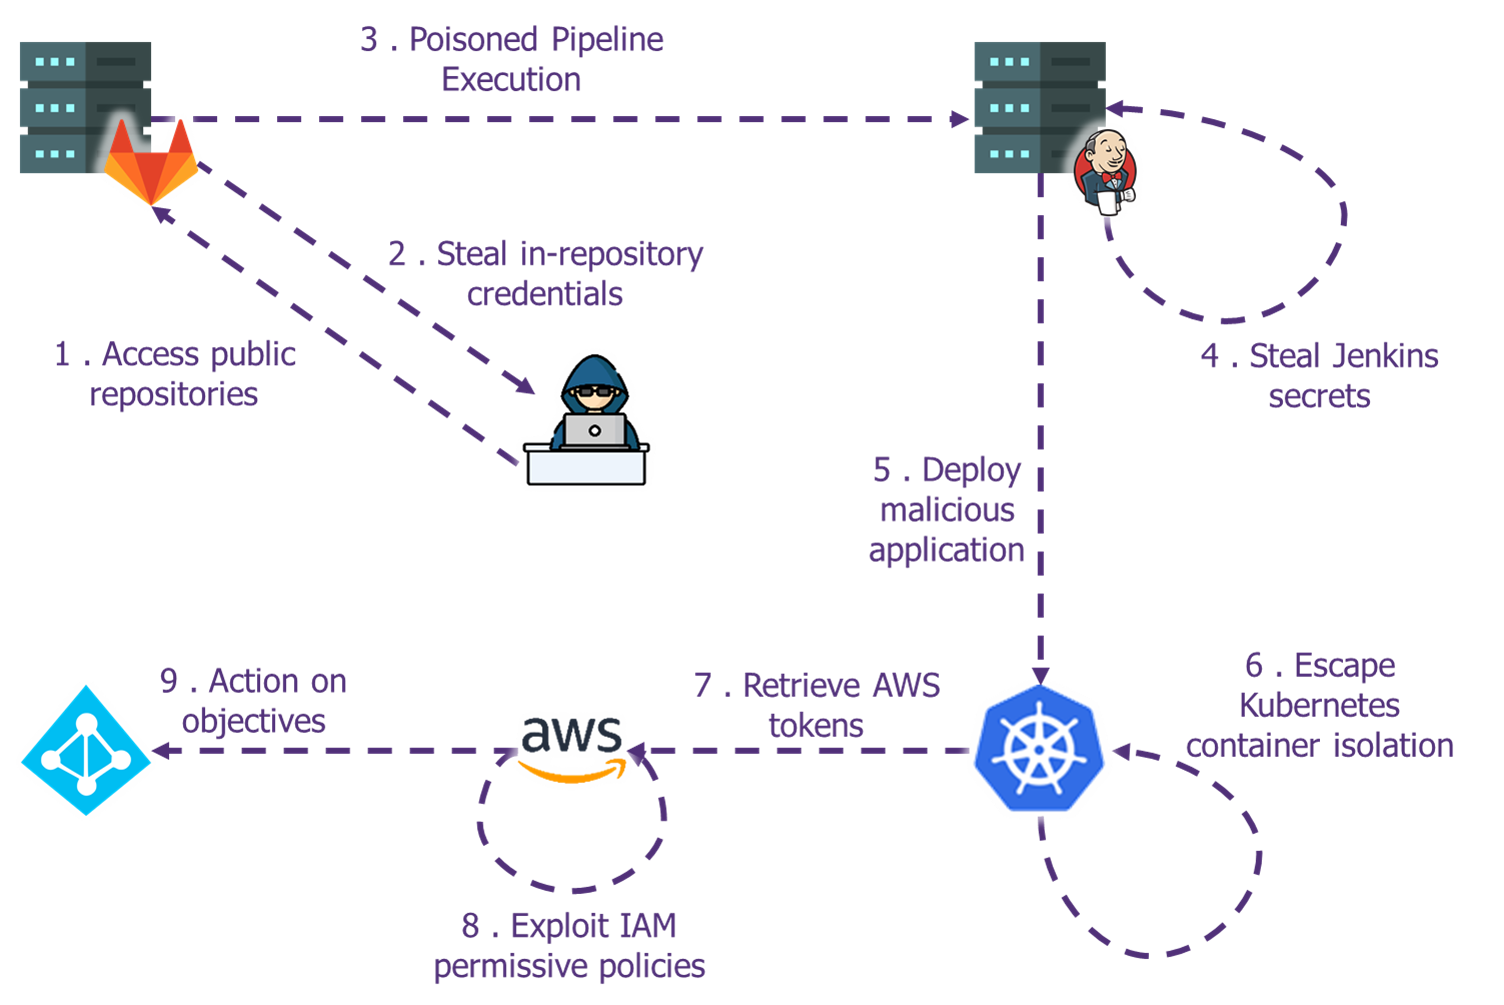 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
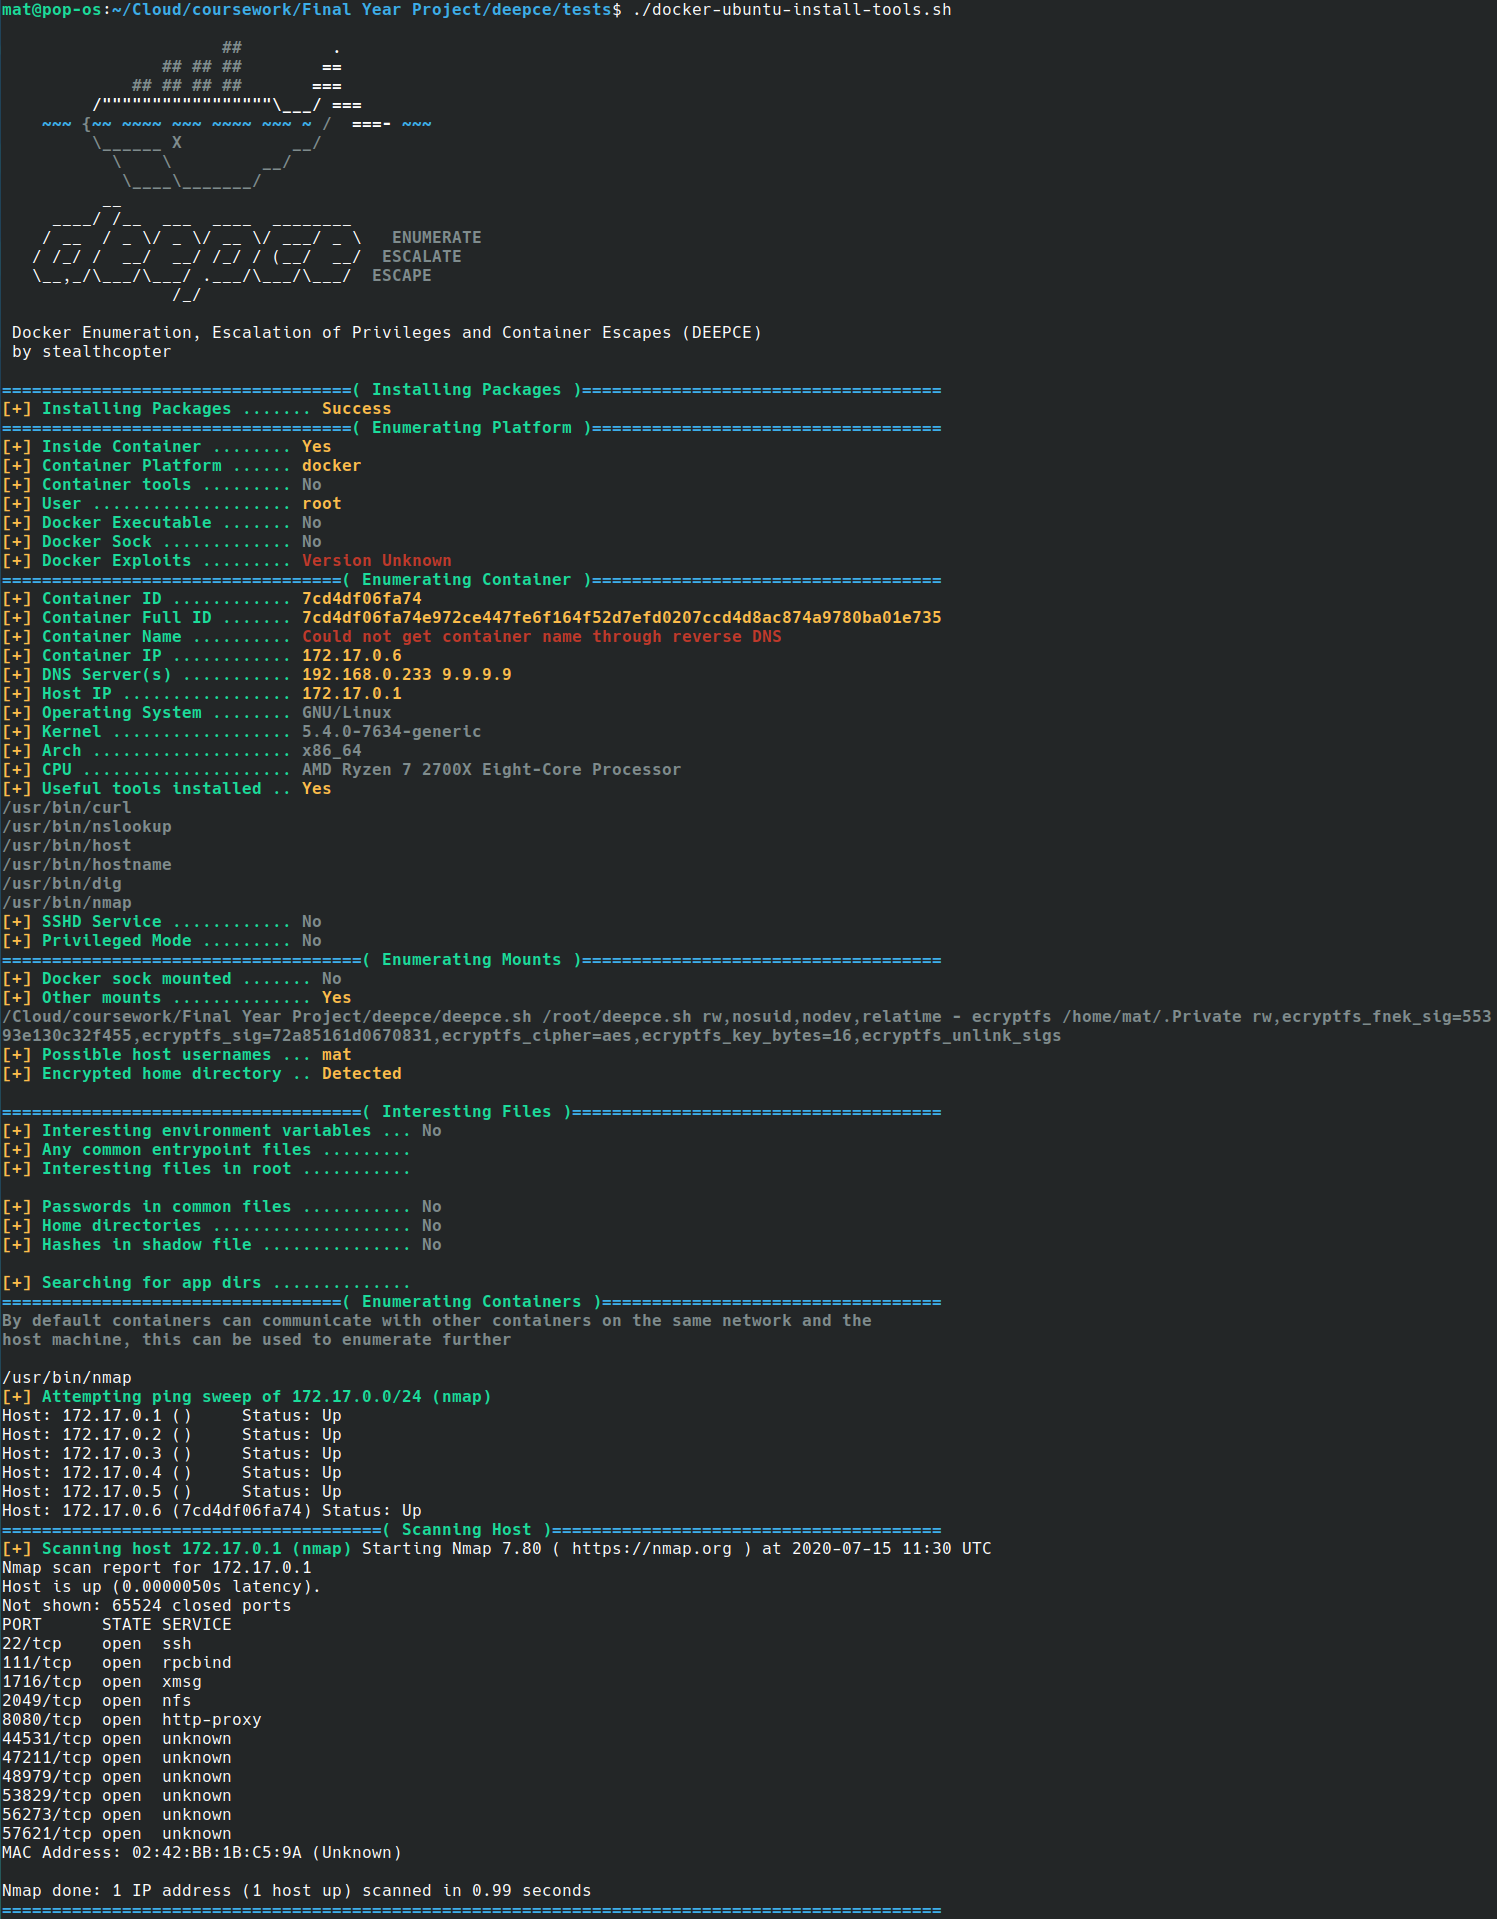 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 kagami/docker_cve-2015-2925
Docker + CVE-2015-2925 = escaping from --volume
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.