cve-2019-5736-reproducer

Reproducer for CVE-2019-5736, a RunC container escape vulnerability. Provides build scripts and a KVM-based lab to confirm the exploit against…

Reproducer for CVE-2019-5736, a RunC container escape vulnerability. Provides build scripts and a KVM-based lab to confirm the exploit against…

Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…

📦 Make security testing of K8s, Docker, and Containerd easier.

Peirates - Kubernetes Penetration Testing tool

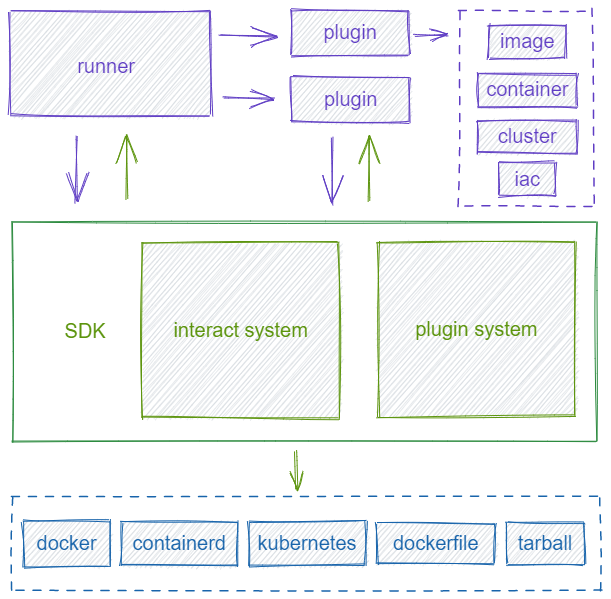
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集

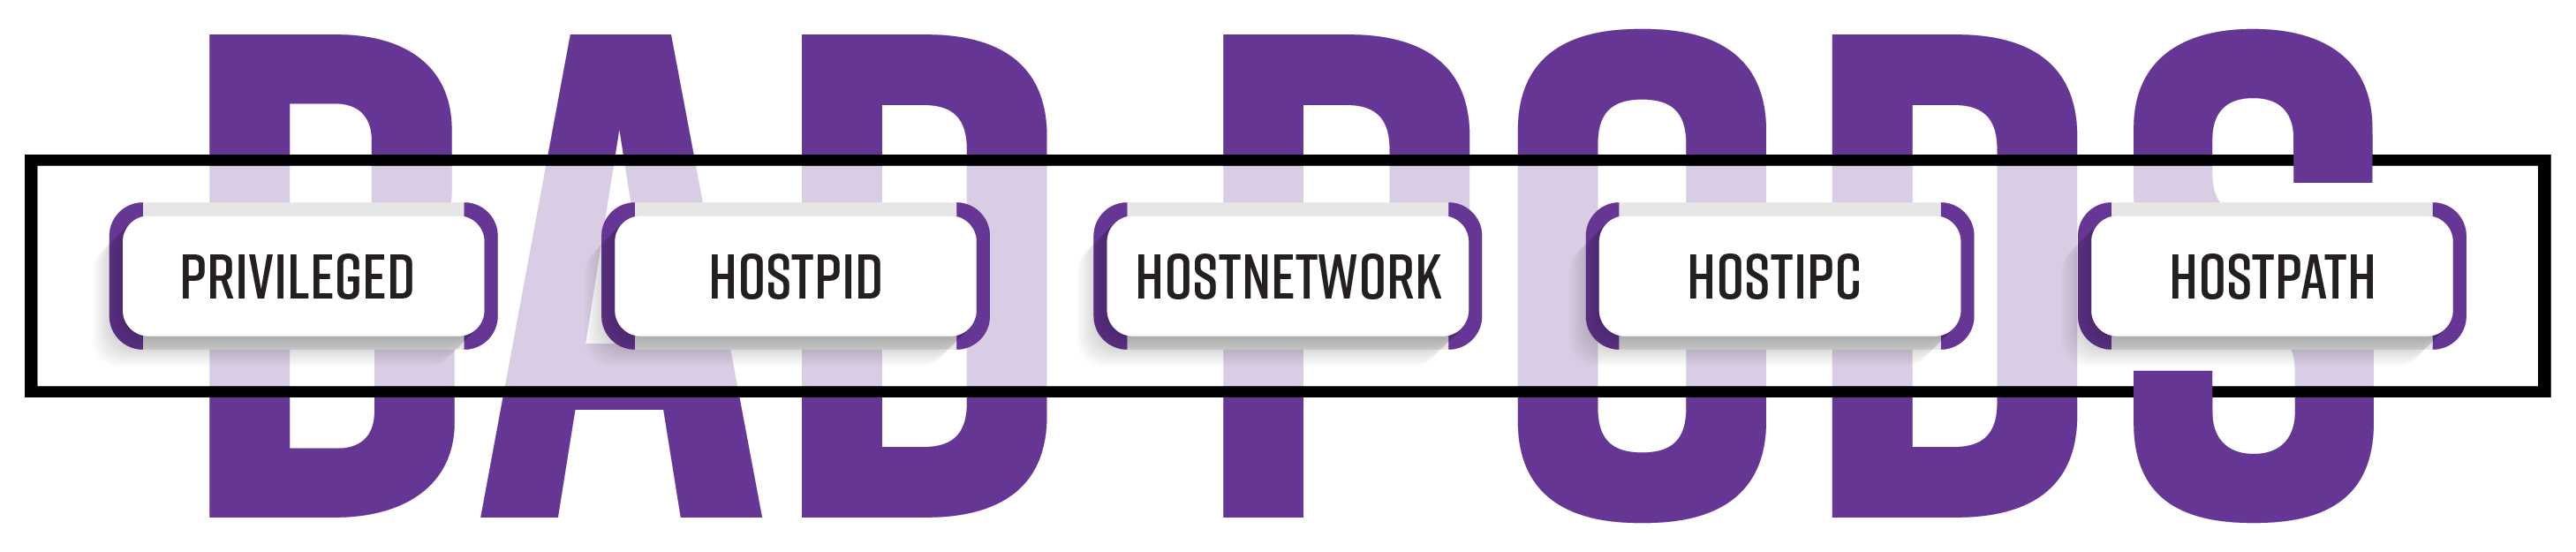
A collection of manifests that will create pods with elevated privileges.

A container analysis and exploitation tool for pentesters and engineers.

PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…

Fawkes is a golang Mythic C2 Agent exclusively written by AI.

Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…

Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…

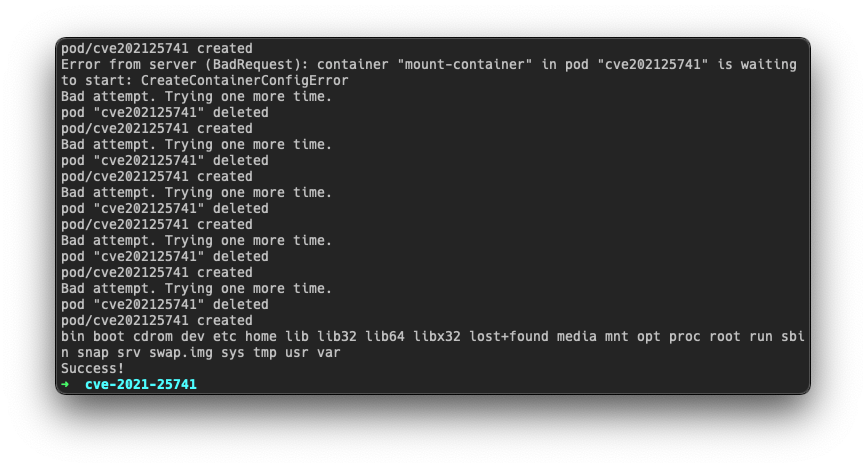
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…

Writeup of CVE-2017-1002101 with sample "exploit"/escape

Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…

Proof-of-concept exploit for CVE-2025-23266 (NVIDIAScape) targeting NVIDIA AI container runtime. Demonstrates container escape via GPU driver…

Proof of concept for CVE-2020-15257 in containerd.

A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492