
grype
 anchore/grype
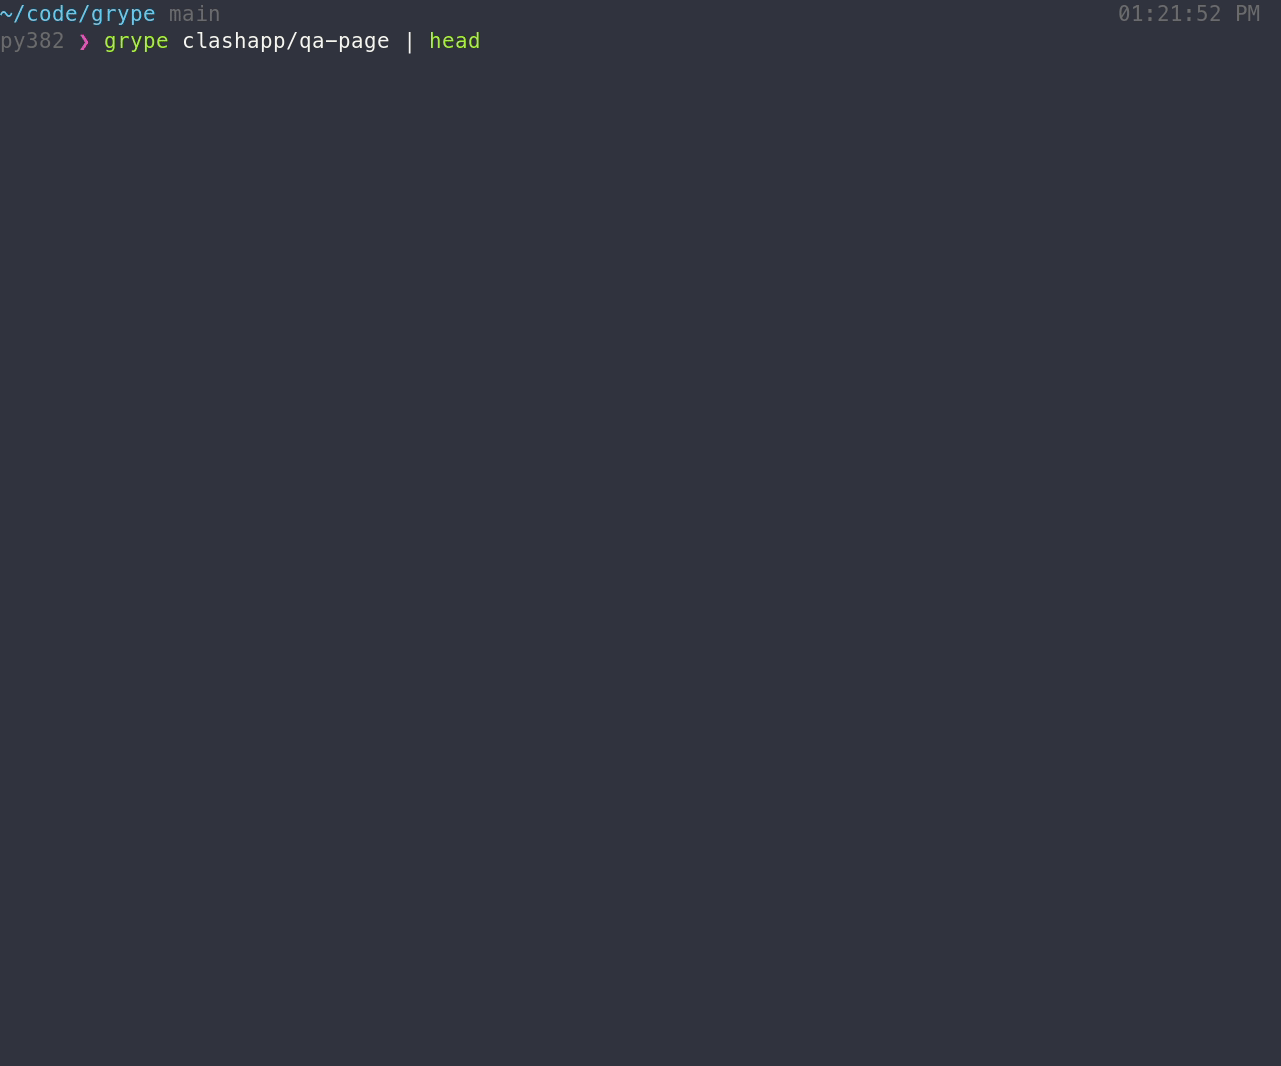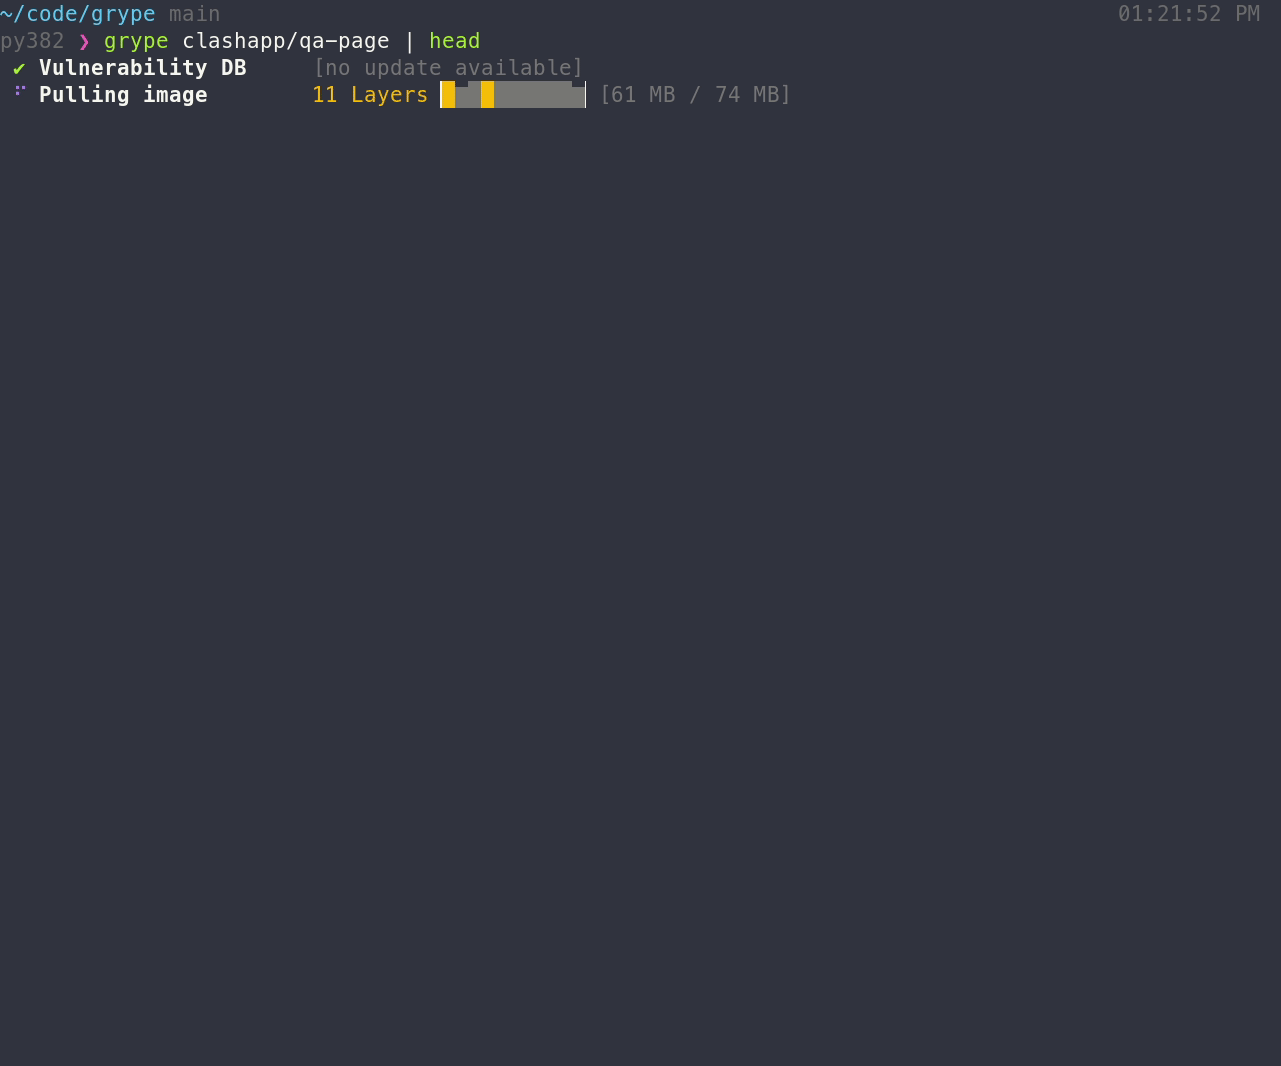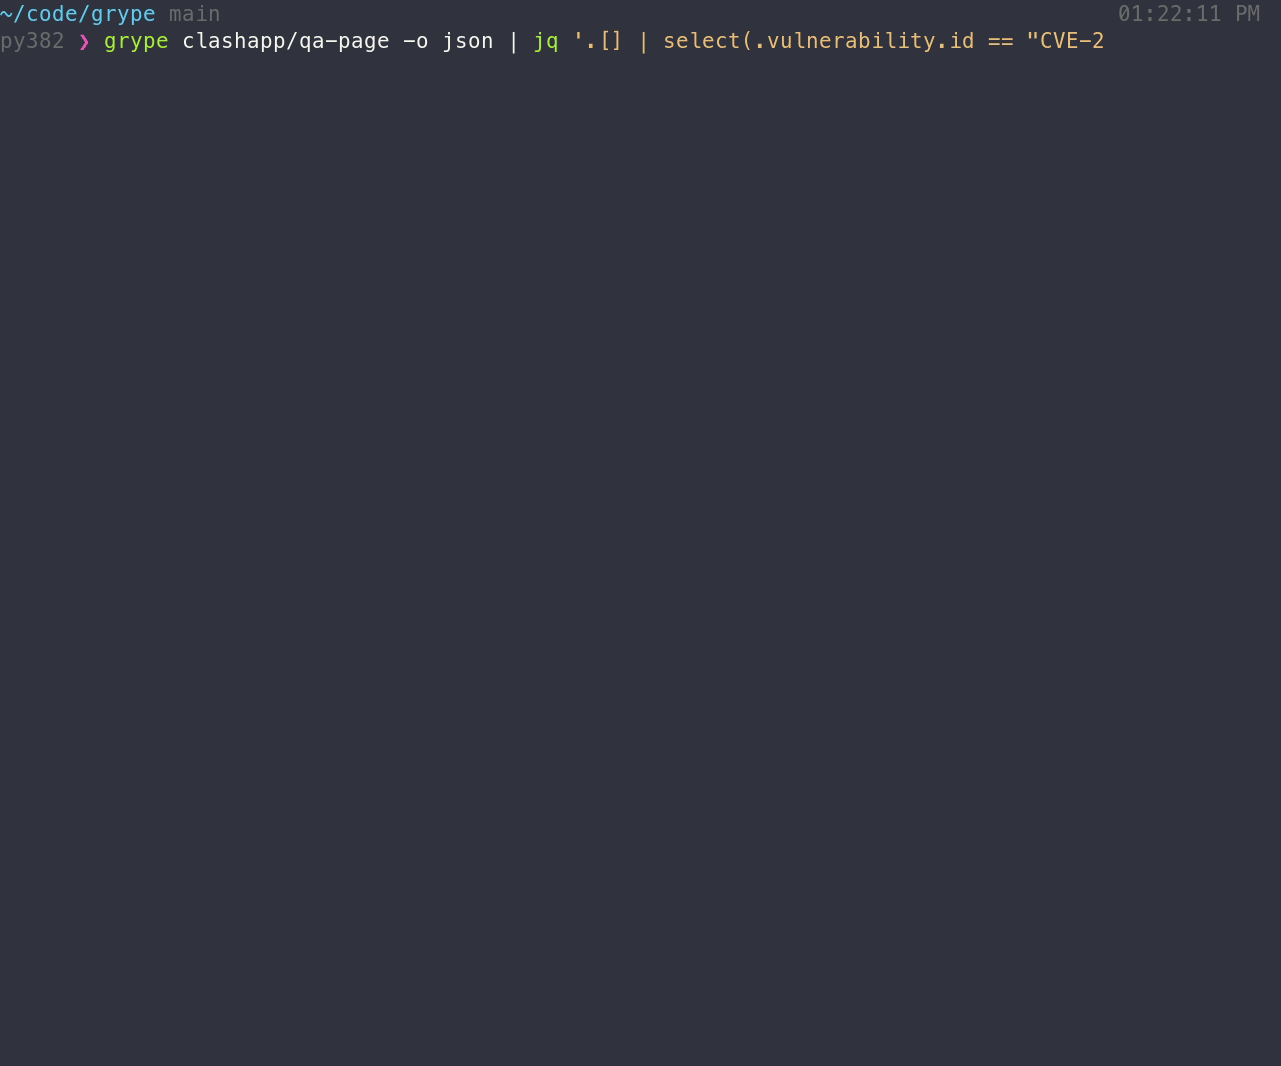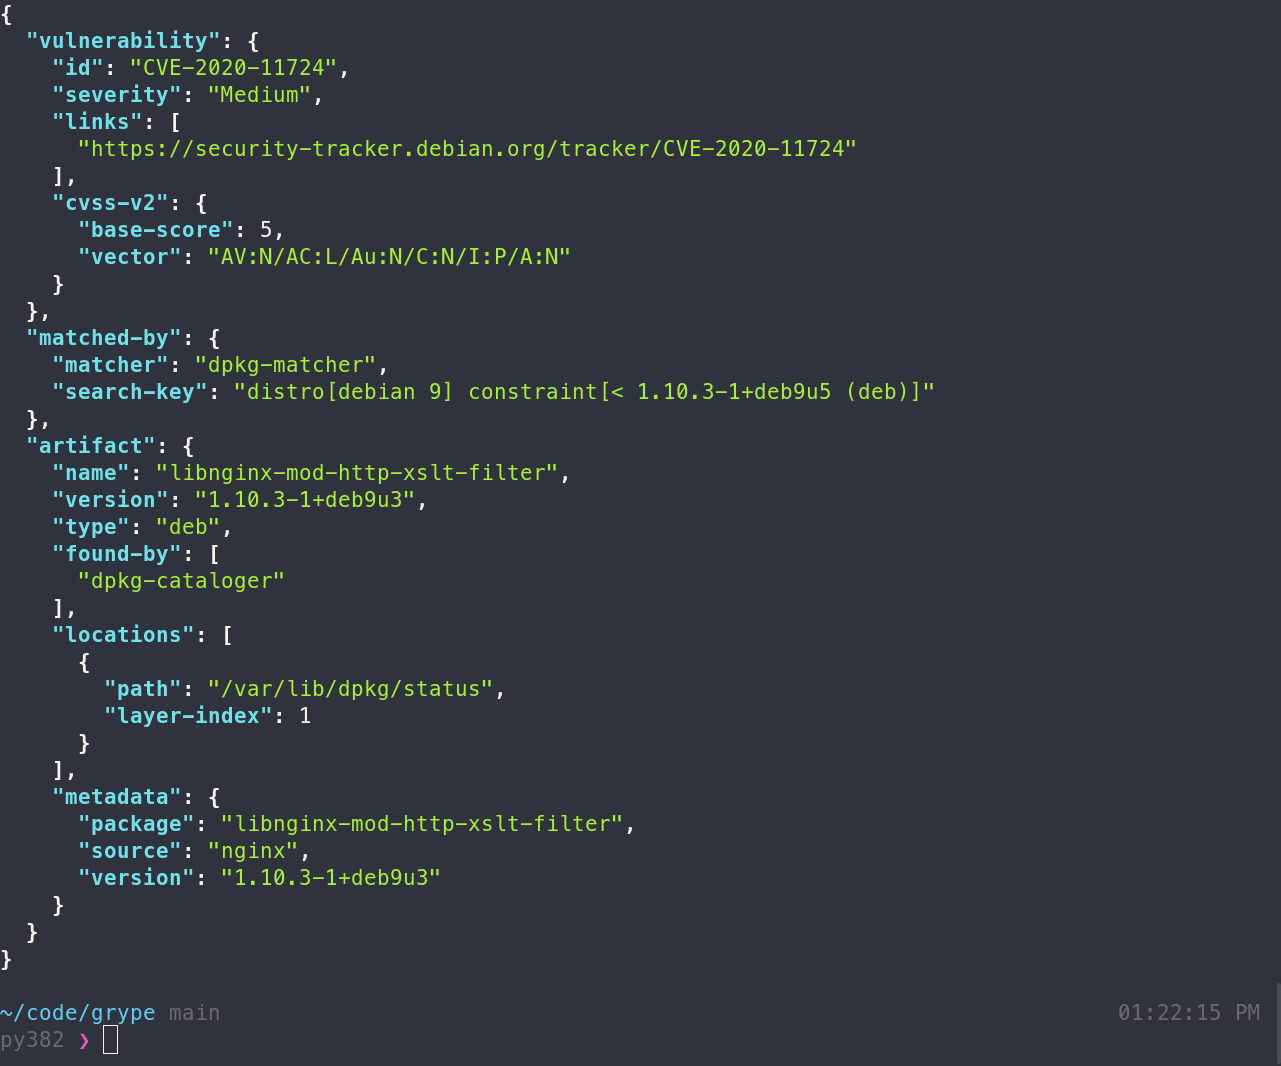
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
12.9k1 day ago
anchore/grypeA vulnerability scanner for container images and filesystems
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
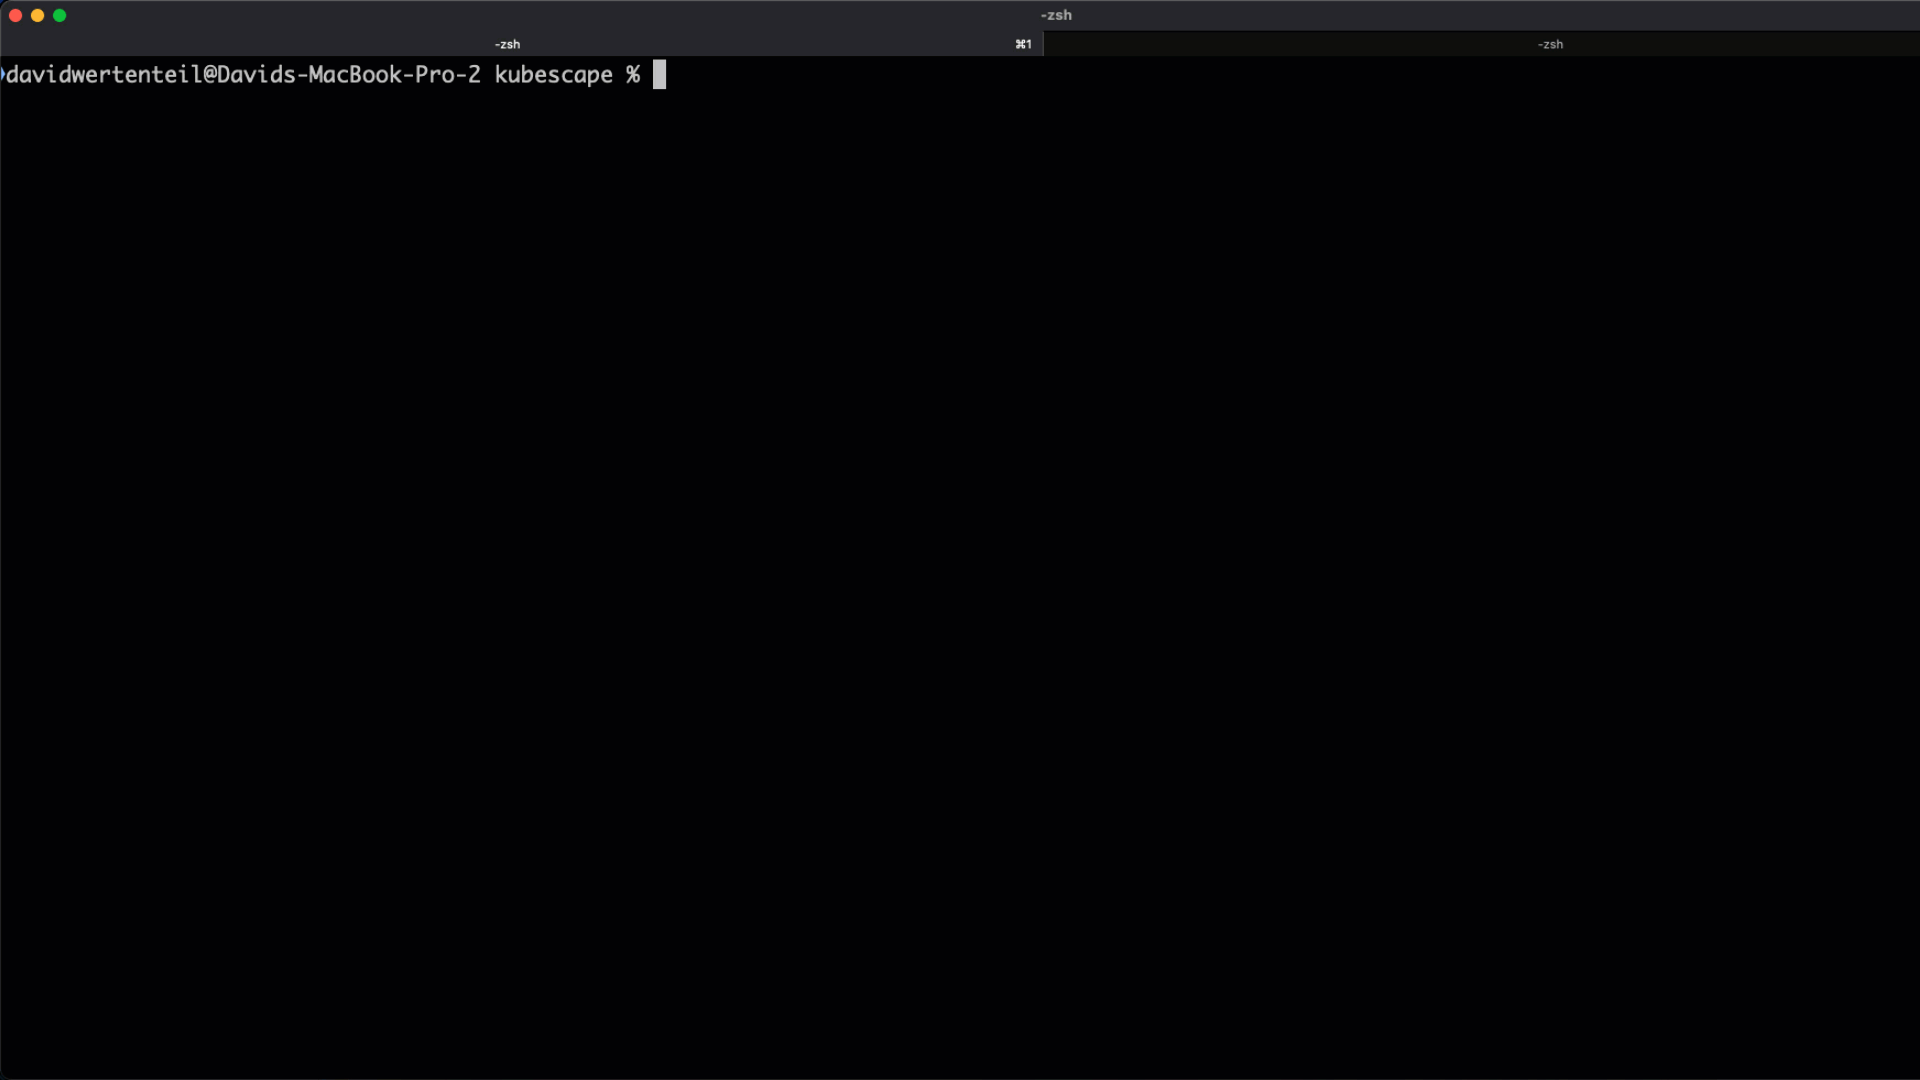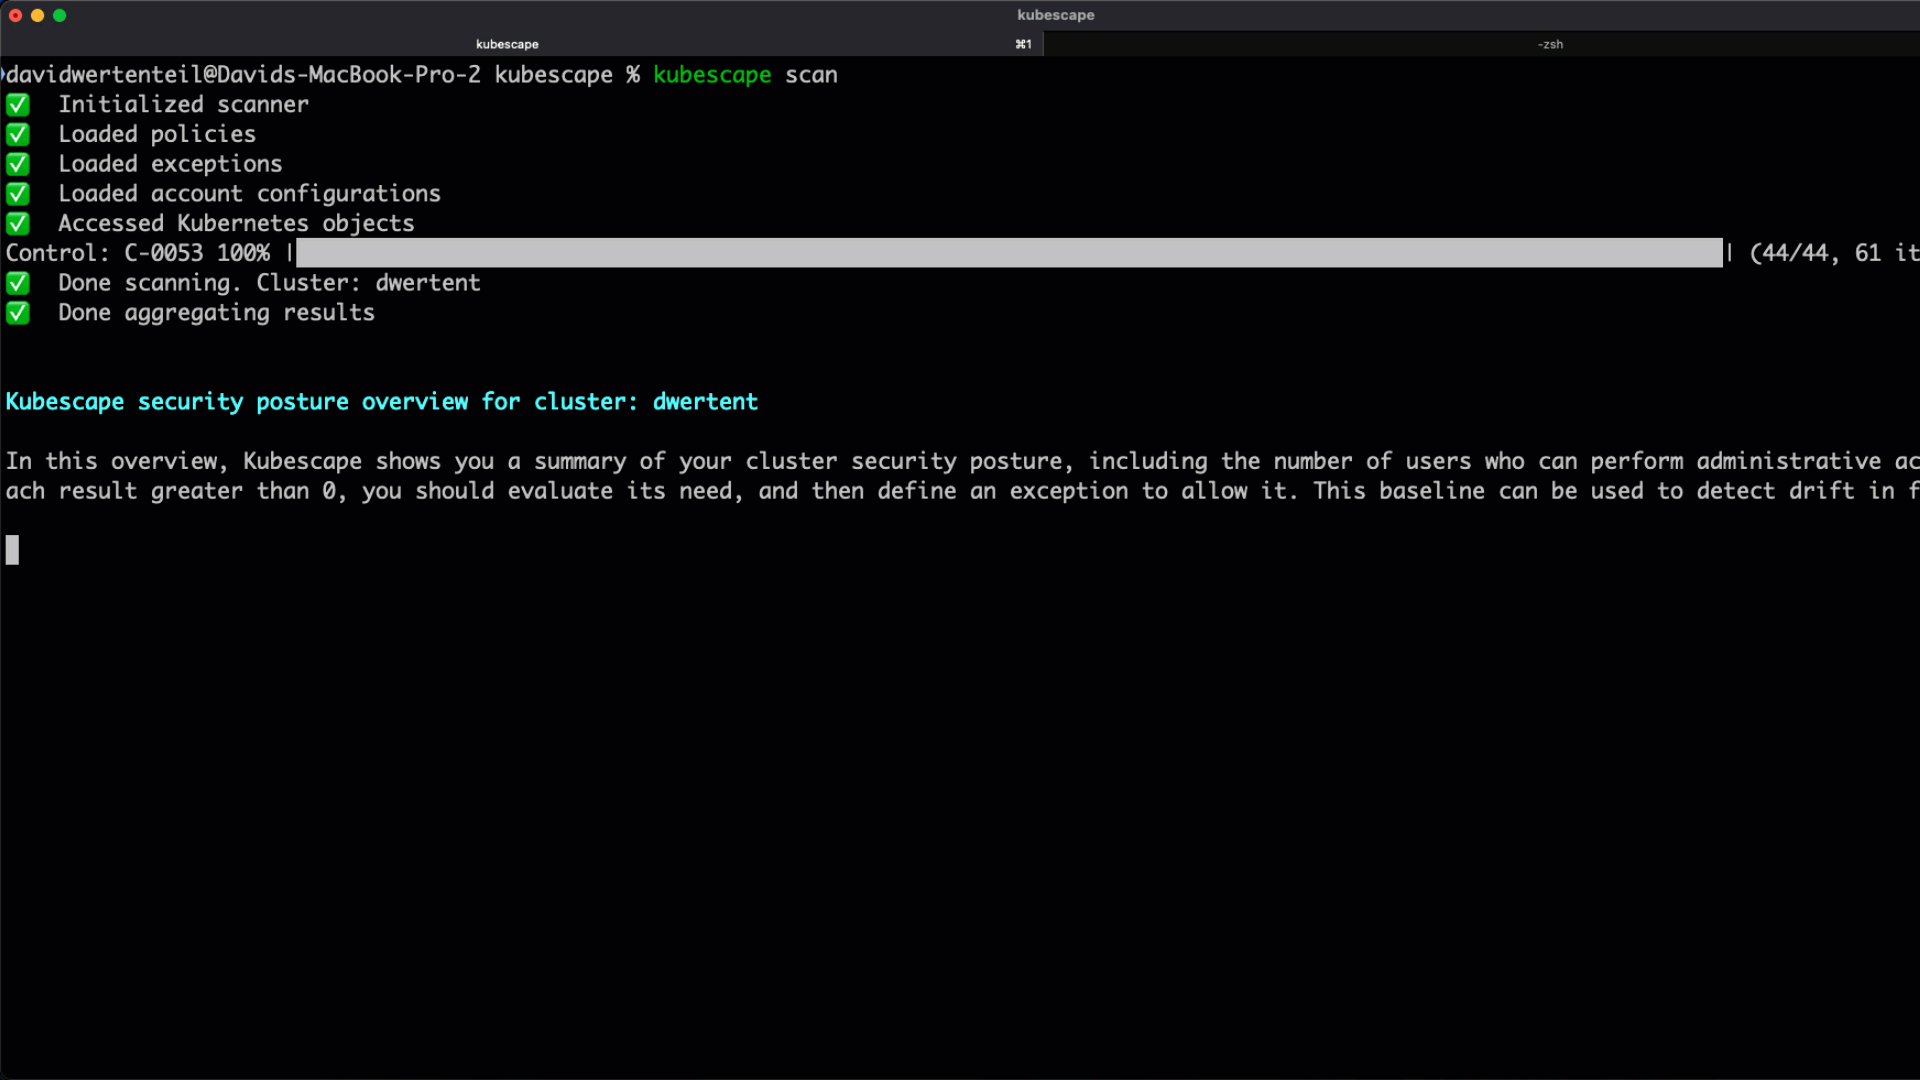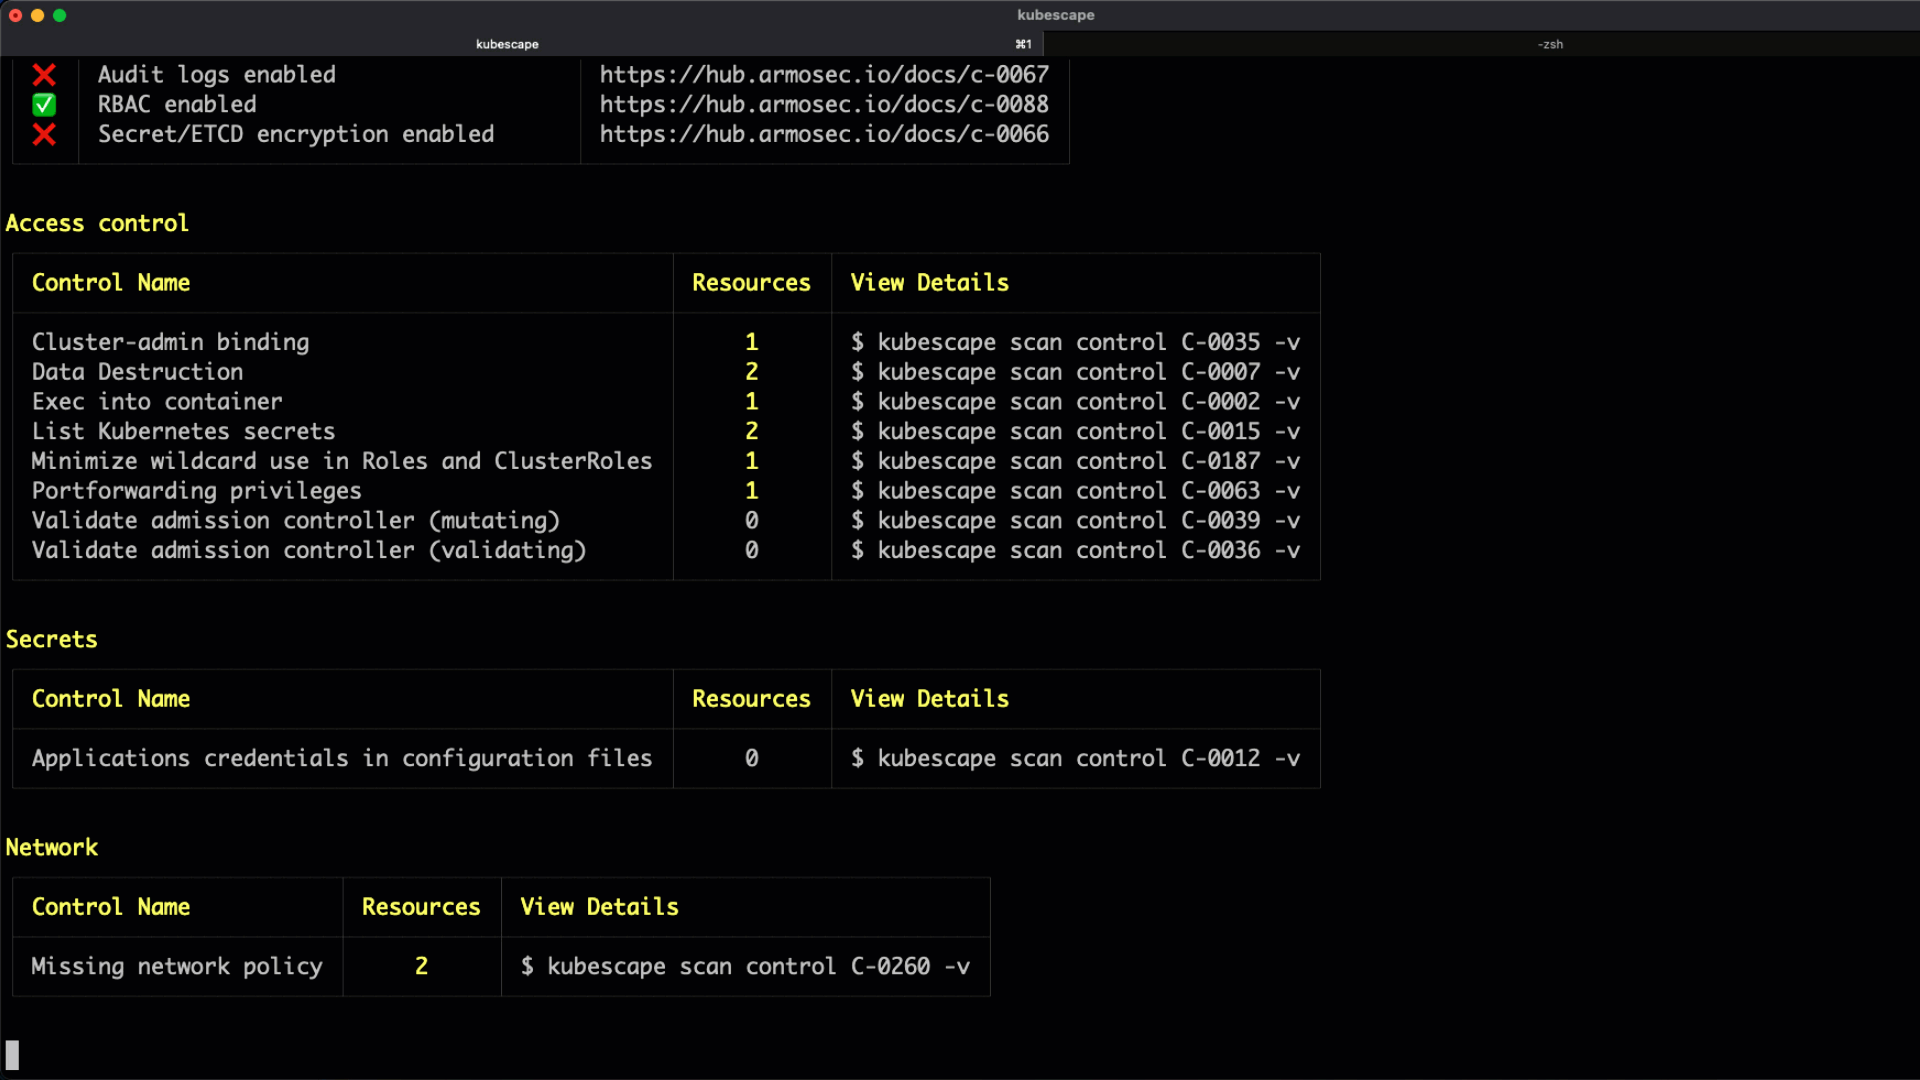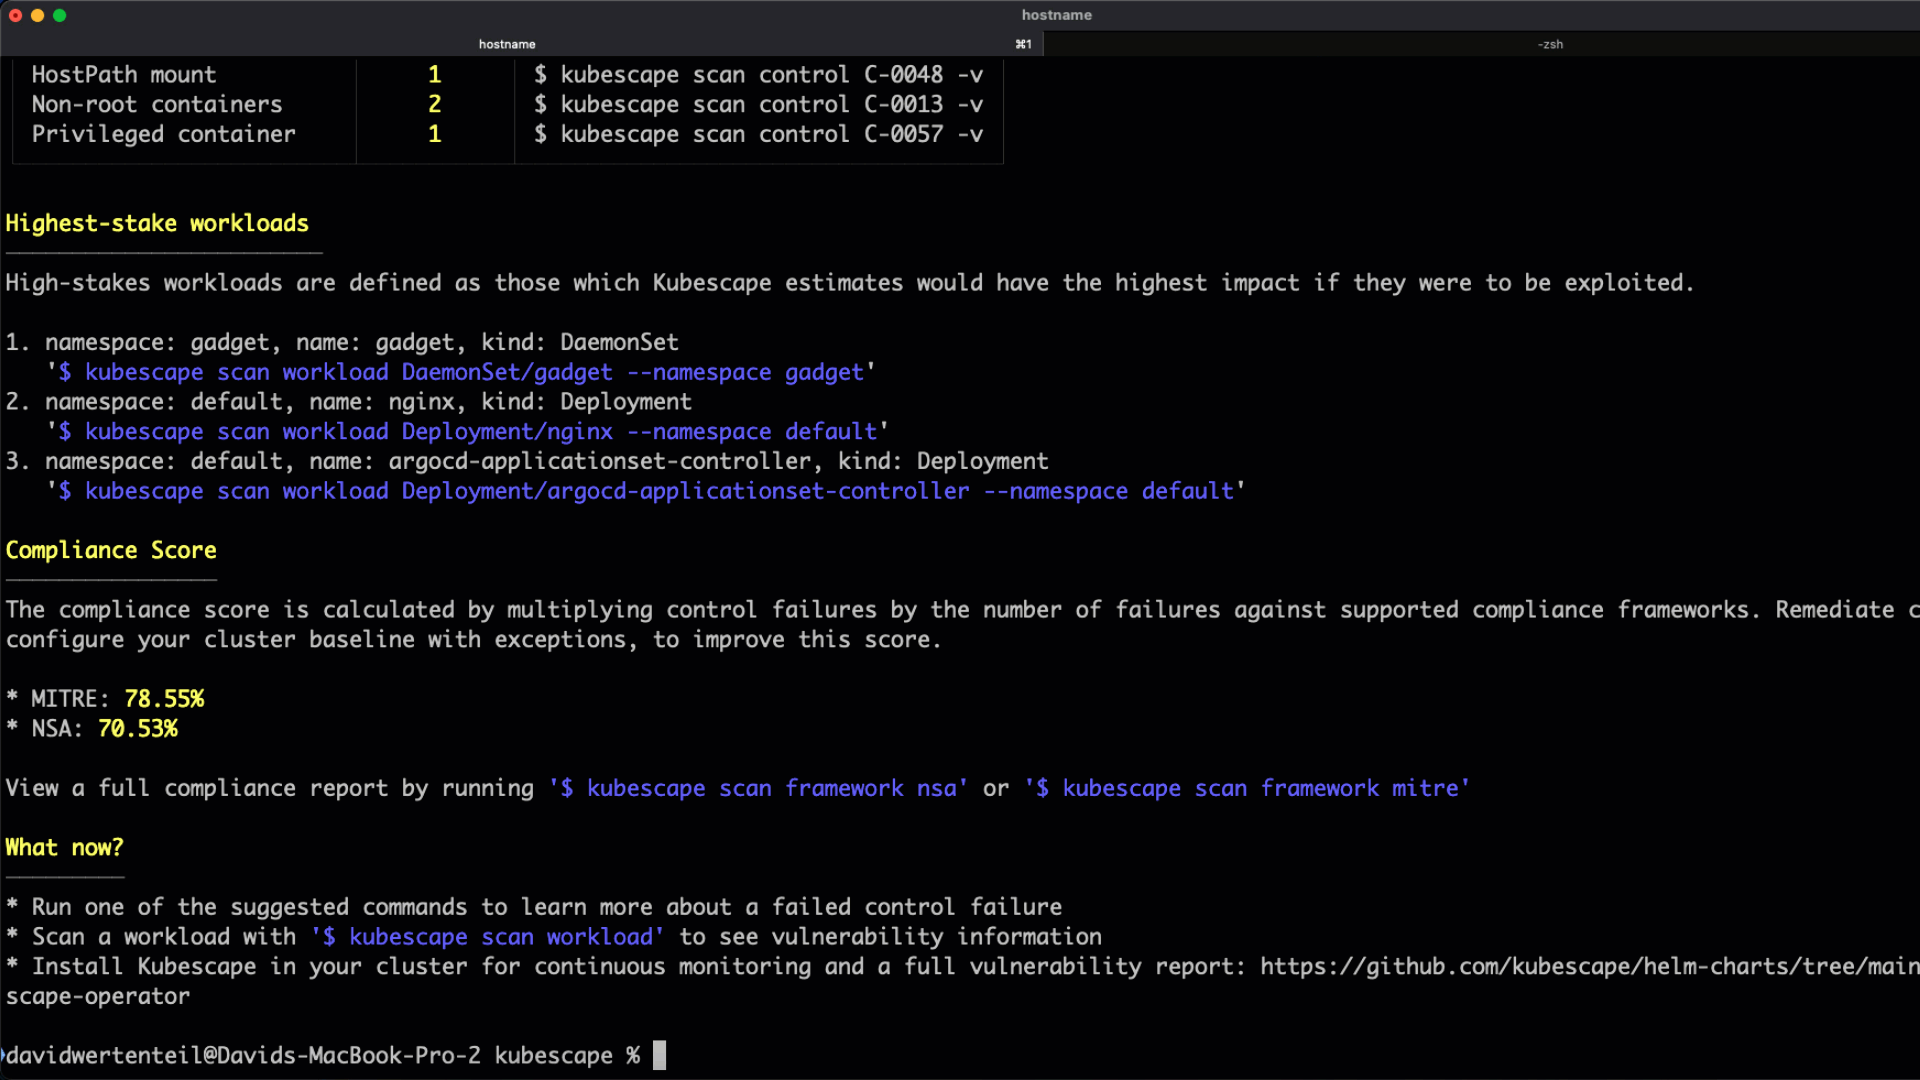 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
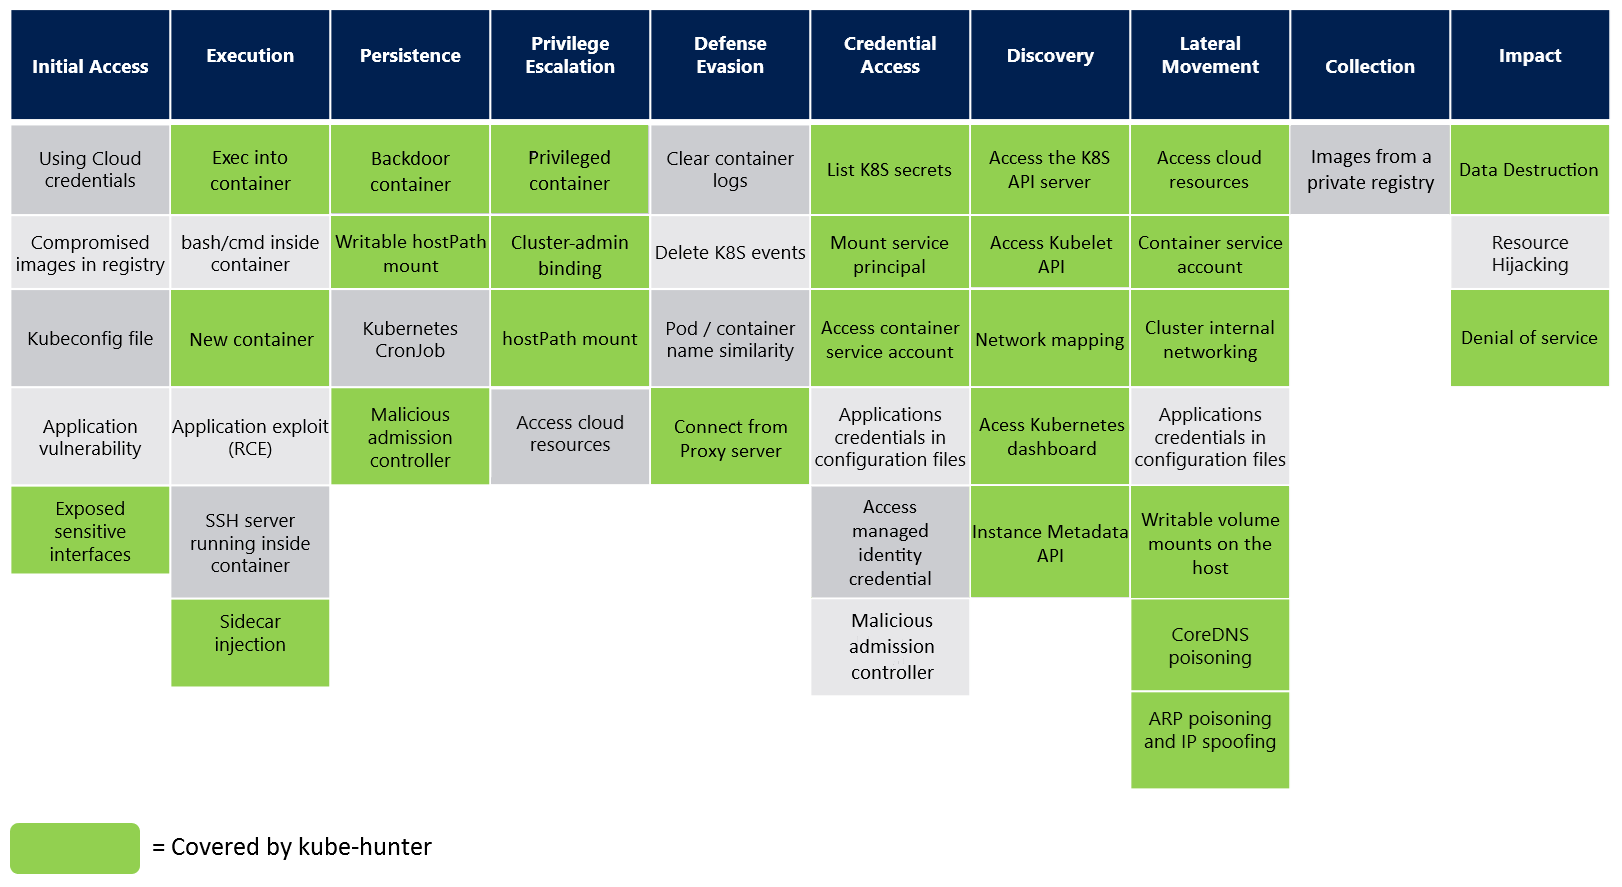 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
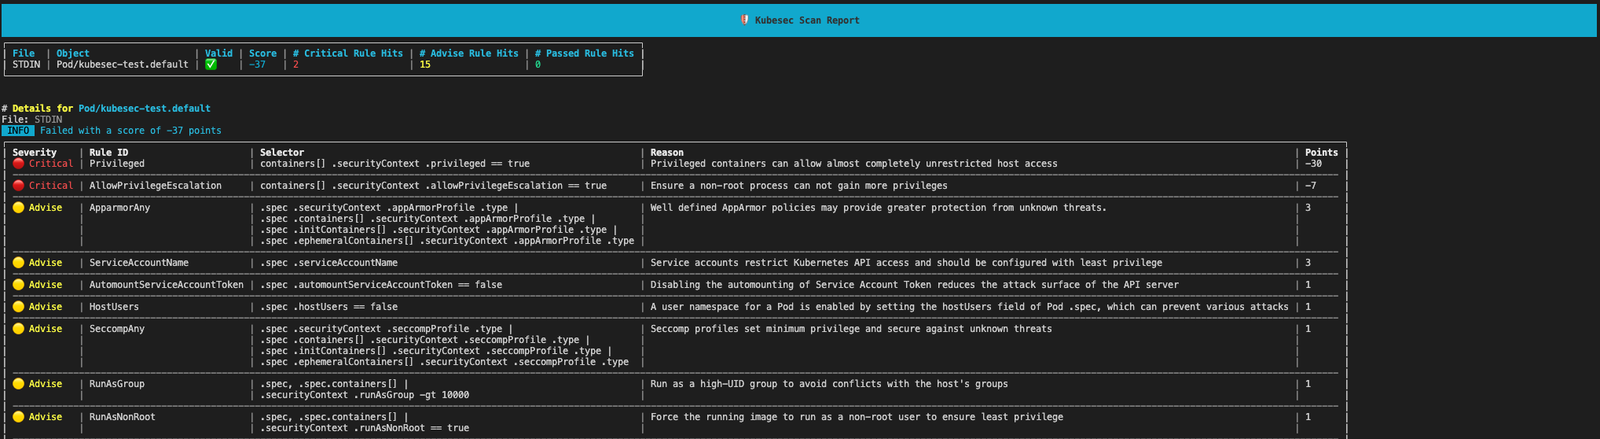 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 nitrocao/cve-2024-21626
PoC and Detection for CVE-2024-21626
 qi4l/cve-2026-31431-container-escape
Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.
 nccgroup/abstractshimmer
Proof of concept for CVE-2020-15257 in containerd.
 ssst0n3/docker-cve-2022-39253-poc
Proof-of-concept exploit for CVE-2022-39253 demonstrating Docker container escape via malicious Git repository build, enabling host file system read…