CVE-2026-23111-nftables-lab

Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…

Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…

A vulnerability scanner for container images and filesystems

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

A Linux Host-based Intrusion Detection System based on eBPF.

Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…

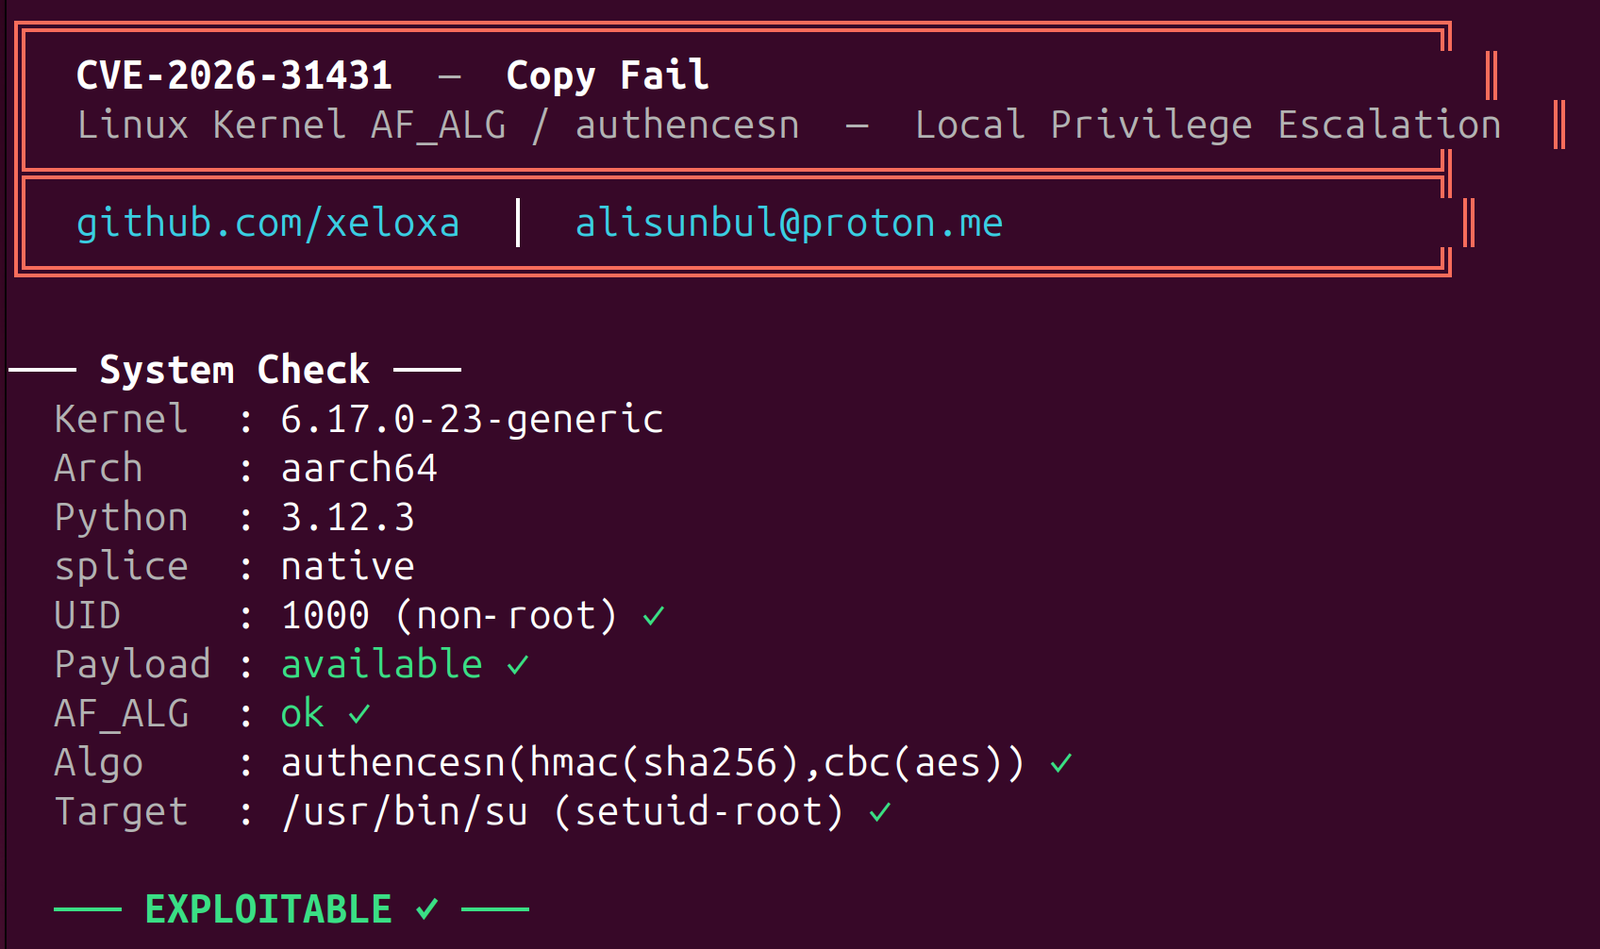
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.

insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.

3 linux kernel bugs chains to do secure comm app using side channel to establish key and establish covert channe;

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP

Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape

PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…

Exploit for CVE-2019-5737, a Docker runc container escape vulnerability, with build and run instructions for Linux and Windows.

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…

📦 Make security testing of K8s, Docker, and Containerd easier.

Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463

A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492