
CVE-2021-21978
 greyorder/cve-2021-21978
CVE-2021-21978 exp
container-escapeexploitationremote-access-tool+2
23
greyorder/cve-2021-21978CVE-2021-21978 exp
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 cyberark/pipeviewer
A tool that shows detailed information about named pipes in Windows
 tamatahyt/cve-2026-53576
Kestra Unauthenticated RCE Exploit (CVE-2026-53576)
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
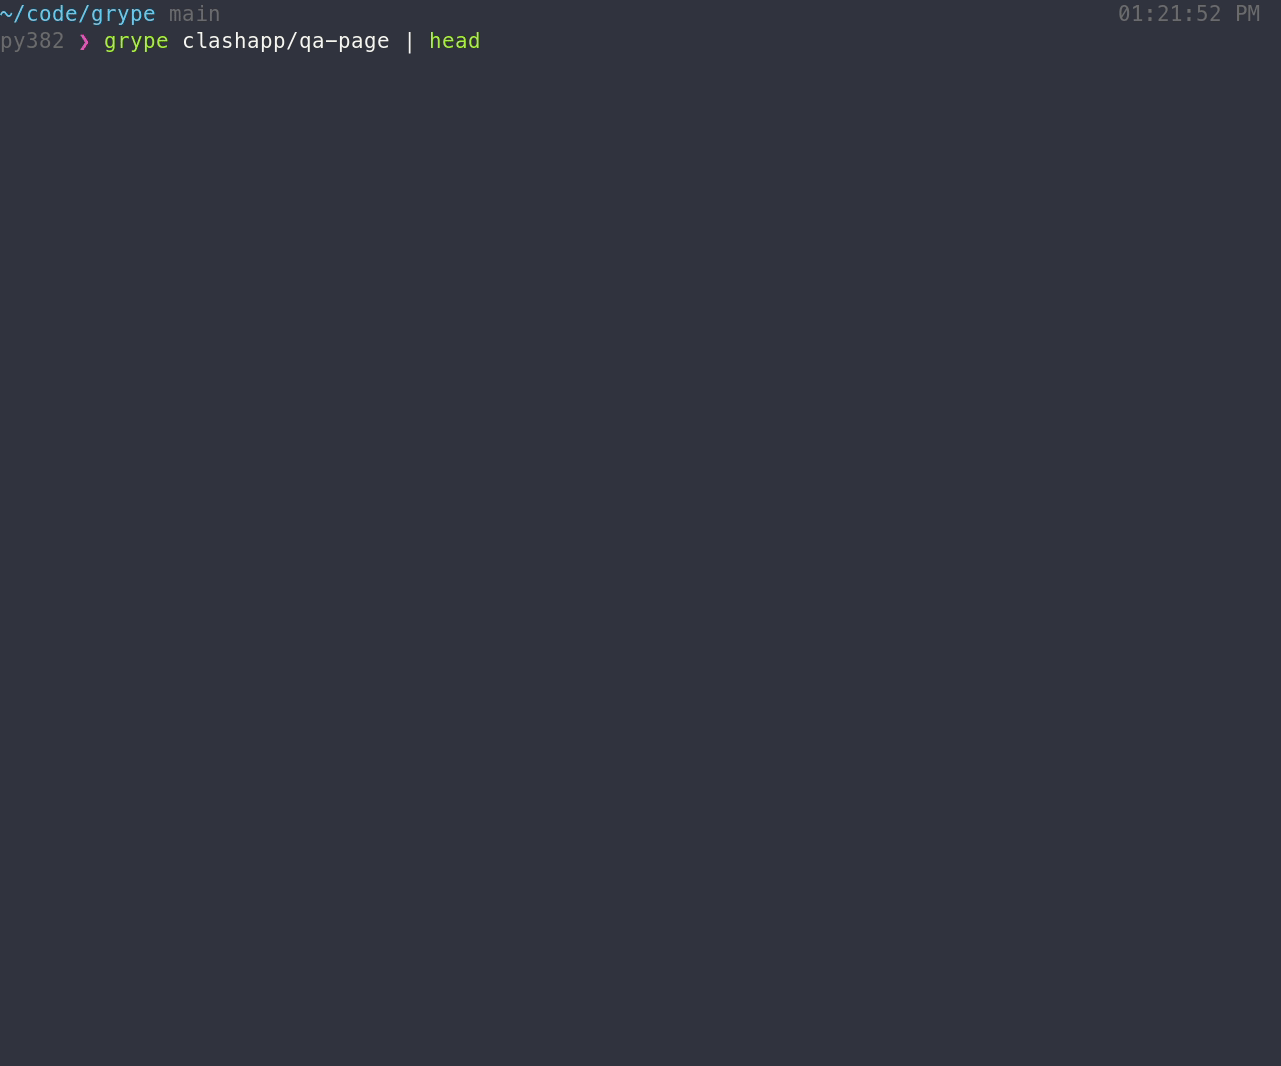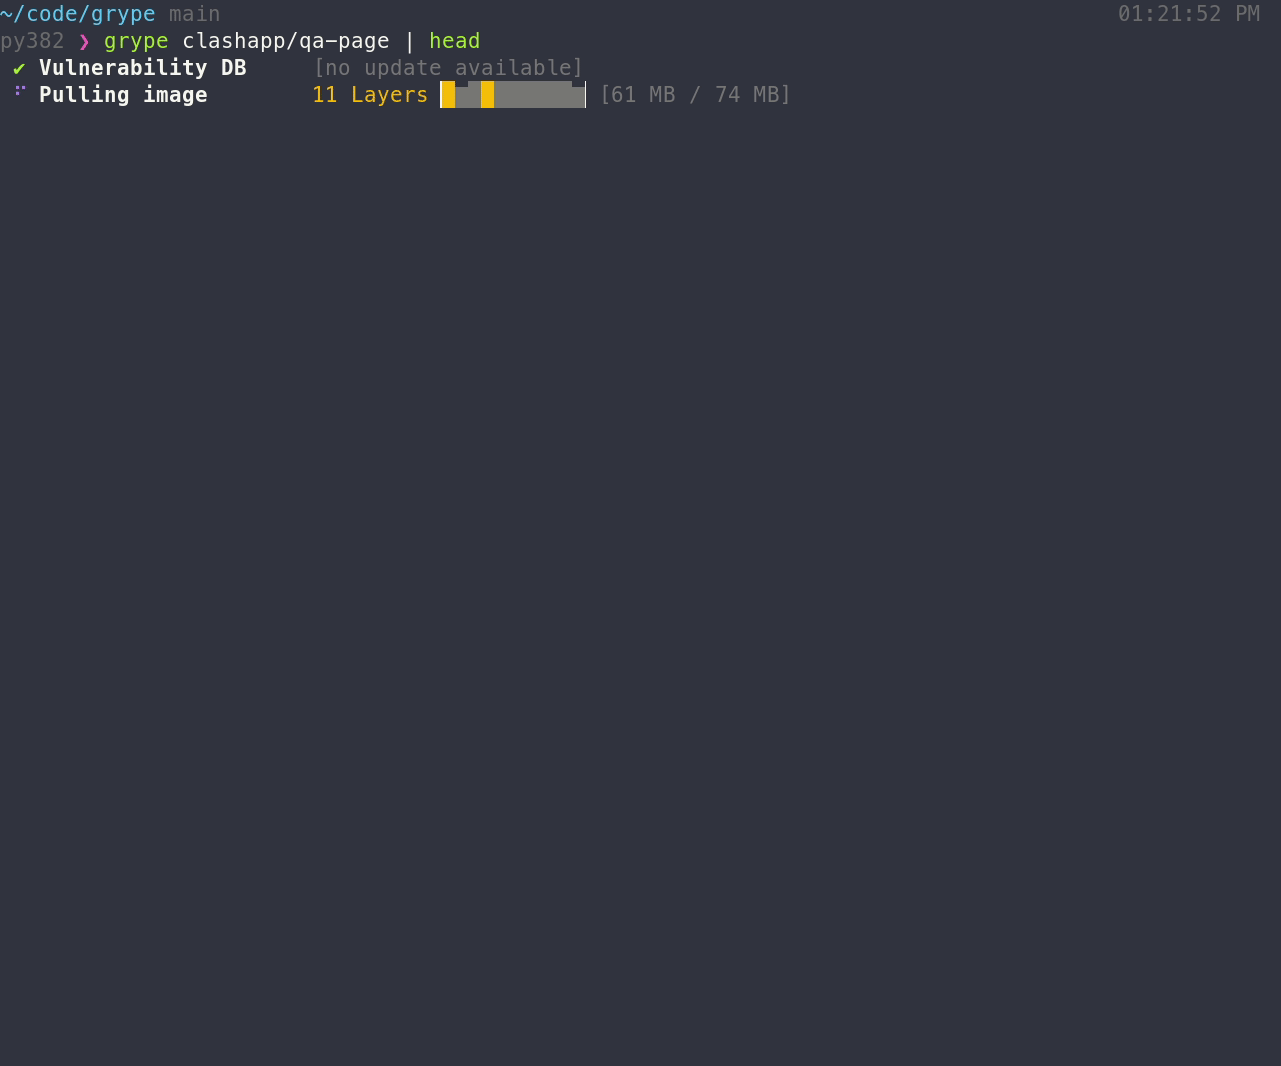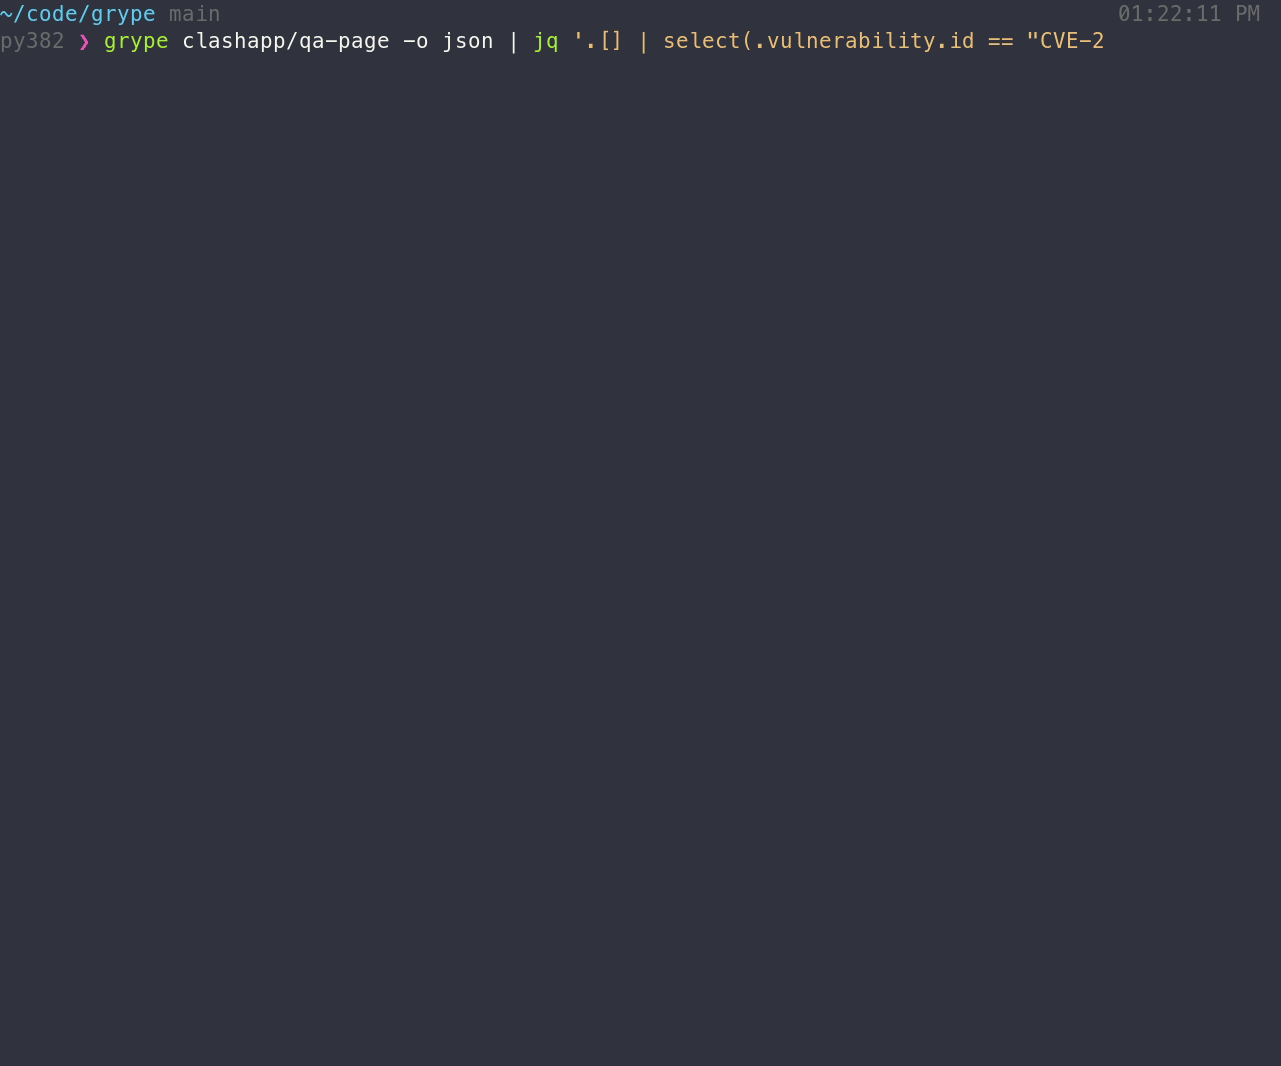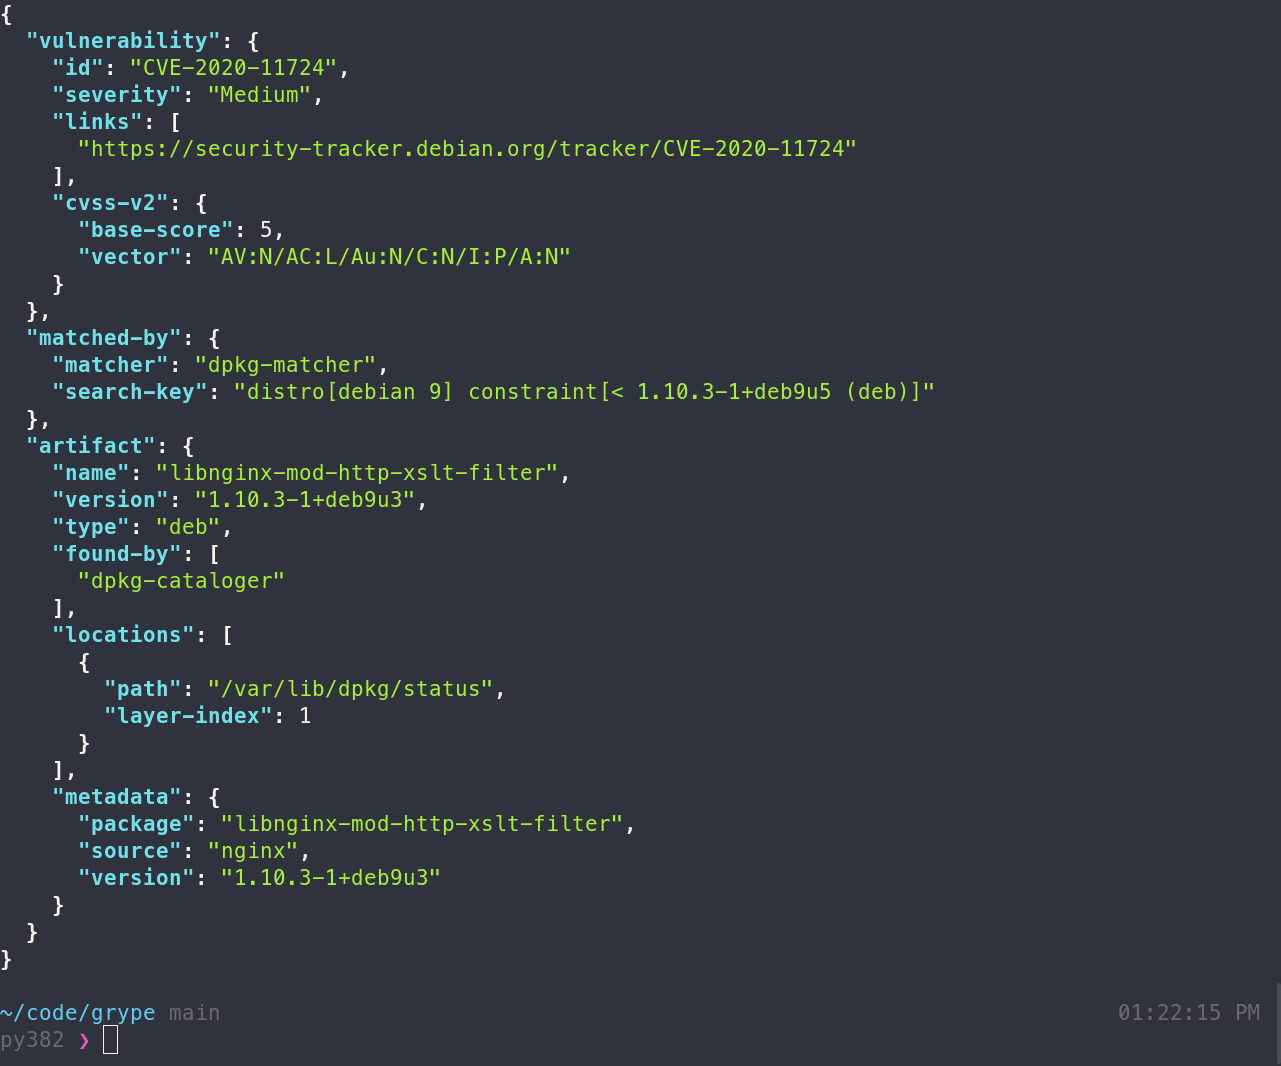 anchore/grype
A vulnerability scanner for container images and filesystems
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 qianlijaingshan/fastgpt-sandbox-audit
FastGPT Python sandbox escape chain audit tool (CVE-2026-32128 related, v4.14.8 inspect chain)
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.