POC-CopyEscape-CVE-2026-17106

PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

FastGPT Python sandbox escape chain audit tool (CVE-2026-32128 related, v4.14.8 inspect chain)

POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20

Docker Container Escape POC via mlx-metal importlib

A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer


CVE-2025-23266 – Fully Weaponized NVIDIA Container Toolkit Exploit

Este script es para uso educativo y en entornos autorizados como HackTheBox. El uso contra sistemas sin permiso explícito es ilegal.

一个容器逃逸漏洞POC

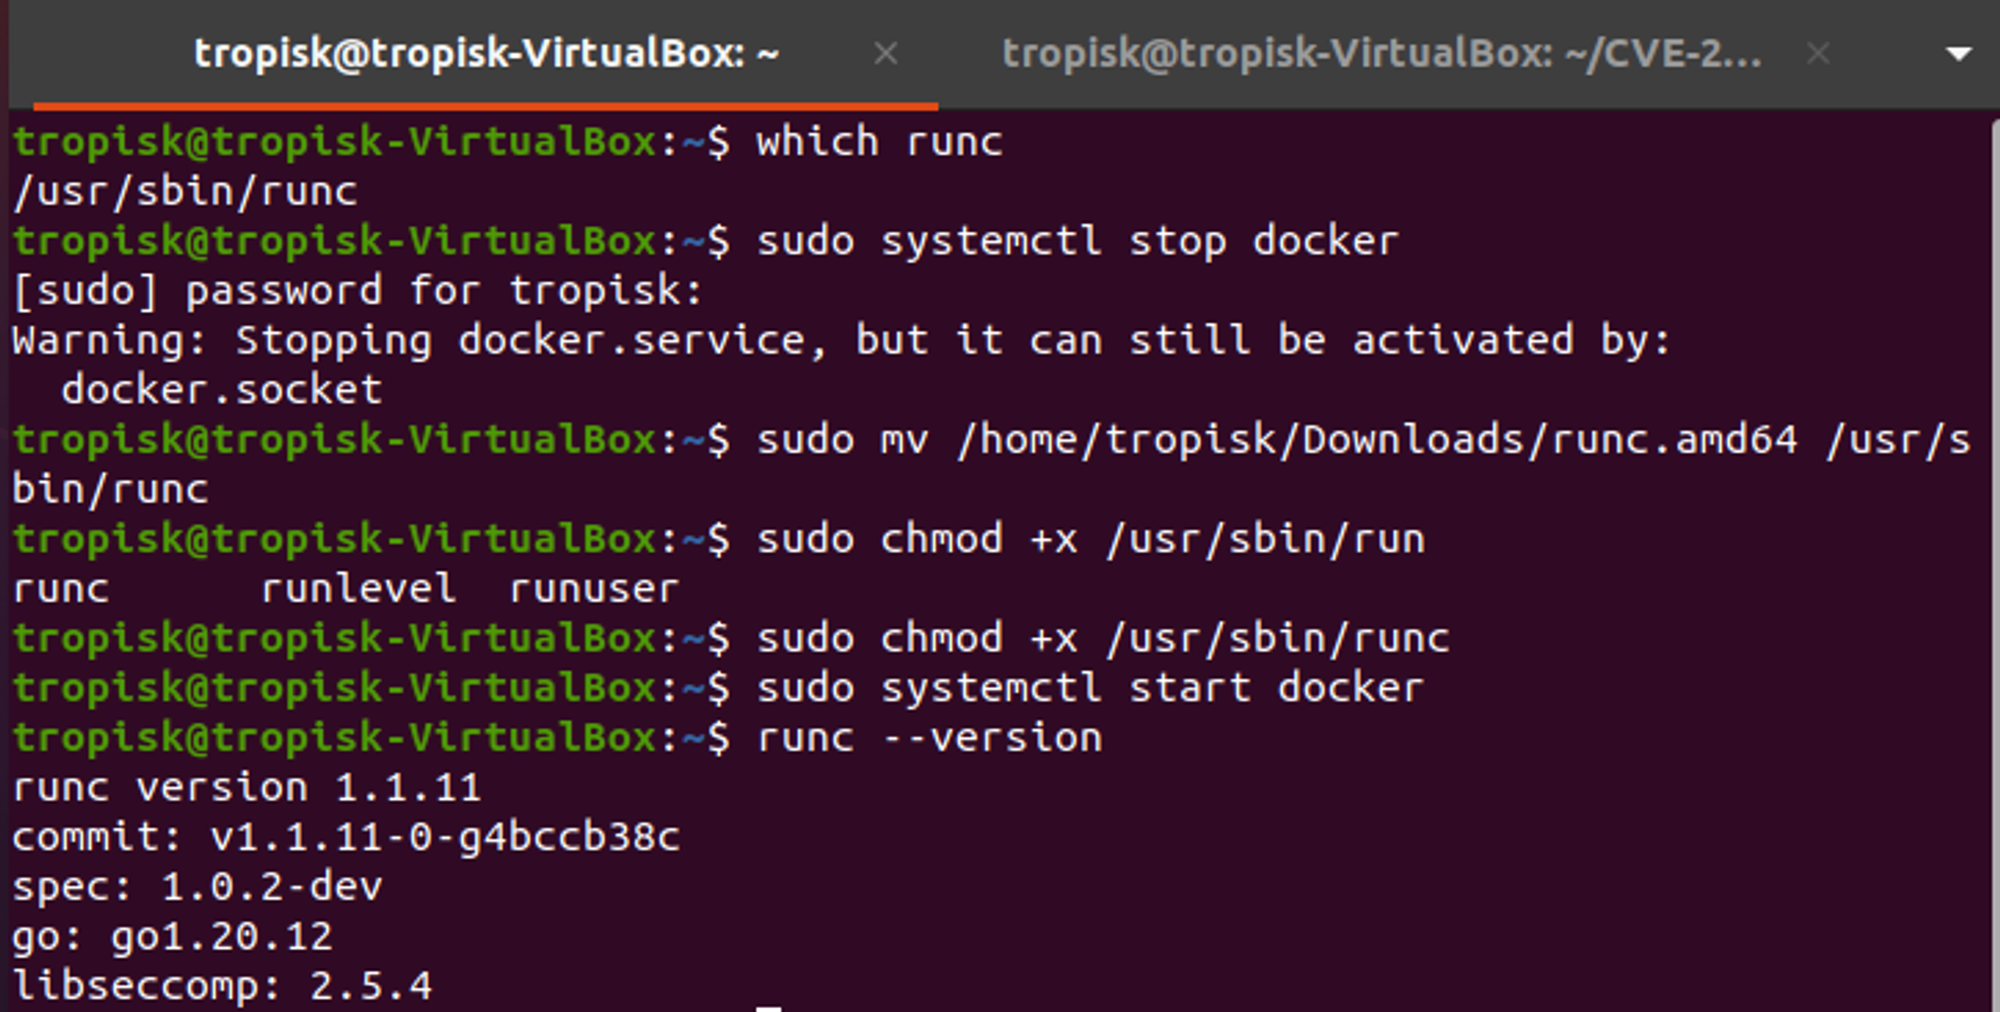
Analyzes and exploits a container escape vulnerability in legacy Docker/runc versions, demonstrating fd leakage to access the host filesystem, with…

Modified version of CVE-2019-5736-PoC by Frichetten

In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.

Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.

Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…