

CVE-2019-5736
 likekabin/cve-2019-5736
Destructive Docker container escape exploit for CVE-2019-5736, overwriting host /usr/bin/docker-runc with a payload triggered via docker exec.
binary-exploitationcontainer-escapeexploitation+3
1
likekabin/cve-2019-5736Destructive Docker container escape exploit for CVE-2019-5736, overwriting host /usr/bin/docker-runc with a payload triggered via docker exec.
 louisliunova/cve-2022-1227_exploit
A script for exploiting CVE-2022-1227
 followboy1999/cve-2022-25365
Proof-of-concept exploit for CVE-2022-25365, a privilege escalation vulnerability in Docker Desktop for Windows via named pipe impersonation.
 zaydbf/cve-2025-9074-poc
Bash-based PoC exploit for CVE-2025-9074 targeting unauthenticated Docker Engine API to achieve container escape and remote code execution via…
 gmeghnag/test-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 demonstrating container escape and privilege escalation in OpenShift environments.
 matesz44/cve-2025-9074
CVE-2025-9074: Docker Desktop LPE via Docker Engine API wo/ AuthN in posix sh
 khaclep007/cve-2022-0185
Demo exploits for CVE-2022-0185, a Linux kernel heap buffer overflow. Includes FUSE-based privilege escalation and a kctf version achieving root RCE…
 hikame/docker_escape_pwn
Escape from Docker using CVE-2017-1000112 and CVE-2017-18344, including gaining root privilage, get all capbilities, namespace recovery, filesystem…
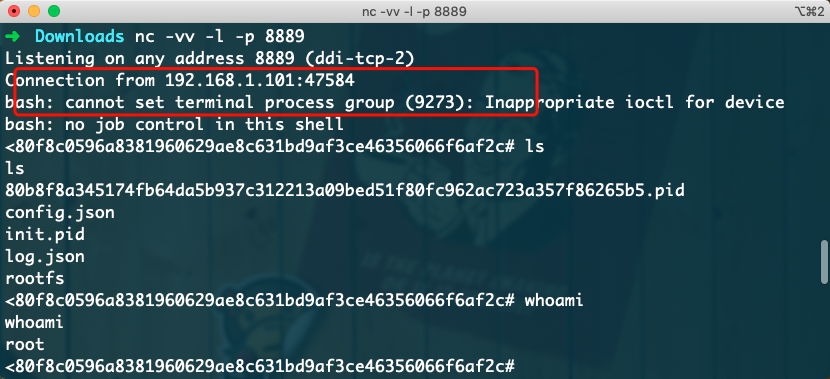 si1ent-le/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a Docker container escape via runc binary overwrite, enabling host shell access through libseccomp…
 datadog/dirtypipe-container-breakout-poc
Container Excape PoC for CVE-2022-0847 "DirtyPipe"