

Insular
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
android-securitycontainer-escapedynamic-analysis-sandboxing+3
222
secure-system/insularIsolate your big brother apps https://secure-system.gitlab.io/Insular/
 impalabs/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
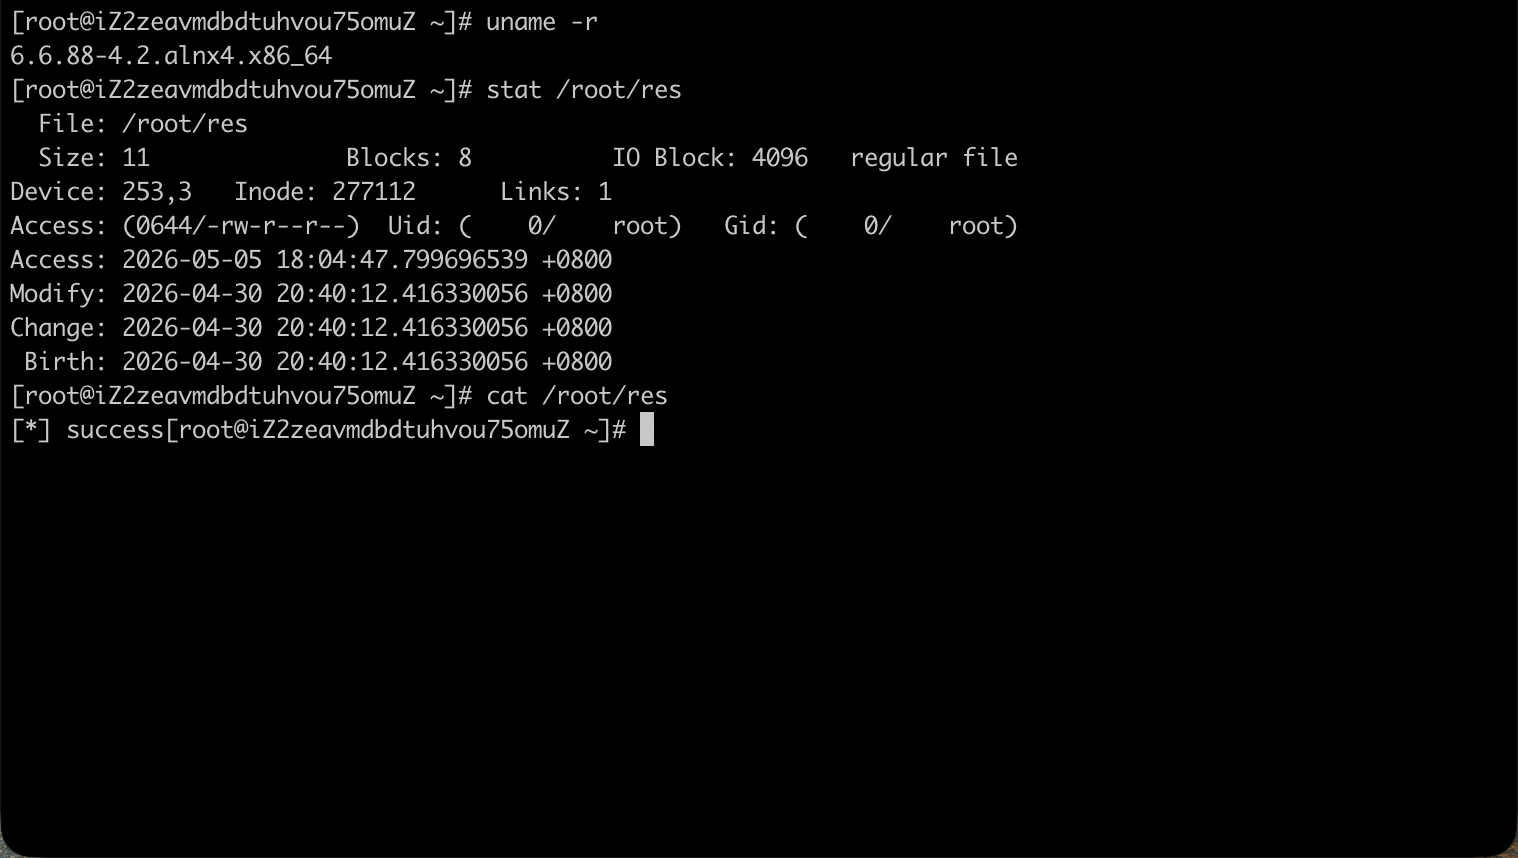 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 sgkdev/page_inject
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
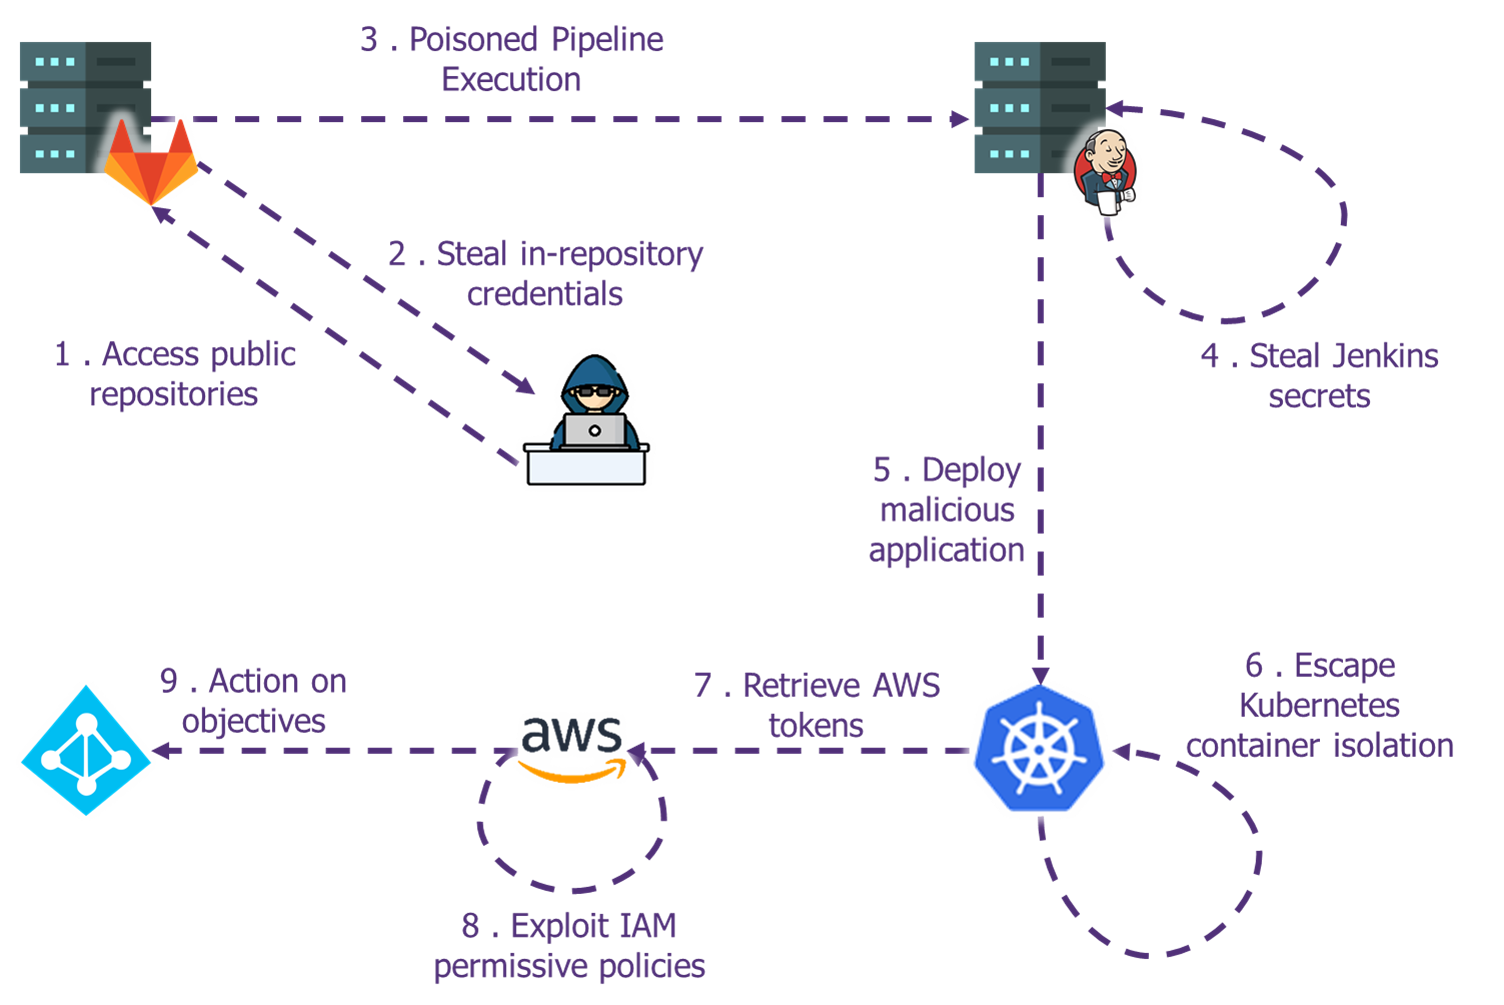 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 veritas501/pipe-primitive
An exploit primitive in linux kernel inspired by DirtyPipe
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
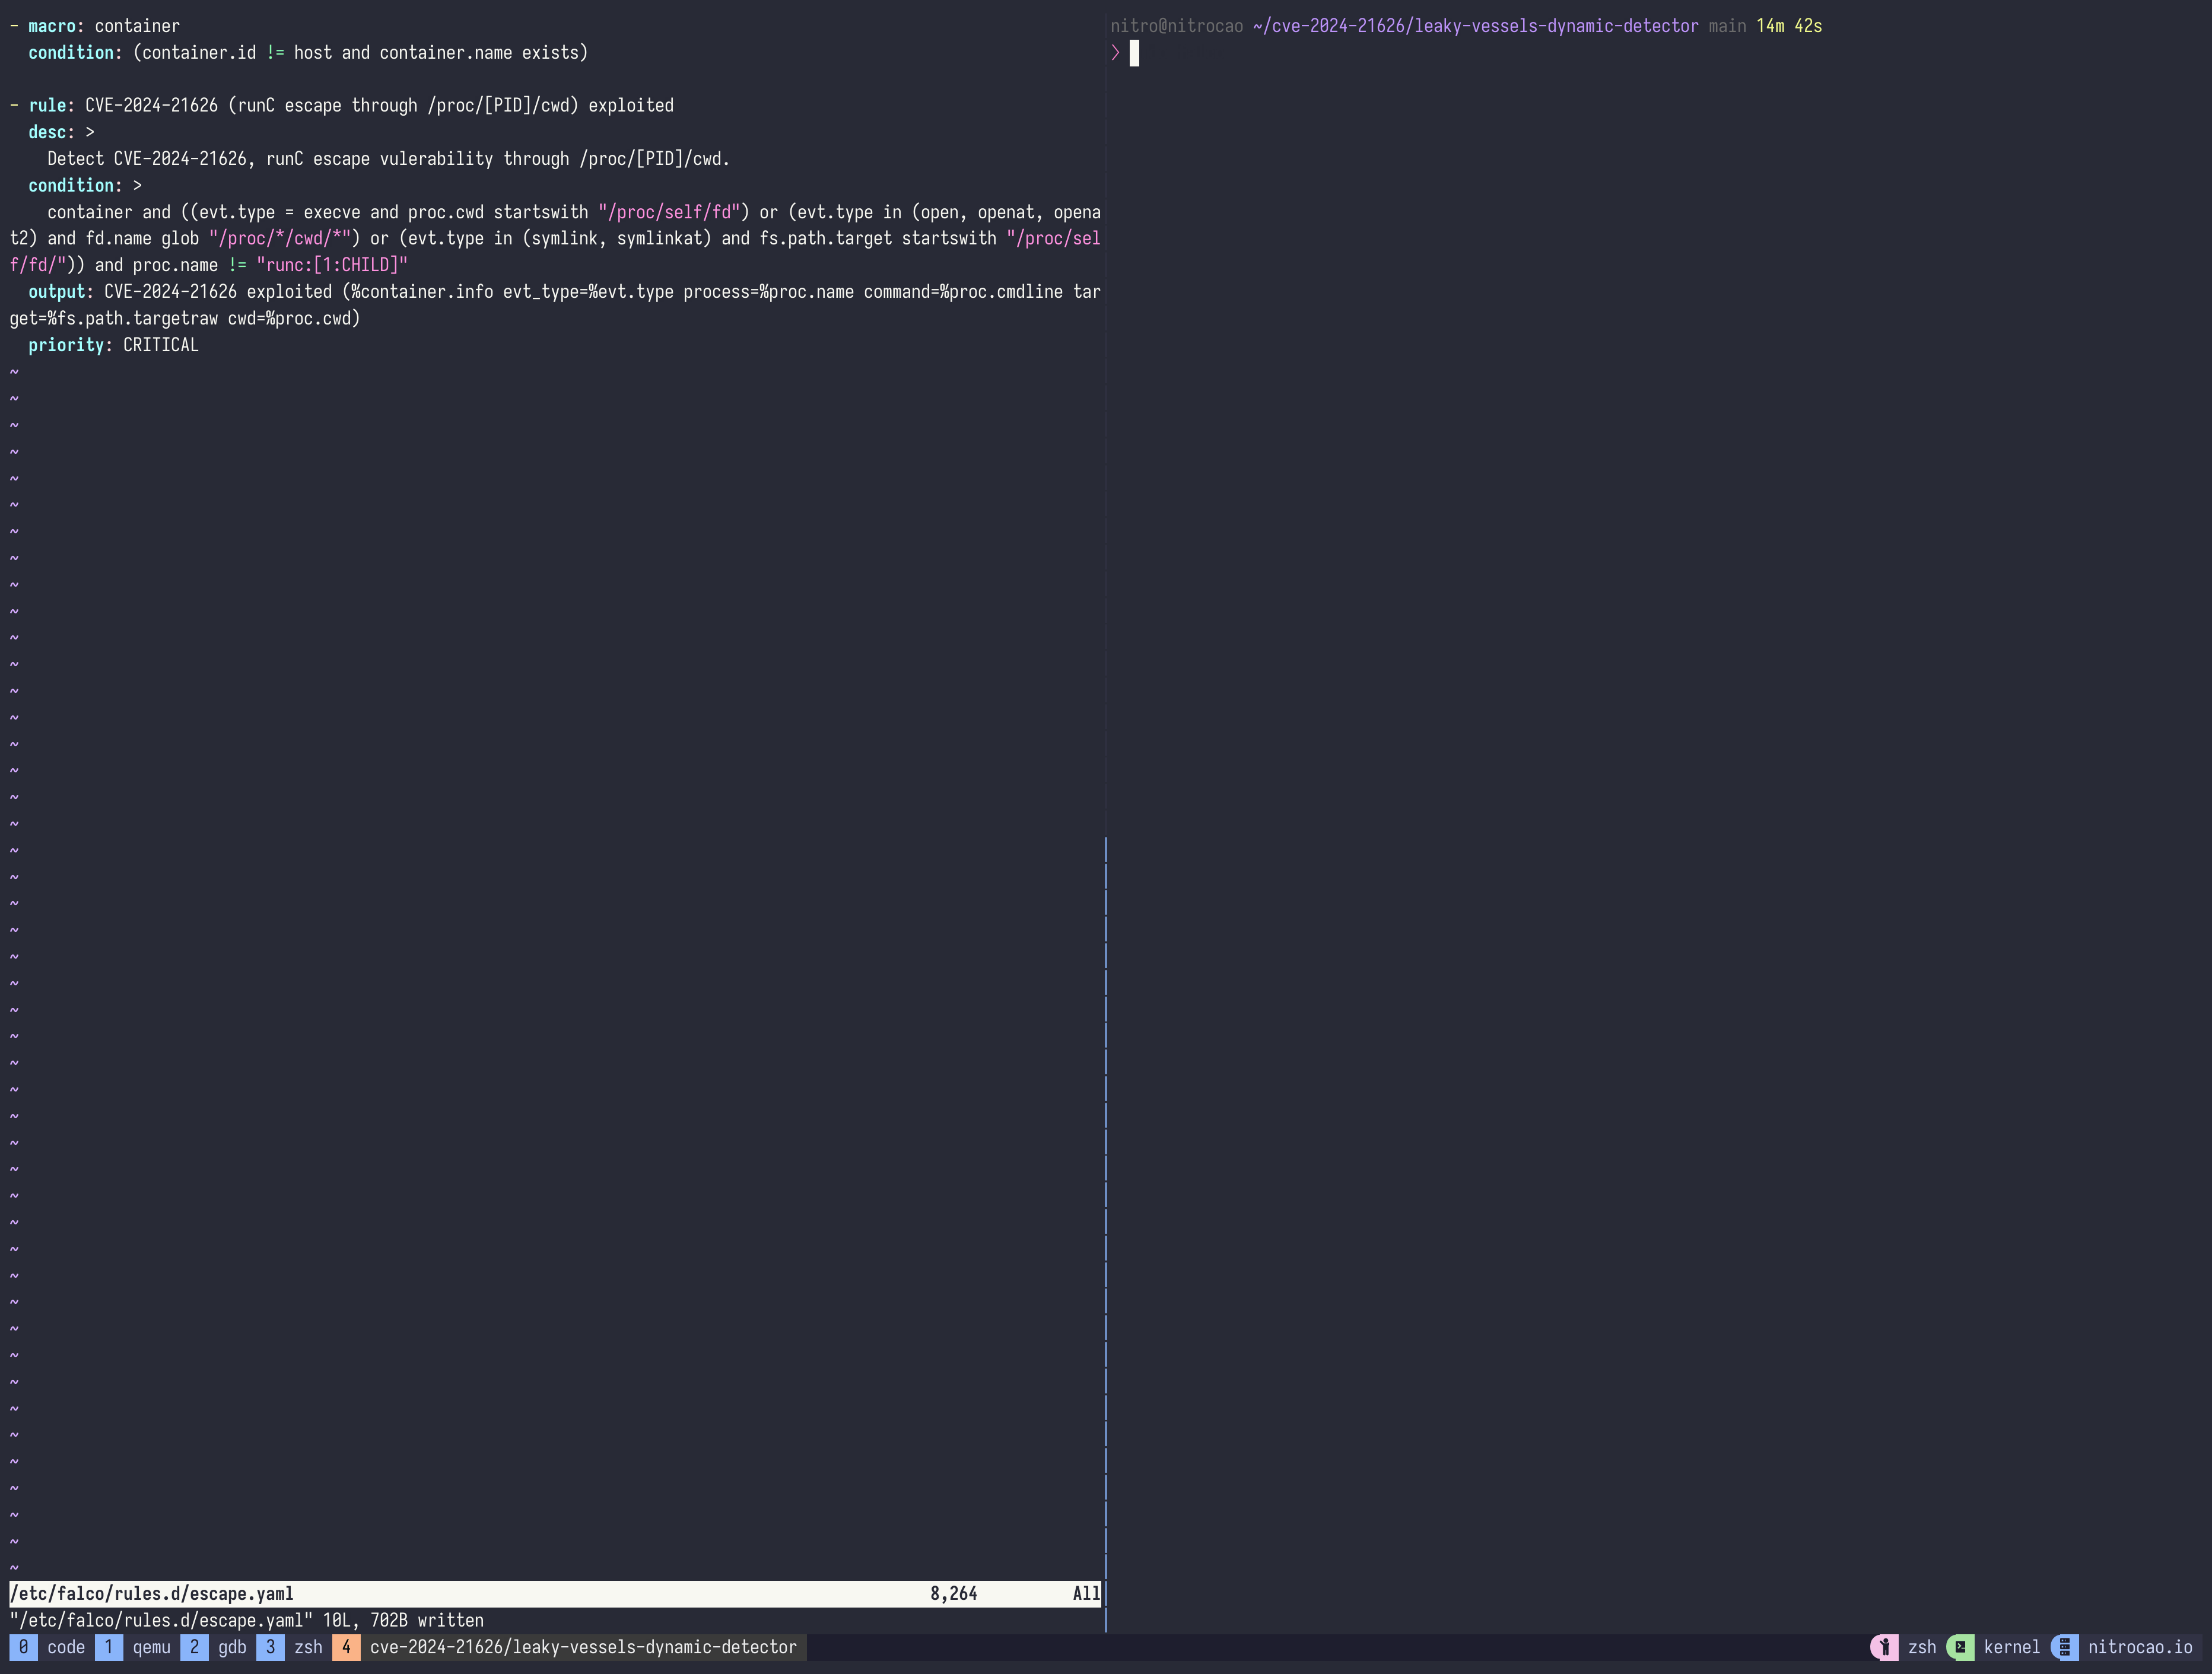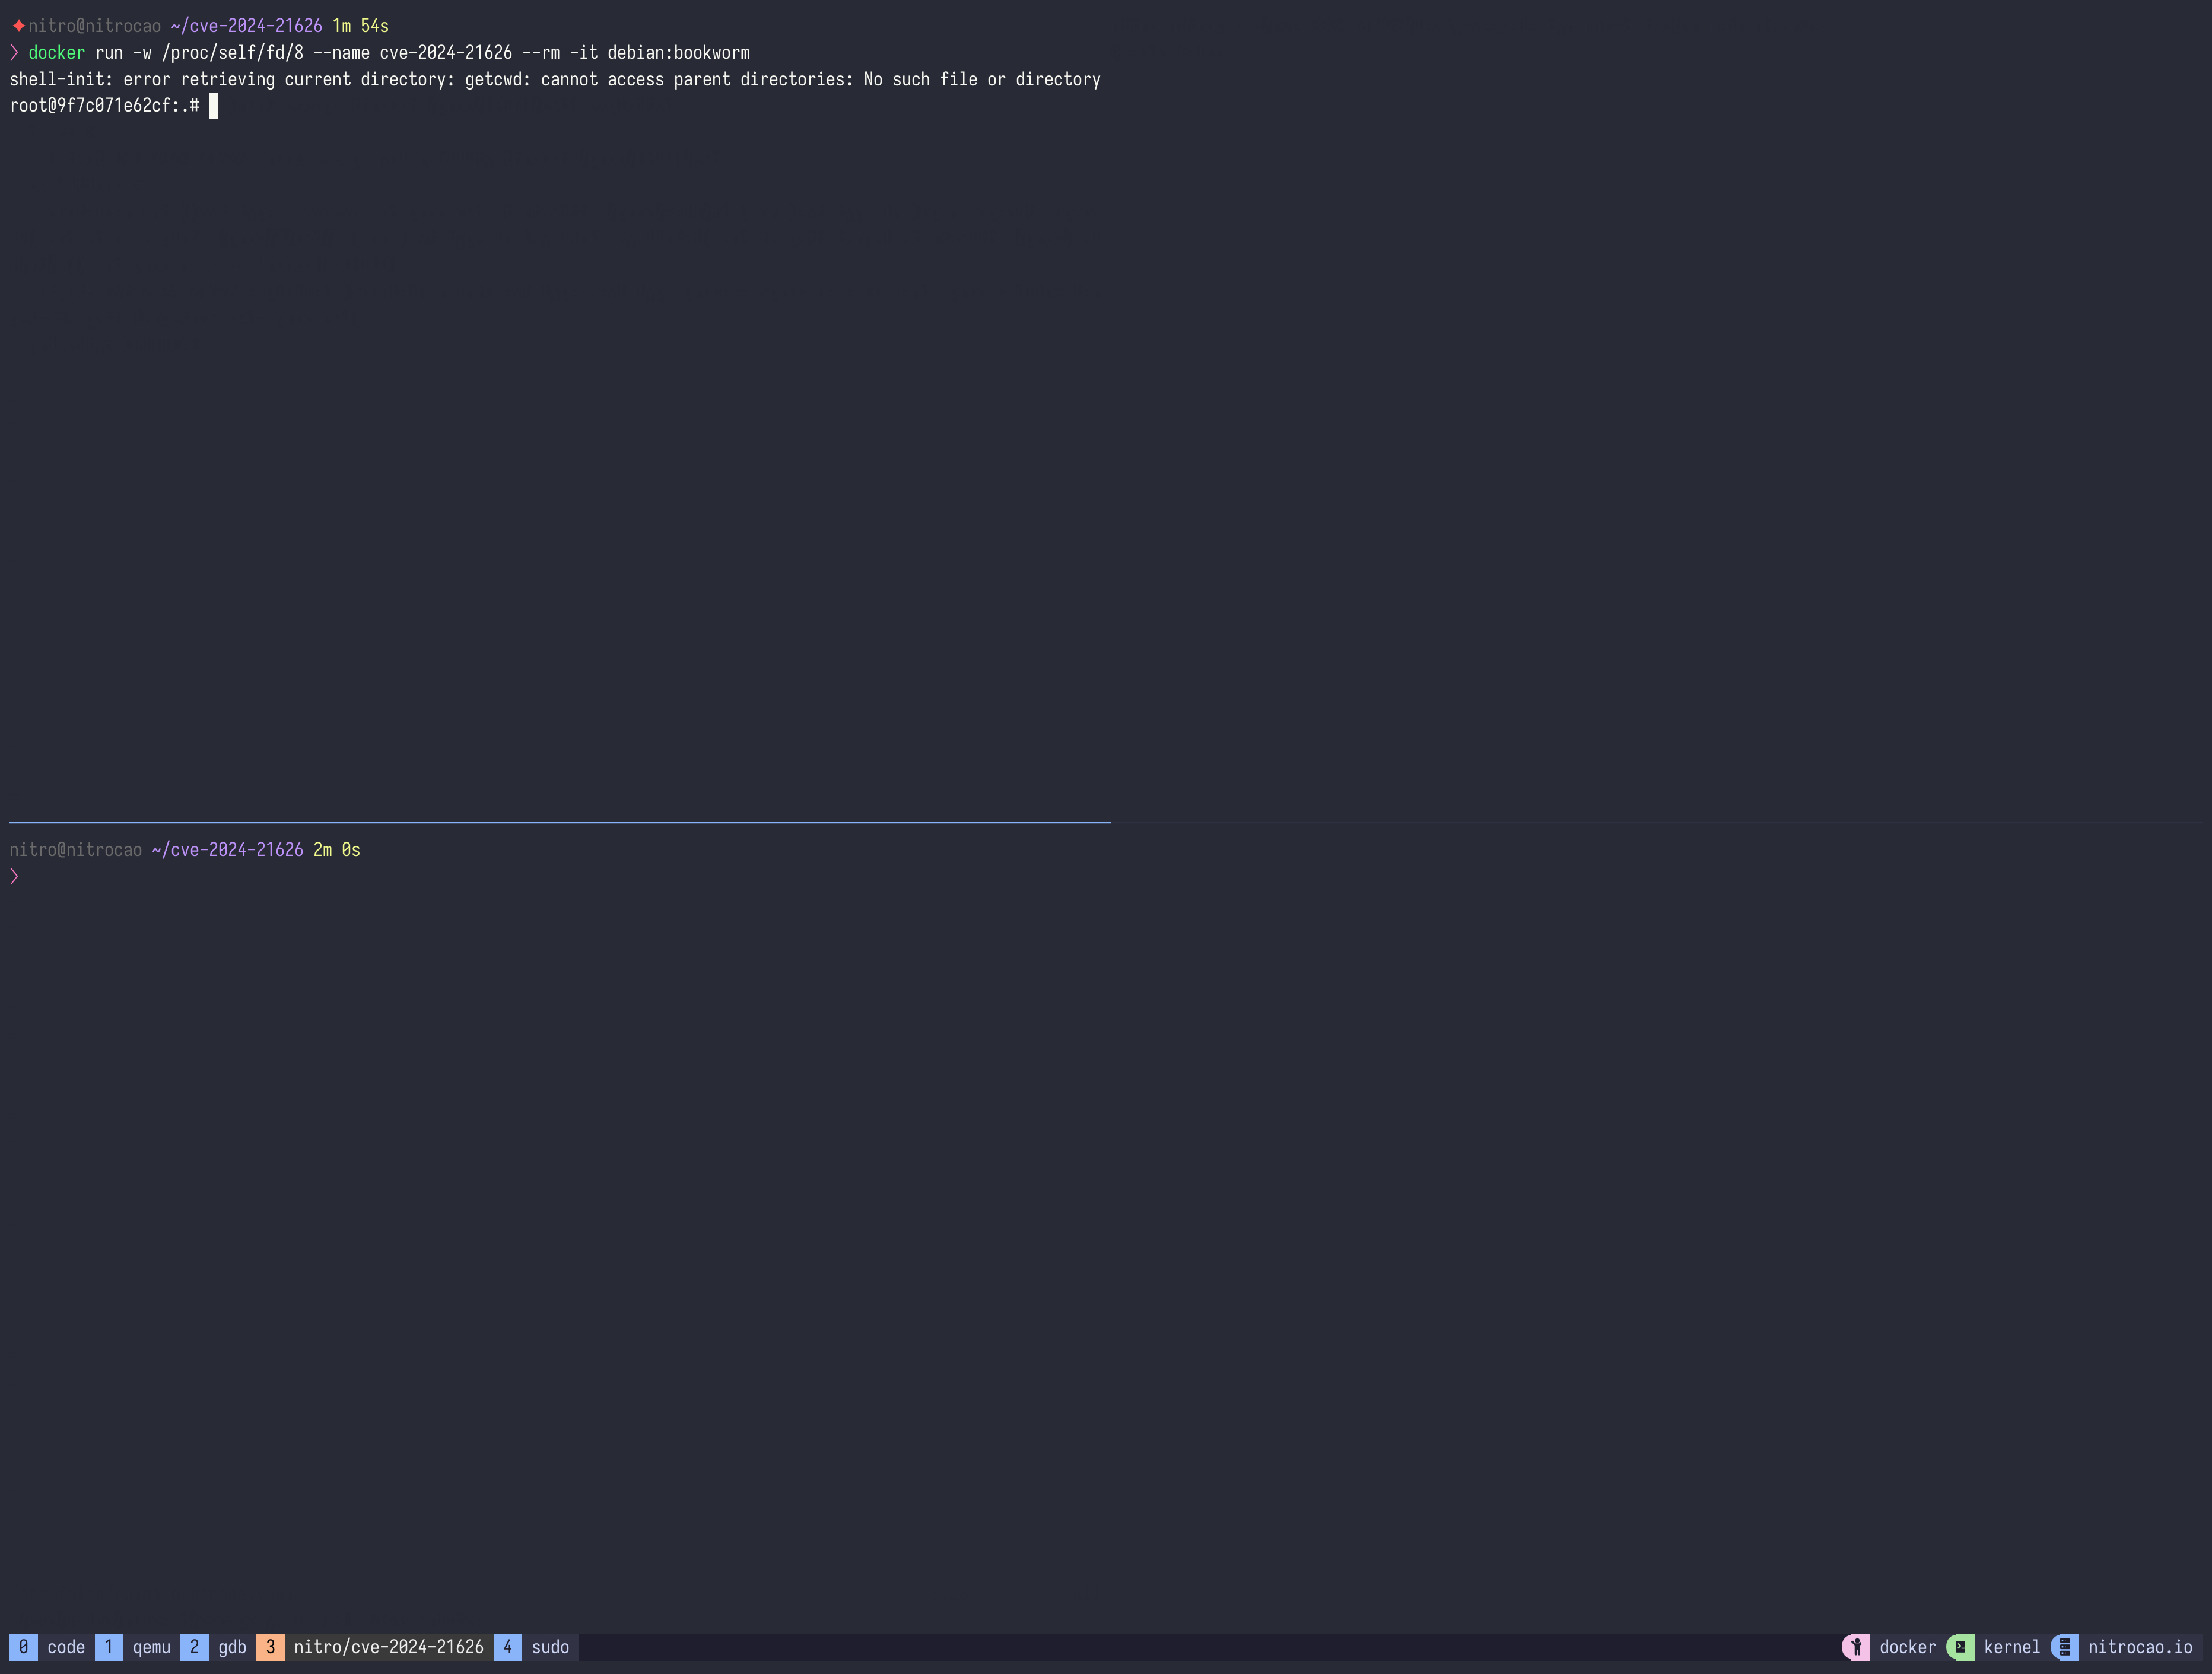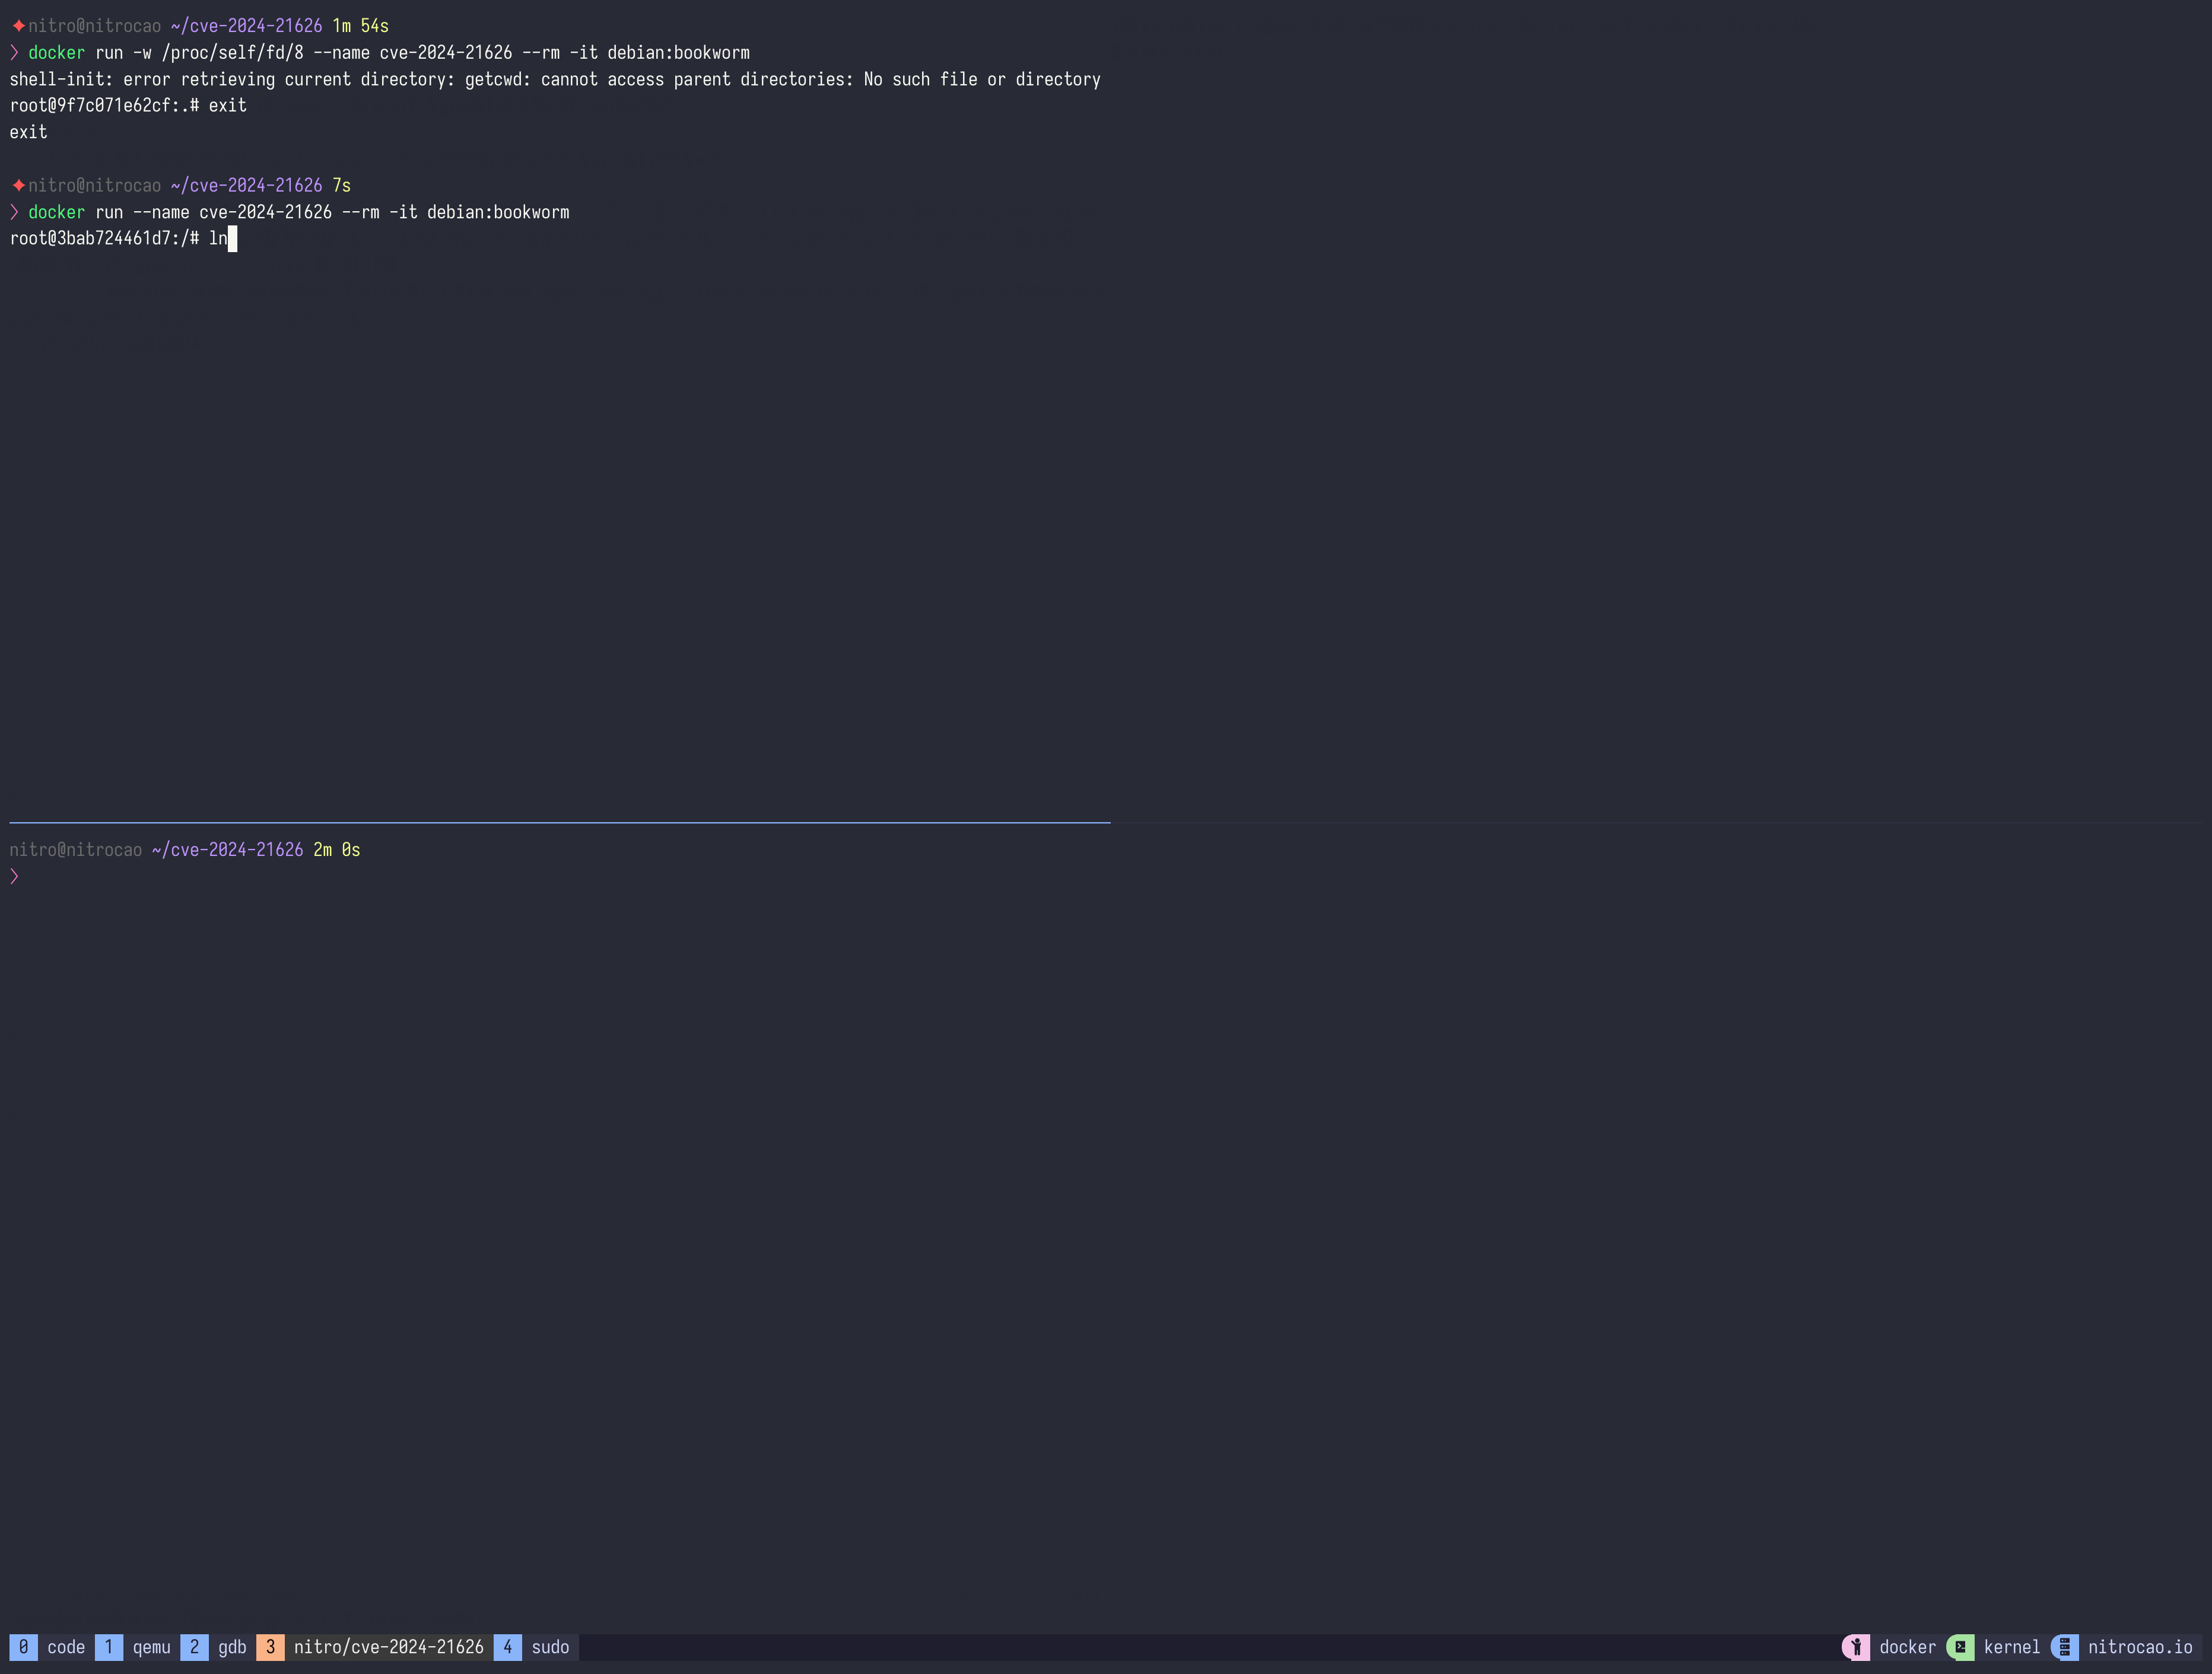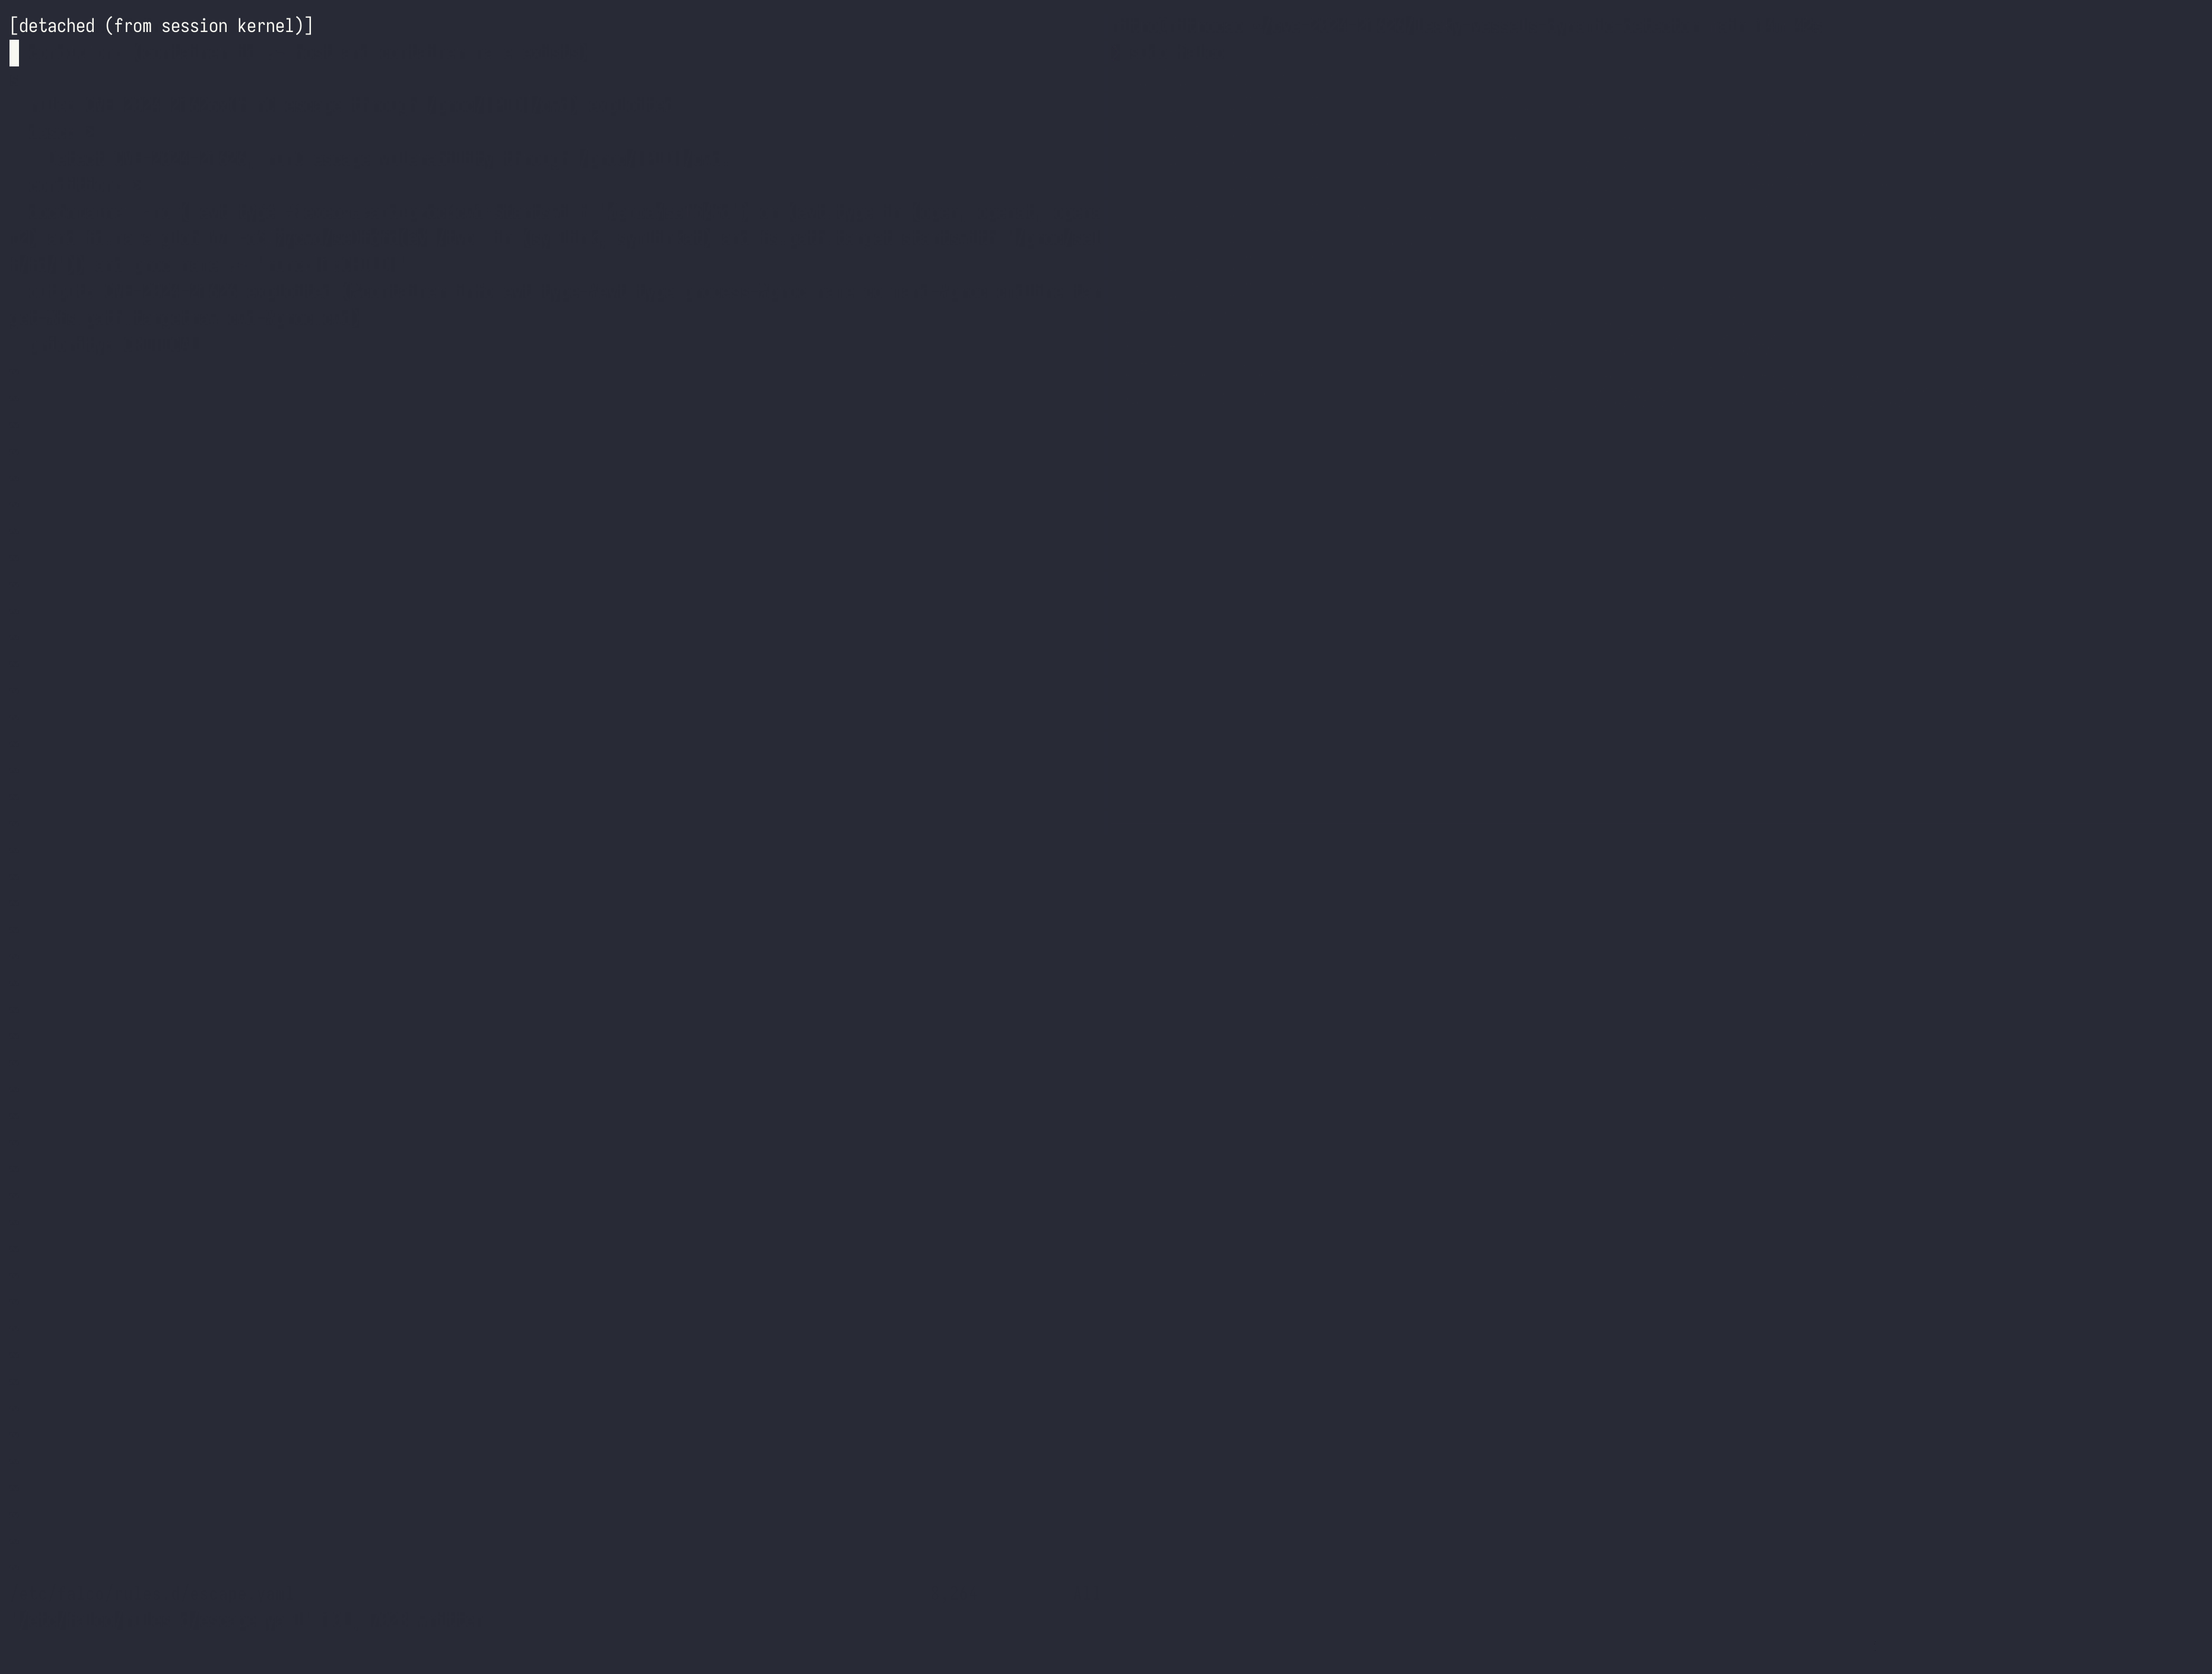 nitrocao/cve-2024-21626
PoC and Detection for CVE-2024-21626
 sgkdev/ipv6_frag_escape
Linux LPE - Reliable Jail/Container Escape
 paloaltonetworks/can-ctr-escape-cve-2022-0492
Test whether a container environment is vulnerable to container escapes via CVE-2022-0492
 yoshino-s/cve-2025-1974
Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 greenhandatsjtu/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
 sgkdev/bad_garbage
CVE-2026-53361 AF_UNIX GC vs MSG_PEEK use-after-free container escape
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…