

syft
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
container-escapecontainer-securitydevsecops+3
anchore/syftCLI tool and library for generating a Software Bill of Materials from container images and filesystems
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
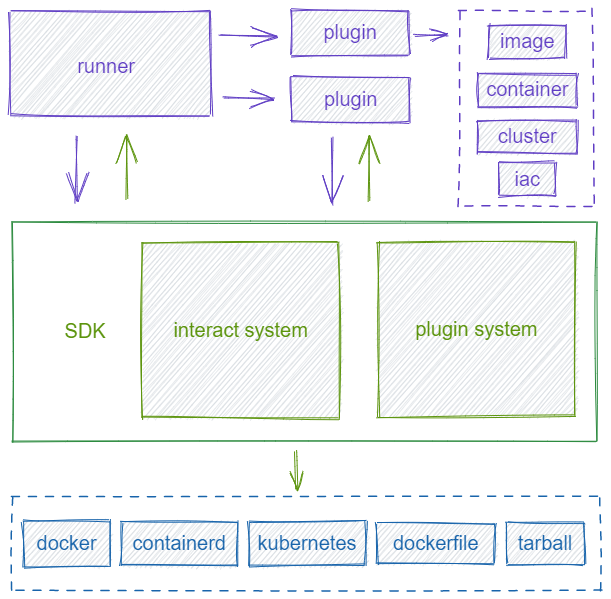 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463
 crusaders-of-rust/cve-2022-0185
CVE-2022-0185
 cyberark/pipeviewer
A tool that shows detailed information about named pipes in Windows
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/