

kubesec
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
1.5k
controlplaneio/kubesecSecurity risk analysis for Kubernetes resources
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 impalabs/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
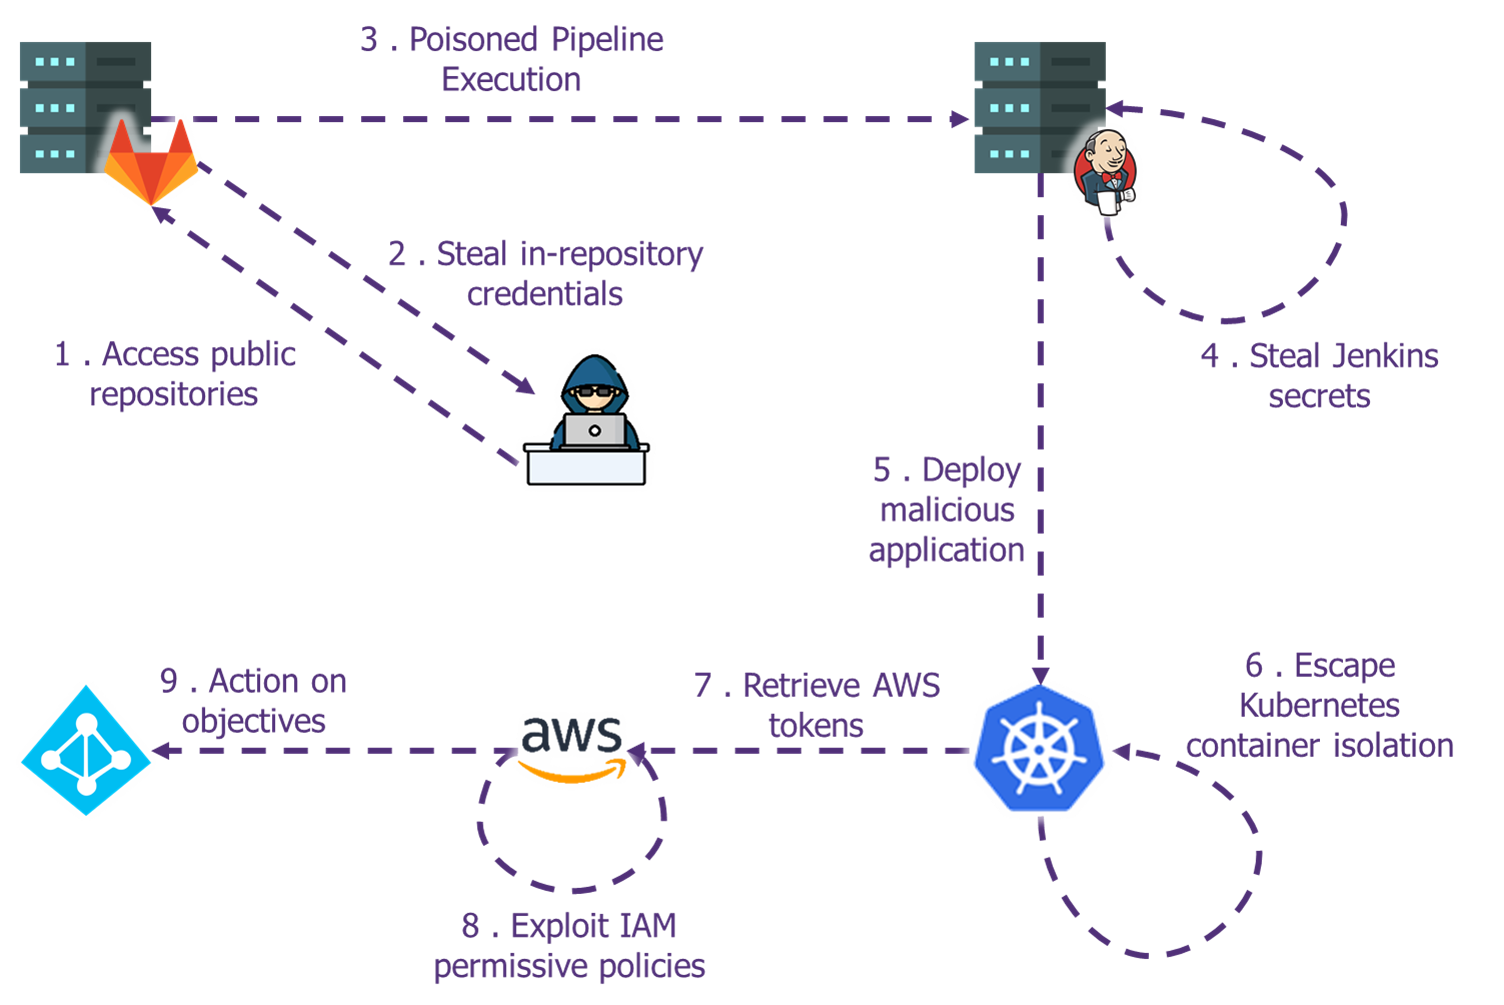 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
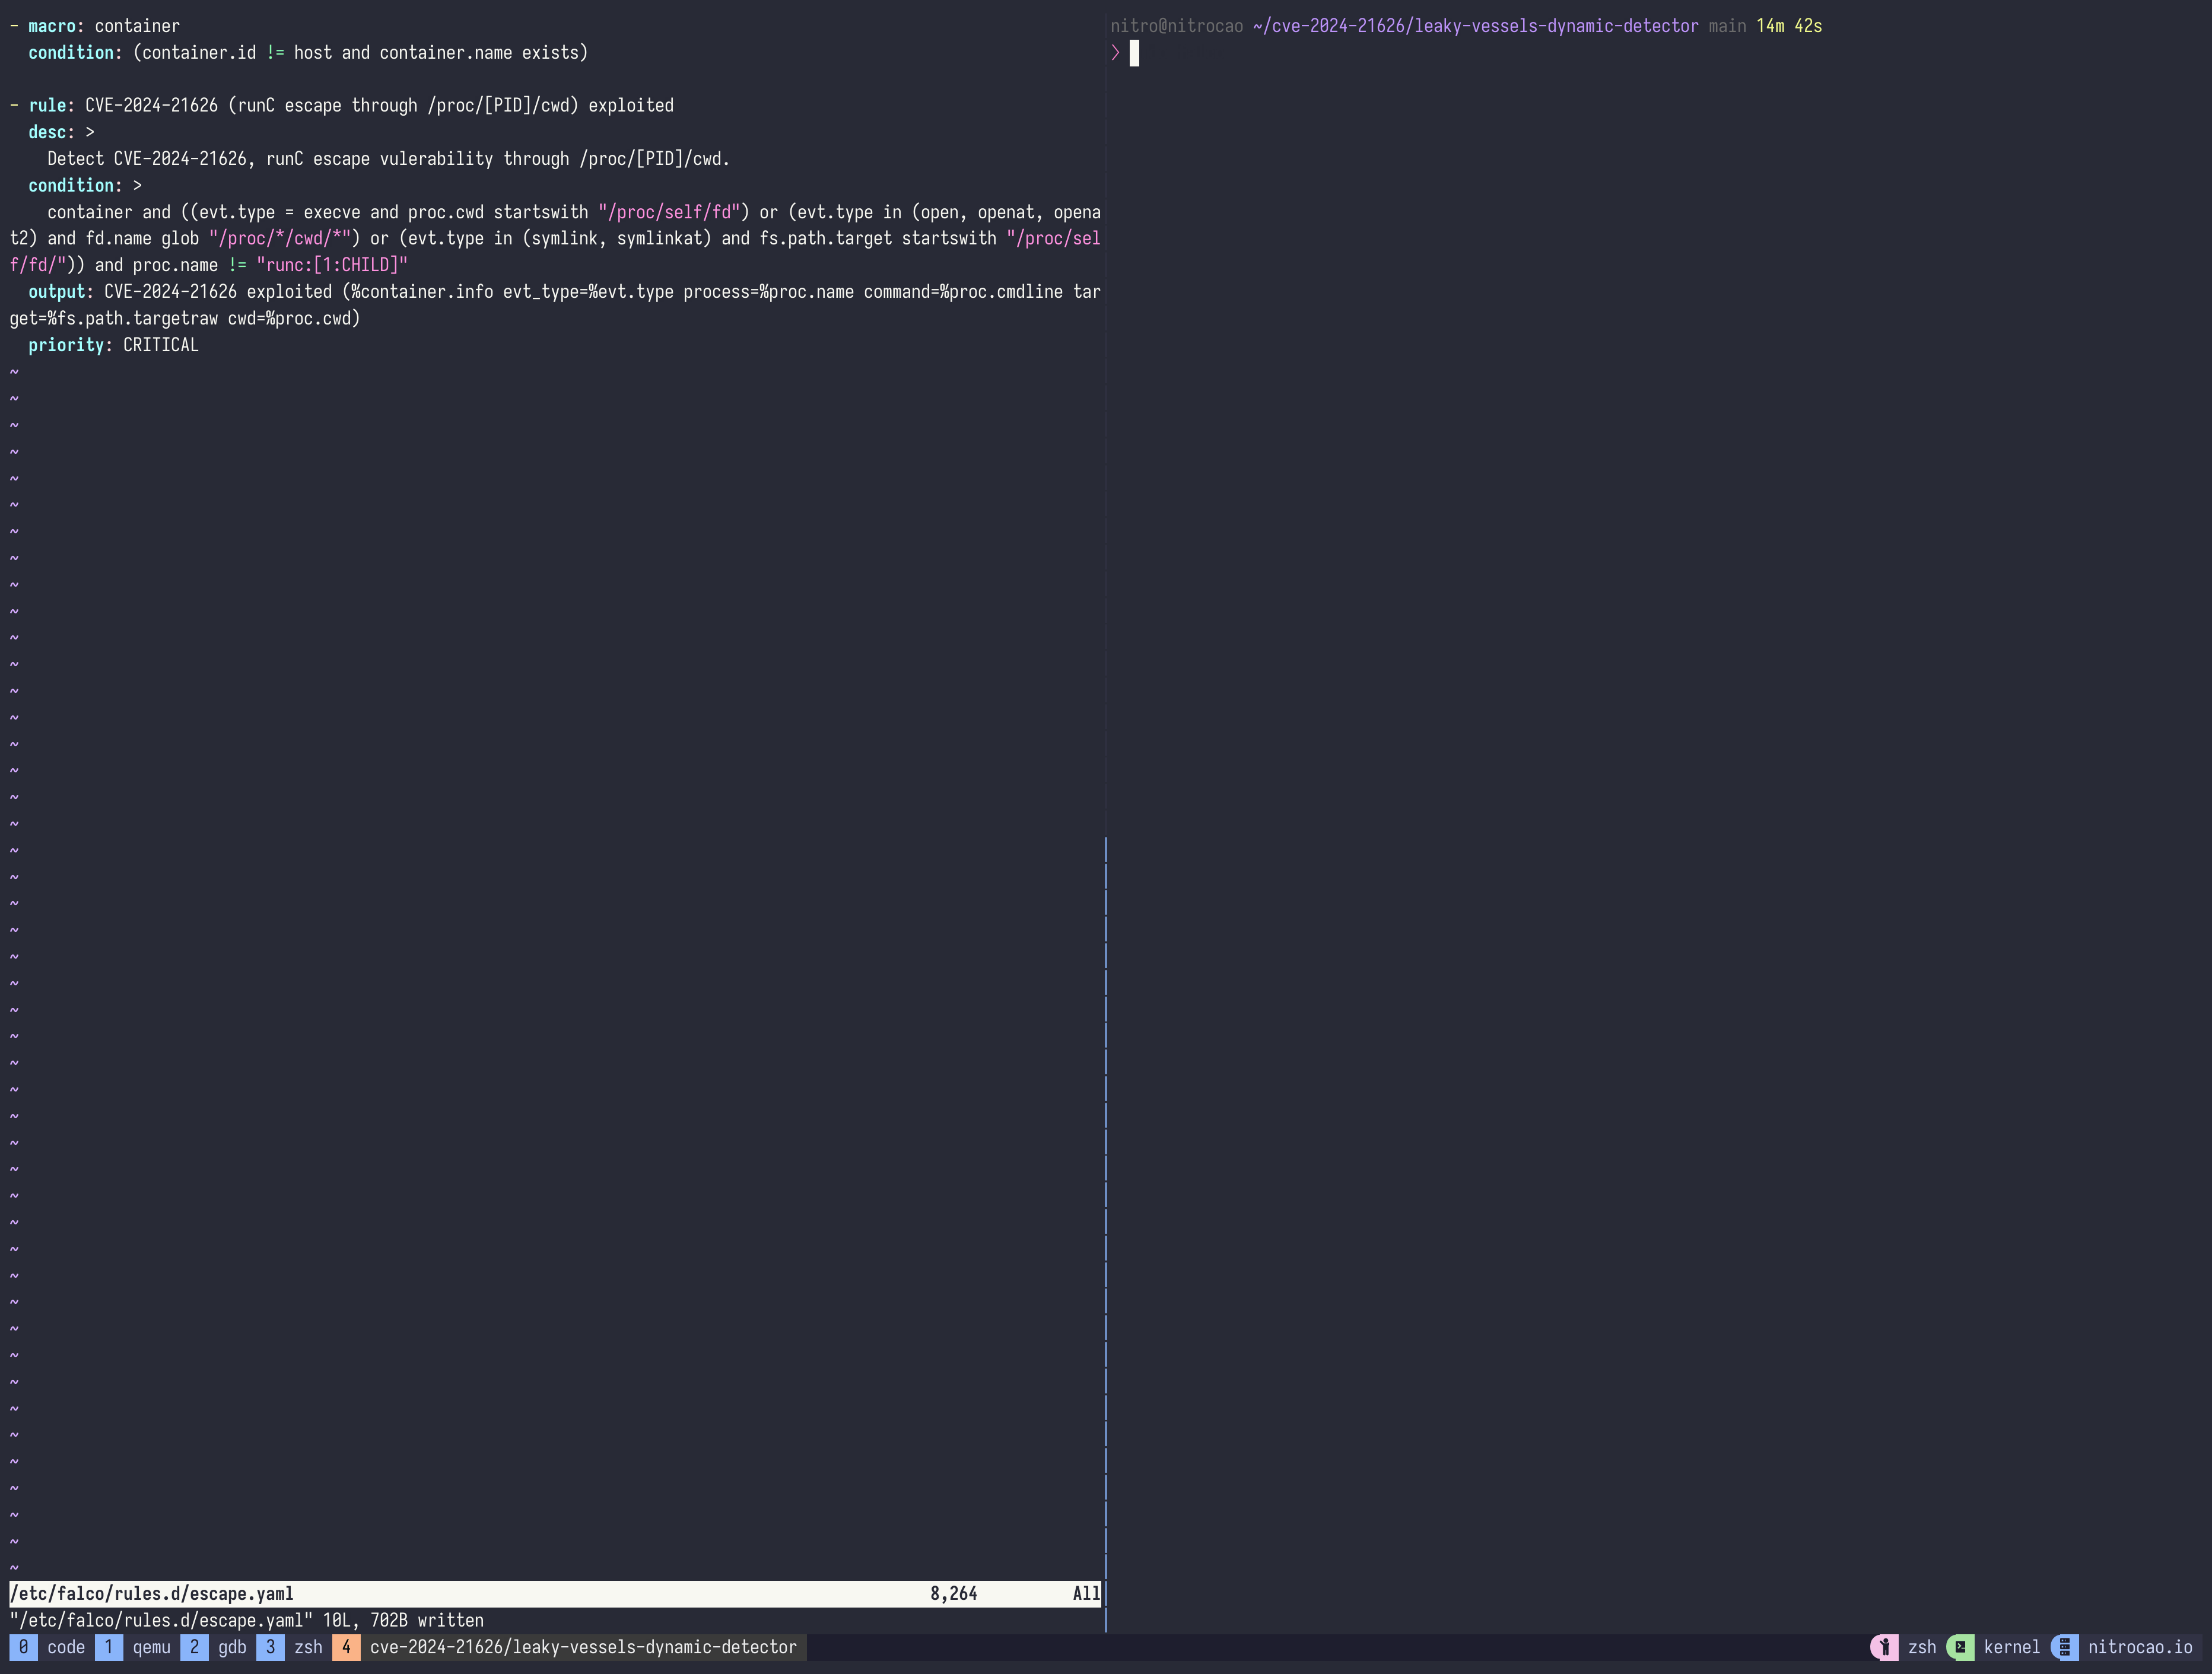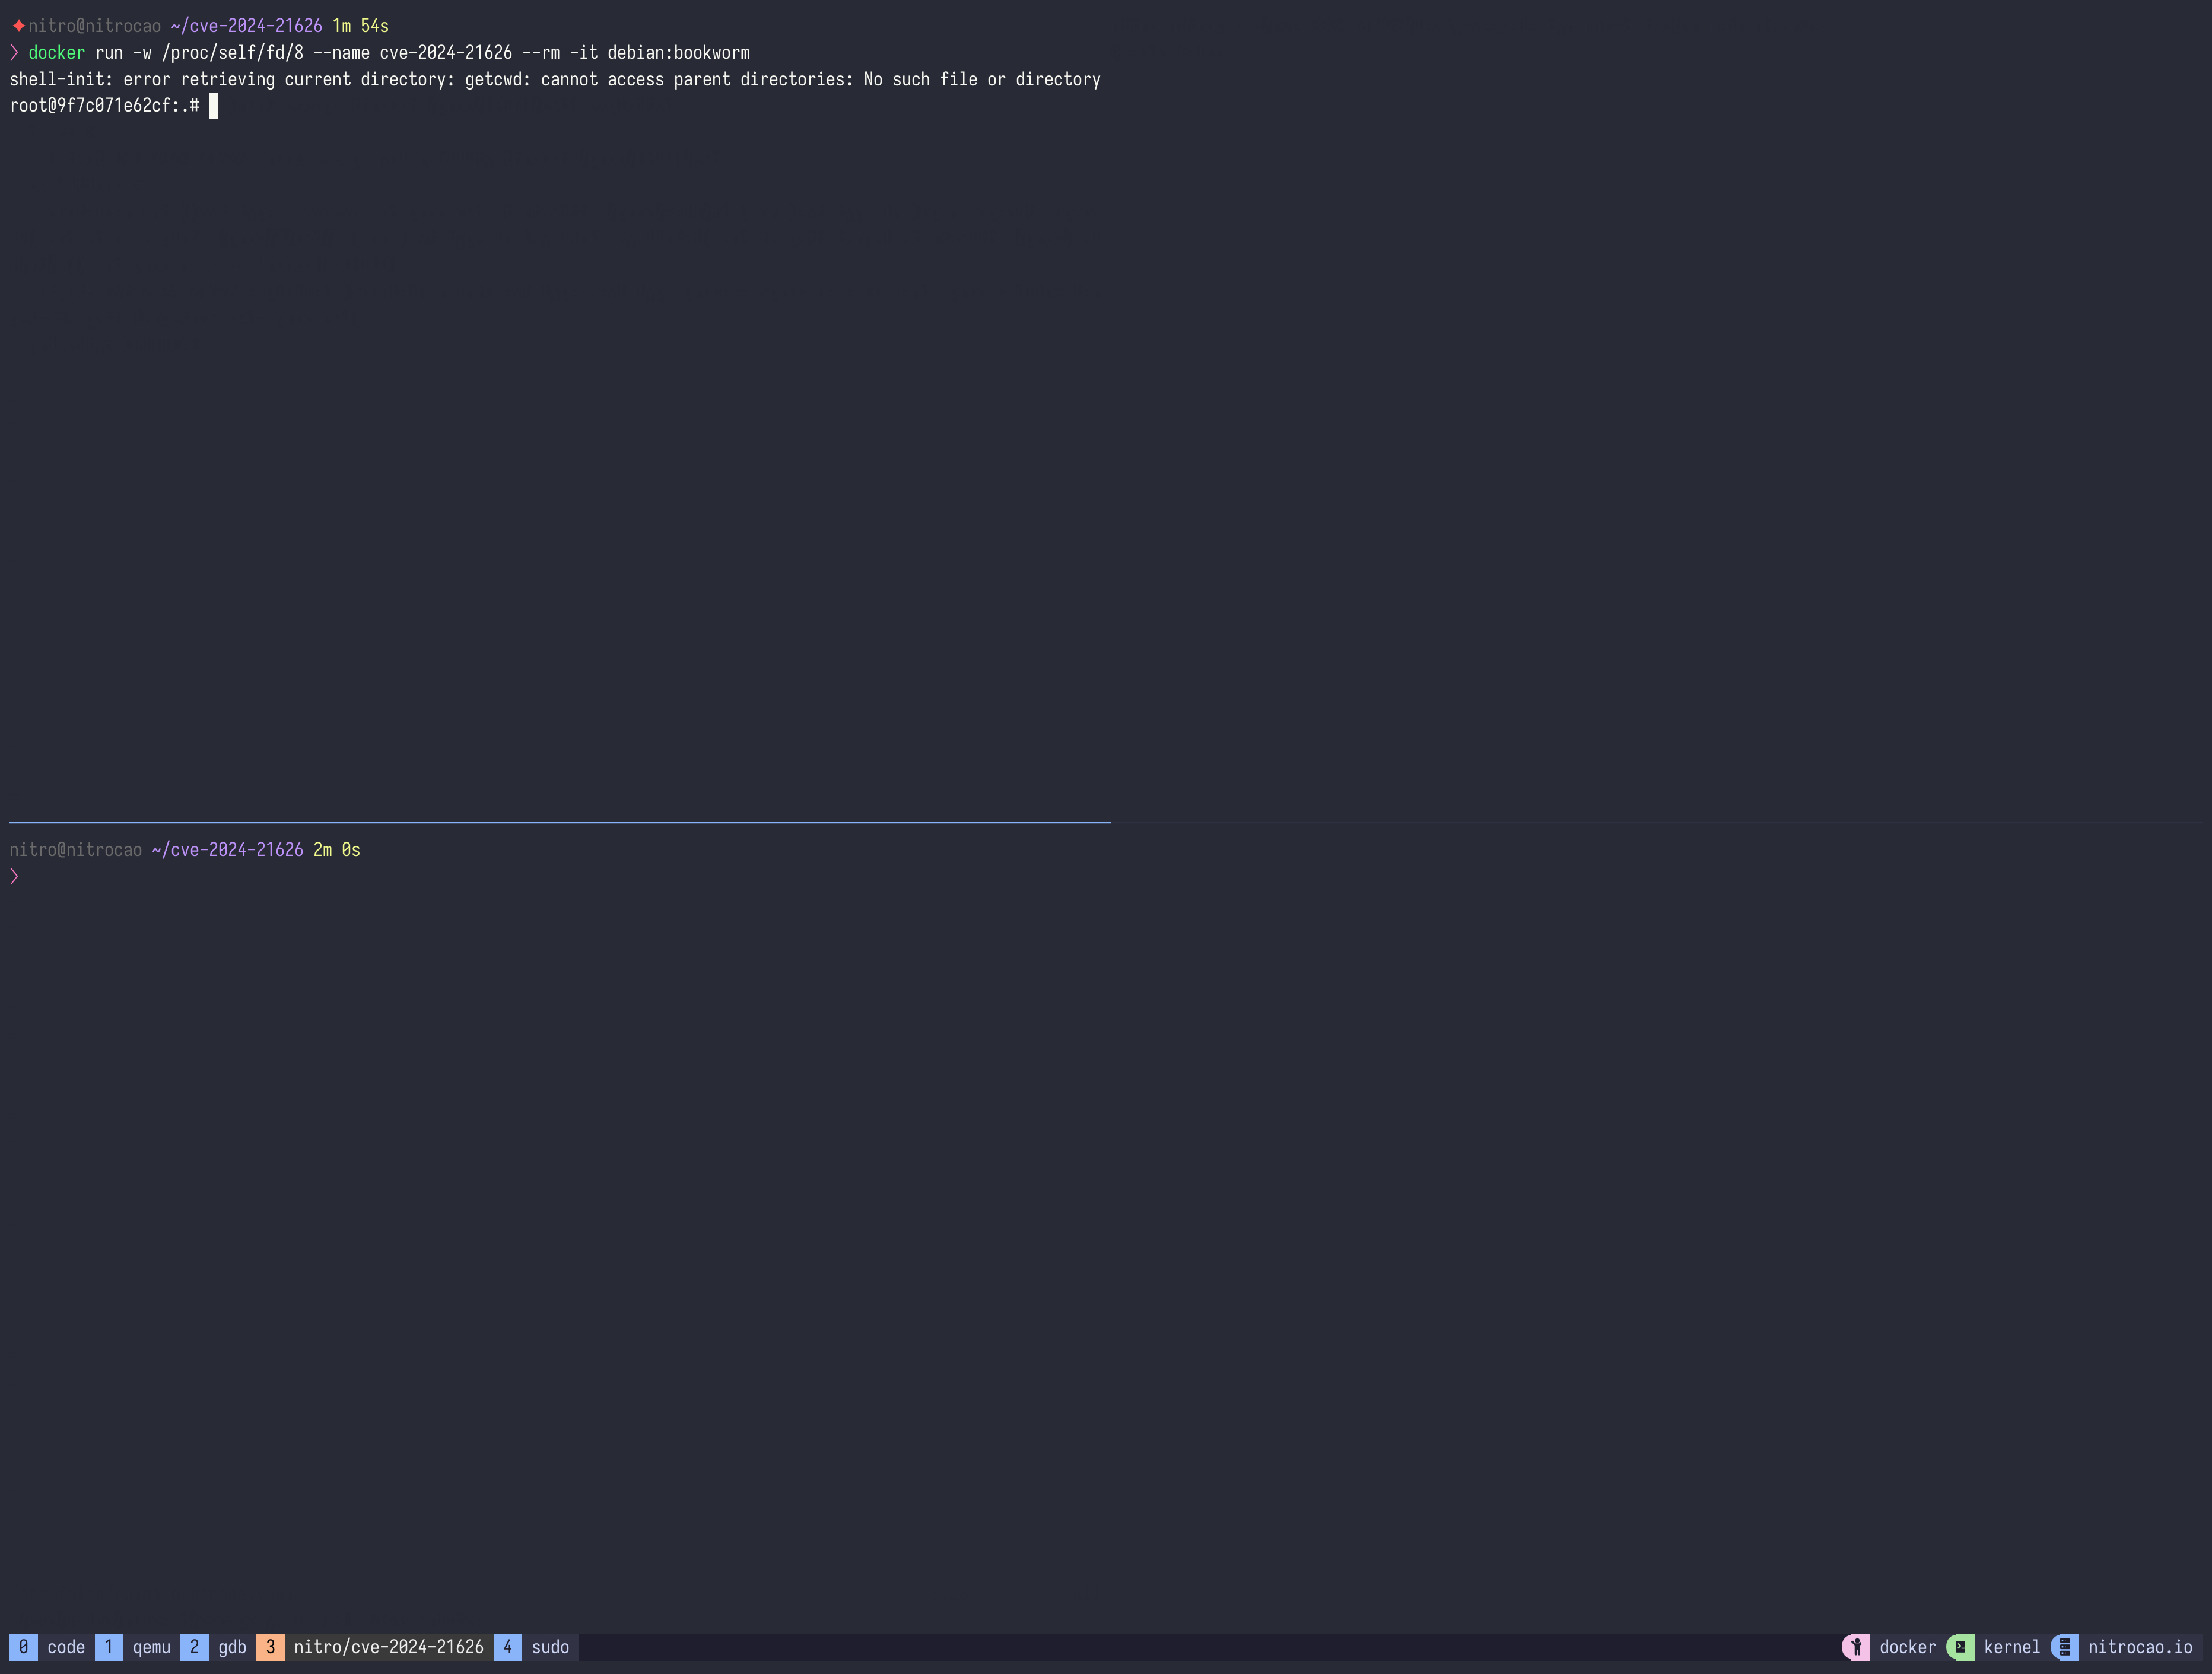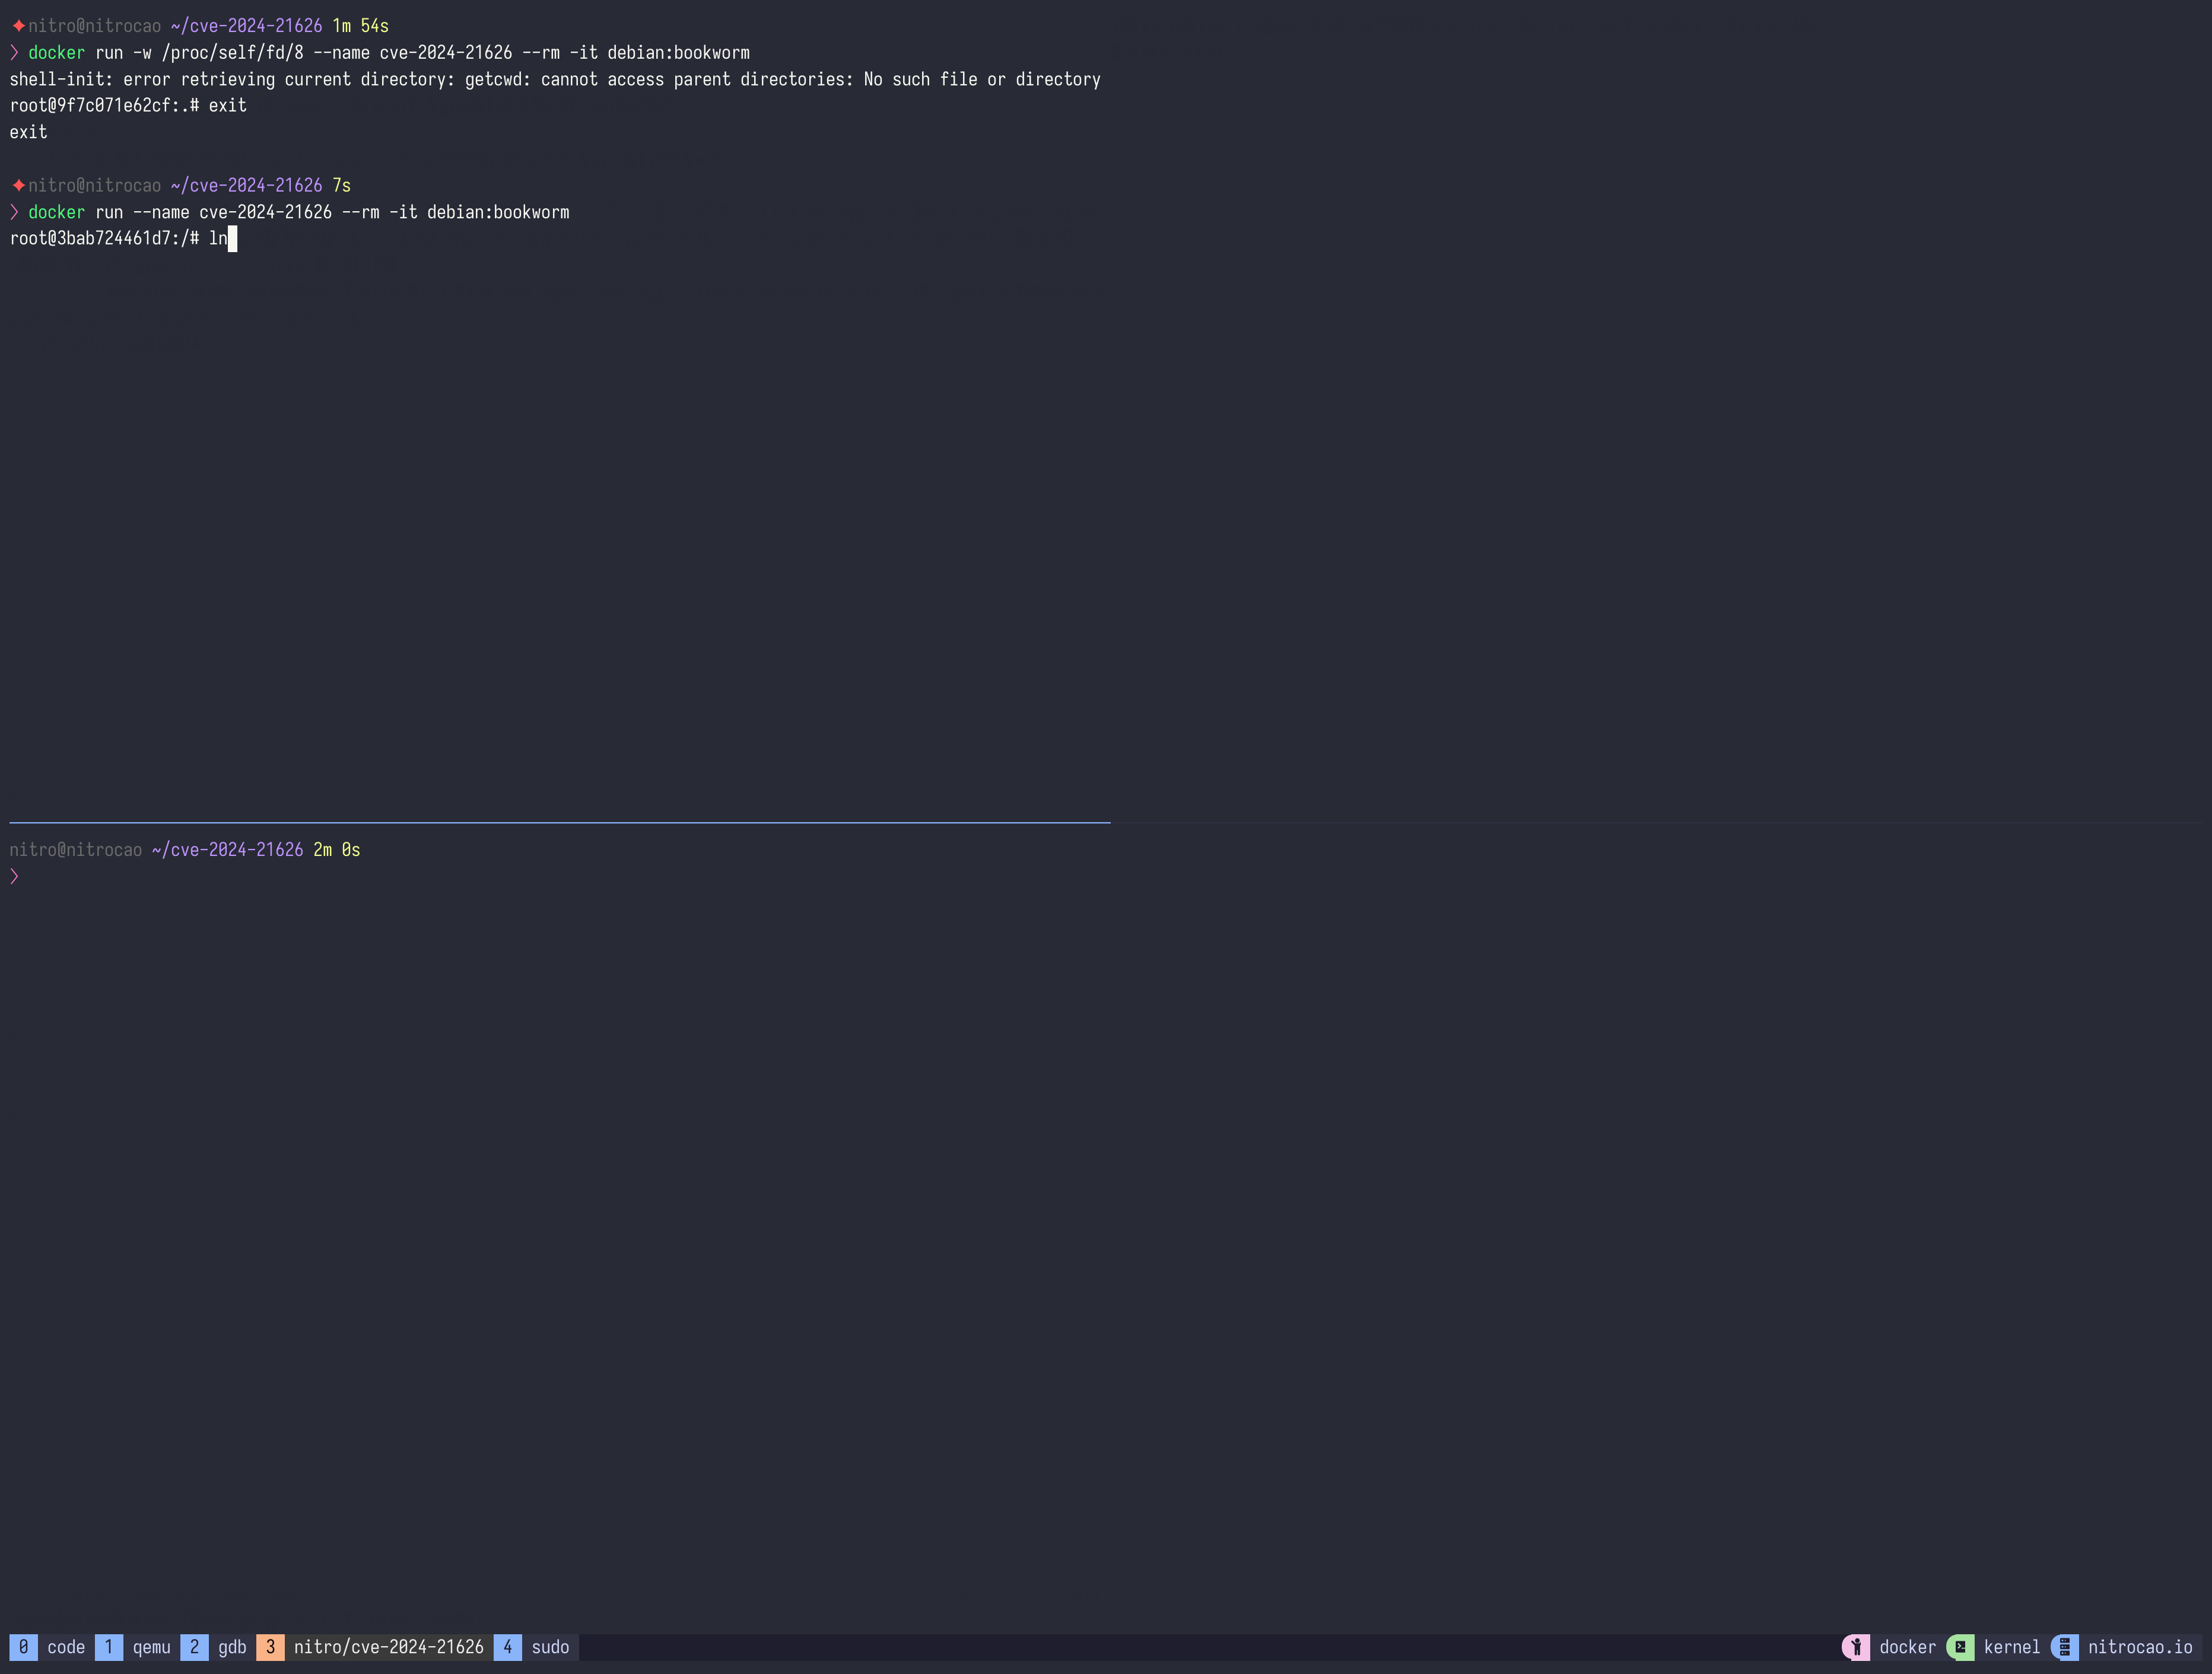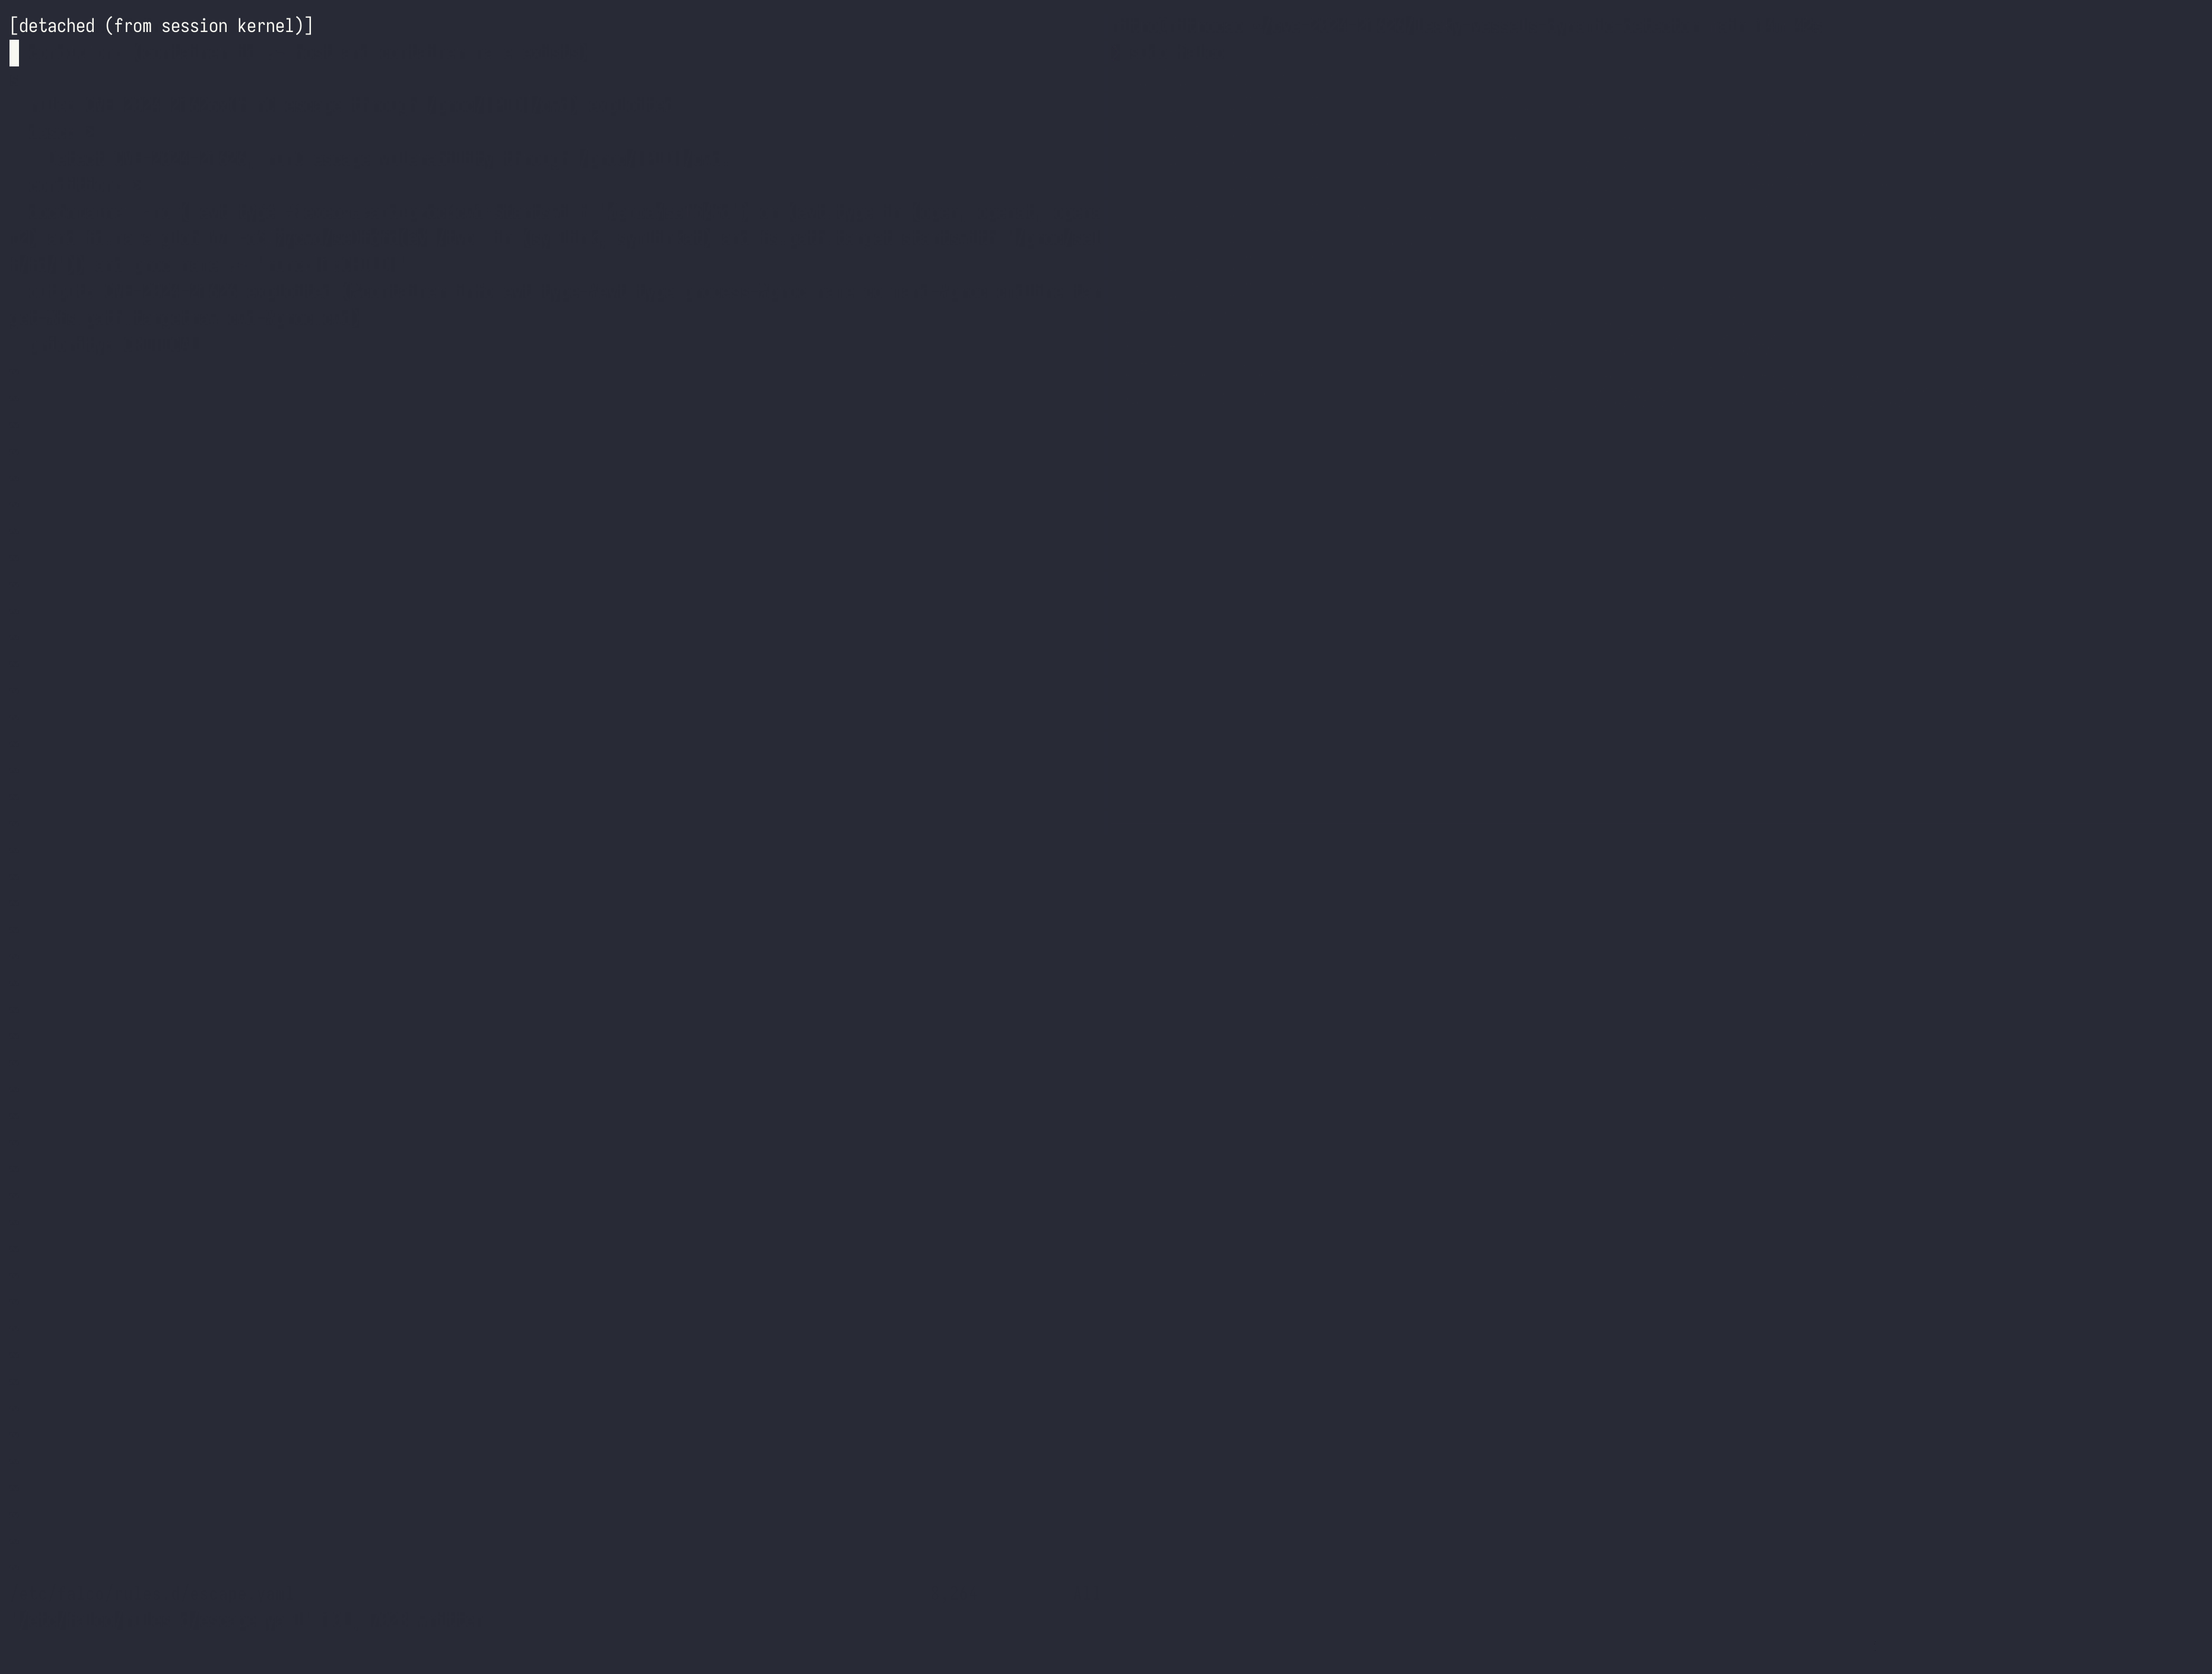 nitrocao/cve-2024-21626
PoC and Detection for CVE-2024-21626
 yoshino-s/cve-2025-1974
Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…
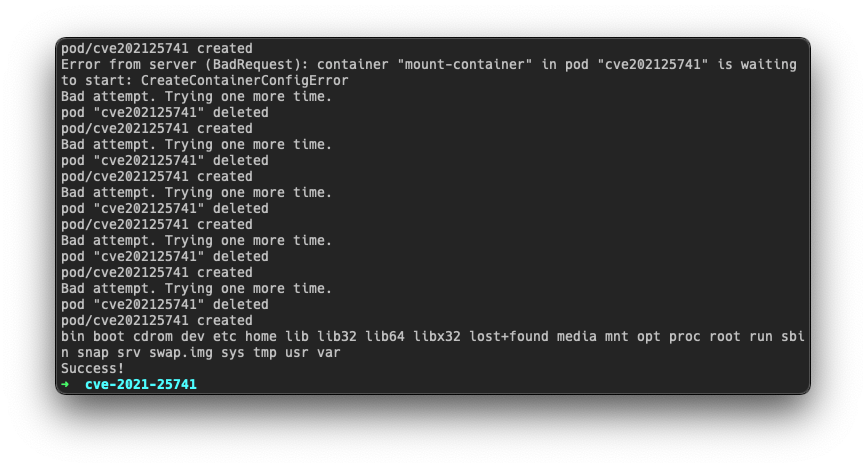 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 qi4l/cve-2026-31431-container-escape
Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.
 nccgroup/abstractshimmer
Proof of concept for CVE-2020-15257 in containerd.
 jpts/cve-2025-23266-poc
Proof-of-concept exploit for CVE-2025-23266 (NVIDIAScape) targeting NVIDIA AI container runtime. Demonstrates container escape via GPU driver…