

kube-hunter
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
cloud-infrastructure-securitycloud-securitycontainer-escape+5
5.1k
aquasecurity/kube-hunterHunt for security weaknesses in Kubernetes clusters
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
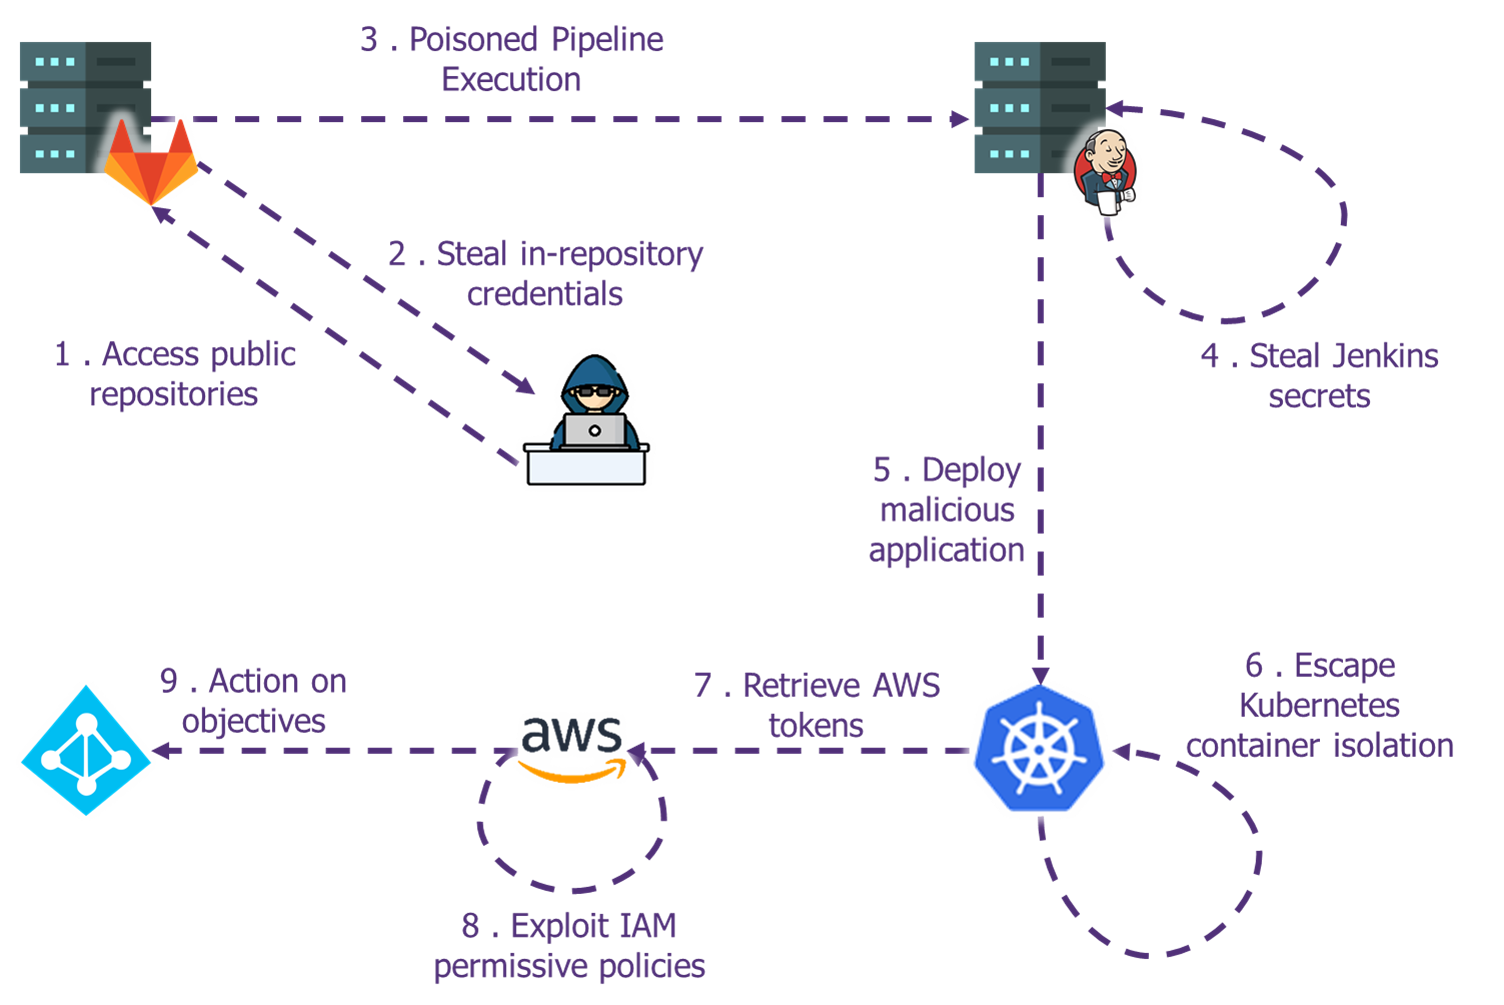 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 sk3pper/cve-2024-21626
Proof-of-concept exploits for CVE-2024-21626, a Docker/runc container escape vulnerability, demonstrating multiple attack vectors to access and…
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
 likekabin/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, appending a payload to the host runc binary via Docker container escape.
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
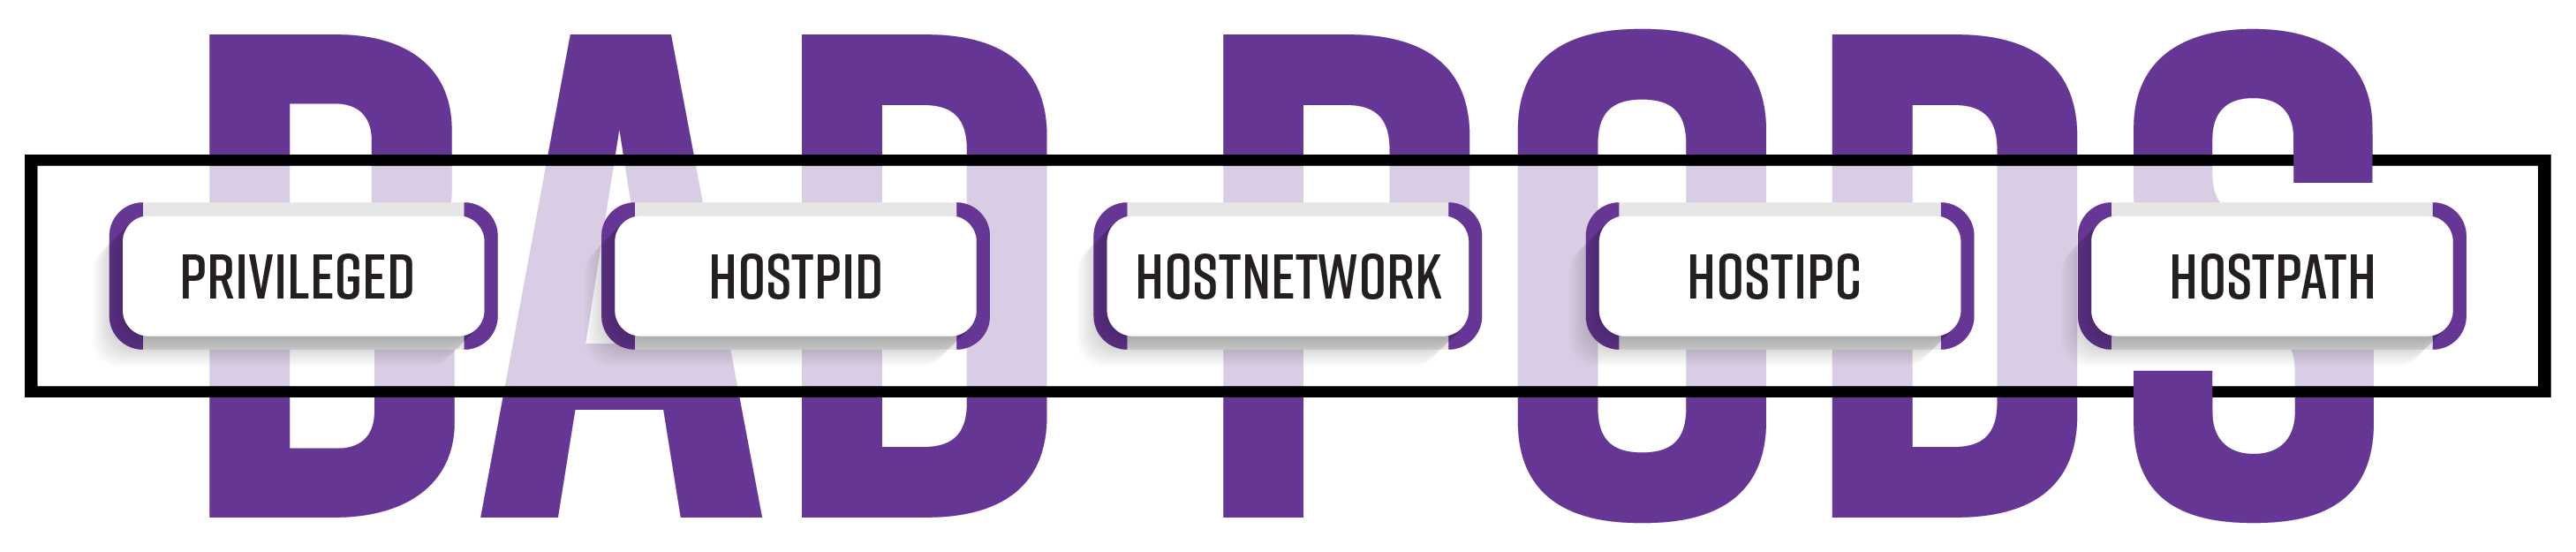 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 fahmifj/docker-breakout-runc
Modified version of CVE-2019-5736-PoC by Frichetten
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 thekevinday/docker_lightman_exploit
Docker CVE-2022-37708
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 sgkdev/ipv6_frag_escape
Linux LPE - Reliable Jail/Container Escape
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…