
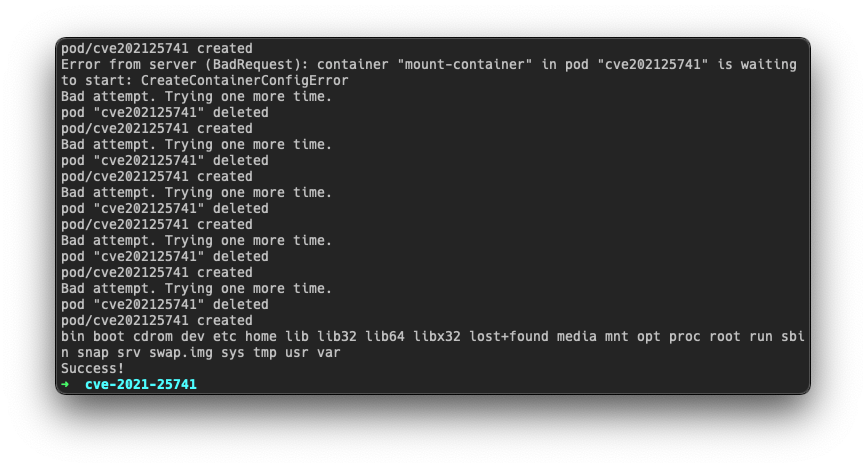
CVE-2021-25741
 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
cloud-securitycontainer-escapeexploitation+2
30
betep0k/cve-2021-25741Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 sgkdev/ptrace_may_dream
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 kianabin/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
 jpts/cve-2022-0847-dirtypipe-container-breakout
Proof-of-concept exploit for CVE-2022-0847 (DirtyPipe) enabling container breakout via kernel privilege escalation. Includes demonstration and…
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 skynet-f-nvidia/cve-2025-31133
CVE-2025-31133 PoC
 pppxo/cve-2025-9074-poc-bash
Bash-based proof-of-concept exploit for CVE-2025-9074 enabling Docker container escape by mounting host Windows C: drive via vulnerable API endpoints.
 louisliunova/cve-2022-1227_exploit
A script for exploiting CVE-2022-1227
 followboy1999/cve-2022-25365
Proof-of-concept exploit for CVE-2022-25365, a privilege escalation vulnerability in Docker Desktop for Windows via named pipe impersonation.
 rocket-panda/cve-2025-9074
Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…
 spiralbl0ck/cve-2024-32462
CVE-2024-32462 code exec sbx escape
 matesz44/cve-2025-9074
CVE-2025-9074: Docker Desktop LPE via Docker Engine API wo/ AuthN in posix sh
 hikame/docker_escape_pwn
Escape from Docker using CVE-2017-1000112 and CVE-2017-18344, including gaining root privilage, get all capbilities, namespace recovery, filesystem…
 billith/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, a runc container escape that overwrites the host runc binary to achieve root code execution on the host.
 h-wookie/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, demonstrating Docker container escape via runC vulnerability with reverse shell payload injection.
 adaammmeeee/little-joke
Some scripts to simulate an attack (used for CVE-2024-21626)
 datadog/dirtypipe-container-breakout-poc
Container Excape PoC for CVE-2022-0847 "DirtyPipe"