
CVE-2024-21626
 sk3pper/cve-2024-21626
Proof-of-concept exploits for CVE-2024-21626, a Docker/runc container escape vulnerability, demonstrating multiple attack vectors to access and…
cloud-securitycontainer-escapecontainer-security+3
2
sk3pper/cve-2024-21626Proof-of-concept exploits for CVE-2024-21626, a Docker/runc container escape vulnerability, demonstrating multiple attack vectors to access and…
 hulnothutu/cve-2026-31431
对 CVE-2026-31431 的复现分析、C 改编的 exp。
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
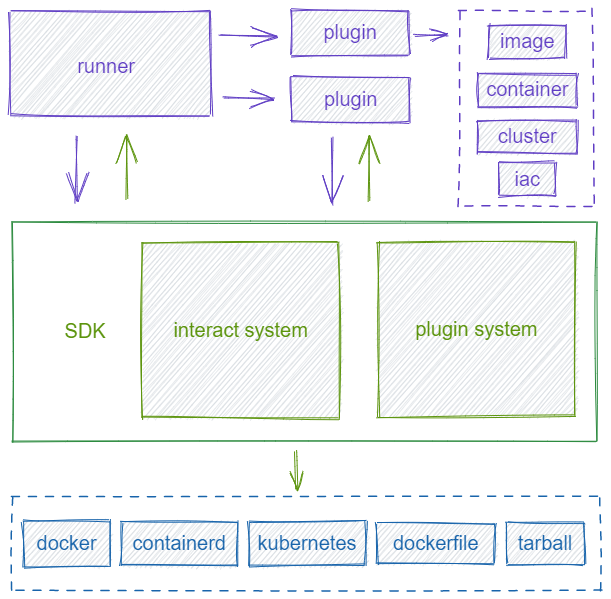 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
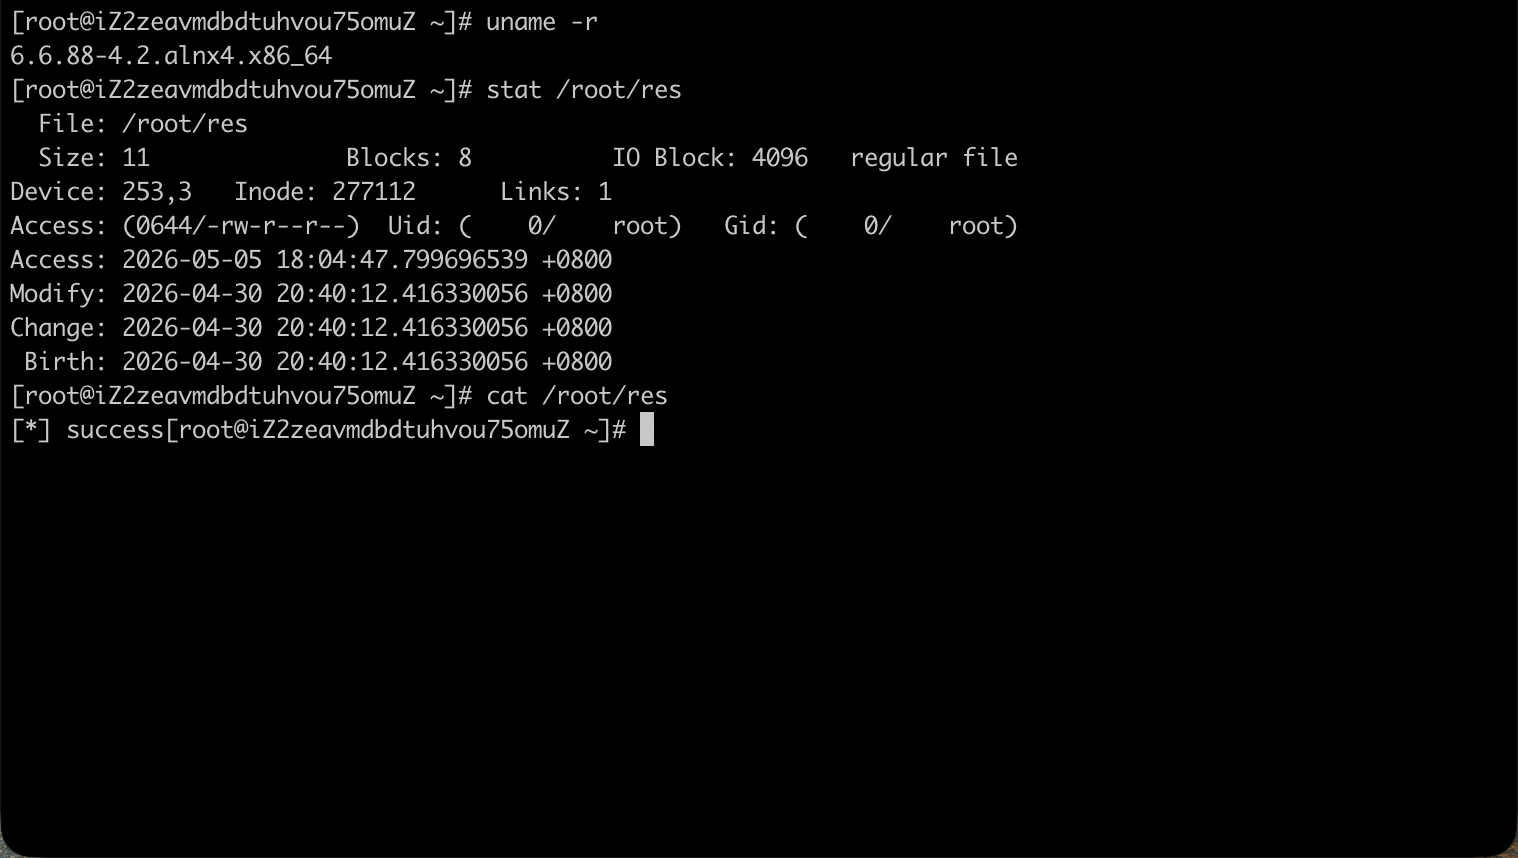 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 yoshino-s/cve-2025-1974
Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…
 qi4l/cve-2026-31431-container-escape
Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.