kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

CLI tool and library for generating a Software Bill of Materials from container images and filesystems

Proof of concept code for Datadog Security Labs referenced exploits.

Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…

CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer

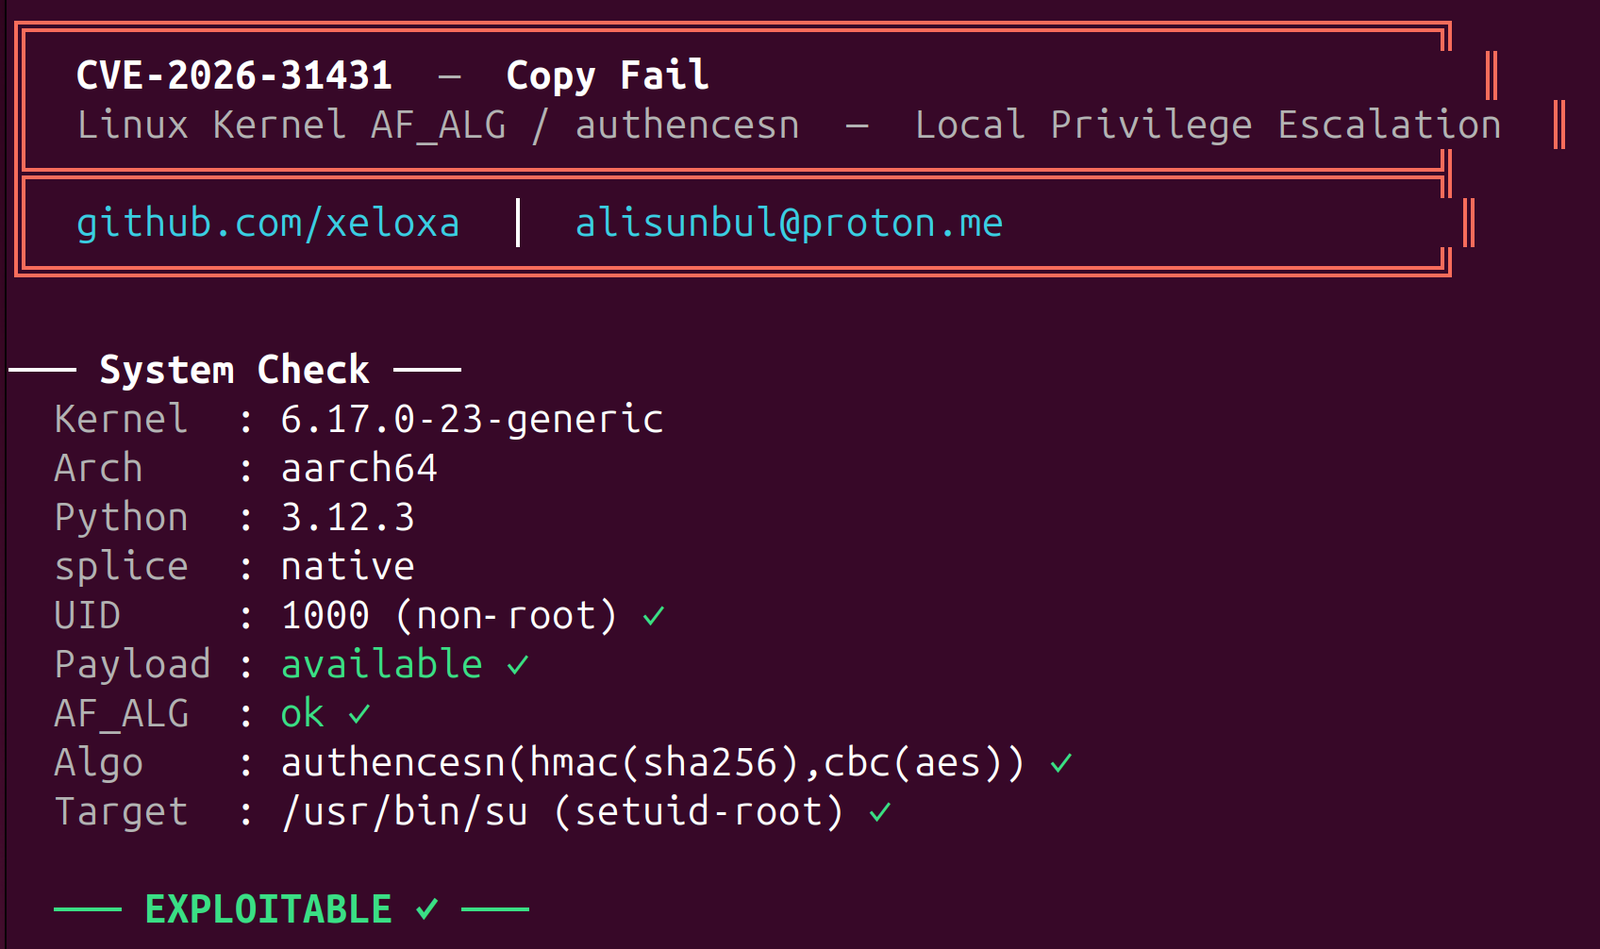
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.

Proof-of-concept demonstrating container escape on Kubernetes via CVE-2026-31431 kernel page-cache corruption, achieving node-level code execution…

POC for CVE-2025-55130

R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

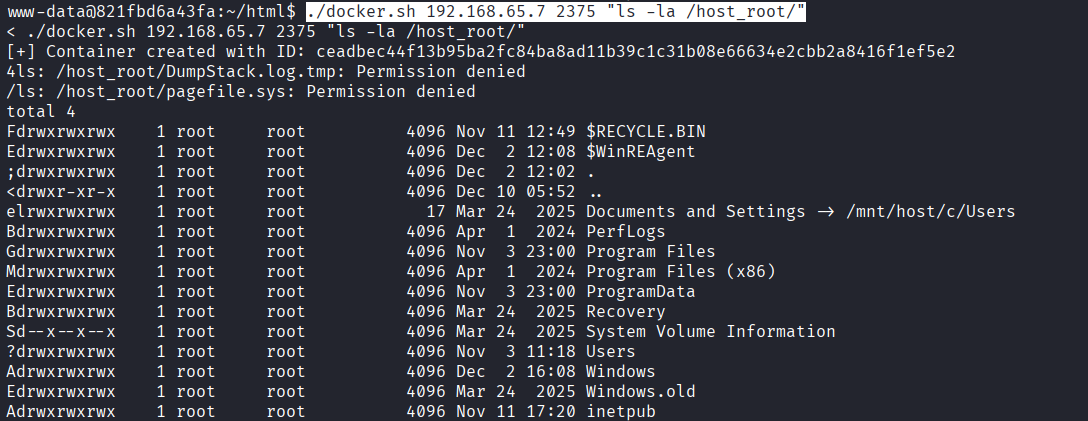
Bash-based proof-of-concept exploit for CVE-2025-9074 enabling Docker container escape by mounting host Windows C: drive via vulnerable API endpoints.

POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20

Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation vulnerability in sudo allowing chroot jail escape via specific sudoers…


Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…

POC code for CVE-2024-29510 and demo VulnApp

Proof-of-concept exploit for CVE-2021-41091: Moby (Docker Engine) directory traversal allowing unprivileged users to execute SUID binaries from…