kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

CLI tool and library for generating a Software Bill of Materials from container images and filesystems

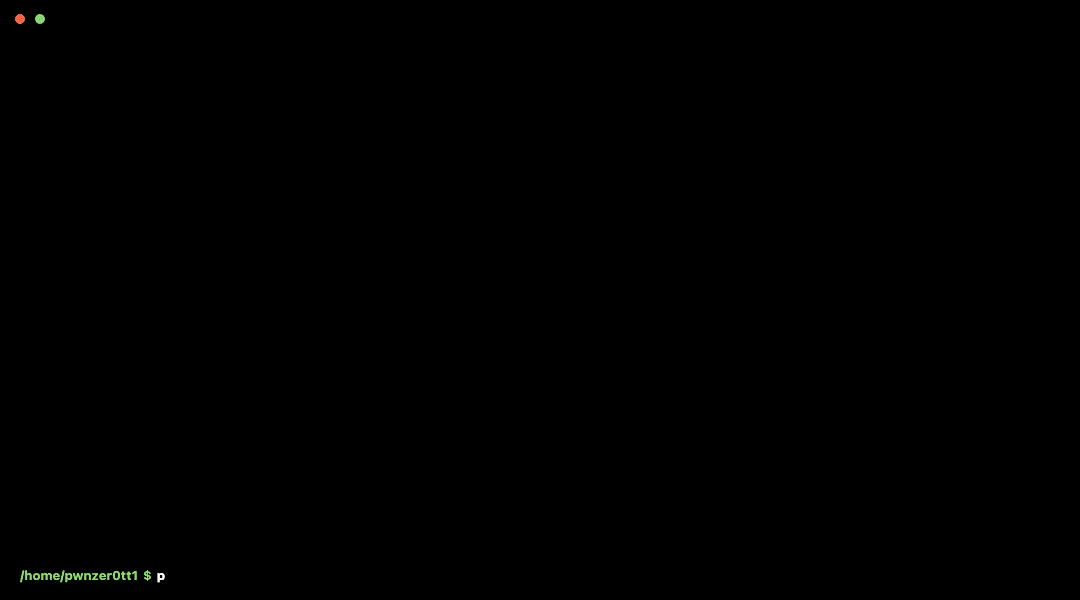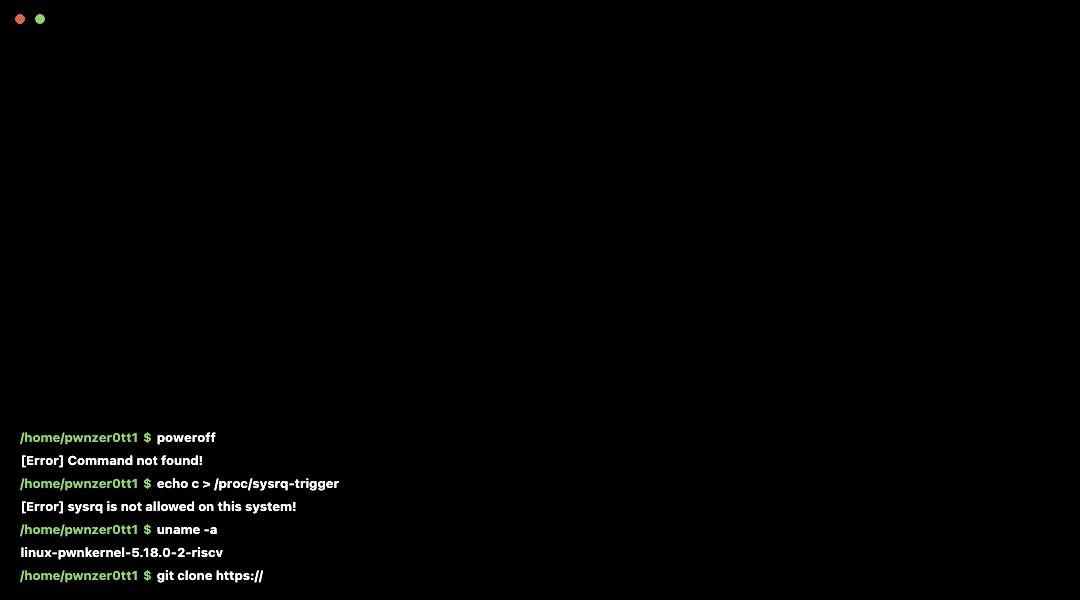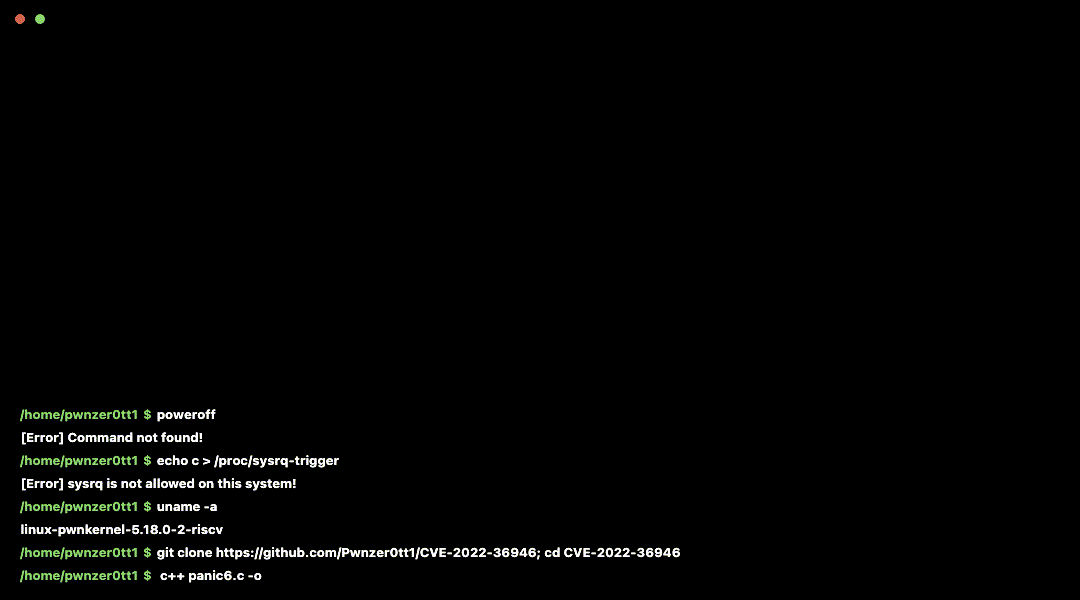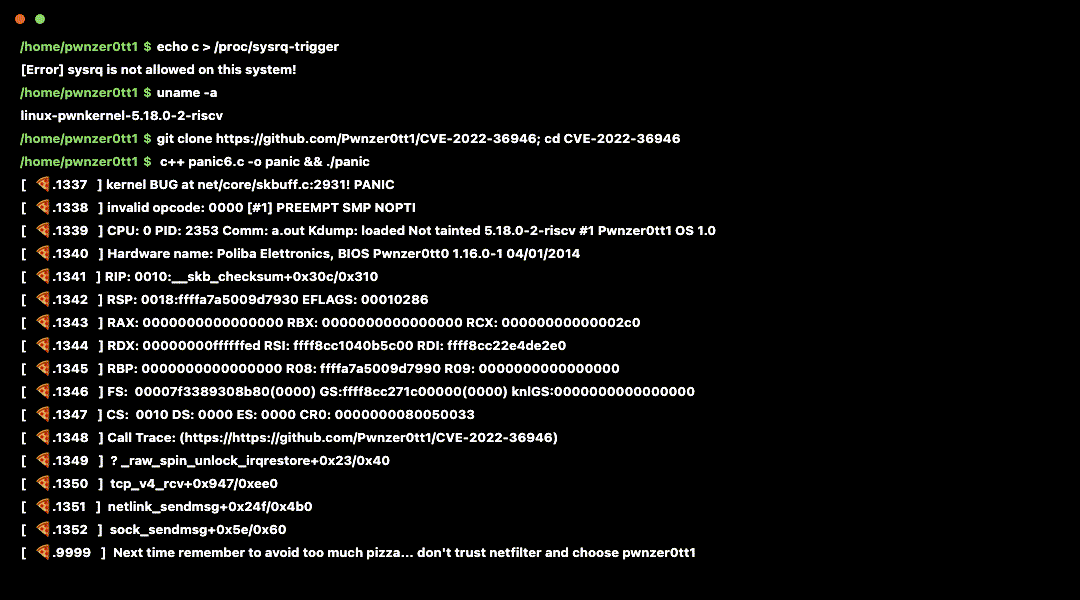
CVE-2022-36946 linux kernel panic in netfilter_queue

An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.

Validation of best practices in your Kubernetes clusters

Proof of concept code for Datadog Security Labs referenced exploits.

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.


PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer

POCs and Tetragon Rules for CVE-2024-21626 and CVE-2025-31133

Linux LPE - Reliable Jail/Container Escape

Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit

PHP poc, exploit for CVE-2025-9074

对 CVE-2026-31431 的复现分析、C 改编的 exp。