Copy-Fail-CVE-2026-31431-Kubernetes-PoC

Proof-of-concept demonstrating container escape on Kubernetes via CVE-2026-31431 kernel page-cache corruption, achieving node-level code execution…

Proof-of-concept demonstrating container escape on Kubernetes via CVE-2026-31431 kernel page-cache corruption, achieving node-level code execution…

Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.

Container escape on any docker container with healthcheck enabled via CVE-2026-31431

Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…

Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.

Proof-of-concept exploit for CVE-2026-31431 demonstrating container escape and privilege escalation in OpenShift environments.

Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.

Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…

POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20

Proof-of-concept exploit for CVE-2019-5736, a Docker container escape via runc binary overwrite, enabling host shell access through libseccomp…

Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.

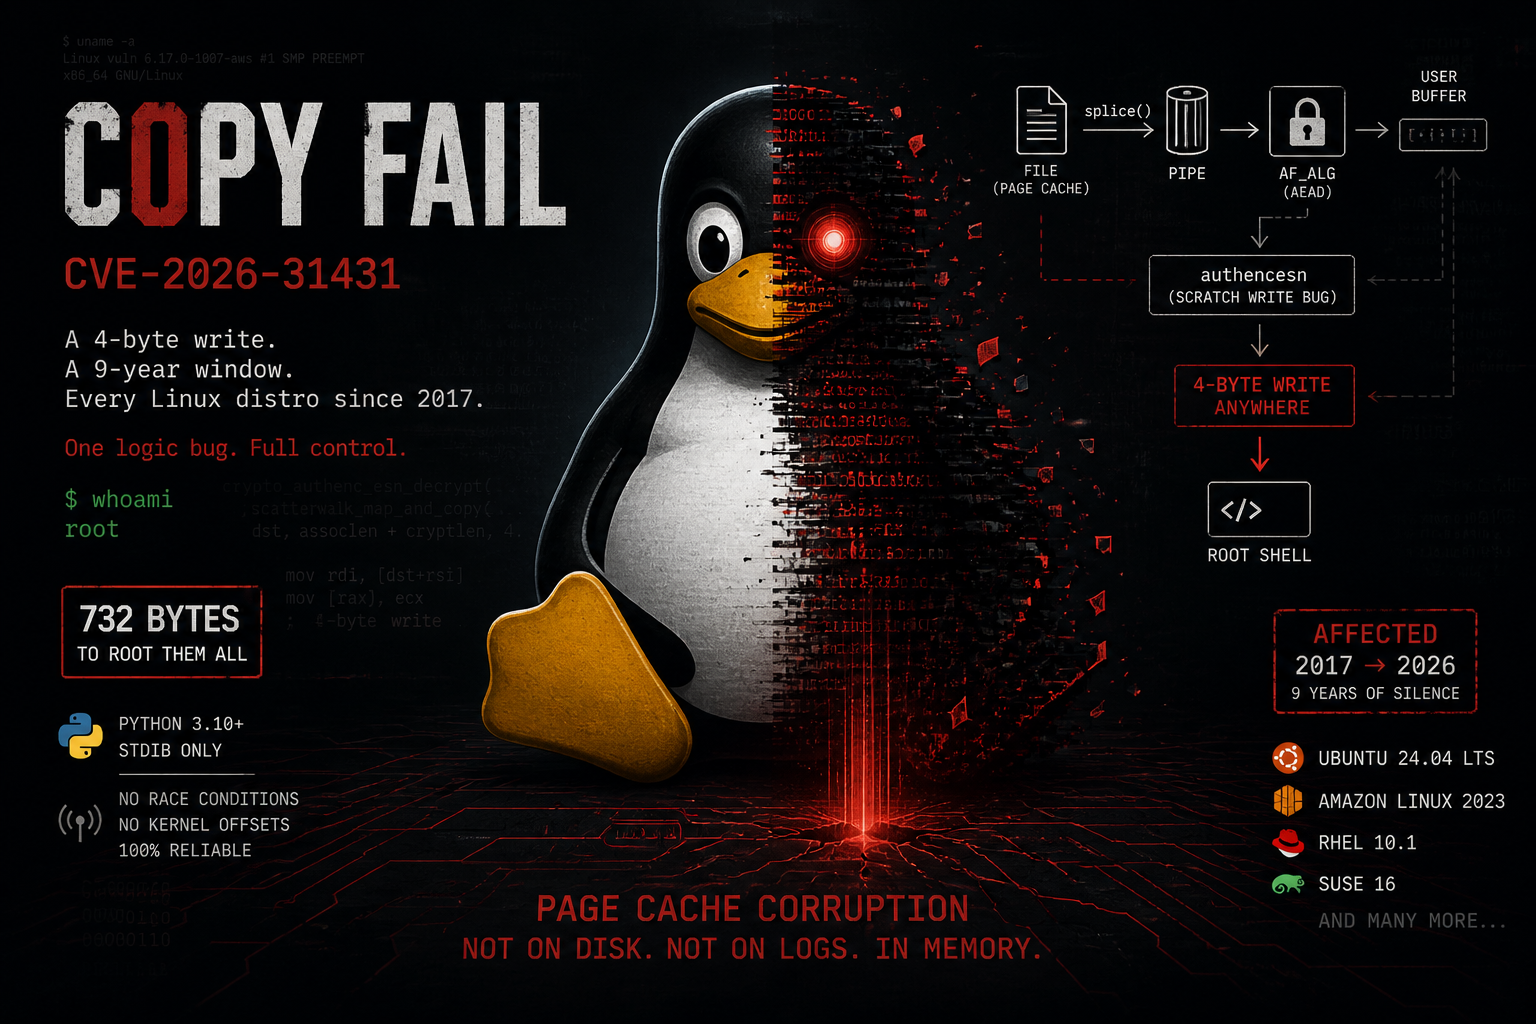
A structured explanation of CVE-2026-31431 (Copy Fail), connecting the three kernel changes that introduced the vulnerability and enabled its…

This project is exploit for some docker containers with similar to vulnerability code: CVE-2020-35191

Docker CVE-2022-37708

Docker + CVE-2015-2925 = escaping from --volume