

Container_escape
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
container-escapecontainer-securityexploitation+4
49
markakd/container_escapeContainer escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
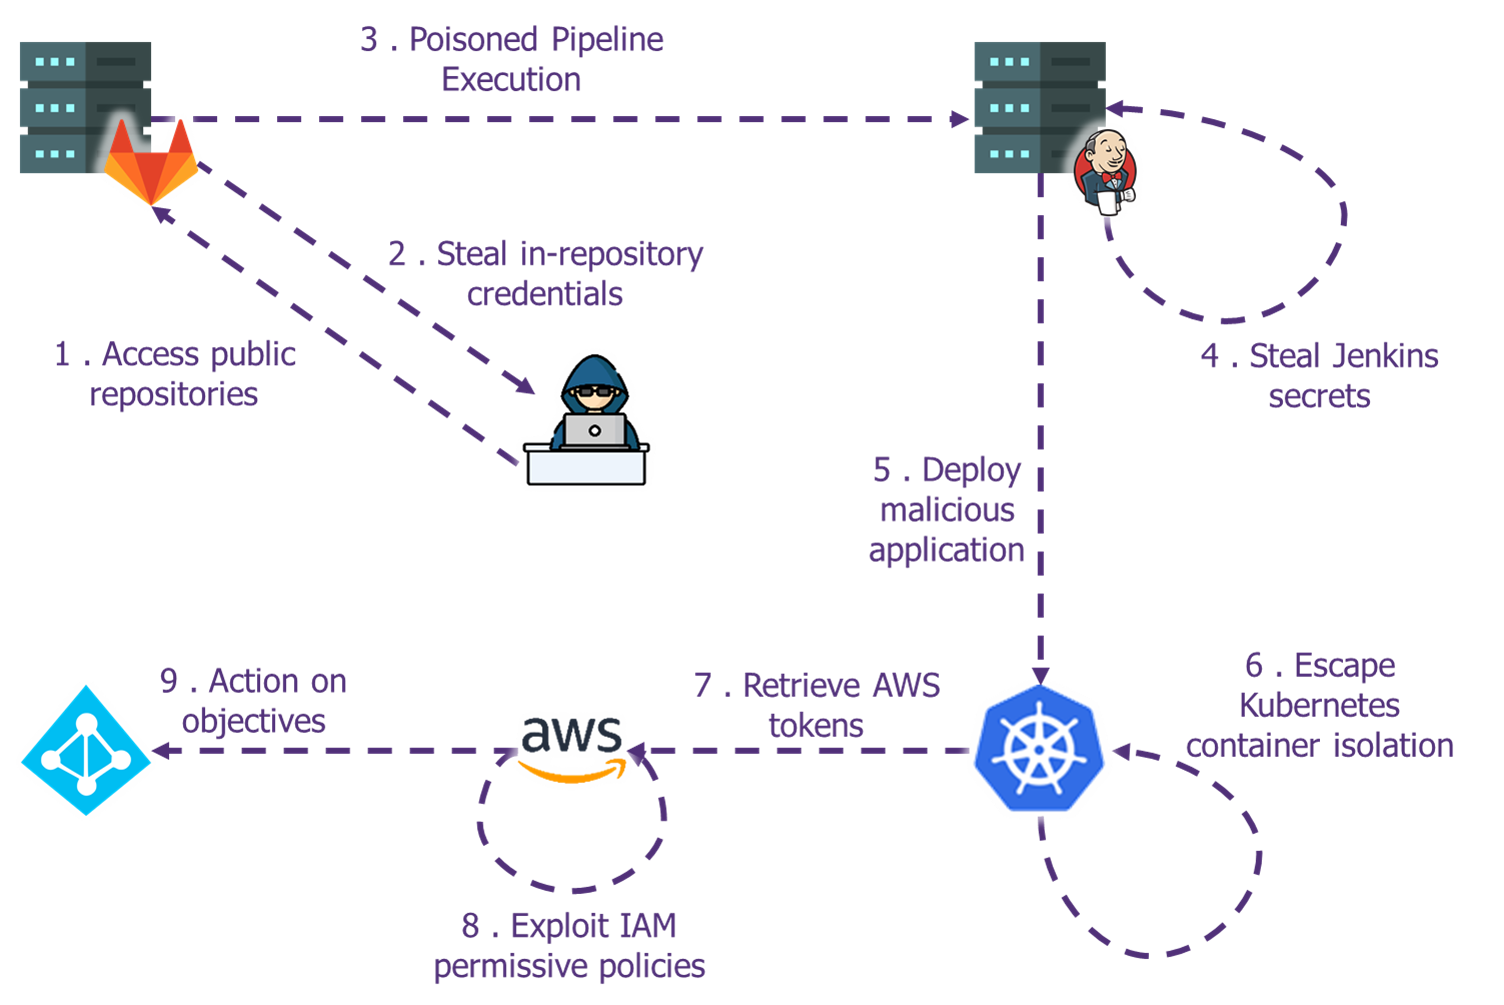 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 george0papasotiriou/cve-2026-5555-container-escape-via-proc-self-fd-symlink-in-shared-volume
Proof-of-concept exploit for CVE-2026-5555, demonstrating container escape via /proc/self/fd symlink in rshared volumes to overwrite host files and…
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 nicetop1027/cve-2026-d0cker
Proof-of-concept exploit for critical runC container escape vulnerability (CVE-2026-Pending) with symlink race condition, including Go PoC, analysis,…
 laysakura/cve-2024-21626-demo
Demonstration of CVE-2024-21626 container escape exploit allowing host root access via malicious Docker image, with step-by-step attack scenario for…