
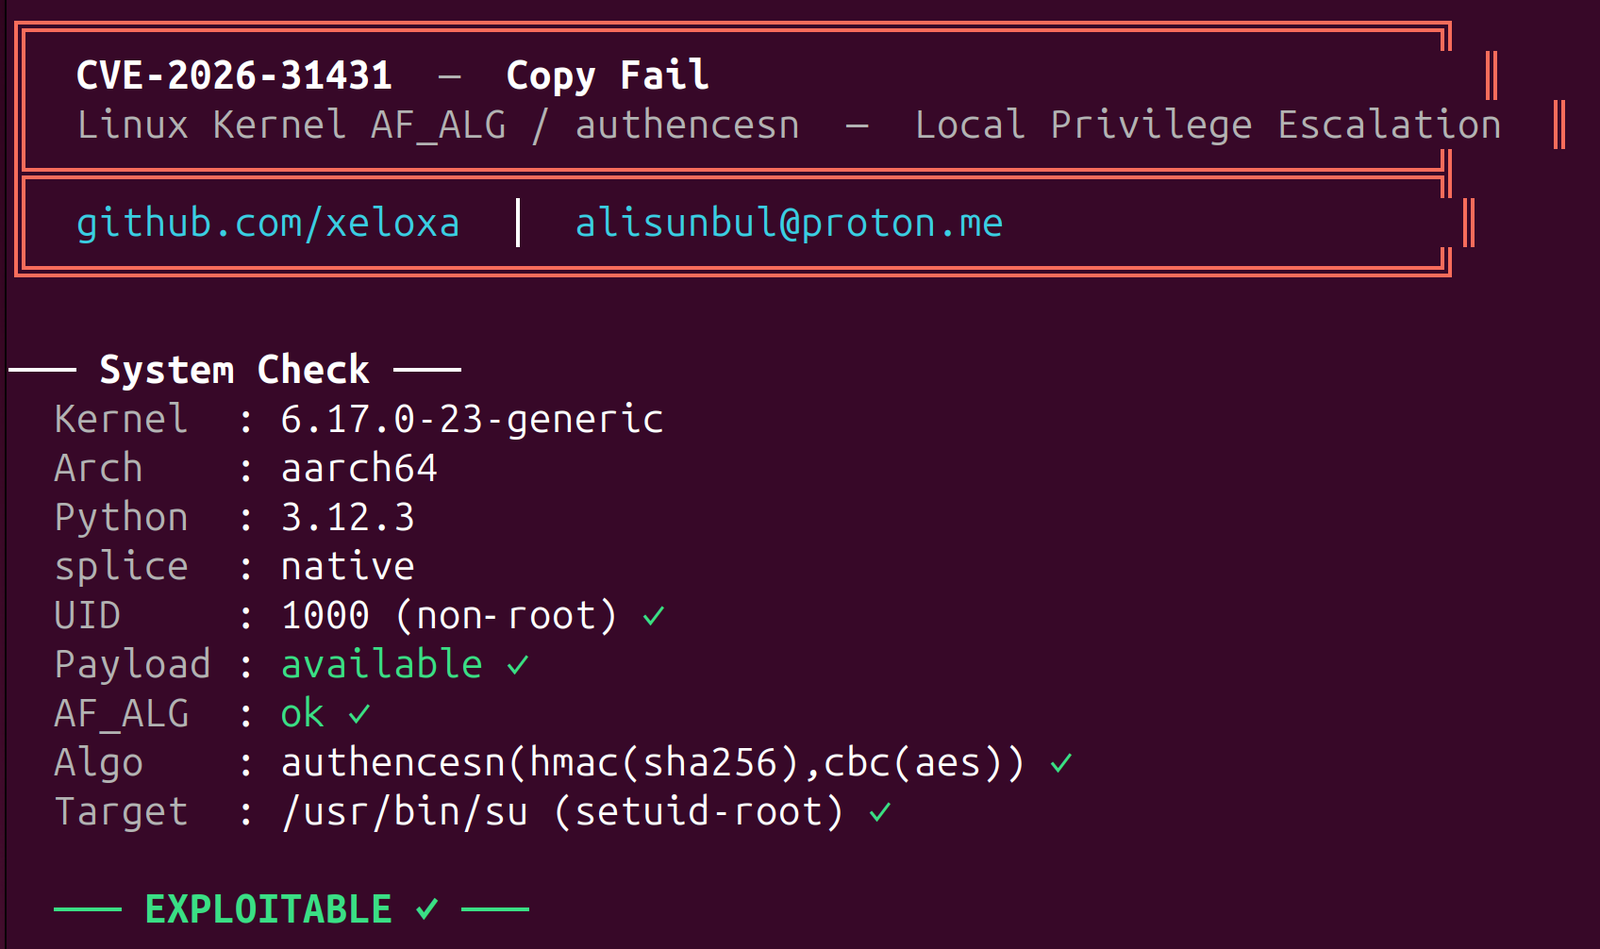
copyfail-exploit
 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
binary-exploitationcontainer-escapeexploitation+3
34
xeloxa/copyfail-exploitCopy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
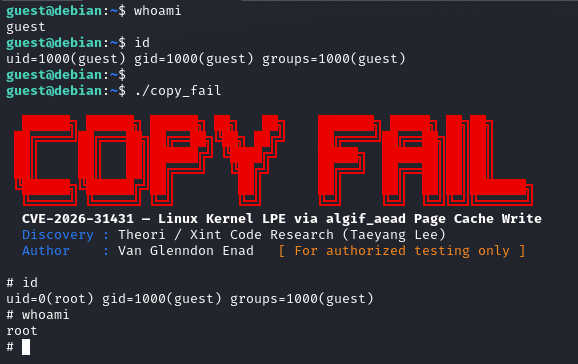 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 mishl-dev/cve_2026_31431
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 gmeghnag/test-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 demonstrating container escape and privilege escalation in OpenShift environments.
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
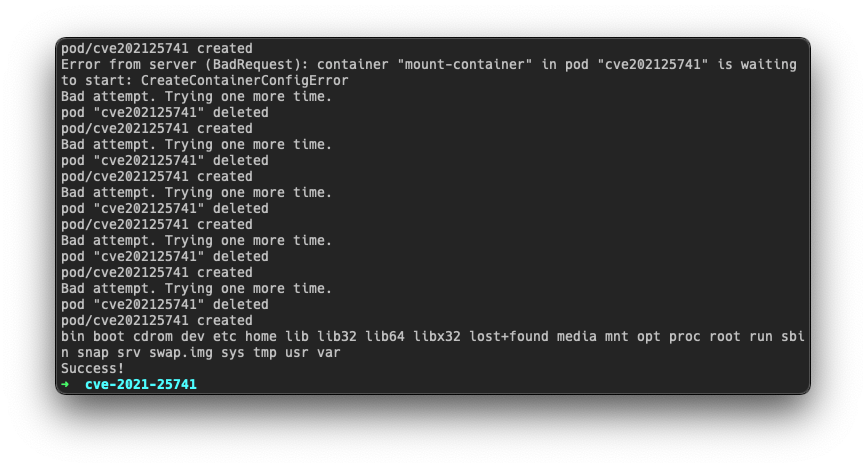 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 berdav/cve-2026-41567
Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.
 sgkdev/bad_garbage
CVE-2026-53361 AF_UNIX GC vs MSG_PEEK use-after-free container escape
 davidrxchester/cve-2026-5817
Docker Container-to-Host Remote Code Execution POC via vllm-metal trust_remote_code=True
 veritas501/pipe-primitive
An exploit primitive in linux kernel inspired by DirtyPipe
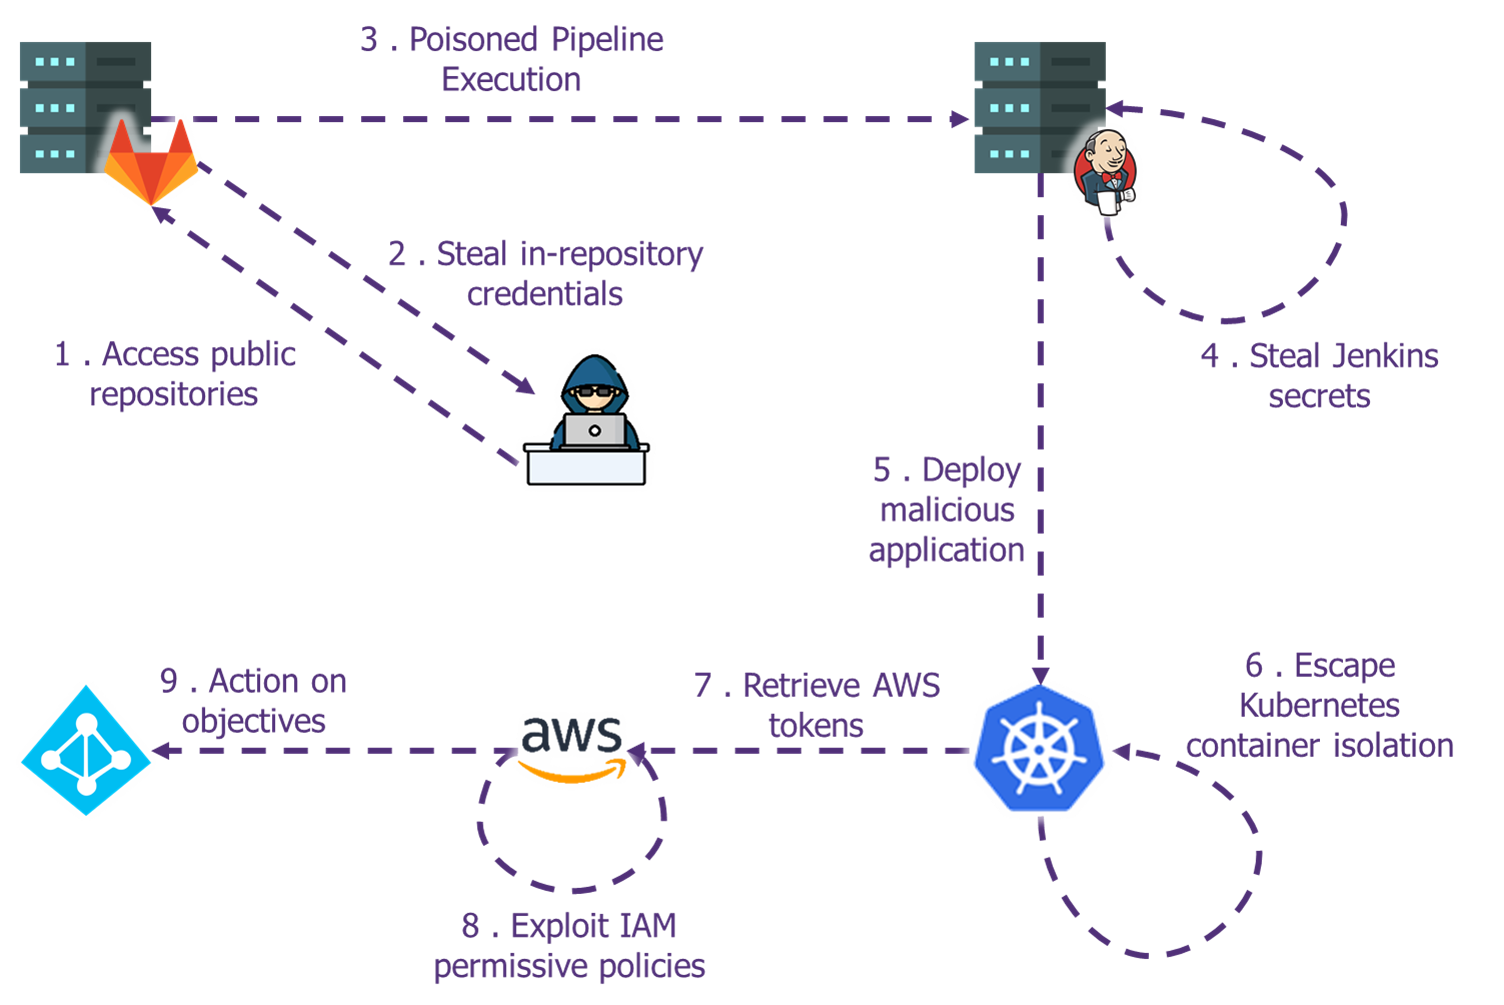 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…