

grype
 anchore/grype
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
anchore/grypeA vulnerability scanner for container images and filesystems
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
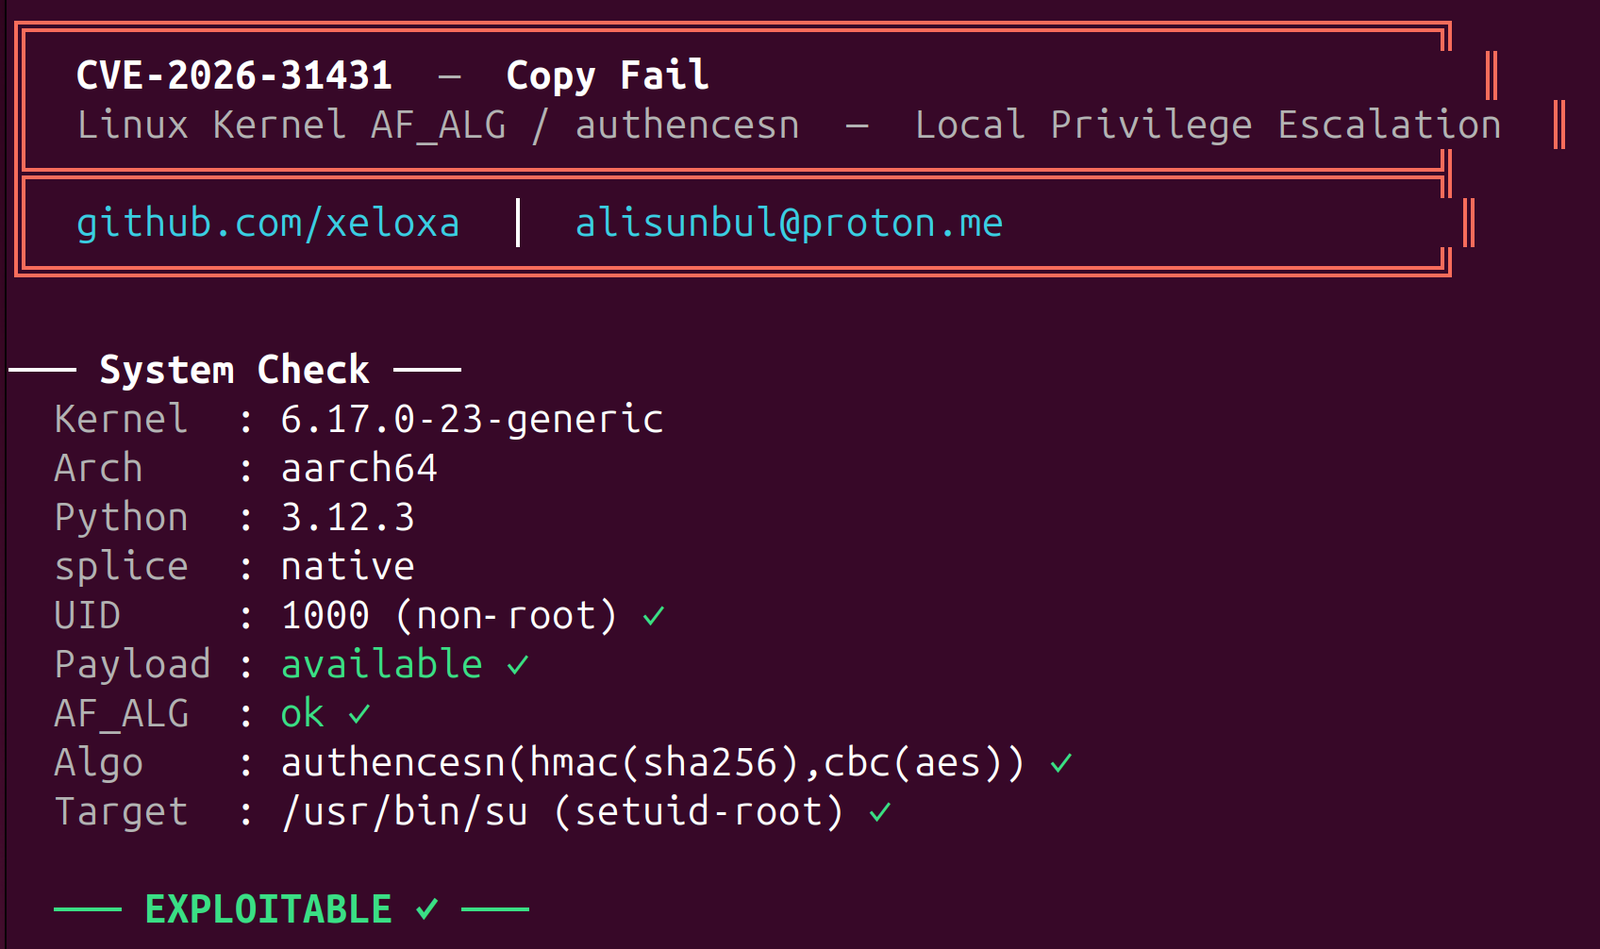 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
 0xfuffm3/cve-2026-31431-copyfail
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 takumak/cve-2019-5736-reproducer
Reproducer for CVE-2019-5736, a RunC container escape vulnerability. Provides build scripts and a KVM-based lab to confirm the exploit against…
 nicetop1027/cve-2026-d0cker
Proof-of-concept exploit for critical runC container escape vulnerability (CVE-2026-Pending) with symlink race condition, including Go PoC, analysis,…
 sonyavalo/cve-2019-5736-dockerattack-and-security-mechanism
In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.
 sofianehamlaoui/cve-2022-0492-checker
A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492
 abian2/cve-2024-21626
Proof-of-concept for CVE-2024-21626, a container escape vulnerability in runc, demonstrating exploitation techniques.
 sk3pper/cve-2024-21626-old-docker-versions
Analyzes and exploits a container escape vulnerability in legacy Docker/runc versions, demonstrating fd leakage to access the host filesystem, with…
 geropl/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runC that allows overwriting the host runC binary to gain root access…
 zpxlz/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in runc/Docker using file descriptor manipulation. For educational and…