

grype
 anchore/grype
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
anchore/grypeA vulnerability scanner for container images and filesystems
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
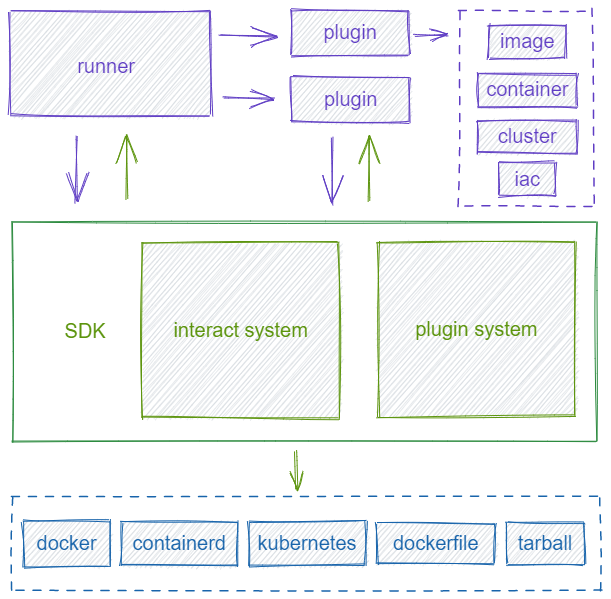 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
 krish-foren6/cve-2026-31431-report-copy-fail-vulnerability-
Detailed analysis of the Copy Fail vulnerability (CVE-2026-31431) in the Linux kernel, including memory corruption mechanism, privilege escalation…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.